
CVE-2026-2035703-x300
 danish1162/cve-2026-2035703-x300
Tozed ZLT X300 5G CPE — Remote Root Code Execution via SDR Rogue Base Station (CVE-2026-2035703, CWE-78, CVSS 9.8) — Coordinated Disclosure
binary-analysiseducationexploitation+4
1
danish1162/cve-2026-2035703-x300Tozed ZLT X300 5G CPE — Remote Root Code Execution via SDR Rogue Base Station (CVE-2026-2035703, CWE-78, CVSS 9.8) — Coordinated Disclosure
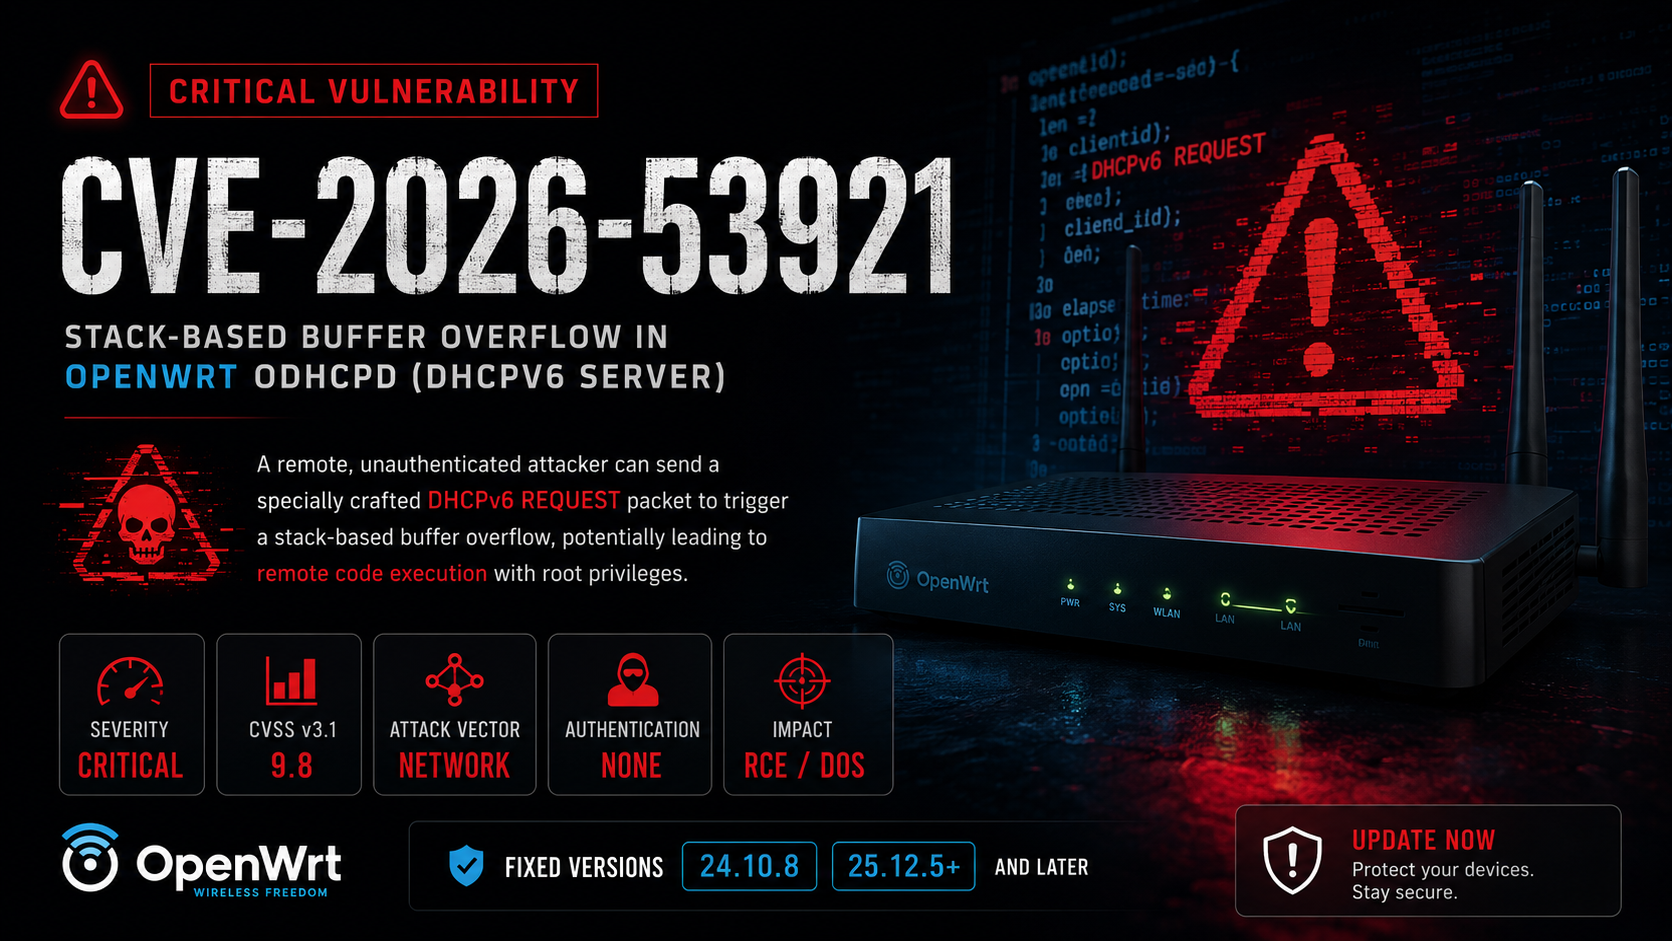
 tc4dy/cve-2026-53921-poc-exploit
CVE-2026-53921 – odhcpd Stack Overflow (CVSS 9.8) 🛡️ Vuln detailed and comprehensive Write-Up and Verifier & Multi-exploit for OpenWrt DHCPv6 RCE.…
 murrez/cve-2026-100740
Python PoC for CVE-2026-100740, an L2TP Host Name AVP out-of-bounds write in D-Link DIR-895L A1_102b07 tunnel_set_params. Fingerprints the device and…
 murrez/cve-2026-13249
Unauthenticated arbitrary file upload on Honeywell PD45 web admin (firmware F10.19.010040–before F10.22.030745) leading to RCE. Python check/exploit…
 digiprosec/microtrick
Self-contained Python PoC exploiting the MikroTrick SSH chain (CVE-2026-86060, CVE-2026-67279) to gain unauthenticated full admin access on MikroTik…
 snyi001/cve-2026-79551-tenda
Tenda Technology Co., Ltd NVR_4H: CH3 v2.1.V27.5.58.6 was discovered to contain a hardcoded cryptographic key.
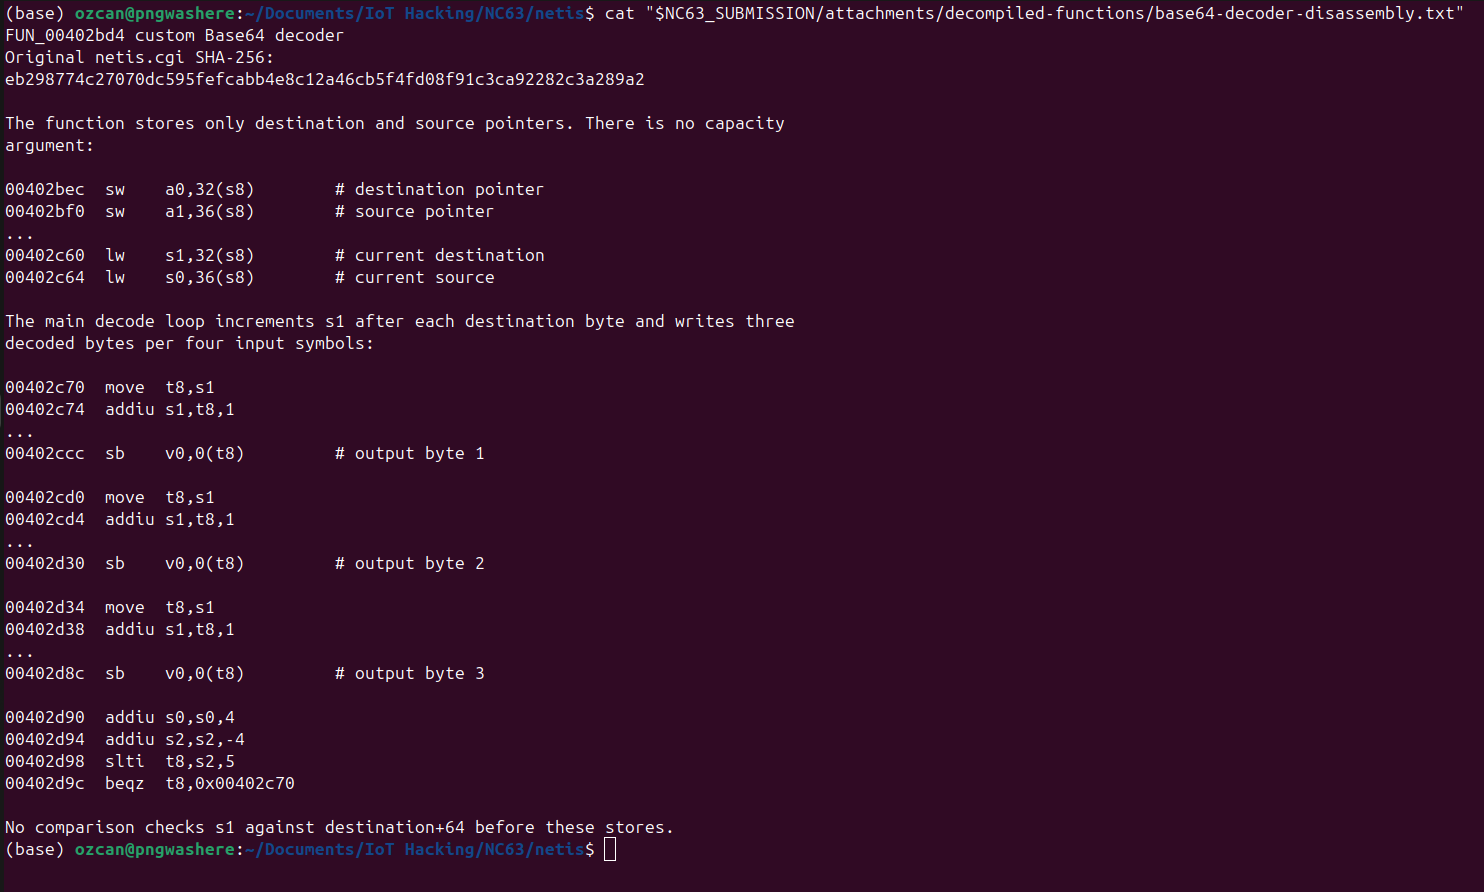 ozcanpng/cve-2026-76070
Original research and PoC for a pre-auth Base64-decoded password stack buffer overflow in Netis NC63 login.cgi
 on3sk-0x1/cve-2026-19900-poc
Proof-of-concept exploit for CVE-2026-19900, an authentication bypass and remote code execution vulnerability in LB-LINK X-PRO routers, allowing…
 poxsky/cve-2026-38577
Proof-of-concept demonstrating hardcoded root credentials (admin/system) in Tenda HG21 XPON modem firmware, enabling unauthorized root access via…
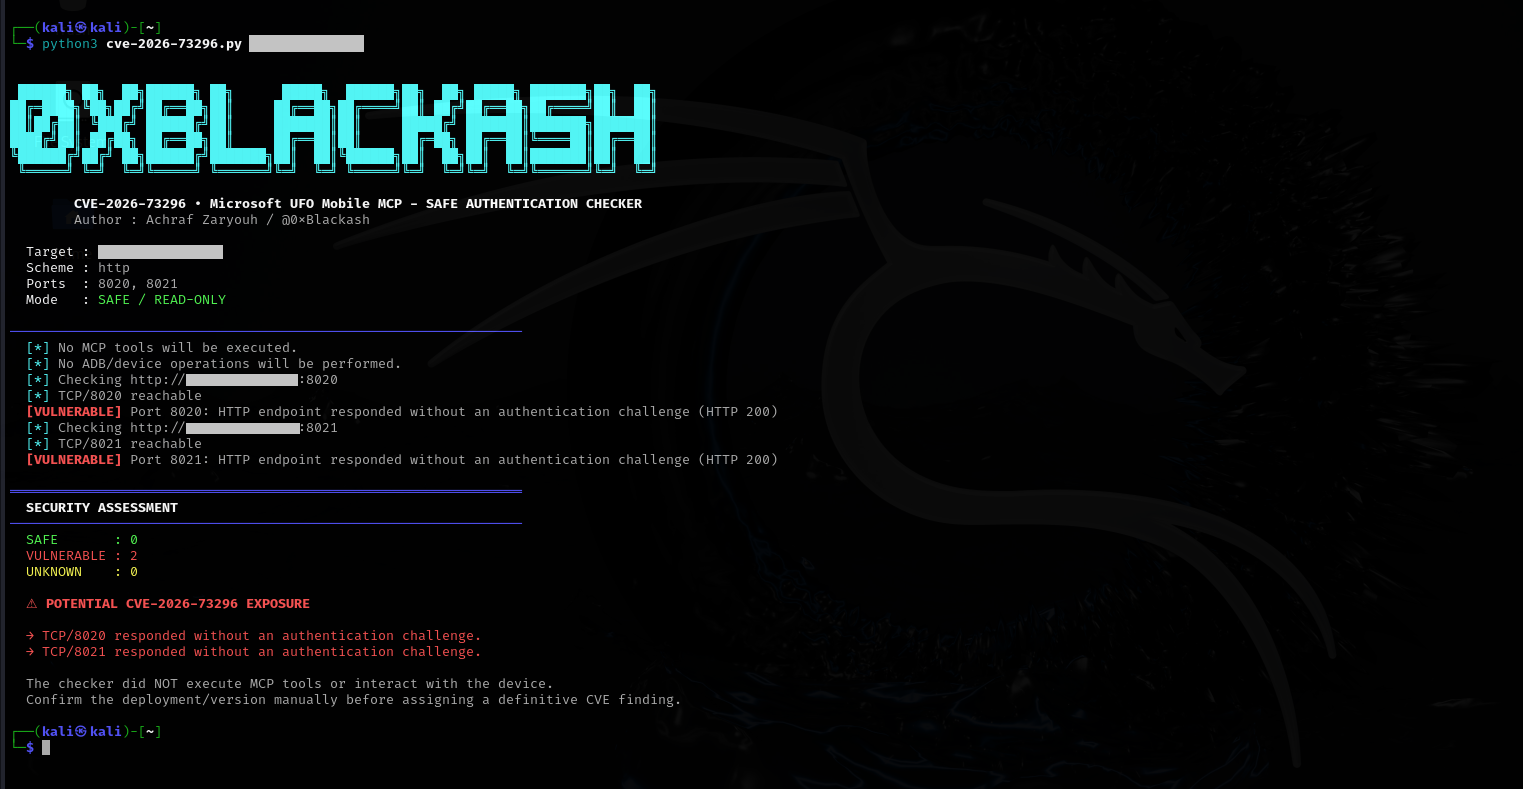 0xblackash/cve-2026-73296
Non-destructive security assessment tool for CVE-2026-73296, checking authentication boundaries on exposed Mobile MCP HTTP servers (ports 8020/8021)…
 olivierlaflamme/unibleed
Unitree G1 RCE PoC & Scripts (CVE-2026-76639 / CVE-2026-76640) technical details at boschko.ca/g1-ble-rce/
 slagzz/cve-2026-9254
TP-Link Archer BE800 V1 — Parental Control LAN RCE
 hunt-benito/the-same-key-opens-every-box-cve-2026-71960-hard-coded-jwt-secret-in-cudy-wr3000-mesh-mqtt
PoC toolkit that unpacks router firmware, decrypts device secrets, forges JWT tokens, and exploits CVE-2026-71960/71961 to take over Cudy WR3000 mesh…
 ozcanpng/cve-2026-73673
Non-destructive PoC and technical write-up for CVE-2026-73673, an unauthenticated firmware-update flaw in Netis NC63 router, with reproduction and…
 hunt-benito/go-without-bounds-cve-2026-67822-stack-overflow-in-tenda-w6-s-wifissidset
PoC for CVE-2026-67822 stack overflow in Tenda W6-S /goform/wifiSSIDset: DoS reproducer, QEMU MIPS shim, and conceptual RCE payload skeleton.
 lucasvanhaaren/cve-2026-22226
Proof of Concept for the CVE-2026-22226
 hunt-benito/zephyr-lwm2m-firmware-update-oob-read-cve-2026-10672-truncated-package-uri
Proof-of-concept exploit for CVE-2026-10672, an out-of-bounds read in Zephyr RTOS LwM2M firmware-update pull client. Includes standalone C…