
CVE-2024-22894
 jaarden/cve-2024-22894
Proof-of-concept exploit for CVE-2024-22894, demonstrating 3DES-encrypted root password extraction from Alpha Innotec/Novelan heatpump firmware,…
cryptographyembedded-systems-securityexploitation+6
3
jaarden/cve-2024-22894Proof-of-concept exploit for CVE-2024-22894, demonstrating 3DES-encrypted root password extraction from Alpha Innotec/Novelan heatpump firmware,…
 l1-0/cve-2023-30146
Some Assmann manufactured IP-Cams leak the administrator password in their backup.
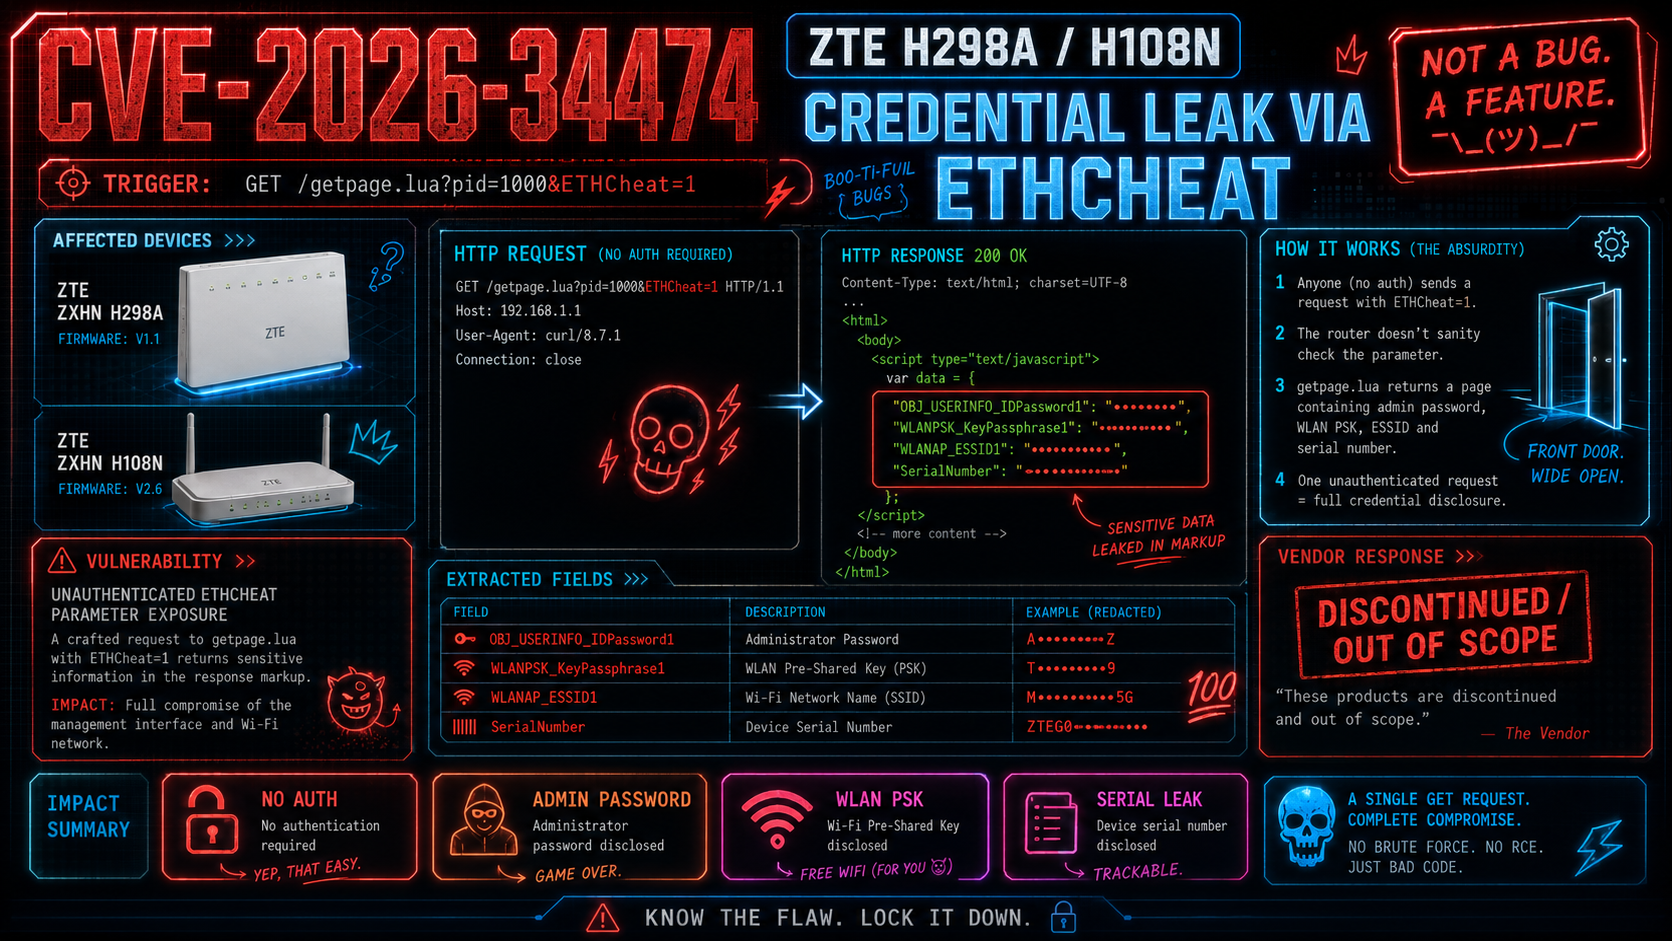 minanagehsalalma/cve-2026-34474-zte-h298a-h108n-sensitive-data-exposure
CVE-2026-34474: unauthenticated ETHCheat=1 requests leak the admin password and Wi-Fi PSK from ZTE H298A/H108N routers.
 gabrielavls/cve-2017-7921
CVE-2017-7921 exploit. Allows admin password retrieval and automatic snapshot download.
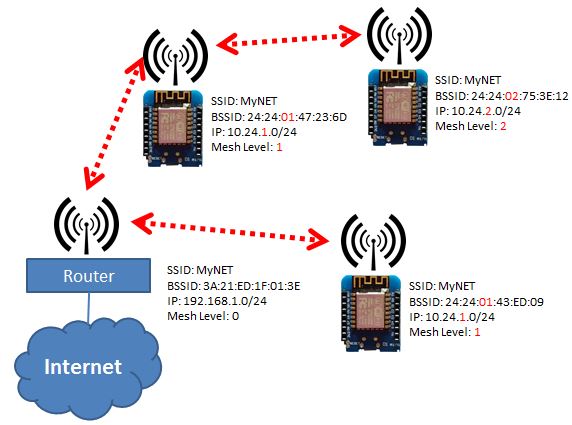 martin-ger/esp_wifi_repeater
A full functional WiFi NAT Router (and now also a WiFi Repeater)
 codeholic2k18/cve-2018-9995
DVR username password recovery.
 kensh1k/cve-2026-36438
Documentation of CVE-2026-36438: a vulnerability in Intelbras VIP 1230 B/D G4 devices allowing remote attackers to obtain administrator account…
 itzmetanjim/cve-2026-8697
Detailed CVE-2026-8697 writeup with POC exploit for a login rate-limit bypass on TP-Link Archer C64 routers via a debug SSH service, enabling…
 0xnslabs/cve-2024-25832-poc
PoC Script for CVE-2024-25832: Exploit chain reverse shell, information disclosure (root password leak) + unrestricted file upload in DataCube3
 entysec/camover
CamOver is a camera exploitation tool that allows to disclosure network camera admin password.
 entysec/rombuster
RomBuster is a router exploitation tool that allows to disclosure network router admin password.
 batchmcnulty/uberscan
Security program for recovering passwords and pen-testing servers, routers and IoT devices using brute-force password attacks.