
xmir-patcher
 openwrt-xiaomi/xmir-patcher
Patches Xiaomi router firmware images to enable SSH access and install custom firmware, with automated Windows and Linux/macOS launcher scripts.
embedded-systems-securityexploitationfirmware-analysis+4
3.7k
openwrt-xiaomi/xmir-patcherPatches Xiaomi router firmware images to enable SSH access and install custom firmware, with automated Windows and Linux/macOS launcher scripts.
 pybluez/pybluez
Python extension module providing Bluetooth access: device inquiry, SDP service browsing, RFCOMM/L2CAP sockets, and experimental BLE scanning and…
 phantom-brigade1/wifisting
GTK4 and CLI wireless security toolkit with 57 standalone modules for Wi-Fi, Bluetooth, 802.15.4, SDR/RF, NFC and router-side or network MITM testing…
 qkaiser/broadcom-wps
Tools to fingerprint WiFi Access Points running the Broadcom SDK and a list of known affected devices.
 wuyou6956-glitch/cve-2026-1668-poc
Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.
 nmatt0/moria
IoT firmware identification and extraction
 mrhenrike/embedxpl-forge
Embedded Device Security Assessment Framework — 700 modules, 350 CVEs, 55 vendors, APT Group Engine. Covers routers, IP cameras, GPON ONTs, ISP CPEs,…
 himitsushell/himitsushell
shell script protector (obfuscation, embedded interpreter, DRM) - invisible to kernel tracing
 amiraliuks/ip-camera-research
Security research on a consumer IP camera built on the Fullhan FH8626V100 SoC (model AJL30PG0803).
 mbanyamer/cve-2026-32707-px4-autopilot-tattu_can-stack-buffer-overflow-dos-
Proof-of-concept exploit for CVE-2026-32707, a stack buffer overflow in the PX4-Autopilot tattu_can driver, causing denial of service via crafted CAN…
 mbanyamer/cve-2026-26235-jung-smart-visu-server-unauthenticated-reboot-shutdown
Proof-of-concept exploit for CVE-2026-26235, an unauthenticated denial-of-service vulnerability in JUNG Smart Visu Server <=1.1.1050, allowing remote…
 trinadh465/device_renesas_kernel_aosp10_r33_cve-2021-33034
Kernel source tree for Renesas AOSP10 R33 with a patch for CVE-2021-33034, addressing a use-after-free vulnerability in the Bluetooth HCI event…
 px4/px4-autopilot
Open-source autopilot stack for drones and unmanned vehicles, supporting multirotors, fixed-wing, VTOL, and rovers with modular architecture and…
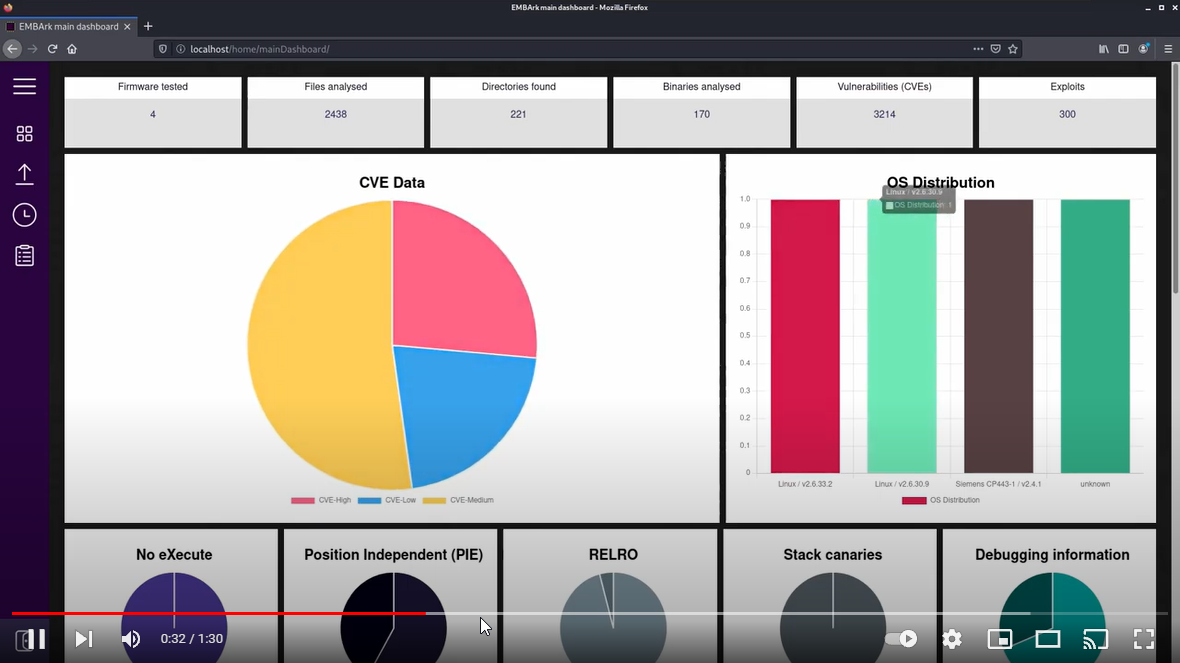 e-m-b-a/embark
Centralized firmware scanning and reporting platform with a web UI, REST API, and automated analysis workflows for securing embedded/IoT devices.
 gitchw/ghostlock-cve-2026-43499
CVE-2026-43499 (GhostLock) — Linux kernel futex PI rt_mutex UAF ARM32 privilege escalation research targeting Huawei Watch 4 Pro (kernel 5.4.210)
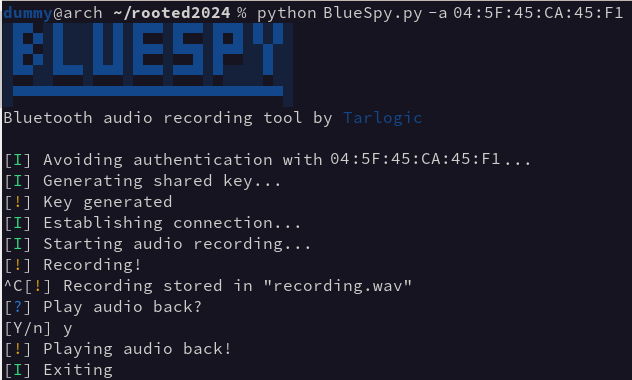 tarlogicsecurity/bluespy
PoC to record audio from a Bluetooth device
 ayushman4/tp-link-archer-cr-700-xss-exploit
Exploiting TP-Link Archer CR-700 Router. (Responsibly Disclosed to TP-Link)
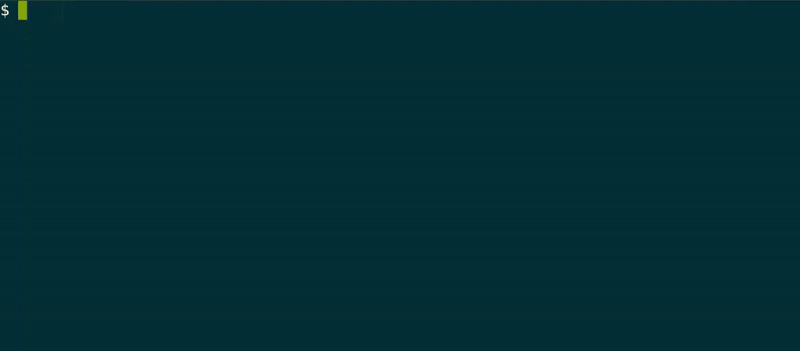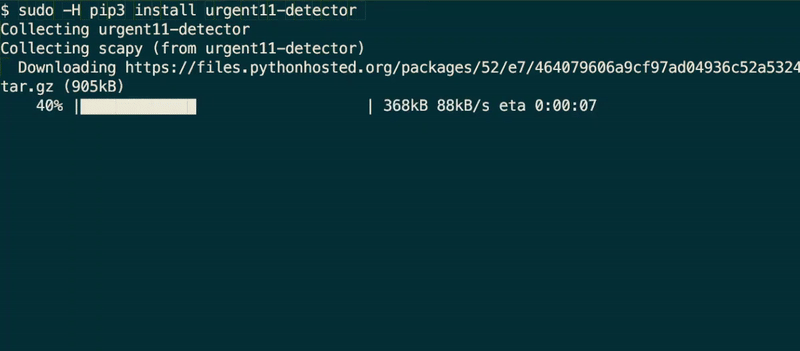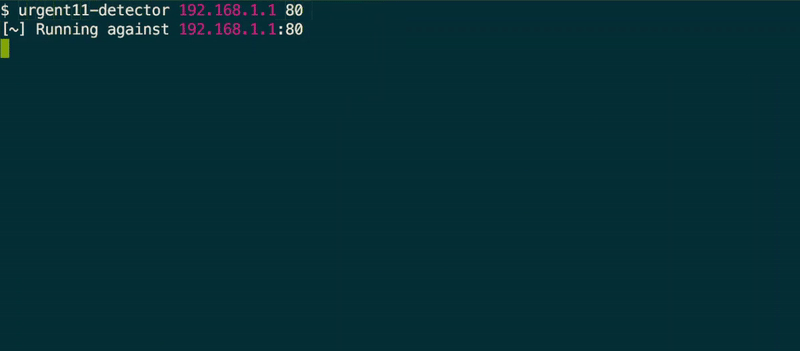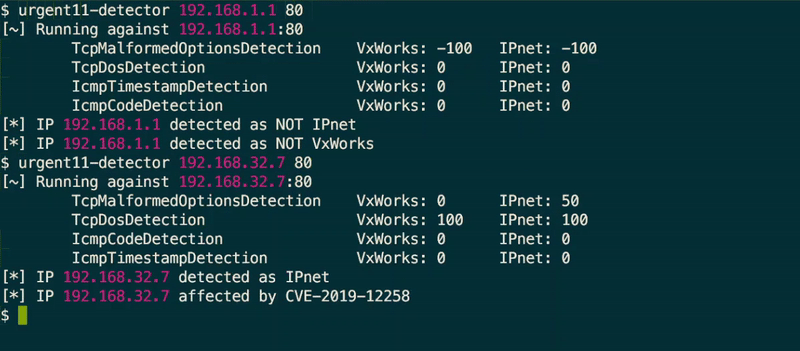 armissecurity/urgent11-detector
URGENT/11 detection tool by Armis