
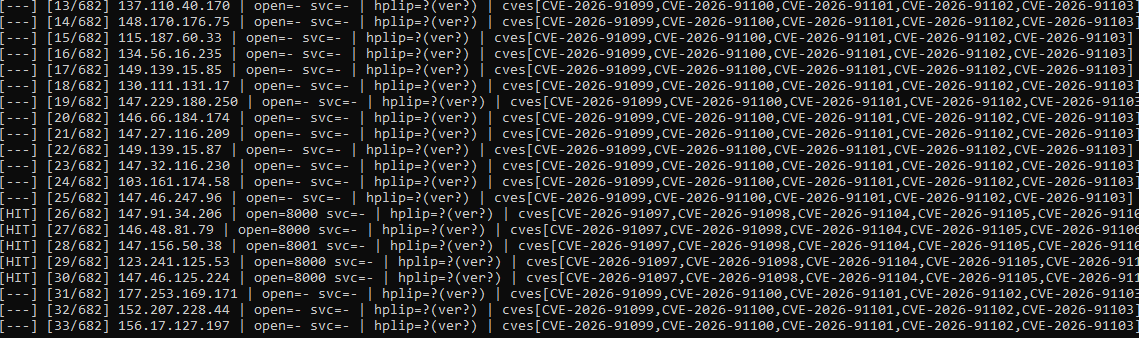
HP-HPLIP-Mass-CVE-checker-2026-09-
 murrez/hp-hplip-mass-cve-checker-2026-09-
Mass check/research exploit for HP HPLIP CVE-2026-91097–91106 (<3.26.6), PAPPL :8000 IPP probes + hpssd templates
exploitationinformation-gatheringiot-security+5
murrez/hp-hplip-mass-cve-checker-2026-09-Mass check/research exploit for HP HPLIP CVE-2026-91097–91106 (<3.26.6), PAPPL :8000 IPP probes + hpssd templates
 luel-4013/misfortune-cookie
Interactive PoC suite for CVE-2014-9222 (Misfortune Cookie) and related router exploits, featuring detection, auth bypass, DoS, and RCE modules with…
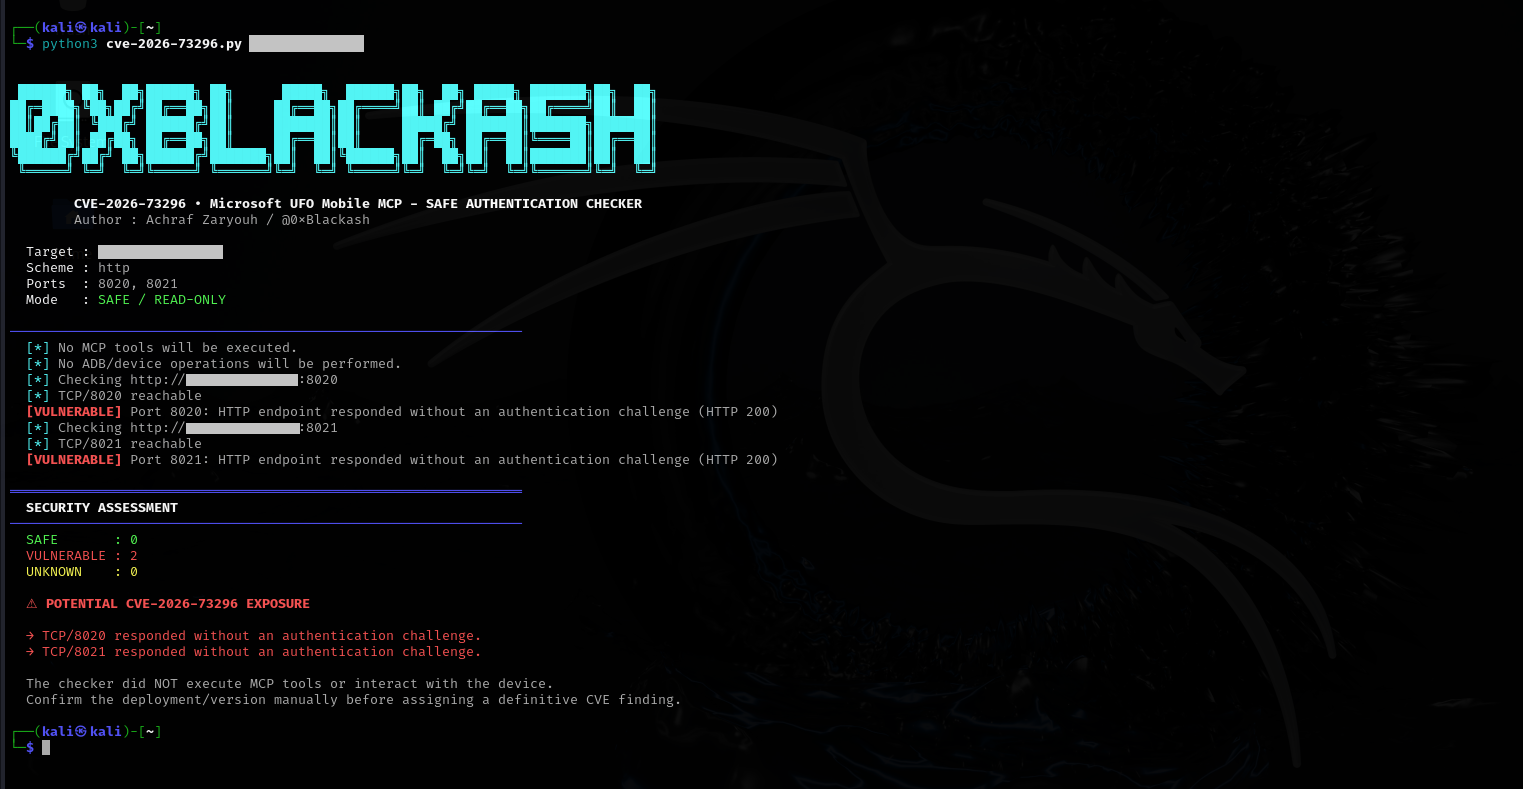 0xblackash/cve-2026-73296
Non-destructive security assessment tool for CVE-2026-73296, checking authentication boundaries on exposed Mobile MCP HTTP servers (ports 8020/8021)…
 kemrec/cve-2025-11142-axis-mediaclip-rce
Proof-of-concept and technical analysis for CVE-2025-11142, an authenticated OS command injection in AXIS VAPIX mediaclip.cgi, with time-based and…
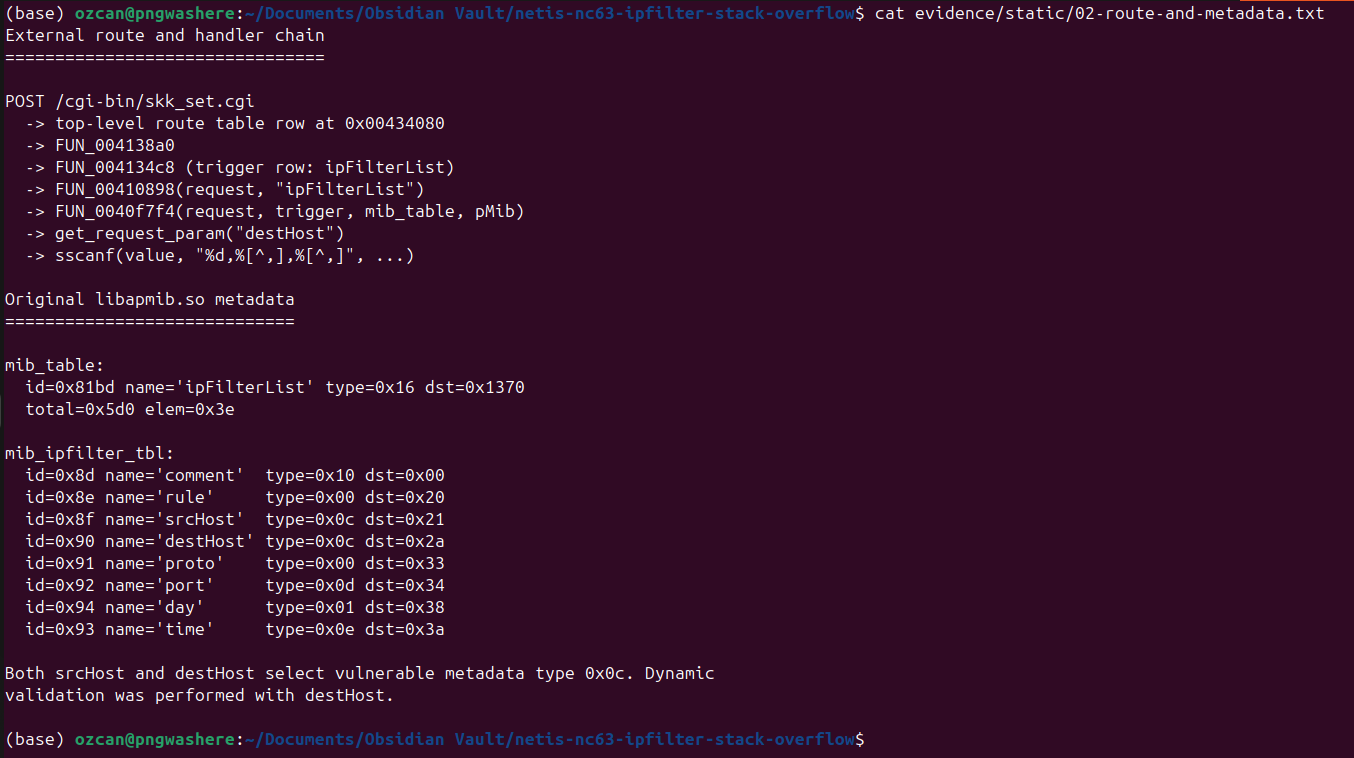 ozcanpng/cve-2026-76071
Original research and PoC for a pre-auth stack buffer overflow via unbounded sscanf scanset in the Netis NC63 ipFilterList handler
 george0papasotiriou/cve-2026-8888-printer-firmware-unsigned-update-via-http
Demonstrates CVE-2026-8888, an unsigned printer firmware update over HTTP, including a malicious update server and vulnerable printer emulator for…
 antoinet/obike
Reverse engineering of the oBike protocol communication (BLE and HTTP)
 spiralbl0ck/iot_hacking_camera_0day
Iot Camera 0day
 corelight/boa-detector
A vulnerable Boa web server detector.
 k3ystr0k3r/routeglass
Multi-threaded router fingerprinting tool that identifies web-exposed network devices by analyzing HTTP responses, headers, and favicon hashes for…
 cybervinner/cp-plus-ez-p21-cve-2026-65893-65894
Documents CP PLUS EZ-P21 IP camera CVEs: arbitrary code execution via debug feature and improper authentication of HTTP endpoints, with responsible…
 likaifeng0/cve-2018-9995_dvr_credentials-dev_tool
Exploit tool for CVE-2018-9995 that extracts credentials from exposed DVR devices via HTTP request with cookie bypass, targeting multiple vendor…
 ret2c/cve-2026-8023
PoC for CVE-2026-8023: Improper Limitation of a Pathname to a Restricted Directory ('Path Traversal')
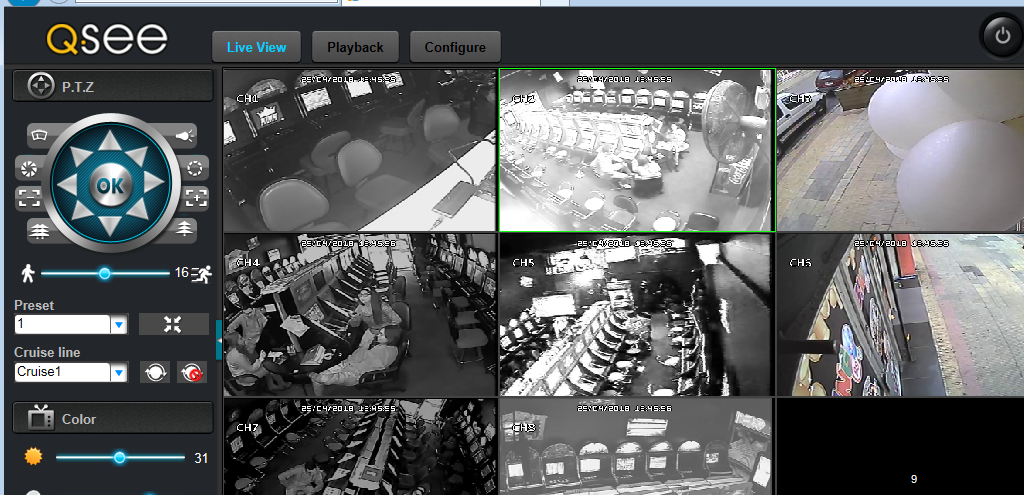 mrali-code/cve-2018-9995_dvr_credentials
Exploit tool for CVE-2018-9995 that extracts DVR credentials via unauthenticated HTTP request to vulnerable Nov, CeNova, QSee, and other DVR devices.
 nadafarafat/bd-alaris-firmware-analysis
Firmware security analysis of BD Alaris 8015 infusion pump (CVE-2016-9355). Identified 6 compound vulnerabilities including plaintext Wi-Fi…
 str0ng4le/cve-2022-30114
Proof-of-concept exploit for CVE-2022-30114, a heap-based buffer overflow in Fastweb FastGate routers. Sends a crafted HTTP Authorization header to…
 thewhiteh4t/cve-2020-9375
TP-Link Archer C50 V3 devices before Build 200318 Rel. 62209 allows remote attackers to cause a denial of service via a crafted HTTP Header…
 mverschu/cve-2017-7921
HikVision Auth Bypass CVE, tool is able to extract credentials, and take snapshots based on magic cookie or supplied credentials.