

CVE-2026-95675
 d6fault/cve-2026-95675
Python PoC exploiting CVE-2026-95675, an unauthenticated root command injection in D-Link DAP-1360 RevB firmware via a hardcoded auth-bypass and the…
embedded-systems-securityexploitationfirmware-analysis+6
1
d6fault/cve-2026-95675Python PoC exploiting CVE-2026-95675, an unauthenticated root command injection in D-Link DAP-1360 RevB firmware via a hardcoded auth-bypass and the…
 whoami-012/cve-2026-96515
Technical report and authenticated reverse-shell PoC for CVE-2026-96515, a root command execution flaw in the Netlink HG323RW router's BOA diagnostic…
 himitsushell/himitsushell
shell script protector (obfuscation, embedded interpreter, DRM) - invisible to kernel tracing
 digiprosec/microtrick
Self-contained Python PoC exploiting the MikroTrick SSH chain (CVE-2026-86060, CVE-2026-67279) to gain unauthenticated full admin access on MikroTik…
 snyi001/cve-2026-79551-tenda
Tenda Technology Co., Ltd NVR_4H: CH3 v2.1.V27.5.58.6 was discovered to contain a hardcoded cryptographic key.
 peterlinccl/vulnerability-dlink-cve-2025-14659
Static analysis (Ghidra) and custom packet-crafting (Scapy) demonstrating a root-level DHCP command injection vulnerability (CVE-2025-14659) in…
 harbingerse7en/cve-2024-20154
Technical writeup analyzing CVE-2024-20154, a stack-based buffer overflow in MediaTek MT6769 NB-IoT baseband firmware, covering reverse engineering…
 nickdaria/wyze-bulb-color-pwned
No-open firmware exploit for the Wyze WLPA19CV2 color bulb
 xernary/cve-2026-82539
Security advisory for TOTOLINK a720r buffer overflow vulnerability
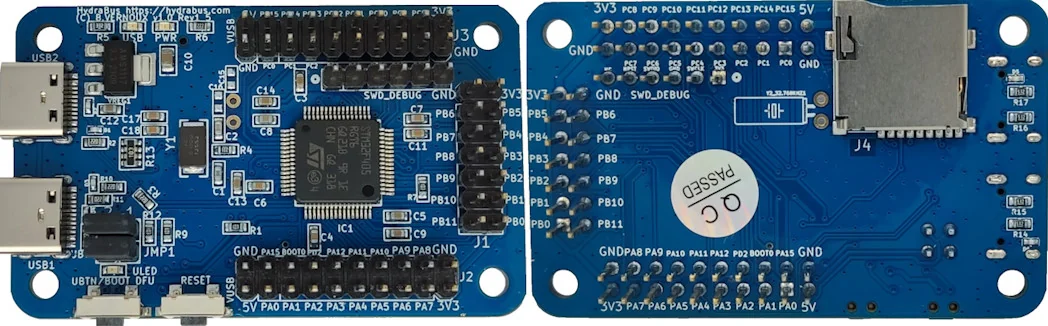 hydrabus/hydrafw
Open-source firmware for HydraBus, a multi-tool for embedded hardware debugging, hacking, and penetration testing, supporting protocols like SPI,…
 christopher-pace/cve-2023-51073
Firmware Update Server Verification Vulnerability on Buffalo LS210D Version 1.78-0.03
 ozcanpng/cve-2026-76070
Original research and PoC for a pre-auth Base64-decoded password stack buffer overflow in Netis NC63 login.cgi
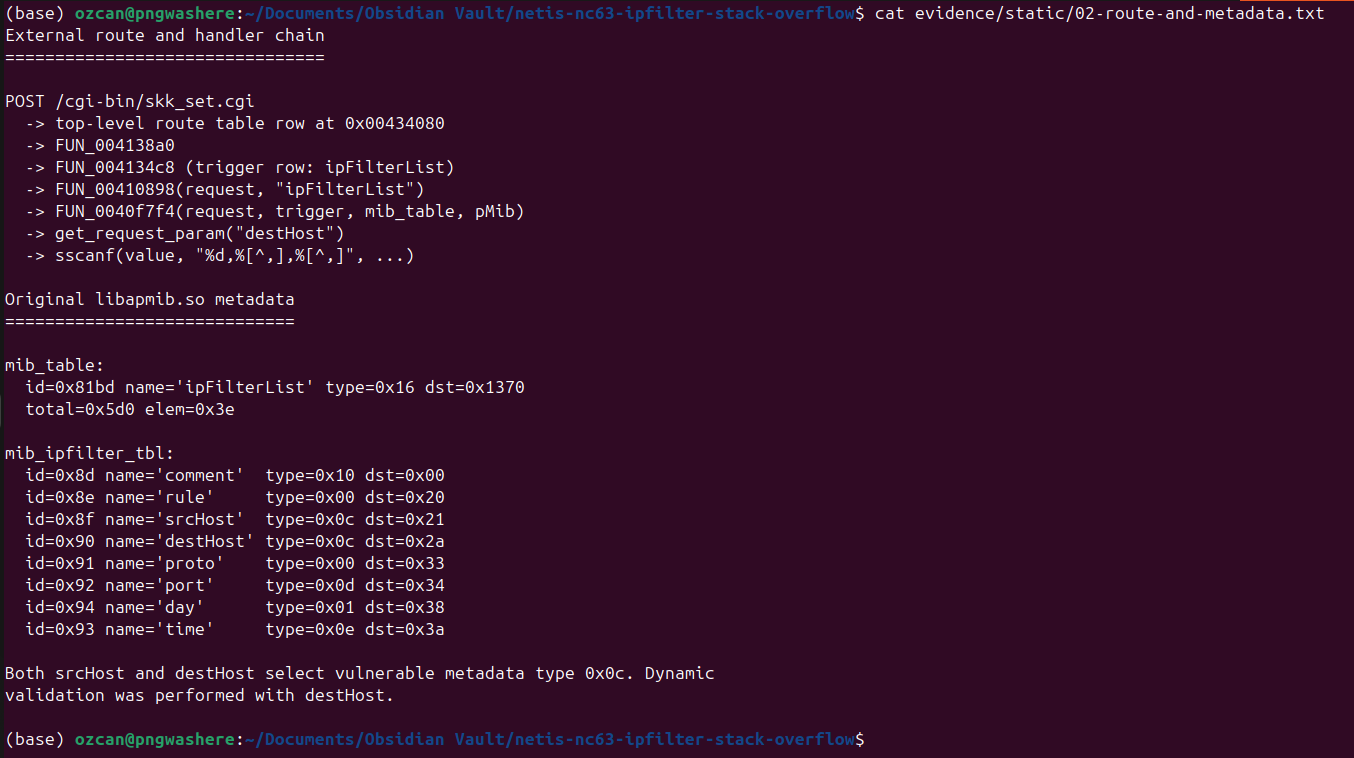 ozcanpng/cve-2026-76071
Original research and PoC for a pre-auth stack buffer overflow via unbounded sscanf scanset in the Netis NC63 ipFilterList handler
 gitchw/ghostlock-cve-2026-43499
CVE-2026-43499 (GhostLock) — Linux kernel futex PI rt_mutex UAF ARM32 privilege escalation research targeting Huawei Watch 4 Pro (kernel 5.4.210)
 limingxi6/cve-2020-9373-netgear-r6400
解决网络安全漏洞
 danyw24/zyxel-p870hn-hardware-hacking
From a bare PCB to root: hardware-hacking a ZyXEL P-870HN (BCM6368) over UART — CVE-2025-0890 + CVE-2024-40891, on my own hardware.
 binarly-io/fwhunt-scan
Tools for analyzing UEFI firmware and checking UEFI modules with FwHunt rules
 cq674350529/pocs_slides
my advisory, poc, slides and scripts related to IoT/protocol security