CVE-2020-25749
Proof-of-concept exploit for CVE-2020-25749 targeting Rubetek cameras with hardcoded Telnet credentials, enabling remote root shell access and full…

Proof-of-concept exploit for CVE-2020-25749 targeting Rubetek cameras with hardcoded Telnet credentials, enabling remote root shell access and full…

CVE-2020-11881: unauthenticated remote DoS for MikroTik SMB service.

MikroTik remote jailbreak for v6.x.x

Reolink Duo 2 WiFi v1.0.280 - Account Enumeration Vulnerability

Tozed ZLT X300 5G CPE — Remote Root Code Execution via SDR Rogue Base Station (CVE-2026-2035703, CWE-78, CVSS 9.8) — Coordinated Disclosure

TP-Link TL-WR1043ND - Authenticated Remote Code Execution

AJCloud AJY IPC Firmware Path Traversal via jdbhttpd

DeadManSwitch in rust with several triggers (remote local and network)

Pre-Authenticated Full Root Remote Command Execution in Voltronic Power SNMP Web Pro 1.1

A privacy-preserving Raspberry Pi home security camera that uses advanced end-to-end encryption.

AIO Cloud Managment Server

Cross-Site Request Forgery (CSRF) vulnerability in the password change function, which allows remote attackers to change the admin password without…

Proof-of-concept exploit and analysis for command injection and hardcoded backdoor credentials in D-Link NAS devices, enabling unauthenticated remote…

A remote Denial of Service (DoS) exploit for PX4 Autopilot versions ≤1.17.0-rc2 via a stack‑based buffer overflow in the MavlinkLogHandler.

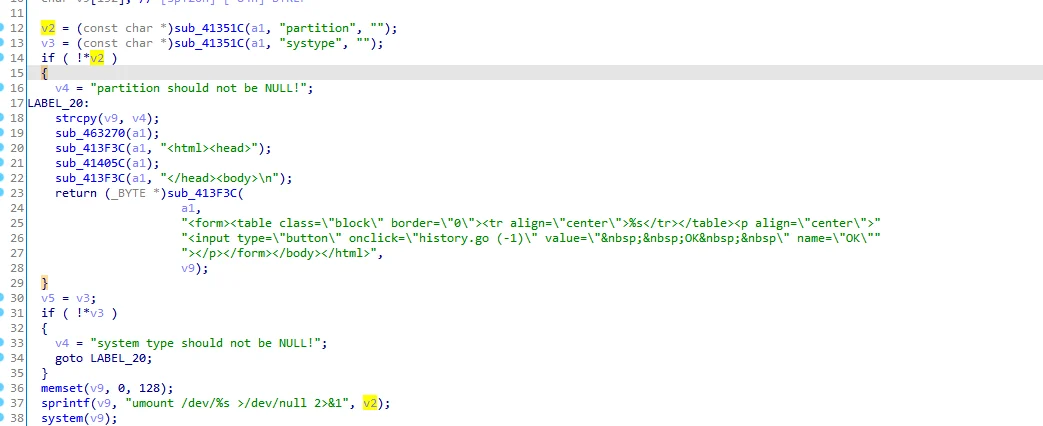
Proof-of-concept exploit for D-Link DIR-825M stack buffer overflow and command injection in /boafrm/formDiskFormat, enabling remote code execution as…

PoC tools for CVE-2026-58457: Unauthenticated OS Command Injection leading to remote root on Shenzhen Aitemi M300 Wi-Fi Repeater (MT02). Includes…

CVE-2018-19537

From Solder to Shell: Full Hardware Exploitation of the Linksys WRT54GL Router (CVE-2022-43973)