
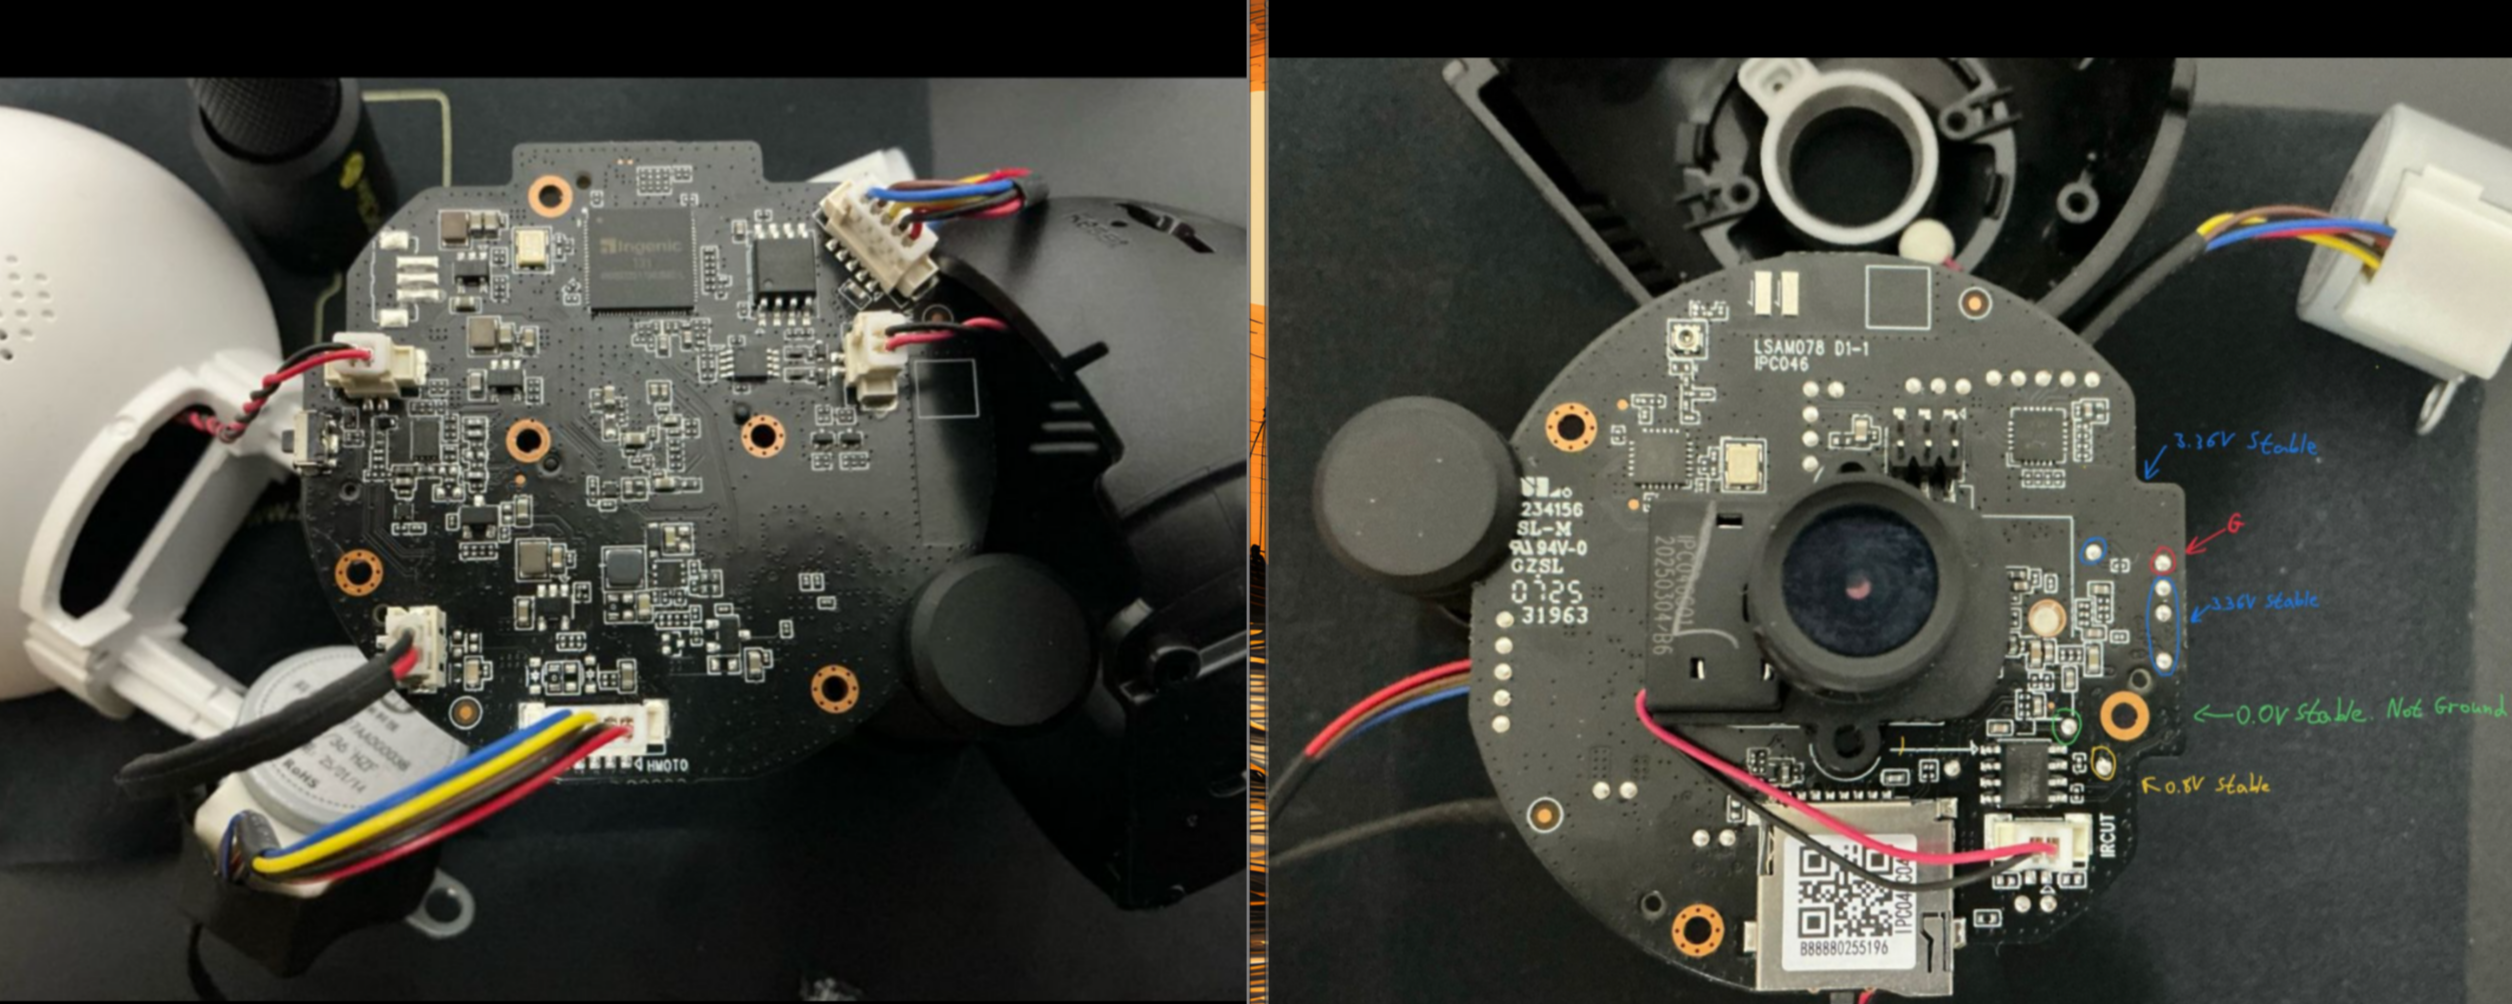
Xiaomi-C200-Firmware-Analysis
 h3xdum/xiaomi-c200-firmware-analysis
From UART to Root: Breaking Into the Xiaomi C200 via U-Boot
data-recoveryembedded-systems-securityexploitation+6
11
h3xdum/xiaomi-c200-firmware-analysisFrom UART to Root: Breaking Into the Xiaomi C200 via U-Boot
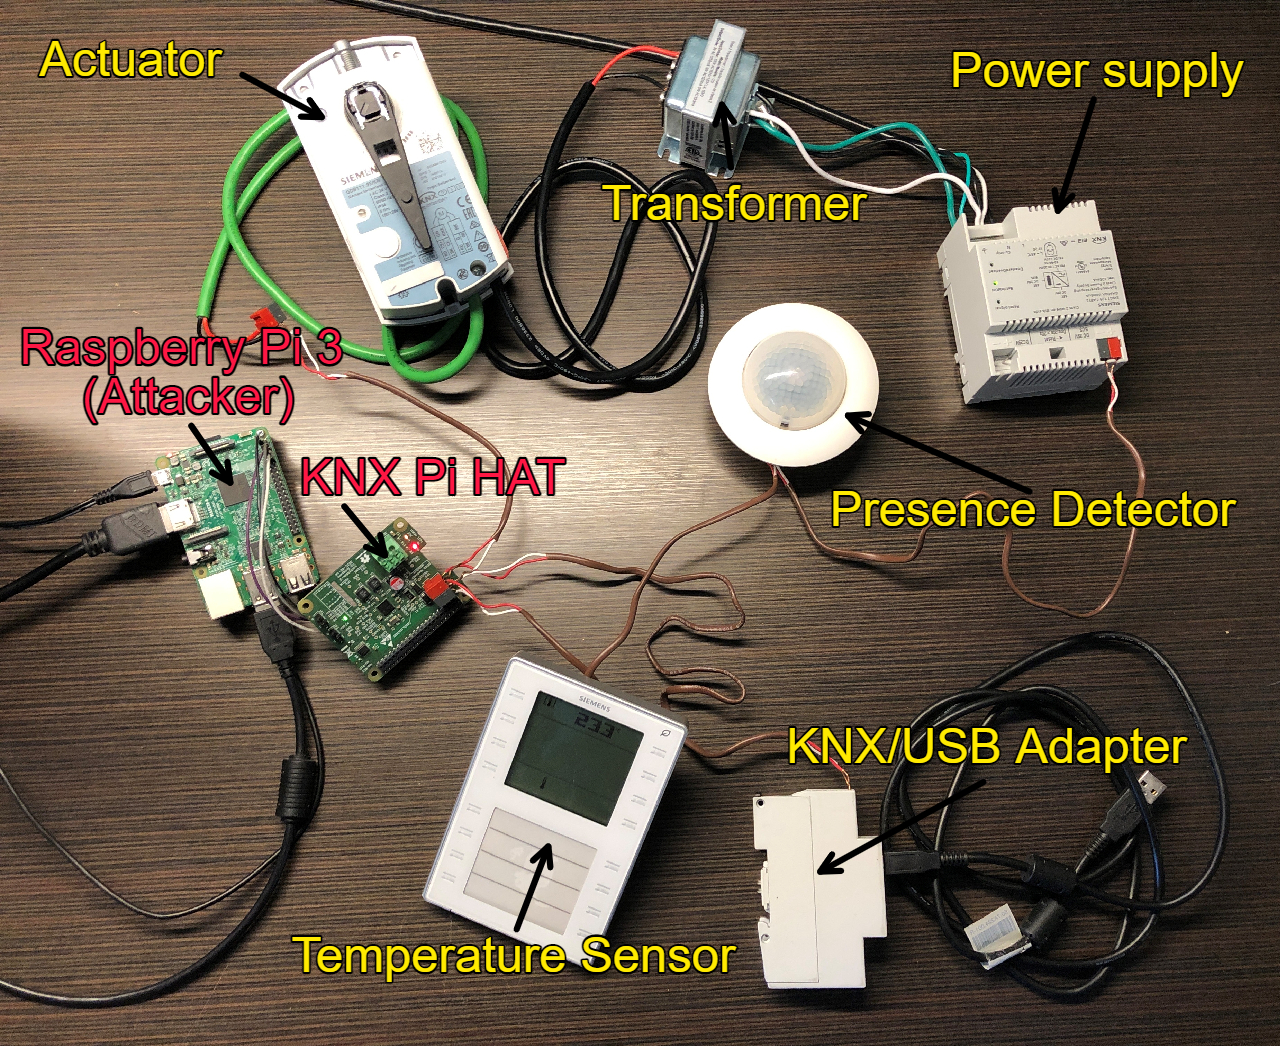 chrism09/knx-bus-dump
A tool to listen on a KNX bus via TPUART and the Calimero Project suite and to dump the data from the packets into a Wireshark-Compatible file hex…
 cyberharsh/mini_httpd-cve-2018-18778
PoC exploit for CVE-2018-18778: arbitrary file read in mini_httpd 1.29 via empty Host header, affecting IoT devices from Huawei, Zyxel, and others.
 k3ystr0k3r/routeglass
Multi-threaded router fingerprinting tool that identifies web-exposed network devices by analyzing HTTP responses, headers, and favicon hashes for…
 hivesecurity/pso-printer-security-offensive
Offensive security tool for printer pentesting
 sermikr0/cve-2026-38426
CVE-2026-38426 — strcpy() Stack Buffer Overflow in Tasmota fetch_jpg() boundary[40] (Tasmota <= 15.3.0.3)
 h-rat/evilcrowrf_custom_firmware_cc1101_flipperzero
This firmware is an alternative to the EvilCrowRF default firmware. Module: CC1101 - Compatible Flipper Zero file.
 shlln/cve-2026-90847
Proof-of-concept for CVE-2026-90847, an authenticated RCE in iux_set.cgi via malicious .cfg tar upload that writes commands into crontab for…
 dersecure/cve-2024-33676
Technical disclosure of CVE-2024-33676: weak authentication on Enel X JuiceBox EV chargers enabling PII extraction, settings manipulation, and OS…
 chrisjd20/hikvision_cve-2017-7921_auth_bypass_config_decryptor
This python file will decrypt the configurationFile used by hikvision cameras vulnerable to CVE-2017-7921.
 woolf/rtspbrute
Tool for RTSP that brute-forces routes and credentials, makes screenshots!
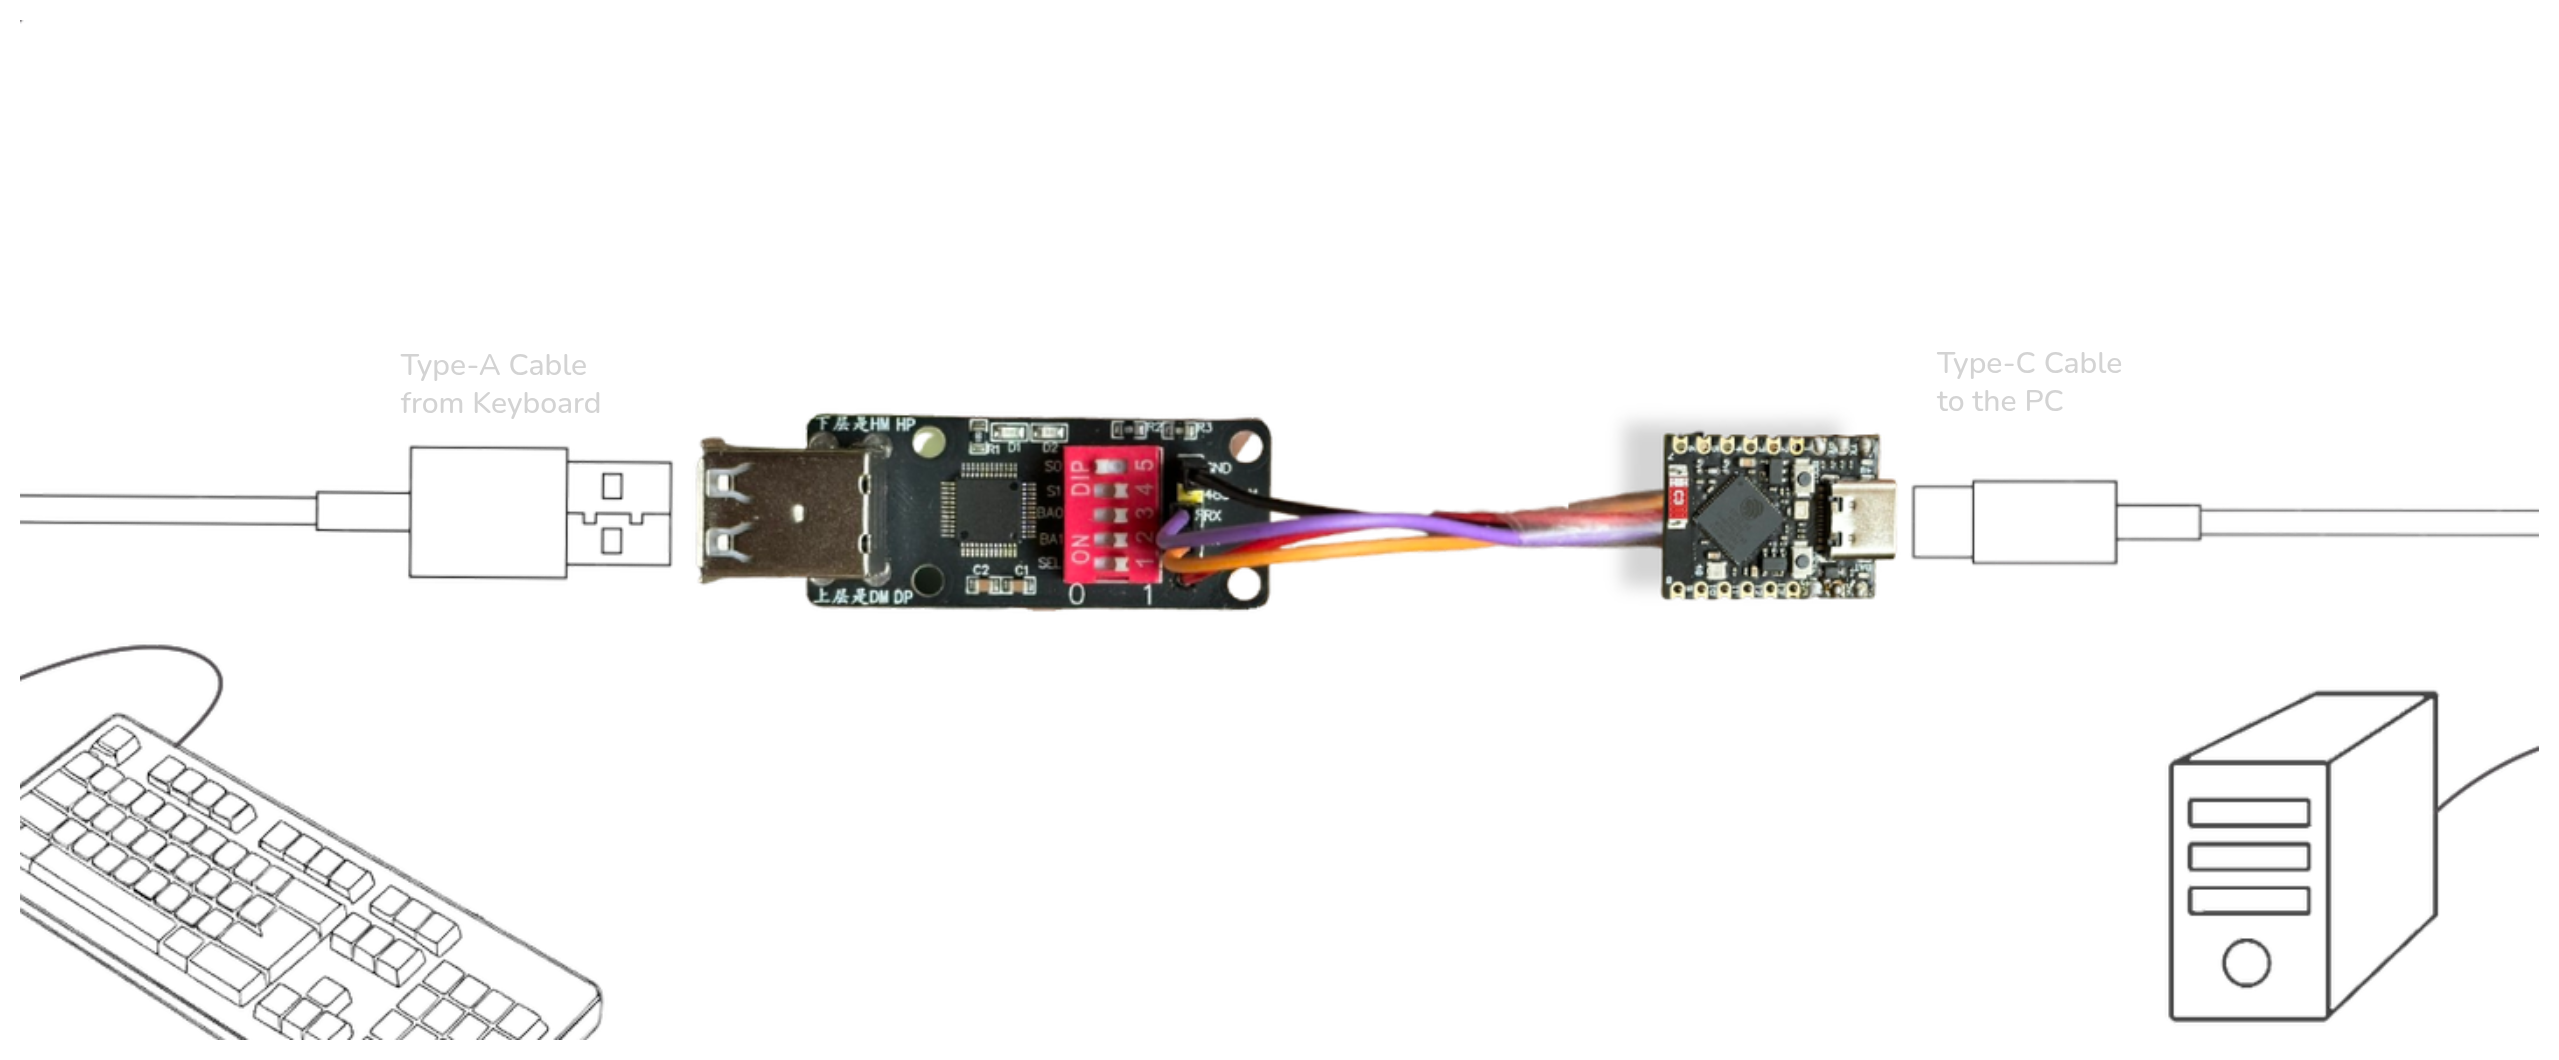 itsmmdoha/ducklogger
A ESP32-S3–based usb keylogger with wifi, easy DIY-able with widely available hardware.
 p4tq/hikvision_cve-2017-7921_auth_bypass_config_decryptor
Decrypts Hikvision IP camera configuration files extracted via CVE-2017-7921 authentication bypass, revealing user credentials and device settings.
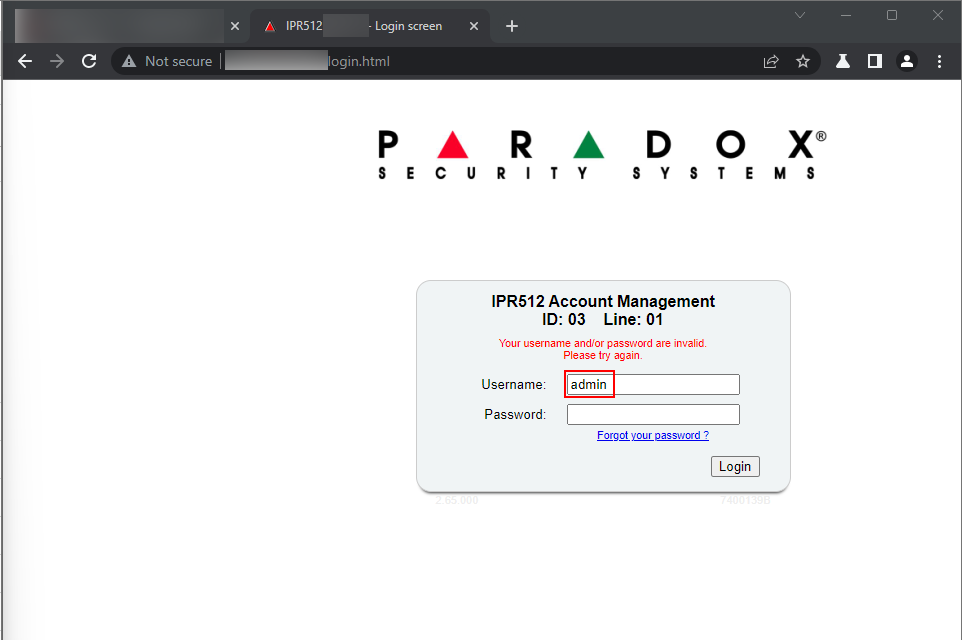 darknesschieftain/injection-vulnerability-in-paradox-security-systems-ipr512-cve-2023-24709-poc
In Paradox Security System IPR512 Web console login form page, attacker can input JavaScript string, such as "</script>" that will overwrite…
 zzh217/cve-2018-9995_batch_scanning_exp
CVE-2018-9995_Batch_scanning_exp
 fr0stm0urne/cve-2023-33768
DoS against Belkin smart plugs via crafted firmware injection
 purseclab/cve-2023-33768
DoS against Belkin smart plugs via crafted firmware injection