
cve-2022-46718-leaky-location
 biscuitehh/cve-2022-46718-leaky-location
CVE-2022-46718: an app may be able to read sensitive location information.
exploitationinformation-gatheringios-security+3
27
biscuitehh/cve-2022-46718-leaky-locationCVE-2022-46718: an app may be able to read sensitive location information.
 feliam/cve-2014-4378
Exploit analysis for CVE-2014-4378: information disclosure in Apple CoreGraphics via crafted PDF, enabling memory layout leak and bypass of ASLR,…
 bazad/x18-leak
CVE-2018-4185: iOS 11.2-11.2.6 kernel pointer disclosure introduced by Apple's Meltdown mitigation.
 xcodeon1/ipa-scope
Static analysis tool for iOS applications that extracts links, API keys, subdomains, binary info, linked libraries, and strings to aid mobile…
 synacktiv/appledb_rs
Curated database of Apple internal artifacts (entitlements, frameworks, device versions) with API, CLI, and WebUI for iOS/macOS security research and…
 axi0mx/ipwndfu
open-source jailbreaking tool for many iOS devices
 majd/ipatool
Command-line tool that allows you to search for iOS, iPadOS, tvOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS .pkg app…
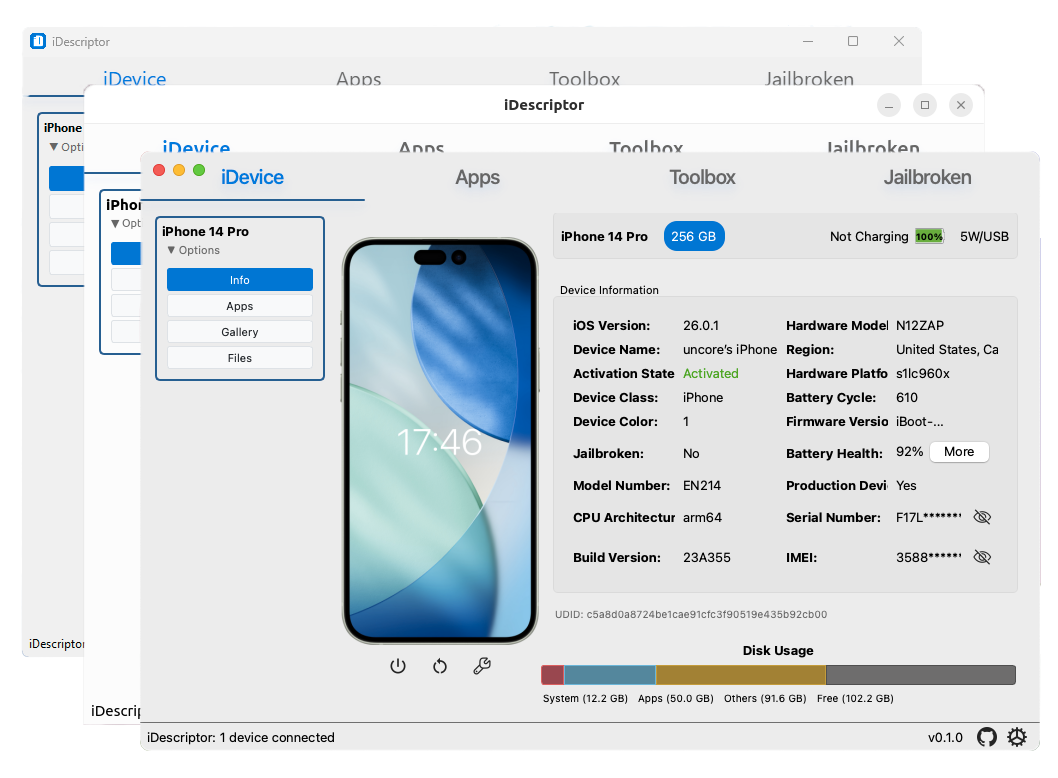 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt
 lucasjacks0n/eggshell
iOS/macOS/Linux Remote Administration Tool
 illusionofchaos/ios-gamed-0day
iOS gamed exploit (fixed in 15.0.2)
 lautarovculic/ioscpy
Now you can mirror and control your jailbroken iPhone over USB
 illusionofchaos/ios-nehelper-enum-apps-0day
iOS 15 0-day exploit (still works in 15.0.2)
 lautarovculic/frida-ipa-extract
Robust Frida-based tool to dump decrypted iOS apps as .ipa from a jailbroken device supports App Store, sideloaded and system.
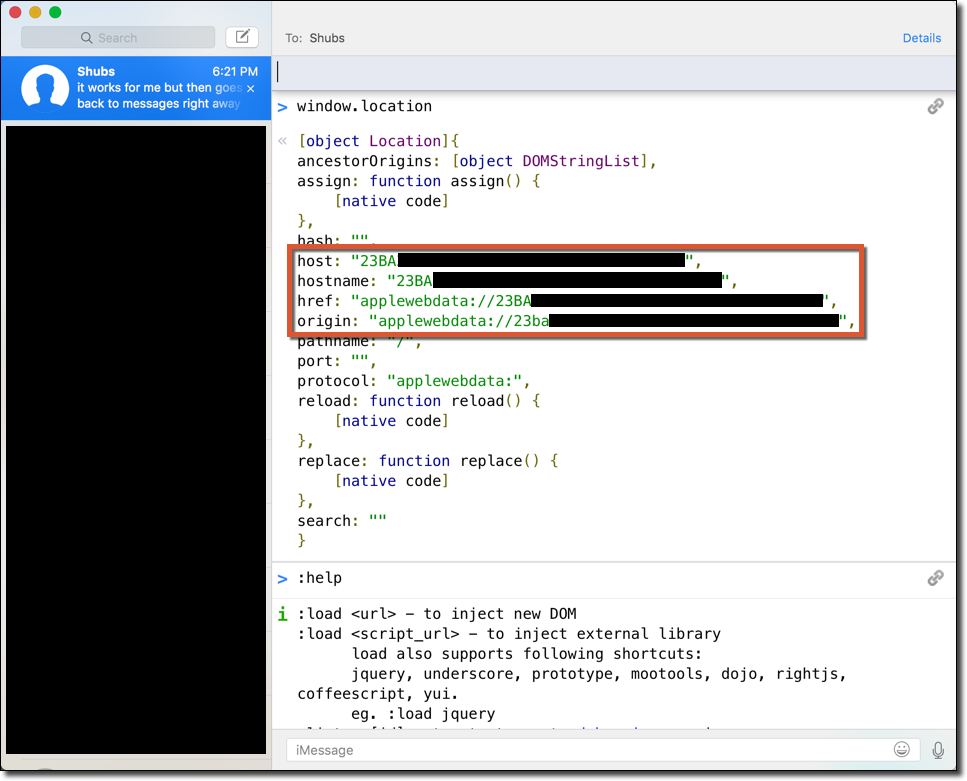 moloch--/cve-2016-1764
Extraction of iMessage Data via XSS
 peterpan0927/cve-2017-2370
on Mac 10.12.2
 speedyfriend433/cve-2026-28867-poc
Kernel info leak Proof of Concept patched in iOS 26.4 / macOS 26.4
 biscuitehh/cve-2023-40429-ez-device-name
CVE-2023-40429: An app may be able to access sensitive user data.
 tihmstar/freepw_tc7200eploit
Technicolor TC7200 - Credentials Disclosure CVE : CVE-2014-1677