MobileApp-Pentest-Cheatsheet

The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…

The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…

A collection of my Frida instrumentation scripts to reverse engineer mobile apps and more.

Write-up and proof of concepts for CVE-2021-30862, 1-click RCE bug in iOS iTunes U

Proof-of-Concept exploit for CVE-2025-14174 (EUVD-2025-203113) - Memory corruption in ANGLE allowing out-of-bounds access and RCE in web browsers.…


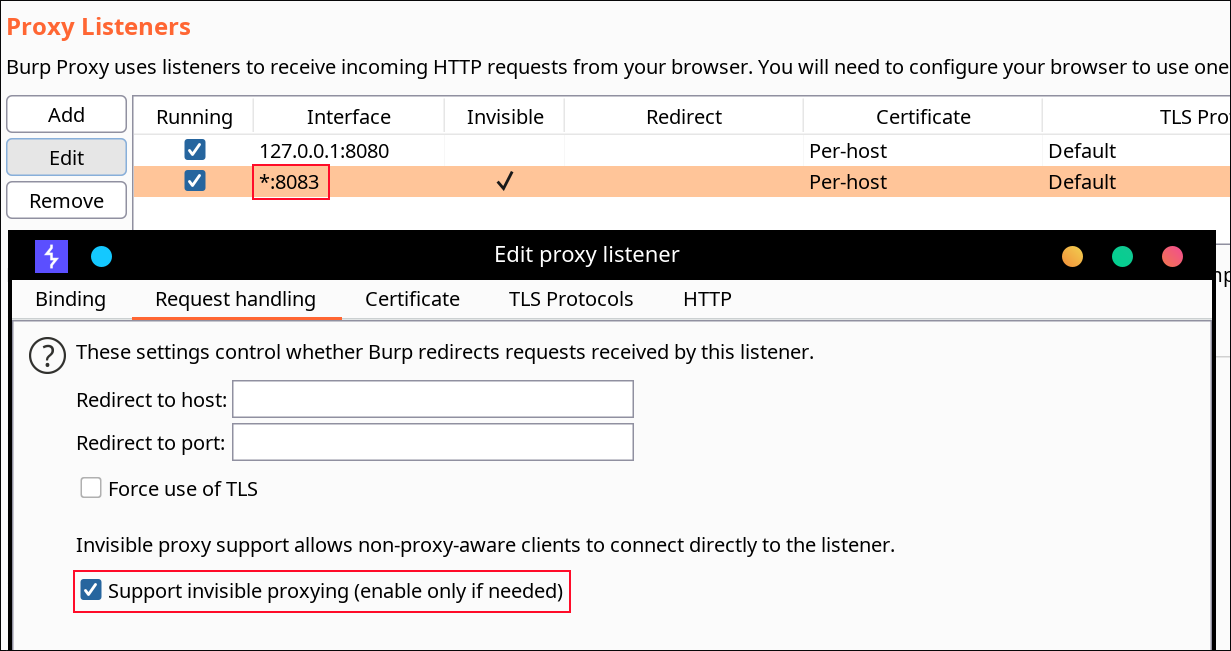
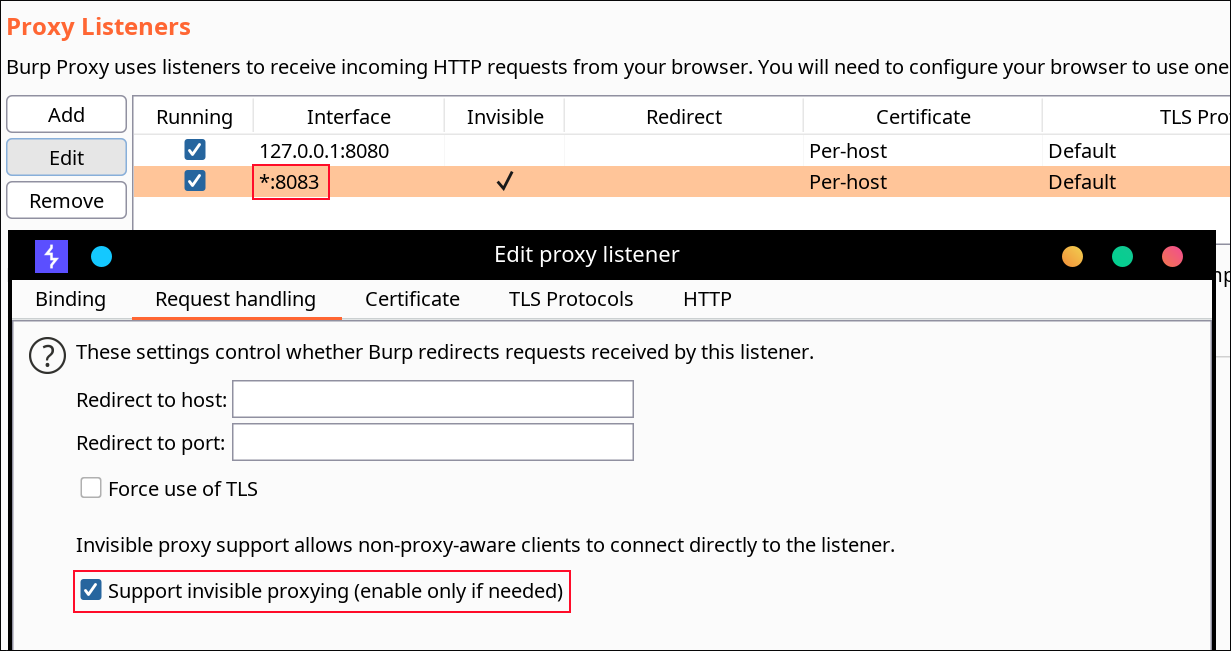
Simple utility for sniffing decrypted HTTP/HTTPS traffic on a macOS/iOS device (either jailbroken or not)

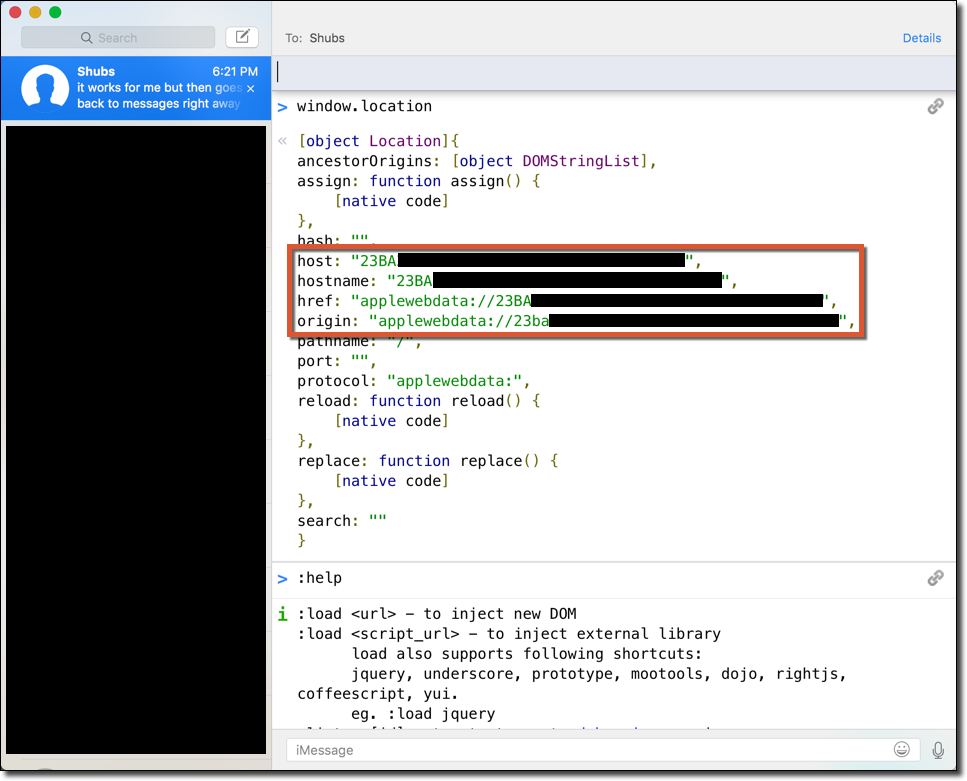
Extraction of iMessage Data via XSS

Frida scripts to rewrite mobile applications at runtime to directly MitM all HTTPS traffic

Flutter Reverse Engineering Framework

Patches Flutter engine libraries to enable runtime reverse engineering, traffic interception, and SSL pinning bypass for Android and iOS apps without…

Proof-of-concept exploit for CVE-2024-25733 demonstrating address bar spoofing in ARC Browser on iOS/iPadOS using JavaScript-based navigation…

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

Open-source mobile security testing suite for iOS and Android. Previously Passionfruit

Unofficial frida extension for VSCode

Proof-of-concept exploit for Apple SSL/TLS verification vulnerability (CVE-2014-1266) in iOS and OS X, demonstrating HTTPS interception via a proxy…

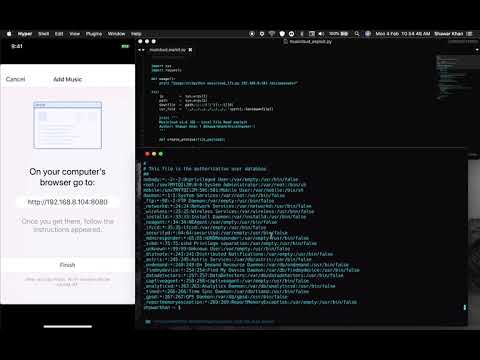
[CVE-2019-8389] An exploit code for exploiting a local file read vulnerability in Musicloud v1.6 iOS Application

iOS browser exploit for CVE-2020-9802, an old JIT bug.

CVE-2016-4657 web-kit vulnerability for ios 9.3, nintendo switch browser vulnerability