

WebKit-Bug-256172
 wh1te4ever/webkit-bug-256172
Safari 1day RCE Exploit
binary-exploitationexploitationios-security+4
1651 year ago
wh1te4ever/webkit-bug-256172Safari 1day RCE Exploit
 sterrasec/ipa-medit
Memory modification tool for re-signed ipa supports iOS apps running on iPhone and Apple Silicon Mac without jailbreaking.
 34306/decrypted
FairPlay decryptor (dump iPA) for iOS Application that running on macOS with SIP-enabled, using CVE-2025-24204. Support macOS 15.0-15.2
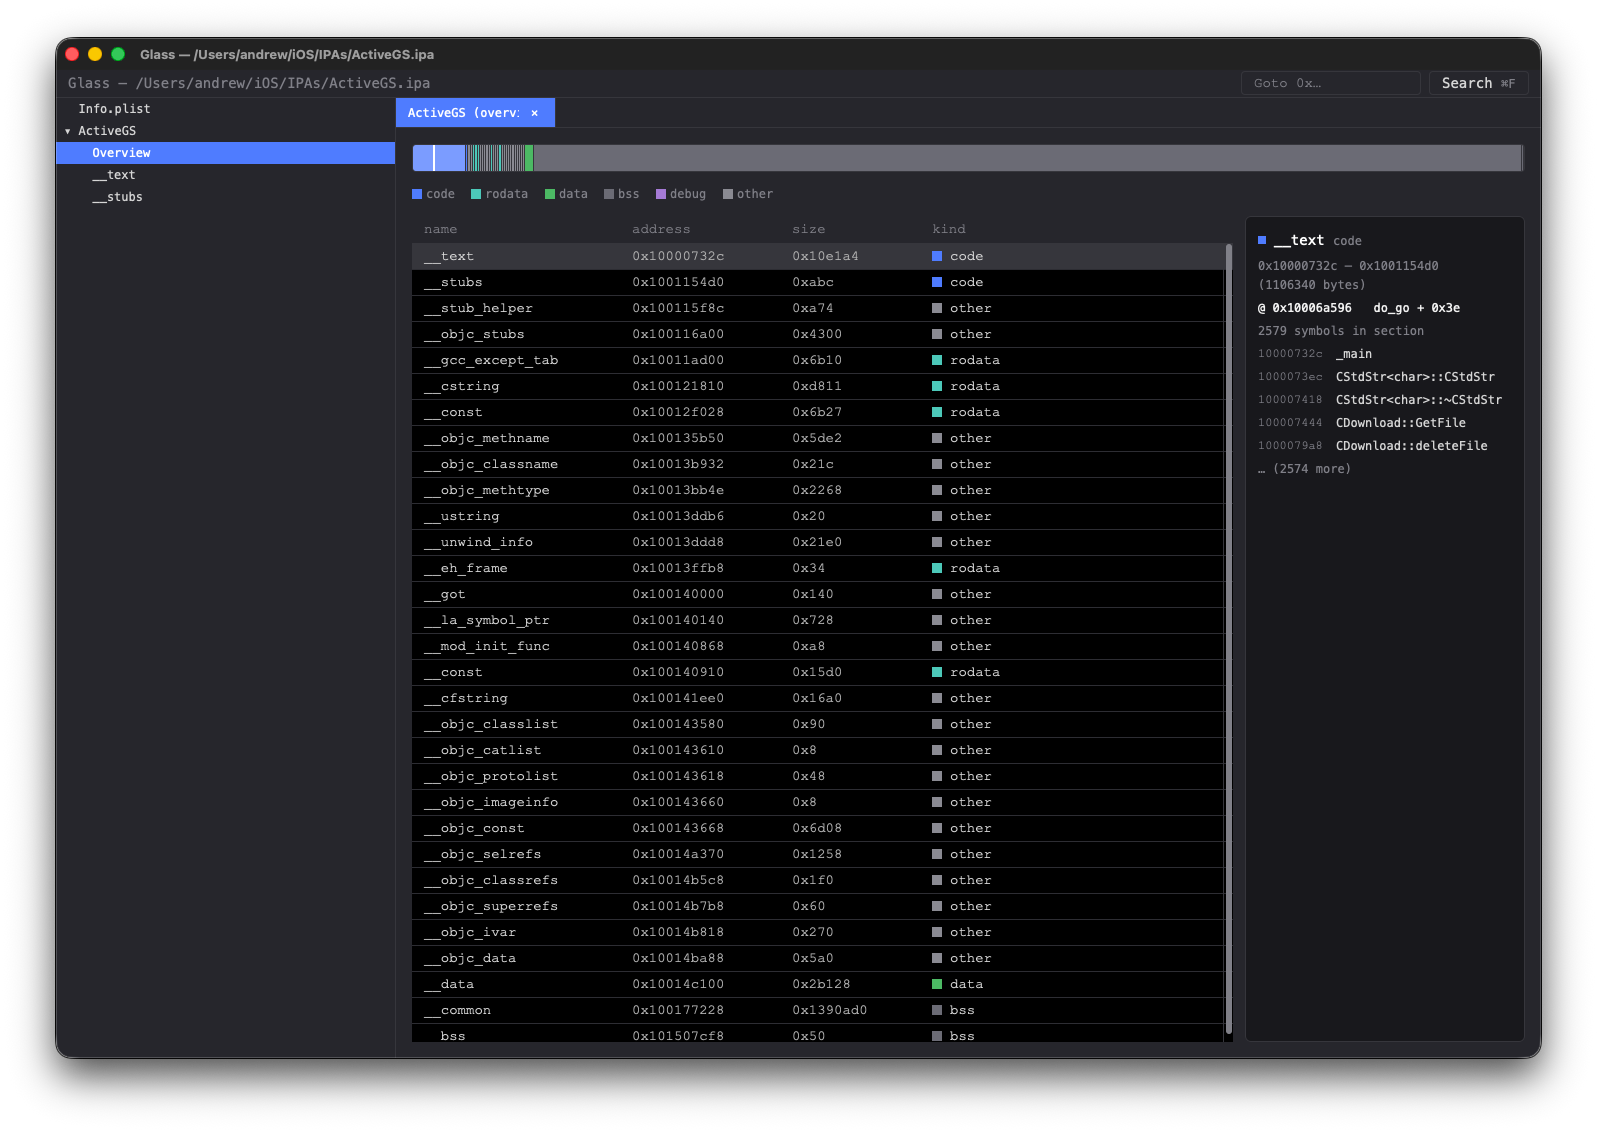 azw413/glass
Glass - a fast and free IDA Pro alternative
 feliam/cve-2014-4377
Exploit for Apple CoreGraphics heap overflow (CVE-2014-4377) enabling arbitrary code execution on iOS 7.1.x via crafted PDF used as HTML image.
 cellebrite-labs/ida_kcpp
An IDAPython module for enhancing c++ support on top of ida_kernelcache
 jsherman212/iomfb-exploit
iOS 14 kernel exploit for CVE-2021-30807 targeting IOMobileFramebuffer, with tunable memory allocation for jailbreak development on A11+ devices.
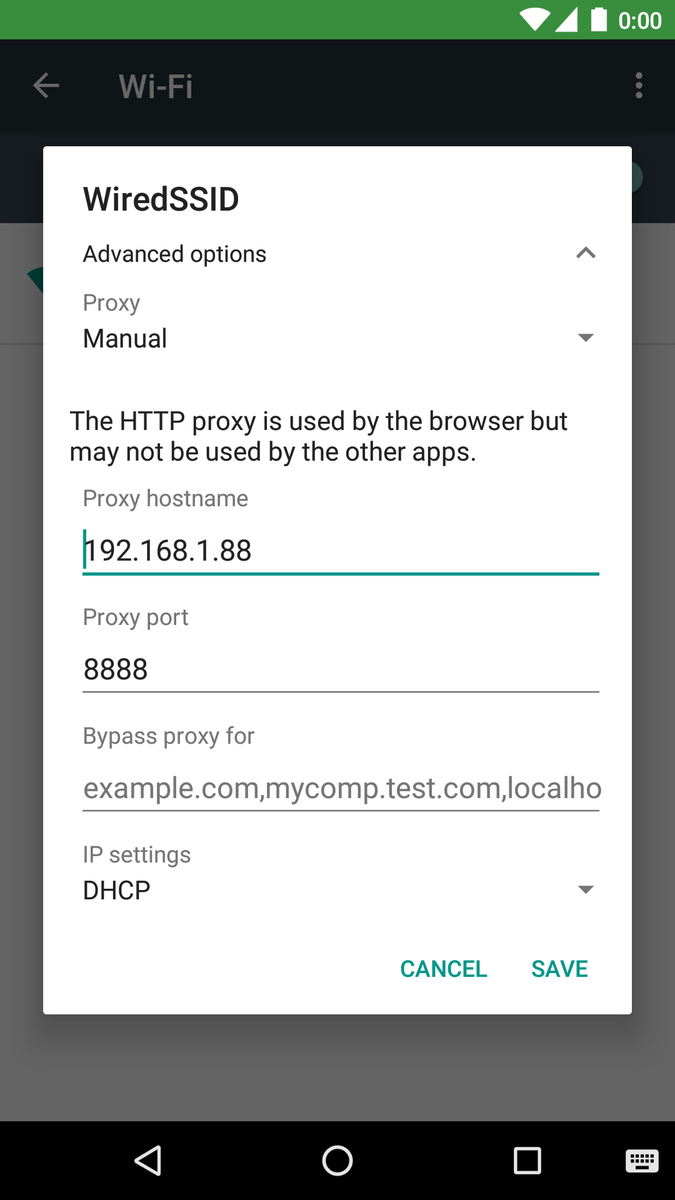 thyrlian/charles-proxy-mobile-guide
Step-by-step guide to intercepting Android and iOS HTTP/HTTPS traffic with Charles Proxy, covering SSL proxying, CA certificate installation, and…
 owasp/maswe
OWASP enumeration of common security and privacy weaknesses in mobile applications, serving as a reference bridging the MASVS verification standard…
 gabrielg/cve-2014-1266-poc
Proof-of-concept exploit for Apple SSL/TLS verification vulnerability (CVE-2014-1266) in iOS and OS X, demonstrating HTTPS interception via a proxy…
 0x742/noia
Web-based tool for browsing mobile application sandboxes, previewing SQLite databases and binary files, and downloading app data via Frida…
 0xjohnnydev/cve-2026-20637-applesepkeystore-uaf
CVE-2026-20637: AppleSEPKeyStore Use-After-Free — iOS/macOS kernel vulnerability (patched in 26.4)
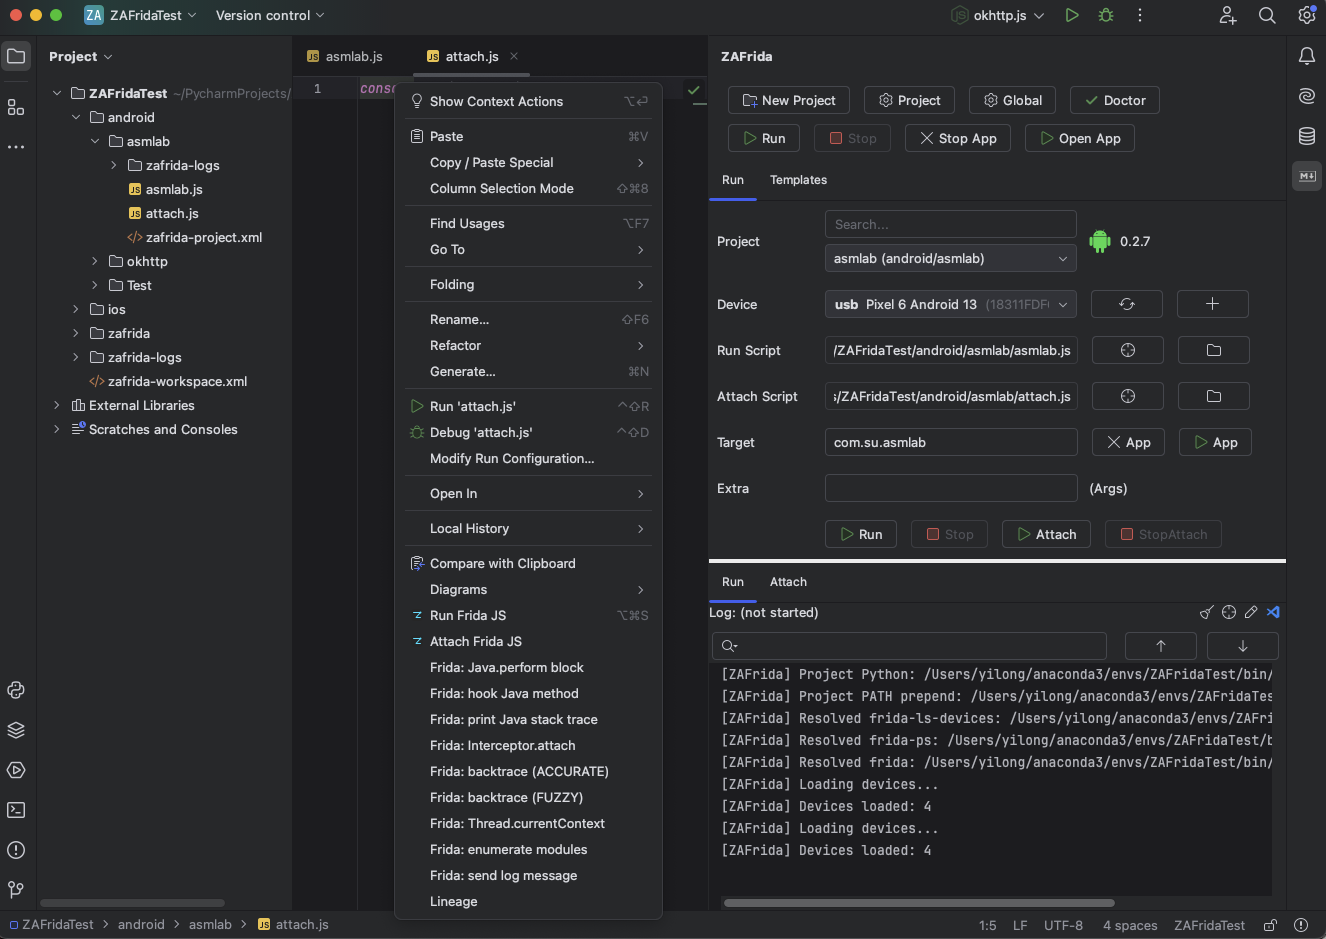 yilongmd/zafrida-ui
A Frida UI tool window inside PyCharm / JetBrains IDEs.
 bytev0rtex/cve-2026-65343
Proof-of-concept for CVE-2026-65343, an out-of-bounds read in AppleKeyStore that leaks kernel pointers to defeat KASLR on iOS 26.6. Includes ACM…
 synacktiv-contrib/cve-2018-4193
exploit for CVE-2018-4193
 jeffssh/cve-2021-30860
Collection of materials relating to FORCEDENTRY
 nightwatchcybersecurity/truegaze
Static analysis tool for Android/iOS apps focusing on security issues outside the source code
 alterakey/trueseeing
Non-decompiling iOS/Android app vulnerability scanner (DC25 demo lab, CB17)