
ghidra2frida
Ghidra extension bridging static and dynamic analysis via Frida, enabling scriptable runtime instrumentation for reverse engineering binaries on…

Ghidra extension bridging static and dynamic analysis via Frida, enabling scriptable runtime instrumentation for reverse engineering binaries on…

Mobile Reconnaissance Framework is a powerful, lightweight and platform-independent offensive mobile security tool designed to help hackers and…

Technical writeup of CVE-2025-24104: an iOS sandbox escape via symlink validation bypass in backup restoration, enabling arbitrary file reads outside…

Mobile app security auditing tool focused on automating SAST analysis, identifying underlying technologies (React Native, Flutter, Xamarin, native),…

iOS Syscall Explorer for IDA 9.X


Kernel info leak Proof of Concept patched in iOS 26.4 / macOS 26.4

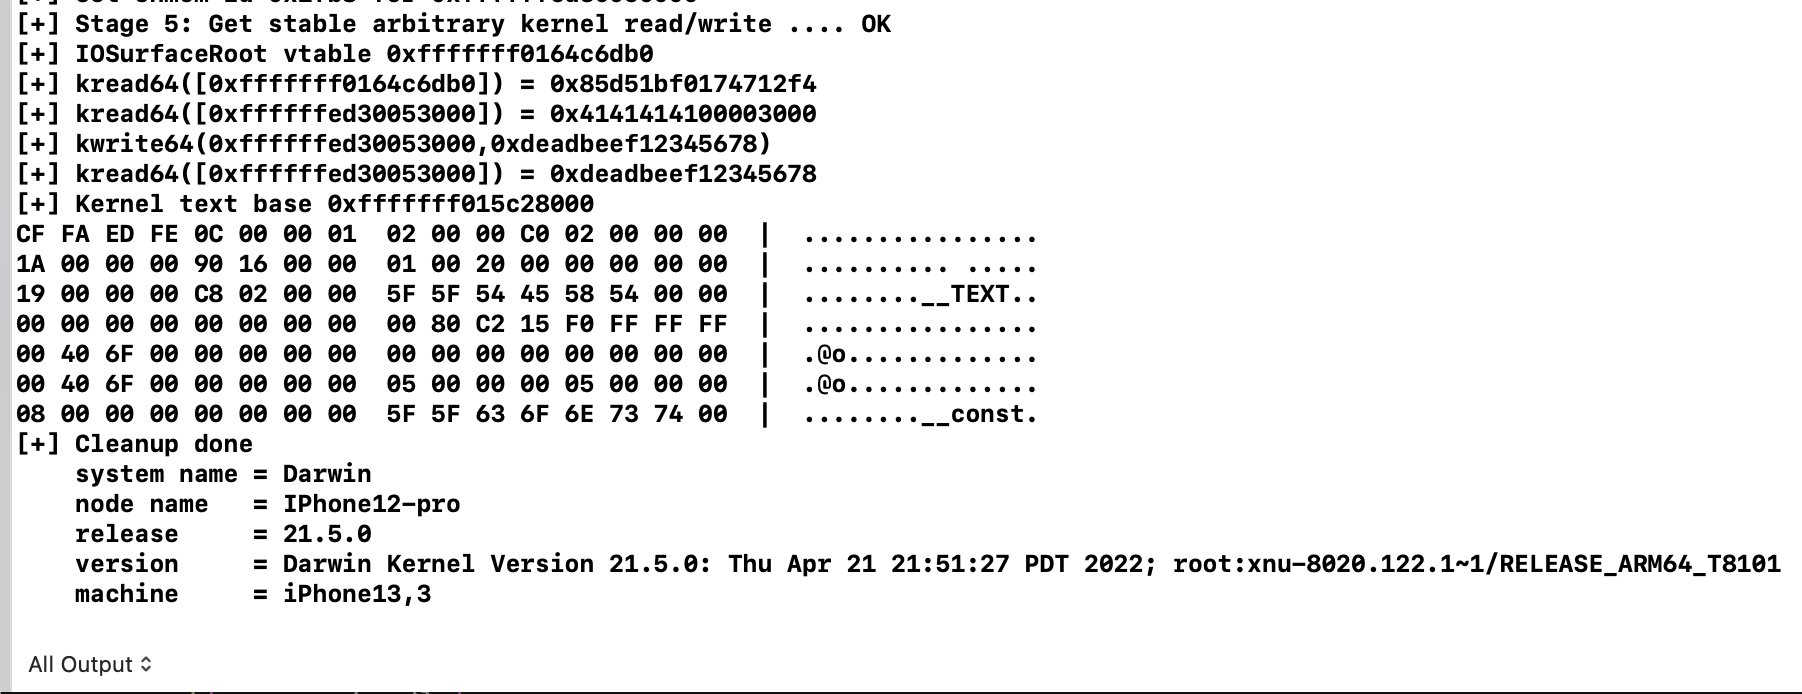
Attempt to steal kernelcredentials from launchd + task_t pointer (Based on: CVE-2017-7047)

CVE-2018-4407,iOS exploit

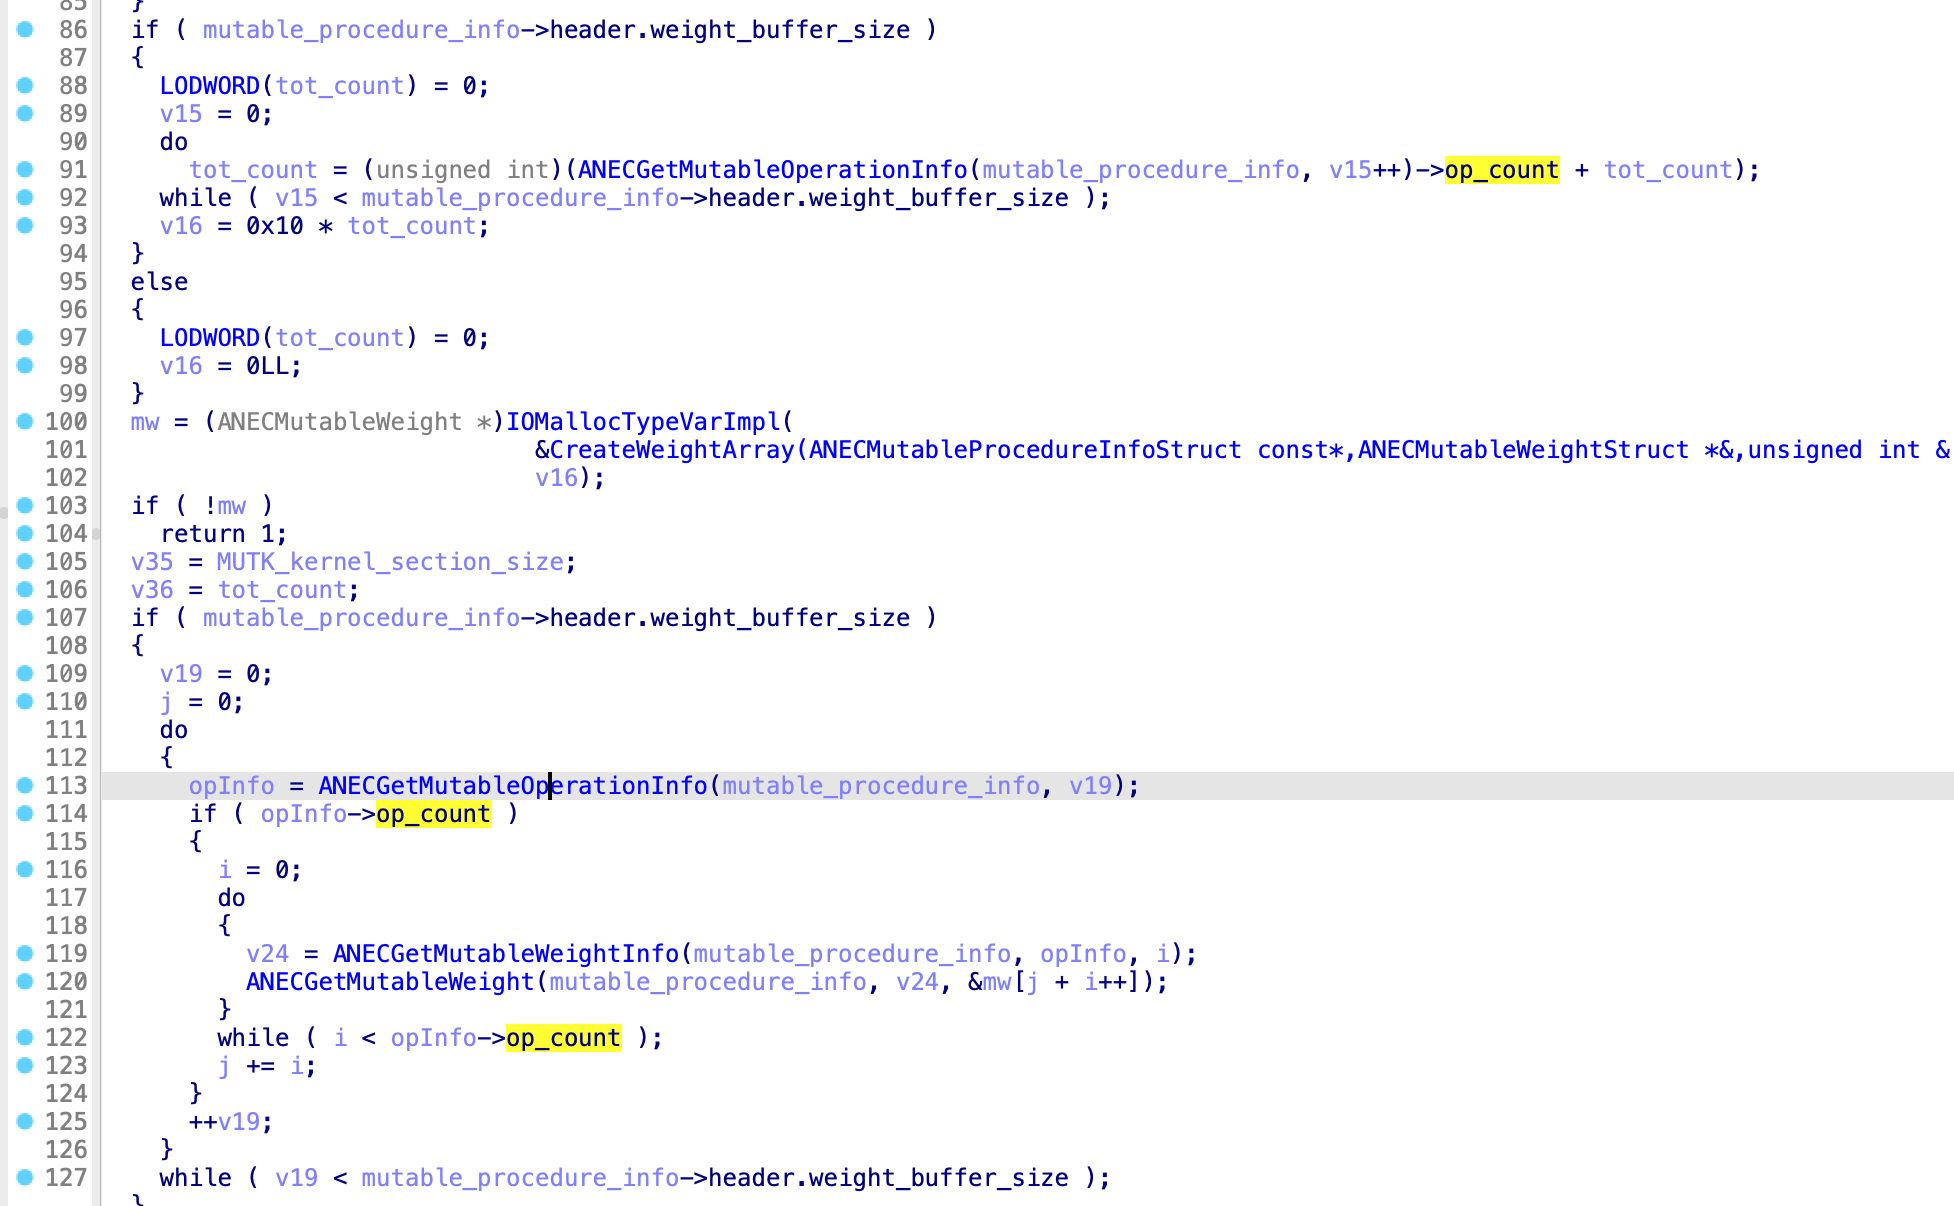
Technical analysis and proof-of-concept for CVE-2022-32932, a double fetch vulnerability in Apple's ANE kernel driver leading to out-of-bounds write…

This is an exploit for CVE-2017-7047, Works on 10.3.2 and below.

Technical analysis and exploit demonstration of CVE-2022-32898, a kernel memory corruption vulnerability in Apple Neural Engine driver, with detailed…

Step-by-step guide to intercepting Android and iOS HTTP/HTTPS traffic with Charles Proxy, covering SSL proxying, CA certificate installation, and…