
ghidra2frida
Ghidra extension bridging static and dynamic analysis via Frida, enabling scriptable runtime instrumentation for reverse engineering binaries on…

Ghidra extension bridging static and dynamic analysis via Frida, enabling scriptable runtime instrumentation for reverse engineering binaries on…

Proof-of-concept for CVE-2023-41992, a macOS kernel vulnerability, demonstrating exploitation techniques and providing a patch analysis.

Exploit analysis for CVE-2014-4378: information disclosure in Apple CoreGraphics via crafted PDF, enabling memory layout leak and bypass of ASLR,…

Static analysis tool for iOS applications that extracts links, API keys, subdomains, binary info, linked libraries, and strings to aid mobile…

Mobile app security auditing tool focused on automating SAST analysis, identifying underlying technologies (React Native, Flutter, Xamarin, native),…

Analysis of public exploits or my 1day exploits

Comprehensive deobfuscated research of the Coruna iOS exploit kit targeting CVE-2024-23222. Analysis of WebKit Type Confusion, PAC Bypass, and…

Research repository detailing exploitation techniques against Apple's Display Co-Processor (DCP), including firmware analysis and hardware-level…

Analysis and PoC for CVE-2025-14174 - ANGLE Metal OOB write (iOS Safari, macOS Chrome)

Frida script that bypasses VMProtect runtime protections on mobile platforms, enabling dynamic instrumentation and analysis of protected binaries.

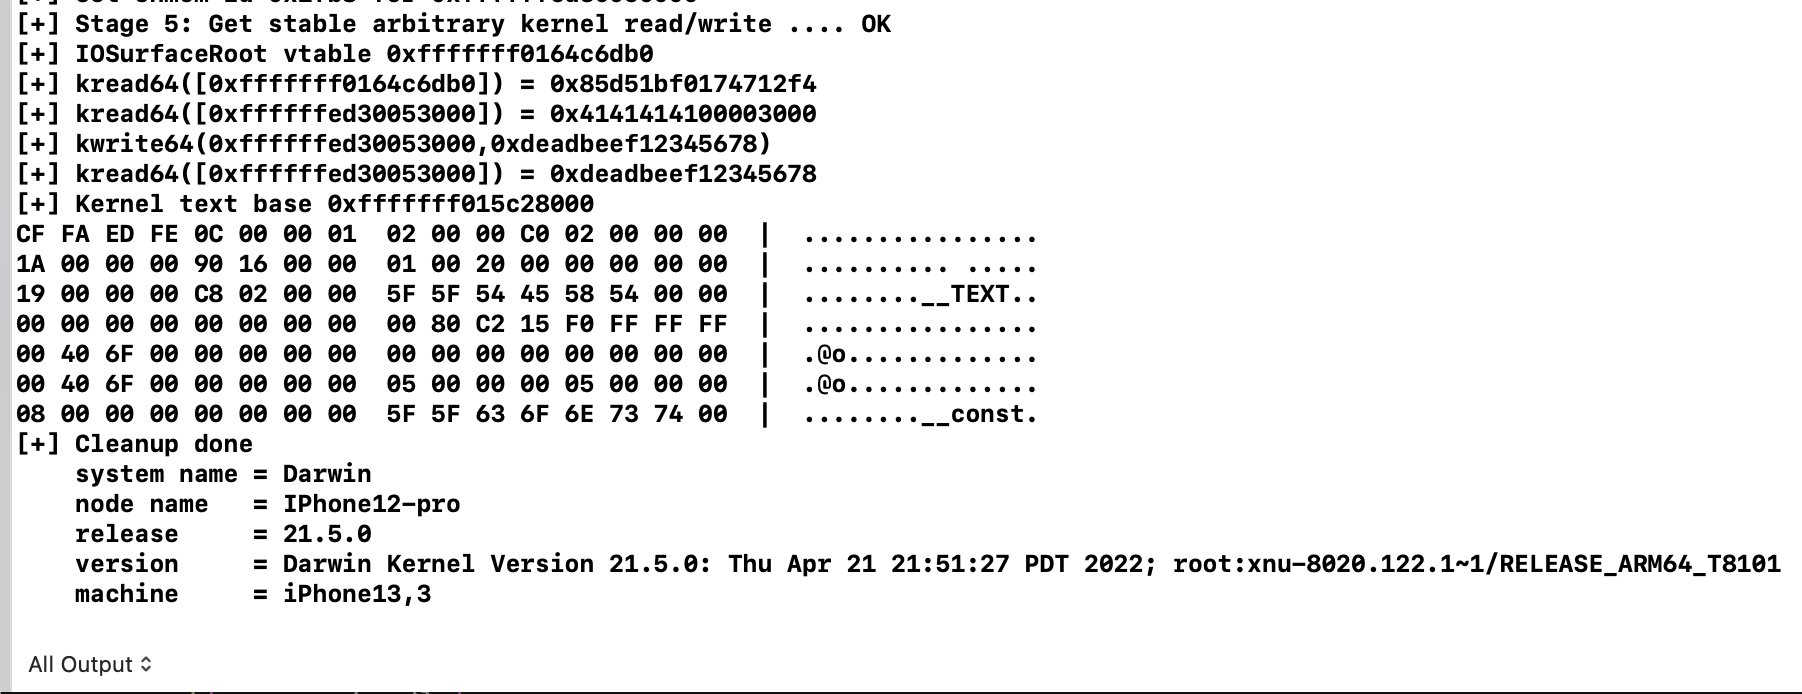
Technical analysis and proof-of-concept for CVE-2022-32932, a double fetch vulnerability in Apple's ANE kernel driver leading to out-of-bounds write…

Static analysis of the DarkSword iOS WebKit exploit chain — delivery, staging, and CVE breakdown (CVE-2025-31277, CVE-2025-43529)

Technical deep-dive into CVE-2025-43504, a remote pre-authentication global buffer overflow in LLDB's debugserver for iOS, with PoC code and…

Proof-of-concept for a stored cross-site scripting (XSS) vulnerability in the URVE Smart Office iOS app, with CVE details, impact analysis, and…

Technical analysis of CVE-2026-28858, a critical buffer overflow in Apple iOS/iPadOS kernel, including exploit flow, mitigation, and defensive coding…

AI powered security analysis extension for Mobile Security Framework MobSF

Technical analysis and exploit demonstration of CVE-2022-32898, a kernel memory corruption vulnerability in Apple Neural Engine driver, with detailed…

OWASP iGoat (Swift) - A Damn Vulnerable Swift Application for iOS