
blanket
 bazad/blanket
CVE-2018-4280: Mach port replacement vulnerability in launchd on iOS 11.2.6 leading to sandbox escape, privilege escalation, and codesigning bypass.
binary-exploitationexploitationios-security+4
262
bazad/blanketCVE-2018-4280: Mach port replacement vulnerability in launchd on iOS 11.2.6 leading to sandbox escape, privilege escalation, and codesigning bypass.
 jgoyd/ios-attack-chain-cve-2025-31200-cve-2025-31201
CVE-2025-31200 is a zero-day, zero-click RCE in iOS CoreAudio’s AudioConverterService, triggered by a malicious audio file via iMessage/SMS.…
 illusionofchaos/ios-nehelper-wifi-info-0day
iOS 15 0-day exploit (still works in 15.0.2)
 owasp/maswe
OWASP enumeration of common security and privacy weaknesses in mobile applications, serving as a reference bridging the MASVS verification standard…
 gabrielg/cve-2014-1266-poc
Proof-of-concept exploit for Apple SSL/TLS verification vulnerability (CVE-2014-1266) in iOS and OS X, demonstrating HTTPS interception via a proxy…
 0xjohnnydev/cve-2026-20637-applesepkeystore-uaf
CVE-2026-20637: AppleSEPKeyStore Use-After-Free — iOS/macOS kernel vulnerability (patched in 26.4)
 bytev0rtex/cve-2026-65343
Proof-of-concept for CVE-2026-65343, an out-of-bounds read in AppleKeyStore that leaks kernel pointers to defeat KASLR on iOS 26.6. Includes ACM…
 amnestytech/inside-pegasus
A curated set of NSO Group internal documents, product materials and sworn testimony that entered the public record in WhatsApp Inc. and Meta…
 yuejd/ios_restriction_passcode_crack---python-version
Crack ios Restriction PassCode in Python
 muirey03/cve-2022-32832
Proof-of-concept and write-up for the CVE-2022-32832 vulnerability patched in iOS 15.6
 billy-ellis/exr-imageio-poc
PoC for CVE-2026-28990, an ImageIO bug patched in iOS/macOS 26.5
 jgoyd/glass-cage-ios18-cve-2025-24085-cve-2025-24201
Glass Cage is a zero-click PNG-based RCE chain in iOS 18.2.1, bypassing LockDown mode protection by exploiting ImageIO (CVE-2025-43300), then…
 stuxctf/mhf
Mobile Helper Framework (mhf) is a tool that automates the process of identifying the framework/technology used to create a mobile application.…
 bazad/gsscred-race
CVE-2018-4331: Exploit for a race condition in the GSSCred system service on iOS 11.2.
 0xjohnnydev/cve-2026-28992-iohidfamily-fastpathuserclient-race-conditions
UAF and AOP coprocessor panic in IOHIDEventServiceFastPathUserClient. No entitlements, reachable from app sandbox.
 robertmak2014-sudow/cve-2026-28995
# CVE-2026-28995 Proof of Concept for CVE-2026-28995 — Path Traversal vulnerability in App Intents on iOS 26.4.2 and below.
 jgoyd/ios18.6.2-persistent-automation-exploit-in-siri-shortcuts-and-apple-swc
This repo documents a vulnerability in Siri Shortcuts and Shared Web Credentials (SWC) allowing malformed payloads to persistently execute, trigger…
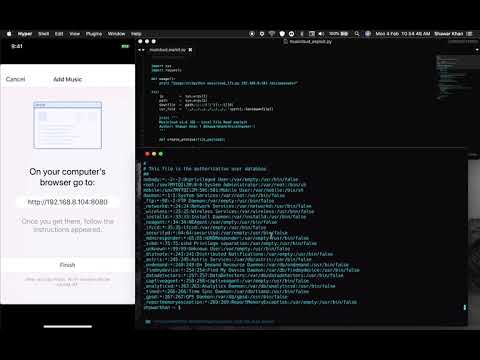 shawarkhanethicalhacker/cve-2019-8389
[CVE-2019-8389] An exploit code for exploiting a local file read vulnerability in Musicloud v1.6 iOS Application