

LIEF
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
ai-assisted-reversingandroid-securitybinary-analysis+12
5.5k
lief-project/liefCross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
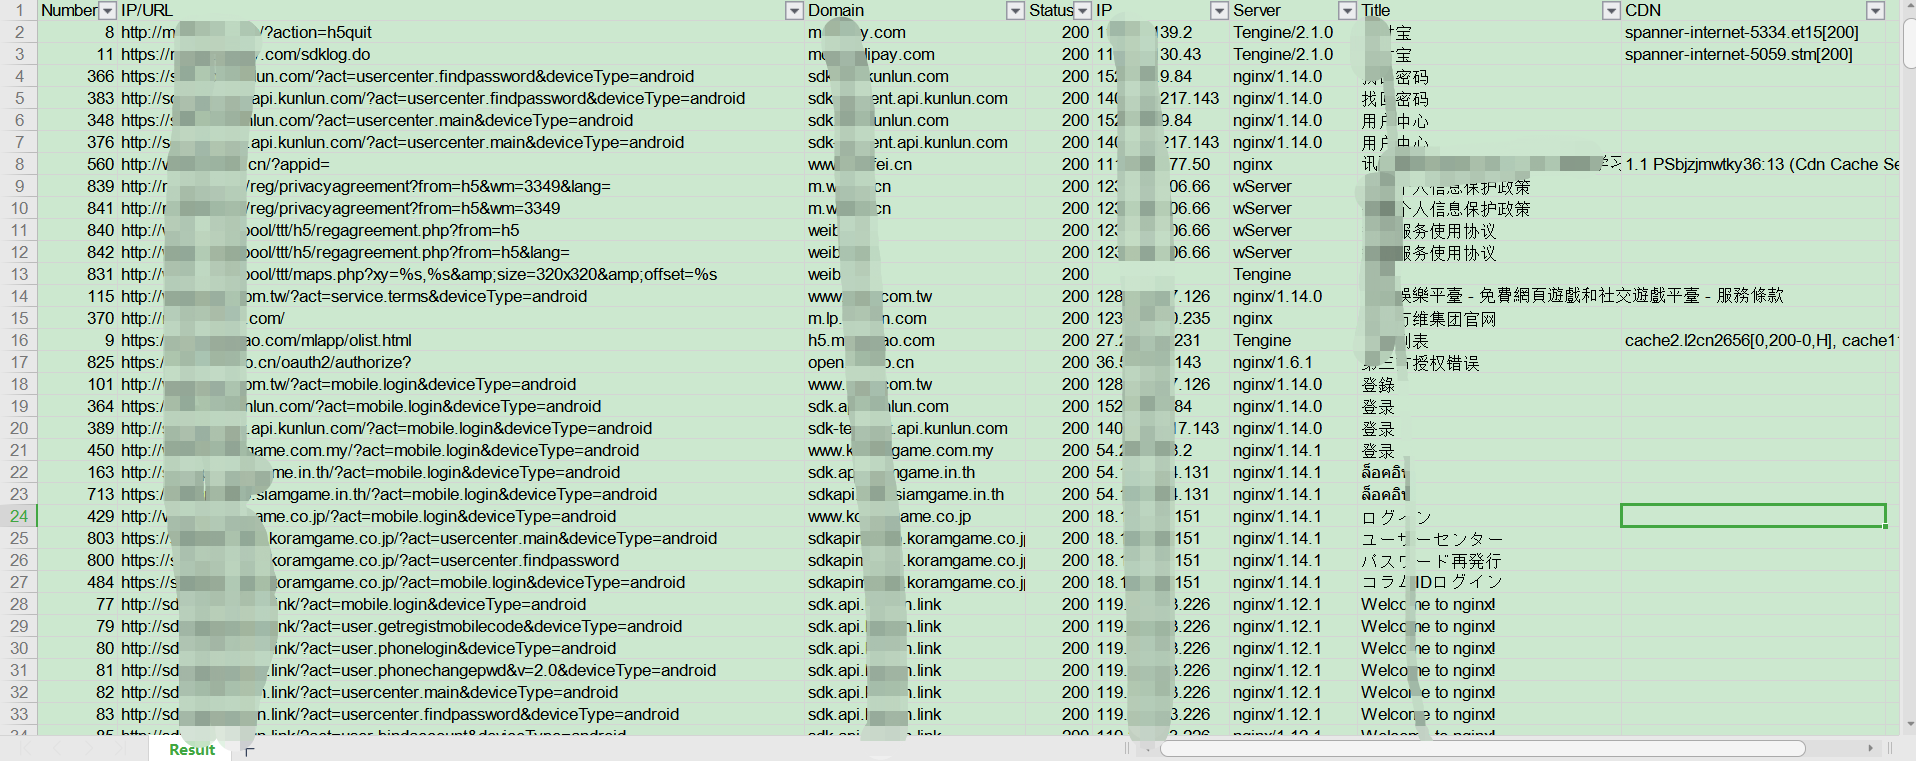 kelvinben/appinfoscanner
一款适用于以HW行动/红队/渗透测试团队为场景的移动端(Android、iOS、WEB、H5、静态网站)信息收集扫描工具,可以帮助渗透测试工程师、攻击队成员、红队成员快速收集到移动端或者静态WEB站点中关键的资产信息并提供基本的信息输出,如:Title、Domain、CDN、指纹信息、状态信息等。
 vaib25vicky/awesome-mobile-security
An effort to build a single place for all useful android and iOS security related stuff. All references and tools belong to their respective owners.…
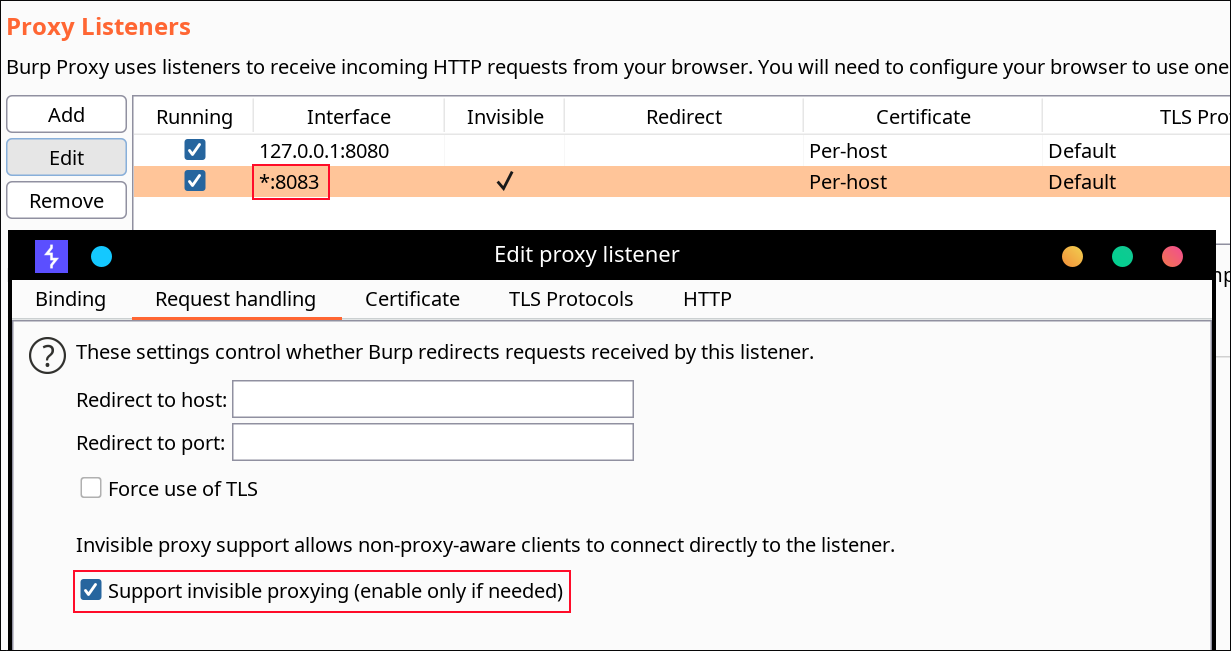 impact-i/reflutter
Patches Flutter engine libraries to enable runtime reverse engineering, traffic interception, and SSL pinning bypass for Android and iOS apps without…
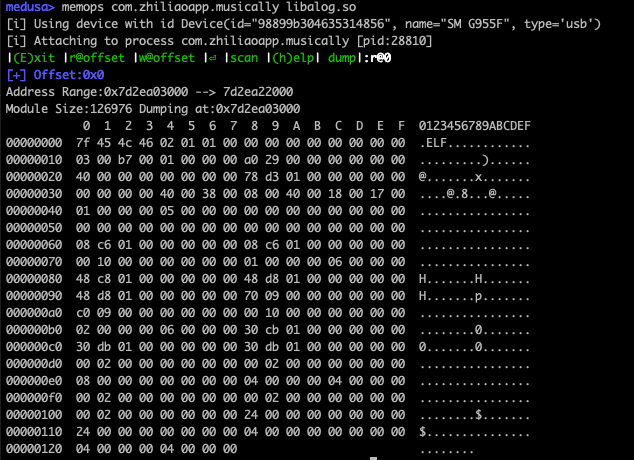 ch0pin/medusa
Mobile Edge-Dynamic Unified Security Analysis
 owasp/masvs
The OWASP MASVS (Mobile Application Security Verification Standard) is the industry standard for mobile app security.
 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
 iddoeldor/frida-snippets
Hand-crafted Frida examples
 m0bilesecurity/rms-runtime-mobile-security
Runtime Mobile Security (RMS) 📱🔥 - is a powerful web interface that helps you to manipulate Android and iOS Apps at Runtime
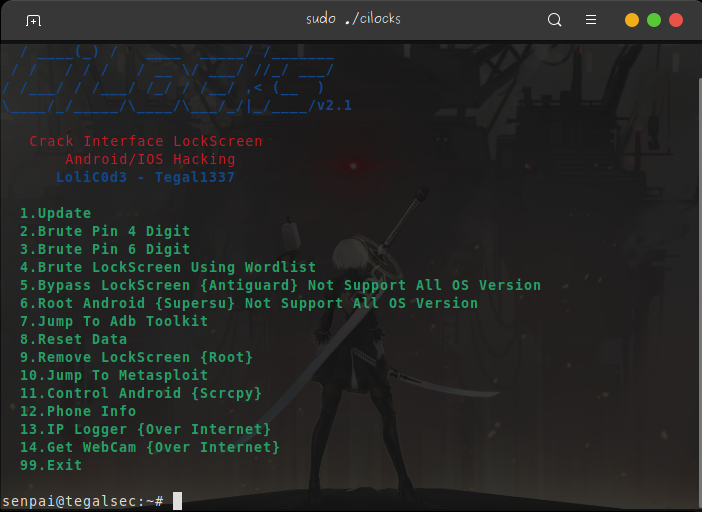 tegal1337/cilocks
Crack Interface lockscreen, Metasploit and More Android/IOS Hacking
 yjeanrenaud/yj_nearbyglasses
attempting to detect smart glasses nearby and warn you
 0xdea/frida-scripts
A collection of my Frida instrumentation scripts to reverse engineer mobile apps and more.
 nowsecure/r2frida
Radare2 and Frida better together.
 hahwul/mobilehackersweapons
Mobile Hacker's Weapons / A collection of cool tools used by Mobile hackers. Happy hacking , Happy bug-hunting
 igio90/dwarf
Full featured multi arch/os debugger built on top of PyQt5 and frida
 federicodotta/brida
The new bridge between Burp Suite and Frida!
 mobsf/mobsfscan
mobsfscan is a static analysis tool that can find insecure code patterns in your Android and iOS source code. Supports Java, Kotlin, Swift, and…
 nowsecure/fsmon
Filesystem monitor tool for Linux/Android iOS/macOS