

rasp
 ostorlab/rasp
Packs a runtime into built APK, AAB or IPA files to detect root, jailbreak, debuggers, Frida hooks, emulators, VPN/proxy interception and repackaging…
android-securityanti-botbinary-analysis+6
ostorlab/raspPacks a runtime into built APK, AAB or IPA files to detect root, jailbreak, debuggers, Frida hooks, emulators, VPN/proxy interception and repackaging…
 msuiche/hotcell
Runtime exploit monitor for Apple document/image pipelines (iOS/macOS) — EXPMON concept: Frida agent + behavioral rules. First target: the…
 doronz88/harlogger
Simple utility for sniffing decrypted HTTP/HTTPS traffic on a macOS/iOS device (either jailbroken or not)
 xv4l3x/hermit
Inspects, decompiles and structurally patches Hermes bytecode (HBC) from React Native apps, with a GDB-style REPL, CFG, decompiler and re-serializing…
 gmh5225/frida-il2cpp-datacollector
Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…
 vighnesh91/ipaforge
Dependency-free Python CLI to unpack, inspect, edit, and rebuild iOS .ipa archives, converting plists and strings to XML while preserving Mach-O…
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
 alonemonkey/frida-ios-dump
Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
 jwalker/frida-ios-dump-modern
An updated Frida iOS dump tool supporting the latest Frida 17.5.2 APIs
 abrignoni/ileapp
Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
 tanprathan/mobileapp-pentest-cheatsheet
The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…

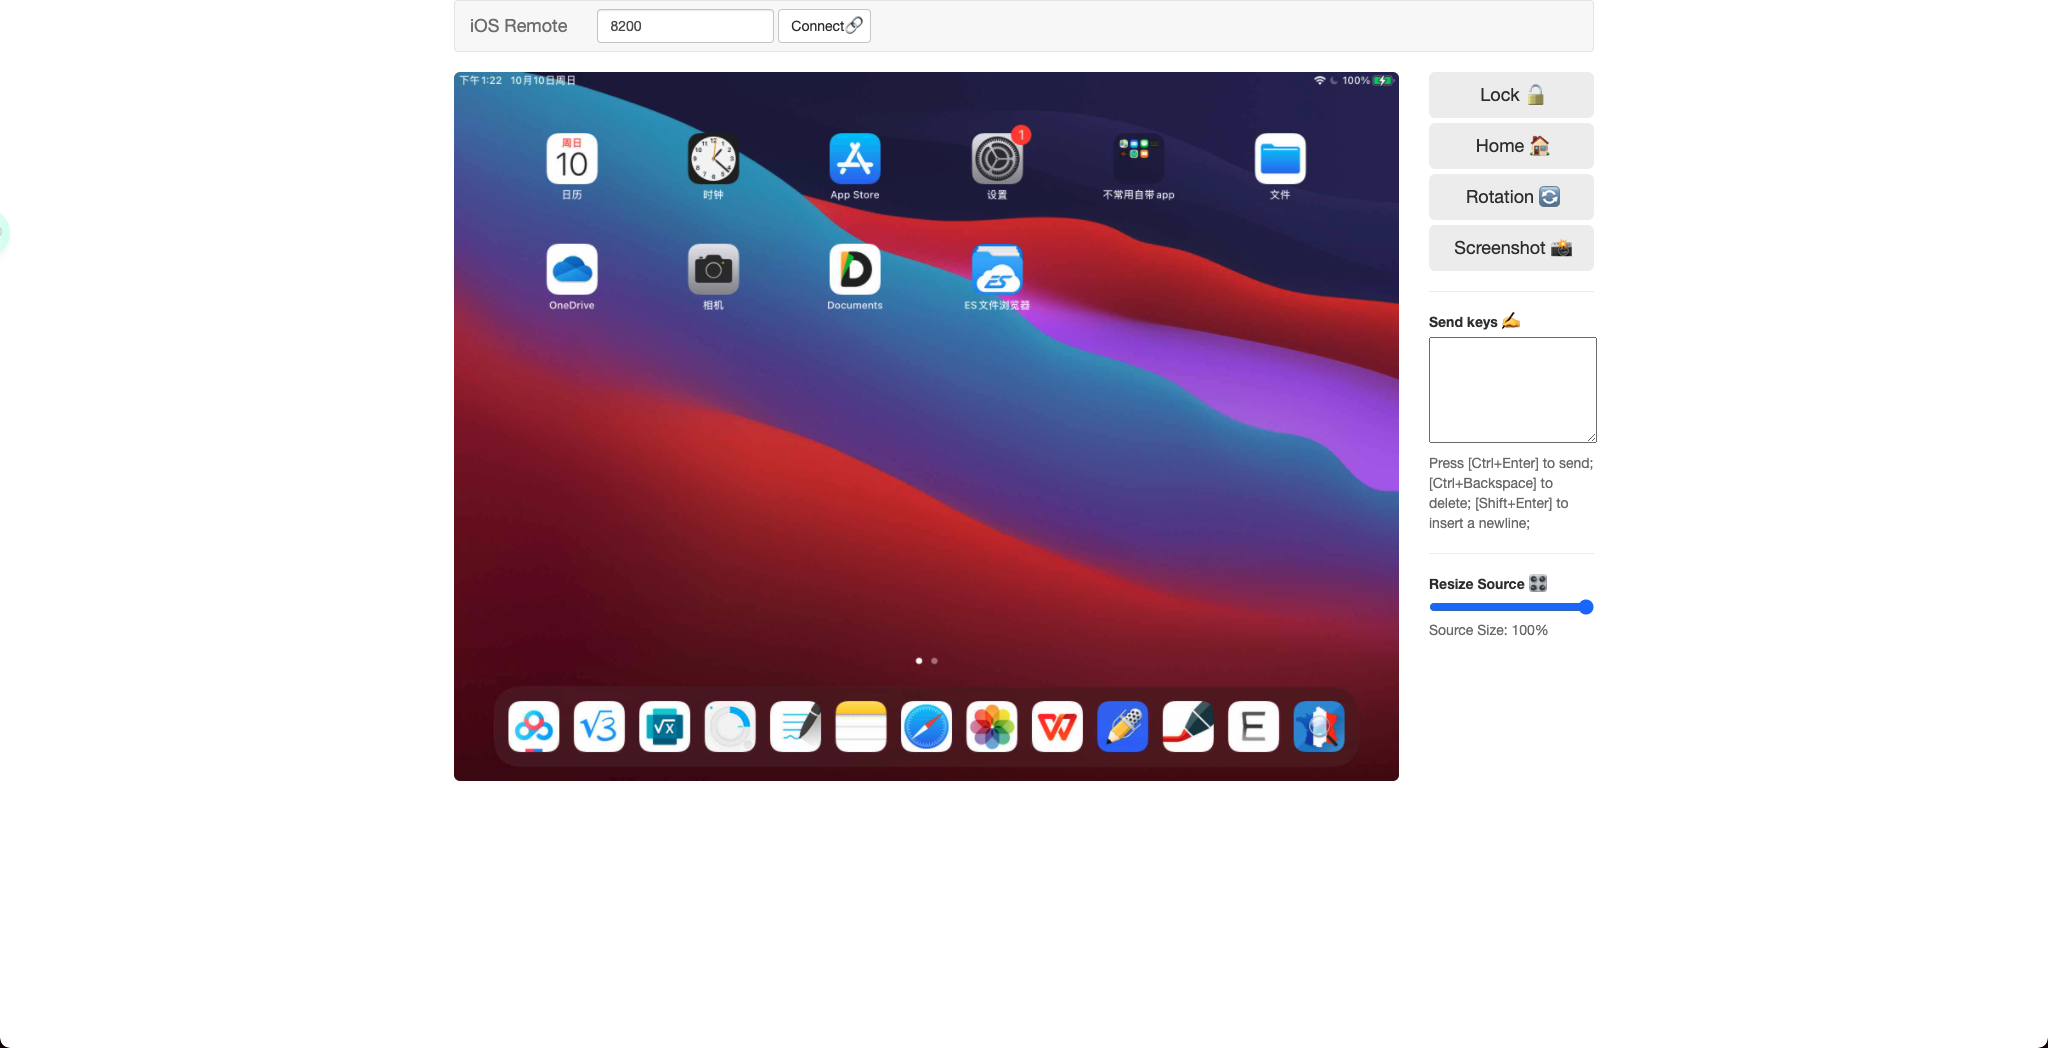 dimcyan/ios-remote
Display and control your iOS device
 george0papasotiriou/cve-2026-6666-xpc-service-nskeyedunarchiver-deserialization-attack-macos-ios-simulation-
Simulated macOS/iOS XPC service vulnerable to NSKeyedUnarchiver deserialization, plus exploit demonstration and crafted plist payload for RCE via…
 userlandkernel/usbusted
Research on Apple's USB protocols
 isecpartners/introspy-ios
Security profiling for blackbox iOS
 l3onkers/fuxios
Modernized Python 3 exploit PoC for CVE-2016-4631 targeting iOS devices. Features network scanning, malformed IP/TCP payload generation, and packet…
 zteeed/cve-2018-4407-ios
POC: Heap buffer overflow in the networking code in the XNU operating system kernel