Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
211 results
Incident-Response-Powershell preview

Incident-Response-Powershell

GitHubbert-janp/incident-response-powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

digital-forensicsdisk-forensicsforensics+6
823

4 months ago
artillery preview

artillery

GitHubtrustedsec/artillery

Open-source blue team tool that protects Linux and Windows systems using multiple host and network defense and detection methods.

anomaly-detectiondefensive-toolshardware-iot-security+5
3396 years ago
ioc-finder preview

ioc-finder

GitHubfhightower/ioc-finder

Simple, effective, and modular package for parsing observables (indicators of compromise (IOCs), network data, and other, security related…

ioc-managementmalware-analysisthreat-intelligence+1
1847 days ago
CAPEsolo preview

CAPEsolo

GitHubcapesandbox/capesolo

Standalone Windows VM malware sandbox running capemon, with GUI triage viewer, YARA signatures, IOC extraction, network analysis, and…

defensive-toolsdynamic-analysis-sandboxingforensics+7
6121 days ago
loki-parse preview

loki-parse

GitHubr3mrum/loki-parse

A python script that can detect and parse loki-bot (malware) related network traffic. This script can be helpful to DFIR analysts and security…

data-exfiltrationdigital-forensicsforensics+5
139 years ago
Mortimer preview

Mortimer

GitHubnccgroup/mortimer

A collection of scripts for processing network forensics type data and intelligence, mainly into a postgres database.

forensicsioc-managementlog-analysis+3
1212 years ago
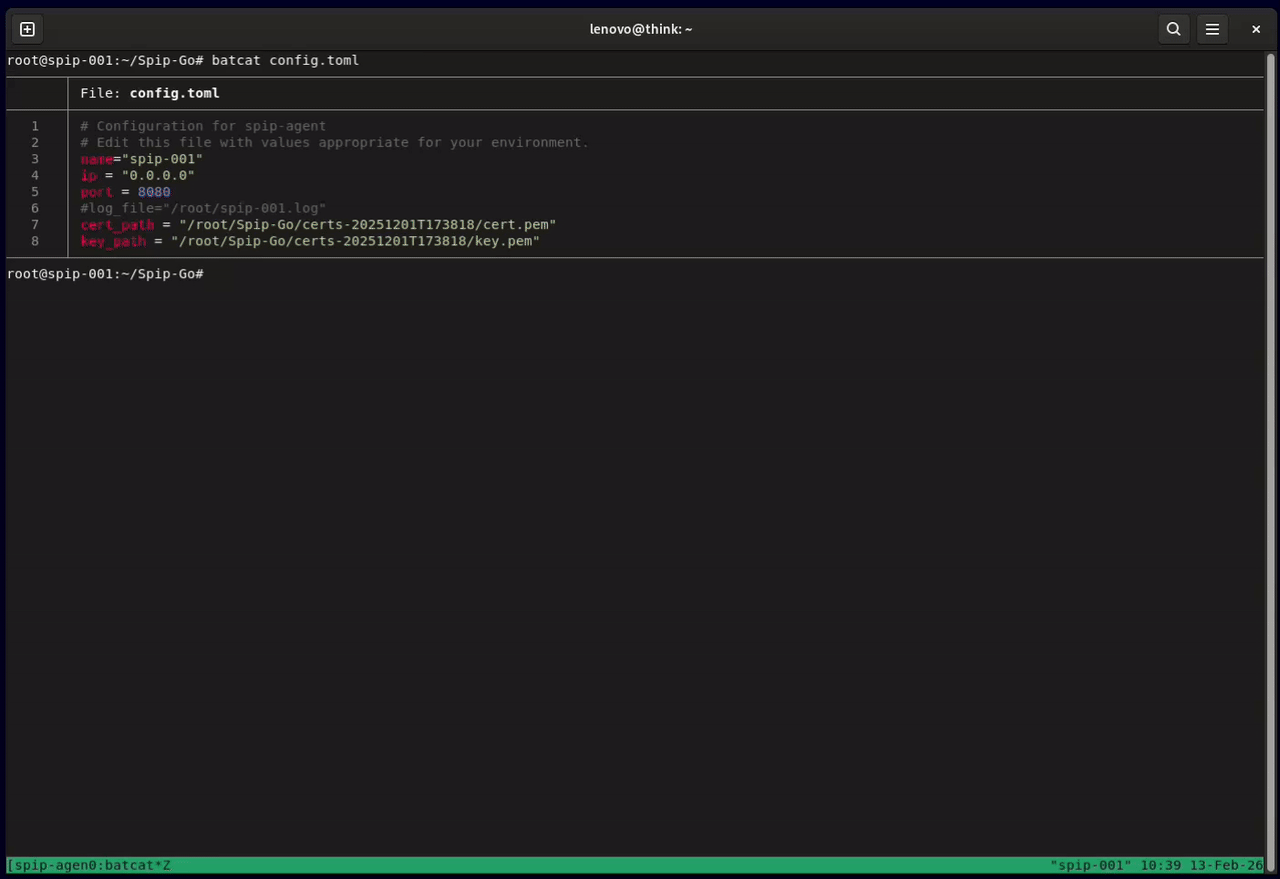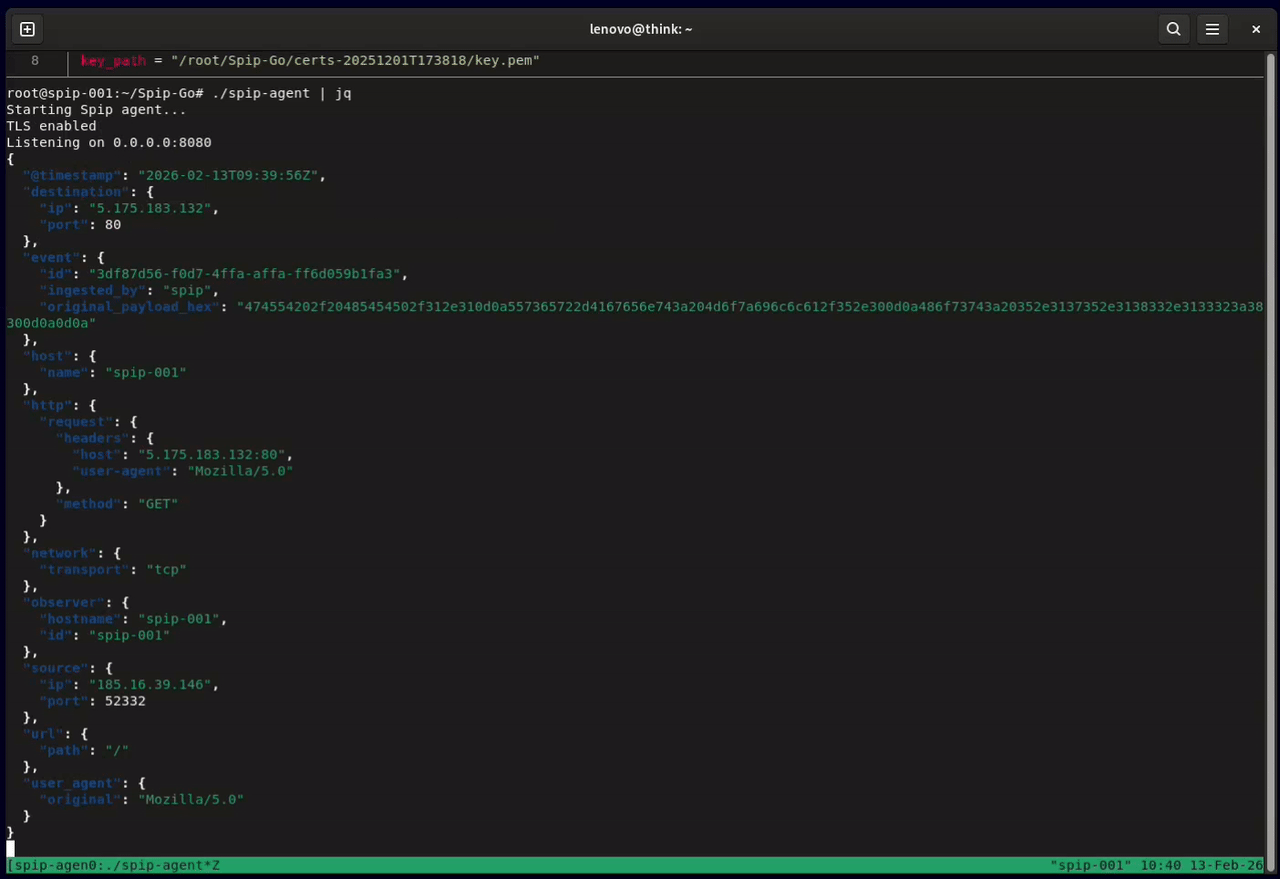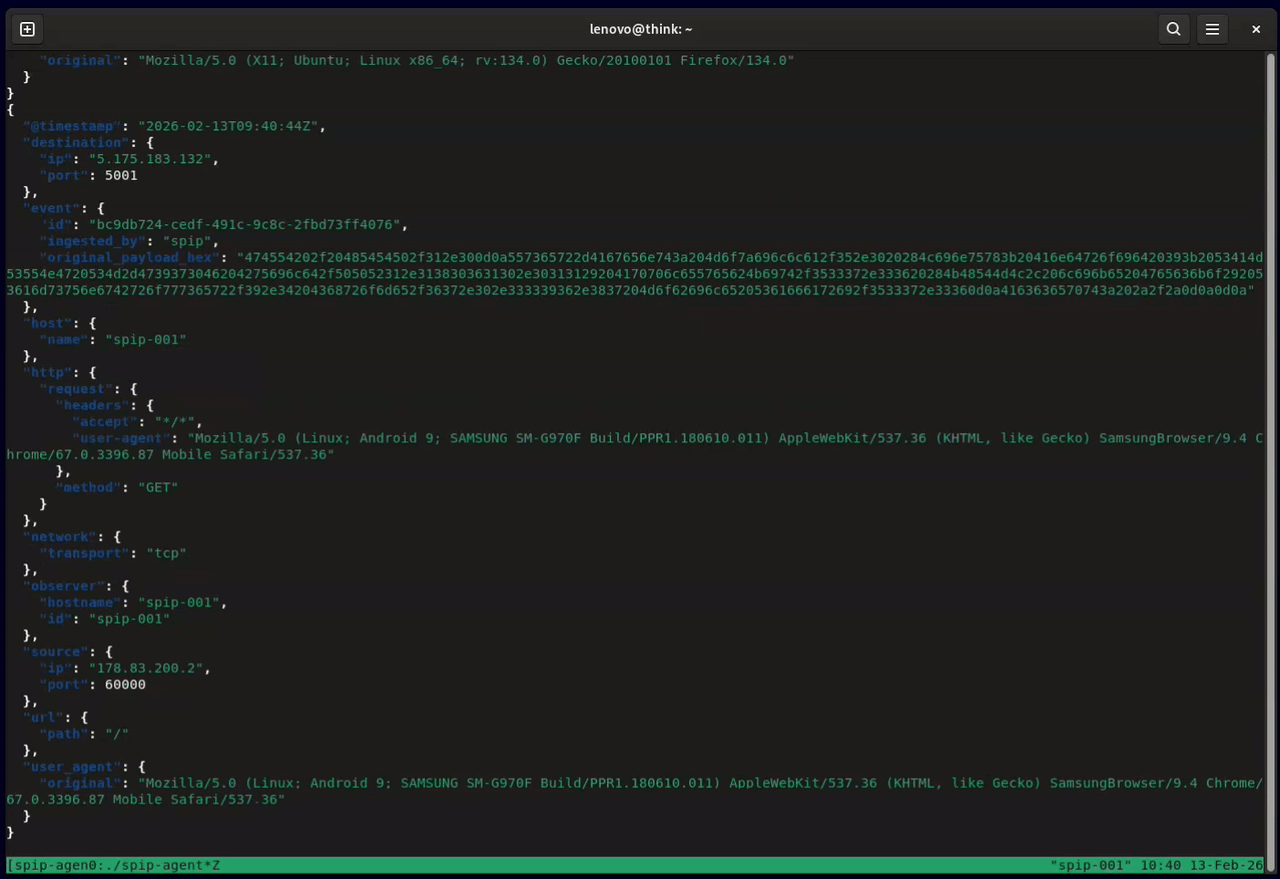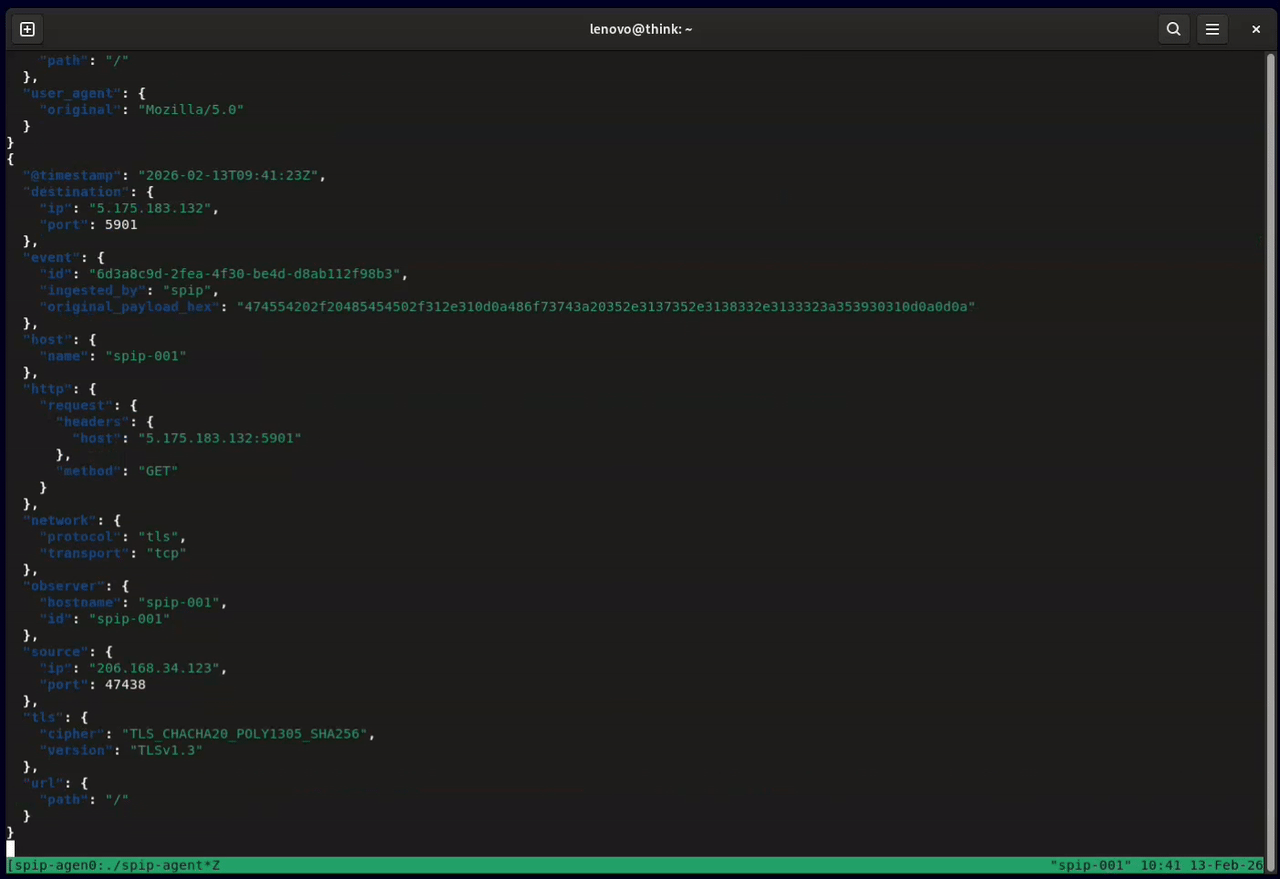
Spip-Go preview

Spip-Go

GitHubhoneylabshq/spip-go

Spip network sensor written in Go

defensive-toolsincident-responseinformation-gathering+7
83 days ago
citrix-netscaler-cve-2026-88771-iocs preview

citrix-netscaler-cve-2026-88771-iocs

GitHubwatchtowrlabs/citrix-netscaler-cve-2026-88771-iocs

Indicators of Compromise and hunting guidance for CVE-2026-88771, an unauthenticated command injection in Citrix NetScaler ADC and Gateway, covering…

command-and-controldefensive-toolsincident-response+5
16 days ago
exim-cve-2019-10149-data preview

exim-cve-2019-10149-data

GitHubcloudflare/exim-cve-2019-10149-data

Curated dataset of IPs, ASNs, and SMTP banners for Exim CVE-2019-10149, with linked advisories and threat actor intelligence for vulnerability…

curated-resourcesinformation-gatheringioc-management+3
36 months ago
security-vulnerability-in-Microsoft-Office. preview

security-vulnerability-in-Microsoft-Office.

GitHubahmed-tarek22752/security-vulnerability-in-microsoft-office.

Blue-team analysis of a malicious DOCX exploiting CVE-2017-0199, covering sandbox detonation, network forensics, IOC extraction, MITRE ATT&CK…

digital-forensicseducationincident-response+6
210 days ago
NetScope preview

NetScope

GitHubspectralzero/netscope

Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…

anomaly-detectiondigital-forensicsincident-response+5
42 months ago
Windows-Defender-Security-Auditor-CVE-2026-50656- preview

Windows-Defender-Security-Auditor-CVE-2026-50656-

GitHubeh-amish/windows-defender-security-auditor-cve-2026-50656-

Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…

configuration-auditingdefensive-toolsincident-response+8
12 months ago
Zeek-CVE-Enrichment preview

Zeek-CVE-Enrichment

GitHubcorelight/zeek-cve-enrichment

Zeek script and Python utility to enrich network security monitoring logs with CVE identifiers for improved threat intelligence and vulnerability…

incident-responseioc-managementlog-analysis+3
12 years ago
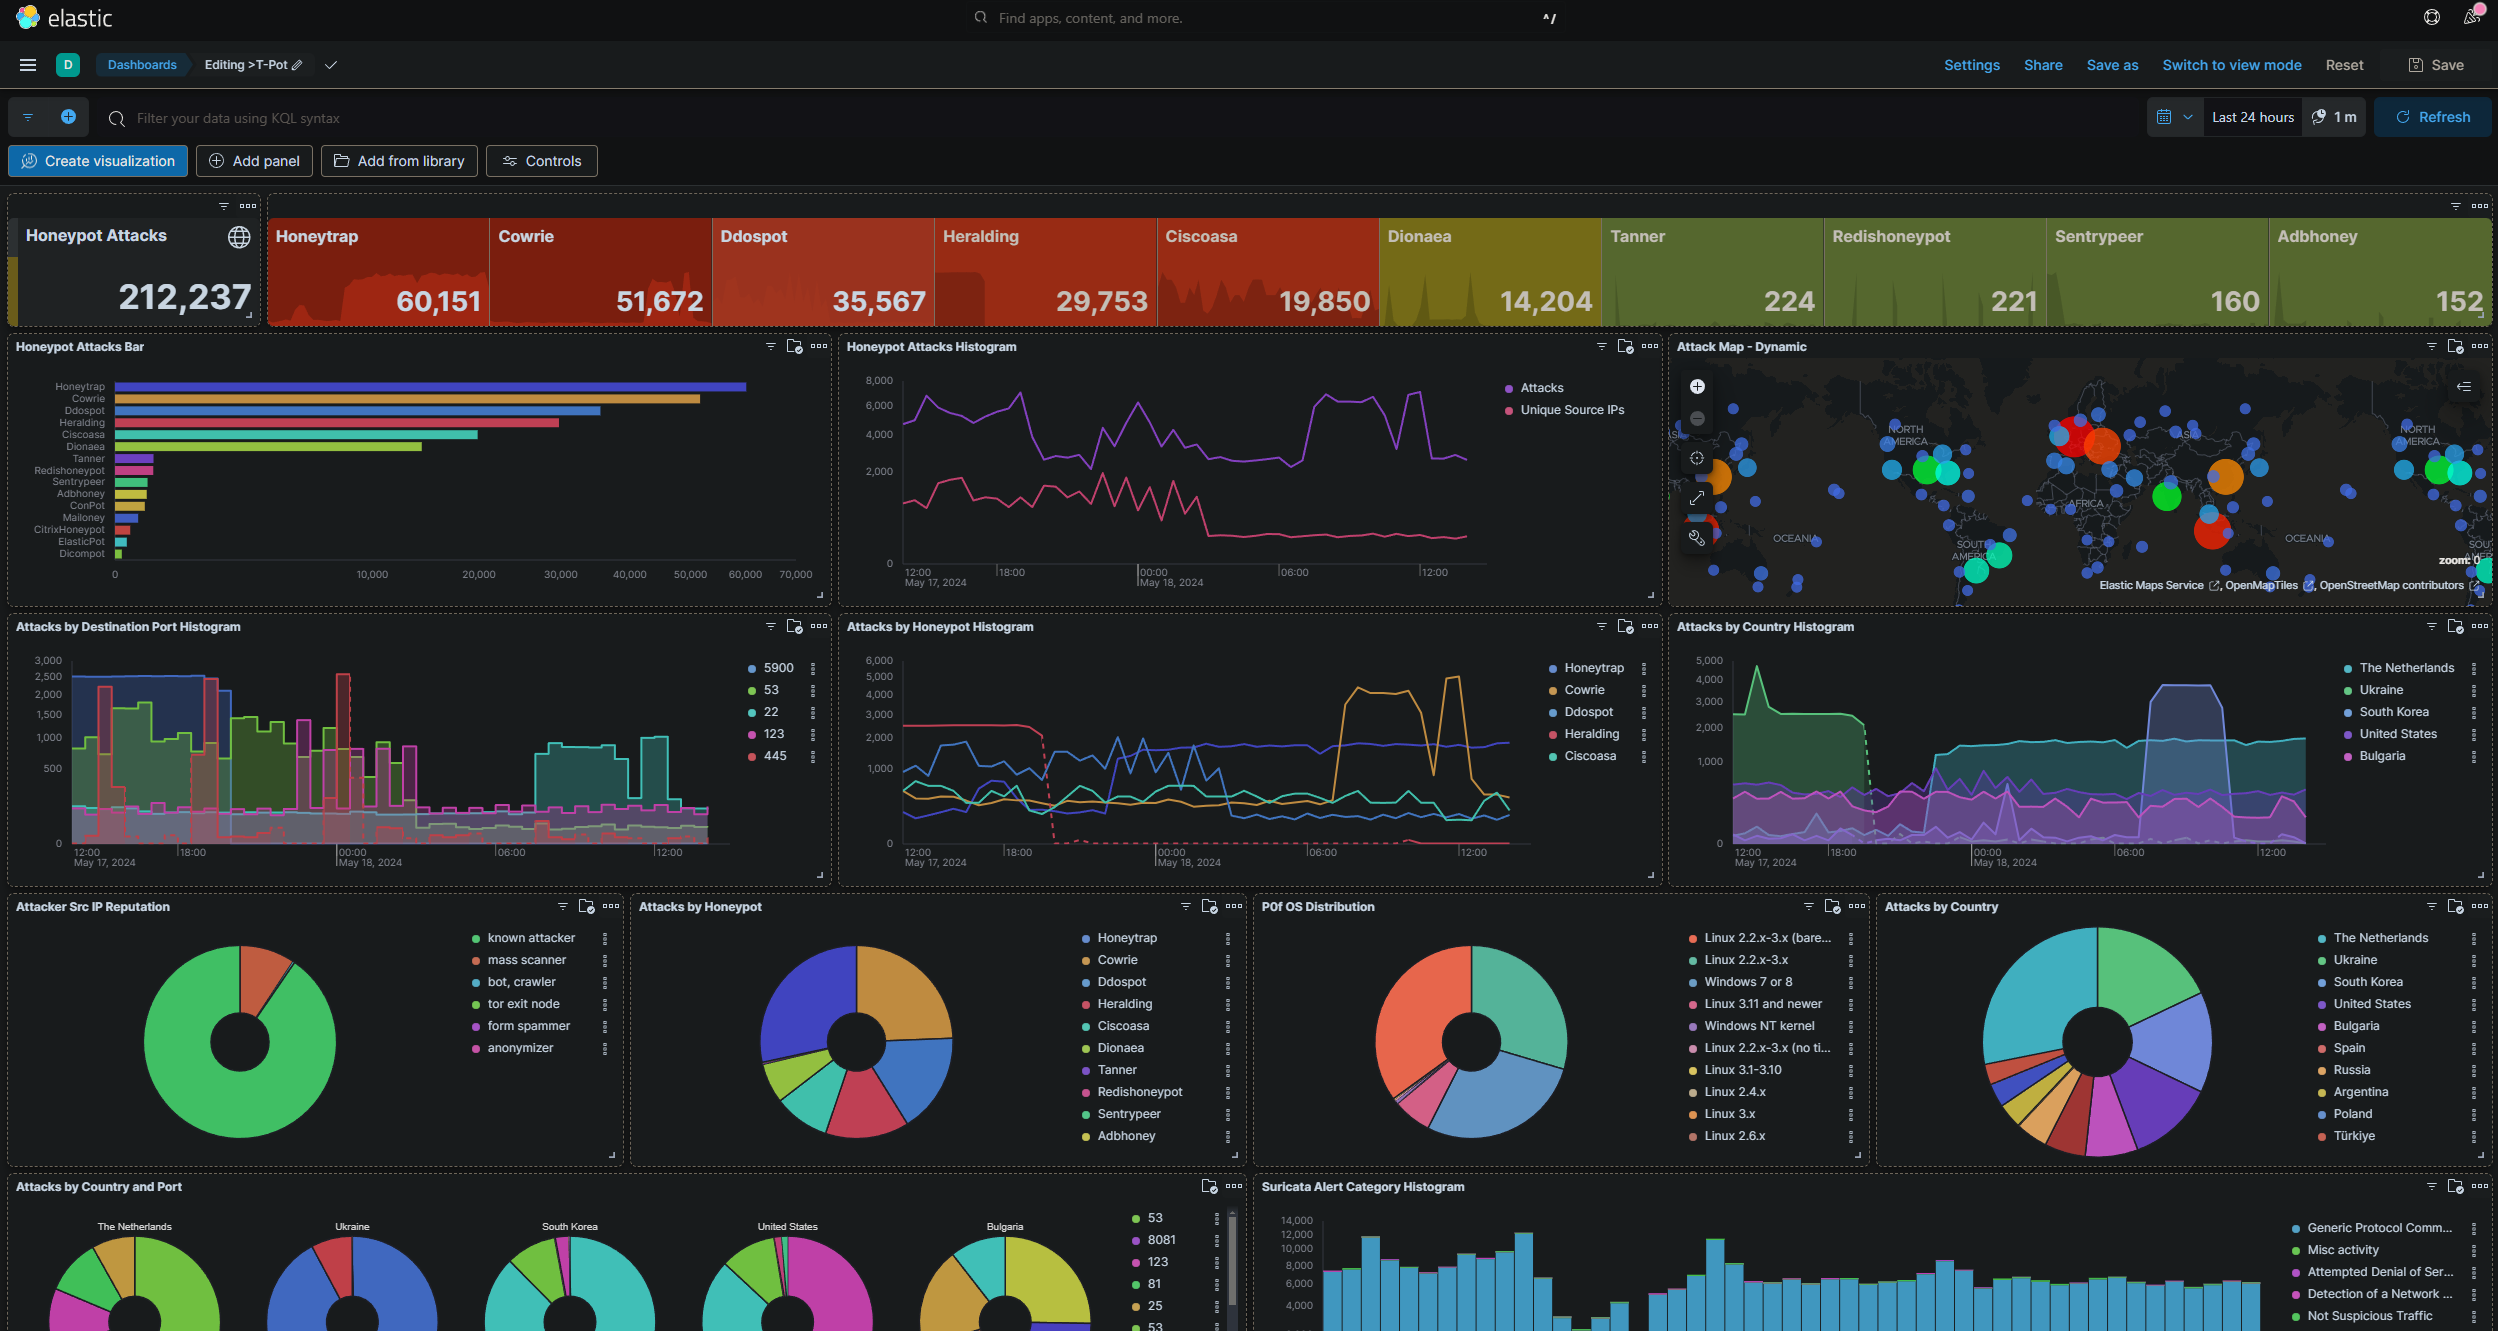
honeypot preview

honeypot

GitHubrxerium/honeypot

🍯Honeypot Threat Intel

defensive-toolsintrusion-detectionioc-management+4
11 year ago
Log4j_Attacker_IPList preview

Log4j_Attacker_IPList

GitHubc3-h2/log4j_attacker_iplist

Curated list of attacker IP addresses targeting the Log4j vulnerability (CVE-2021-44228) for threat intelligence, incident response, and network…

information-gatheringioc-managementlog-analysis+2
4 years ago
qub-network-security-cve-2023-20198 preview

qub-network-security-cve-2023-20198

GitHubdominic471/qub-network-security-cve-2023-20198

Analysis, detection, and mitigation of CVE-2023-20198 exploitation in Cisco IOS XE – QUB CSC3064 Network Security Assessment

educationexploitationids-ips-evasion+6
1 year ago
hassh preview
Archived

hassh

GitHubsalesforce/hassh

HASSH is a network fingerprinting standard which can be used to identify specific Client and Server SSH implementations. The fingerprints can be…

anomaly-detectionforensicsincident-response+5
5541 year ago
maltrail preview

maltrail

GitHubstamparm/maltrail

Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…

anomaly-detectionanti-botdefensive-tools+11
8.6k12h 3m ago
Previous12…12Next