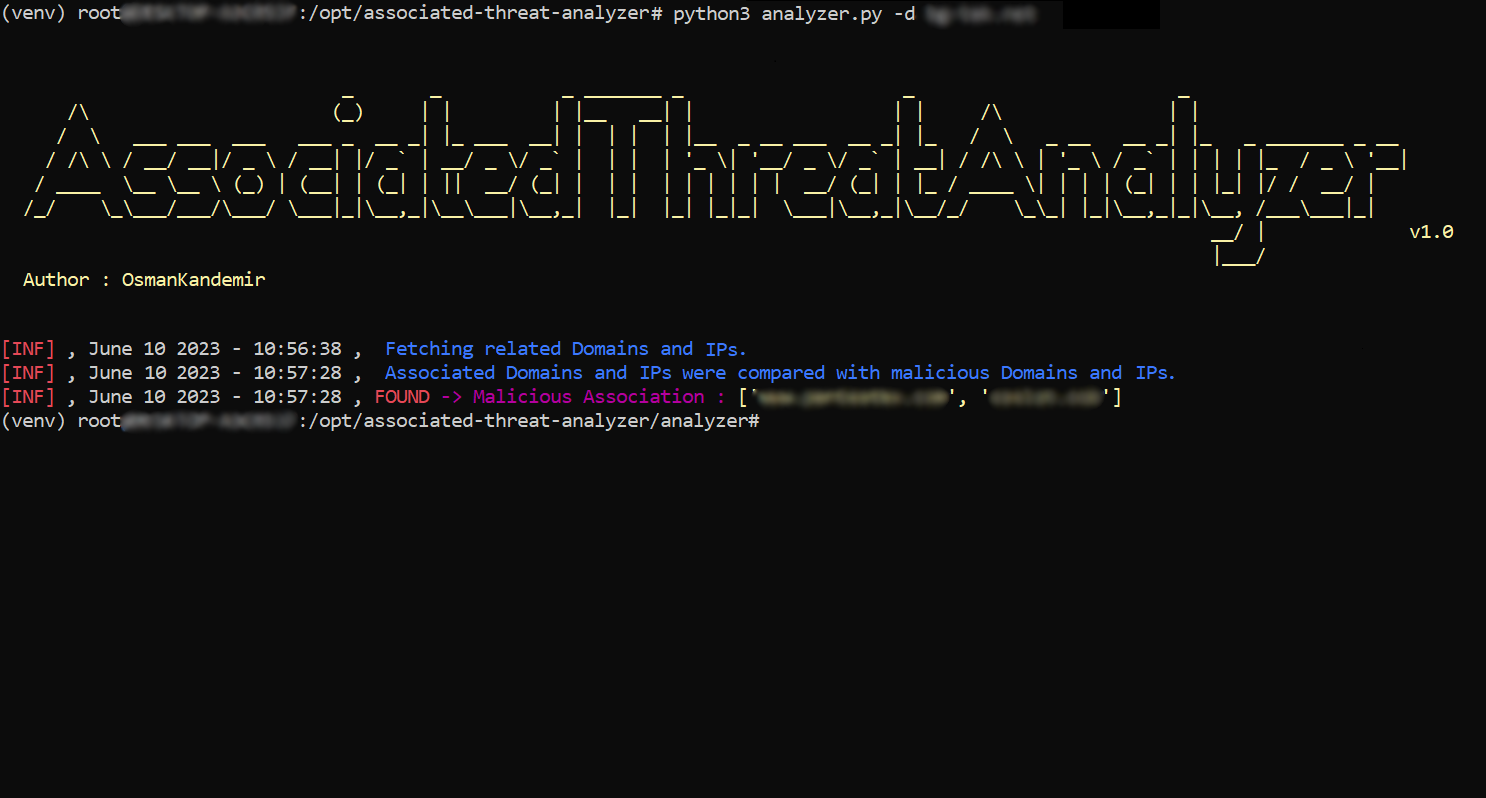
associated-threat-analyzer

Detects malicious IPv4 addresses and domain names associated with a web application by comparing against local threat intelligence lists of known…

Detects malicious IPv4 addresses and domain names associated with a web application by comparing against local threat intelligence lists of known…

This is a webshell fingerprinting scanner designed to identify implants on Cisco IOS XE WebUI's affected by CVE-2023-20198 and CVE-2023-20273

This repository contains informaion about the Fortigate firewall vulnerability (CVE-2022-40684) and affected data that were publicly disclosed by the…

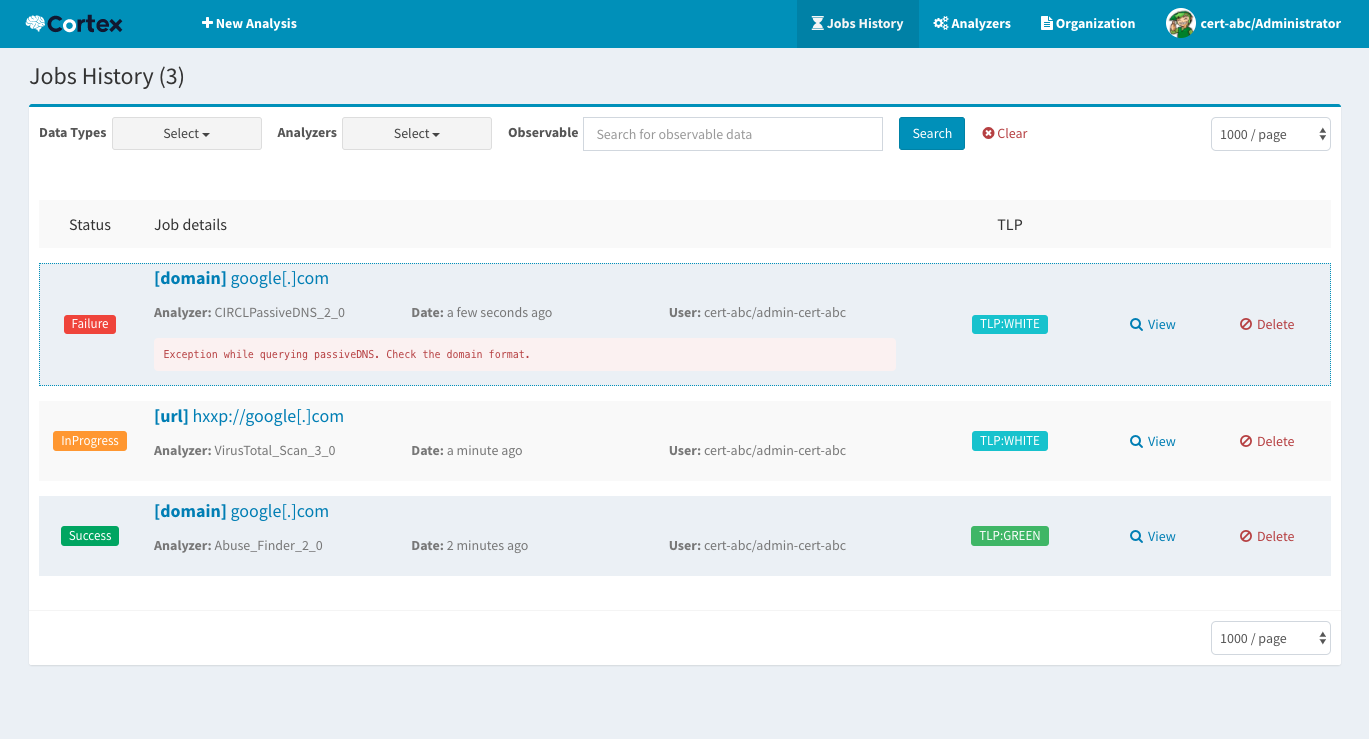
Cortex: a Powerful Observable Analysis and Active Response Engine

Read-only WordPress User Registration CVE-2026-1492 checker for hidden admins, plugin version, uploads PHP, cron, and compromise IOCs.

Indicators of Compromise and hunting guidance for CVE-2026-88771, an unauthenticated command injection in Citrix NetScaler ADC and Gateway, covering…

Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…

IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…

Curated catalog of Remote Monitoring and Management tools abused by threat actors, with YAML profiles, Sigma detection rules, and API access for…

Threat Intel IoCs + bits and pieces of dark matter. Published by Gen Threat Labs.

Taxonomies used in MISP taxonomy system and can be used by other information sharing tool.

A security-first MCP server that empowers AI agents to perform automated reverse engineering, malware analysis, forensics, vulnerability research,…

Curated public database of indicators of compromise aggregated by Wiz Research for threat detection, hunting, and incident response workflows.

Repository created to share information about tactics, techniques and procedures used by threat actors. Initially with ransomware groups and evolving…

Detects GlassWorm supply chain attack payloads by scanning VS Code extensions, npm/PyPI packages, and git repos for invisible Unicode payloads,…

Public repository of Sigma and YARA rules created by Synacktiv

USB HID driver emulation with PID/VID (0x3bca/0x27bb) of Plenom A/S Busylight Alpha, that is supported by Mimikatz. When mimikatz is executed, a…

Tracker of publicly reported prompt-injection techniques, broken down by delivery method, encoding, and propagation behavior, with confirmed models,…