
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
370 results
redtail-ioc preview

redtail-ioc

GitHublukeslp/redtail-ioc

IOCs and a read-only triage checklist from a real Linux root compromise: RedTail miner, XorDDoS persistence, MoneroOcean miner, DirtyFrag LPE…
curated-resourcesdigital-forensicseducation+6
2
3 months ago
Shuffle preview

Shuffle

GitHubshuffle/shuffle

Open-source security orchestration, automation, and response (SOAR) platform with a visual workflow editor, prebuilt security app integrations, and…
defensive-toolsincident-responseioc-management+3
2.5k13 days ago
mvt preview

mvt

GitHubmvt-project/mvt

Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
android-securitydigital-forensicsdisk-forensics+7
15.3k2 days ago
cve-search preview

cve-search

GitHubcve-search/cve-search

Local CVE/CPE vulnerability database with search, ranking, web interface, and API for offline vulnerability analysis and management.
database-securityinformation-gatheringioc-management+4
2.7k1 month ago
intelmq preview

intelmq

GitHubcerttools/intelmq

IntelMQ is a solution for IT security teams for collecting and processing security feeds using a message queuing protocol.
incident-responseinformation-gatheringintrusion-detection+6
1.1k5 months ago
Data-Shield_IPv4_Blocklist preview

Data-Shield_IPv4_Blocklist

GitHubduggytuxy/data-shield_ipv4_blocklist

Curated IPv4 blocklist of malicious addresses, refreshed every 6 hours for firewall and WAF ingestion, with split lists and CTI-ready formats for…
defensive-toolsincident-responseinformation-gathering+5
6144 days ago
attack-stix-data preview

attack-stix-data

GitHubmitre-attack/attack-stix-data

STIX 2.1 collections of the MITRE ATT&CK knowledge base, providing adversary tactics and techniques for enterprise, mobile, and ICS threat…
curated-resourcesioc-managementmobile-security+4
6972 months ago
ThreatIngestor preview

ThreatIngestor

GitHubpedramamini/threatingestor

Automated threat intelligence aggregation tool that extracts and normalizes indicators from multiple sources (OSINT feeds, malware reports) into a…
information-gatheringintrusion-detectionioc-management+3
9314 months ago
Malware-IOCs preview

Malware-IOCs

GitHubexecutemalware/malware-iocs

Curated collection of indicators of compromise extracted from real-world malware investigations, including hashes, domains, and IPs for threat…
curated-resourcesdigital-forensicsincident-response+3
5112 years ago
awesome-dfir-skills preview

awesome-dfir-skills

GitHubtsale/awesome-dfir-skills

A curated collection of DFIR skills and workflows for InfoSec practitioners.
curated-resourcesdigital-forensicseducation+7
3235 months ago
sleep_python_bridge preview

sleep_python_bridge

GitHubcobalt-strike/sleep_python_bridge

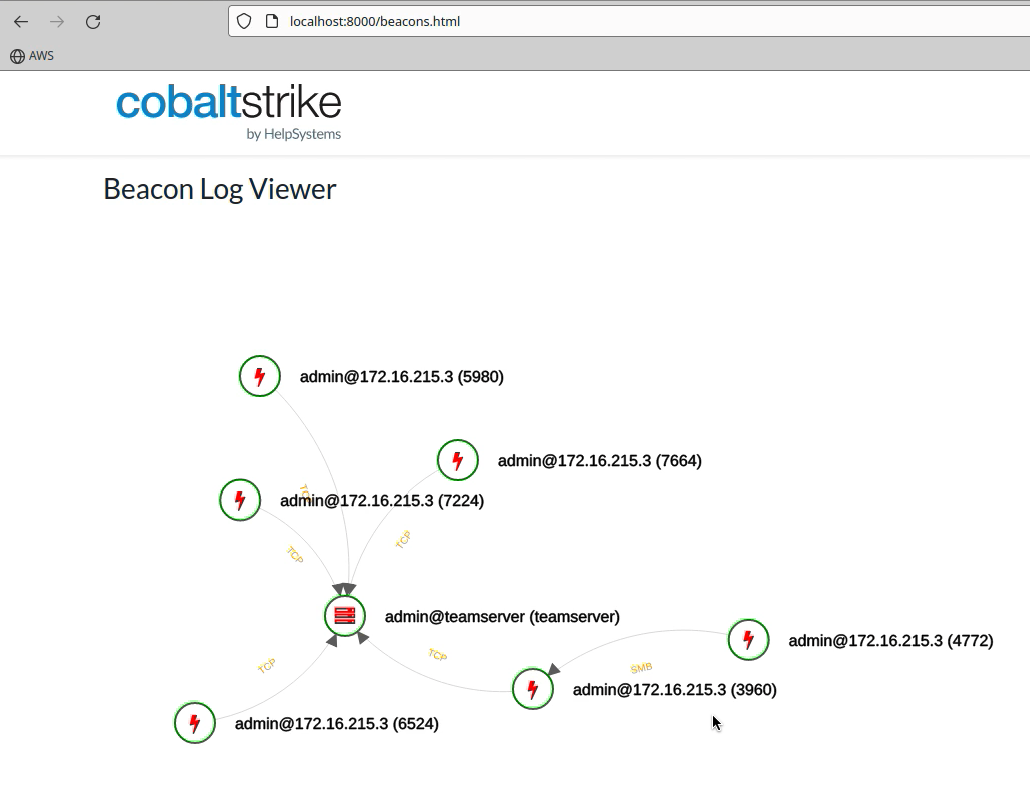
This project is 'bridge' between the sleep and python language. It allows the control of a Cobalt Strike teamserver through python without the need…

command-and-controlioc-managementlog-analysis+3
1881 year ago
BlueBox preview

BlueBox

GitHubsvdwi/bluebox

Open-source threat intelligence platform for malware and observable analysis. Enriches IPs, domains, URLs, and hashes with external sources, performs…
ioc-managementmachine-learningmalware-analysis+4
504 years ago
ThreatPad preview

ThreatPad

GitHubbhavikmalhotra/threatpad

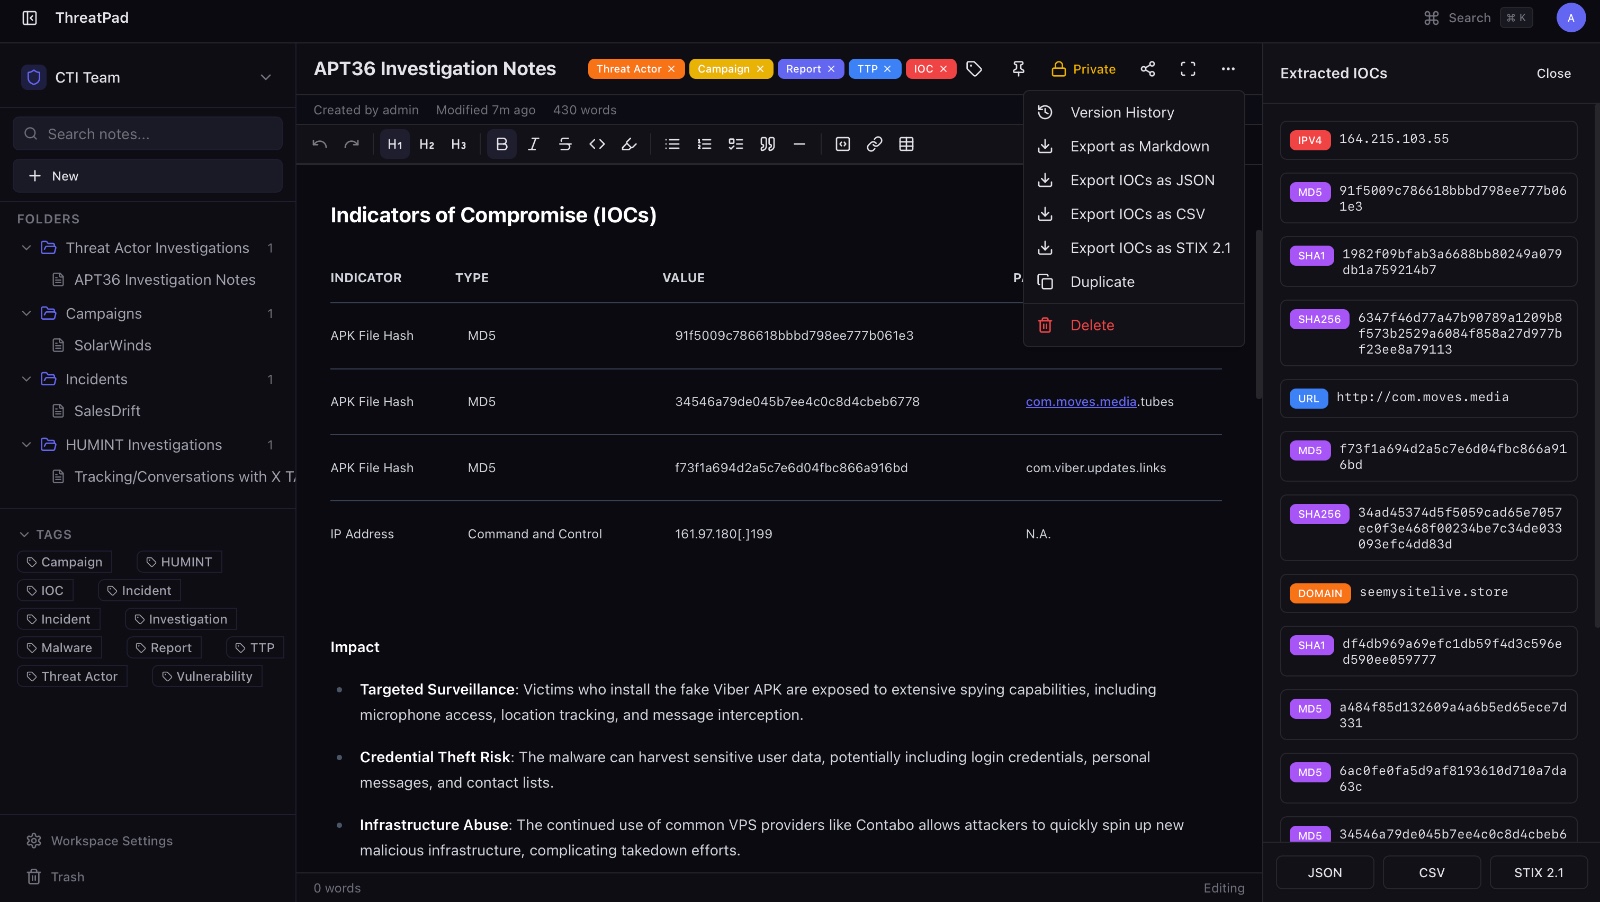
Open-source collaborative note-taking platform for cybersecurity and CTI teams. IOC auto-extraction, STIX 2.1 export, real-time editing, RBAC,…
data-exfiltrationeducationincident-response+5
246 months ago
fortimail-zero-day-cve-2026-104286 preview

fortimail-zero-day-cve-2026-104286

GitHubtechupdate24/fortimail-zero-day-cve-2026-104286

A complete guide and workflow for integrating Agile sprints with DevOps CI/CD pipelines.
email-securityexploitationincident-response+3
9 days ago
gitlab-cve-2026-85706-ioc preview

gitlab-cve-2026-85706-ioc

GitHubjithinkrishnanrs/gitlab-cve-2026-85706-ioc

CVE-2026-85706 — GitLab Path Traversal IOC Scanner & Detection Toolkit. Detect and hunt for exploitation of the critical unauthenticated GitLab CE/EE…
defensive-toolsincident-responseinformation-gathering+8
228 days ago
SOC274---Palo-Alto-Networks-PAN-OS-Command-Injection-Vulnerability-Exploitation-CVE-2024-3400- preview

SOC274---Palo-Alto-Networks-PAN-OS-Command-Injection-Vulnerability-Exploitation-CVE-2024-3400-

GitHubcyberbibs/soc274---palo-alto-networks-pan-os-command-injection-vulnerability-exploitation-cve-2024-3400-

Step-by-step SOC analyst walkthrough for investigating and remediating CVE-2024-3400 (PAN-OS command injection). Covers detection, log analysis,…
digital-forensicseducationincident-response+6
1 year ago
SOC335-CVE-2024-49138-Exploitation-Detected preview

SOC335-CVE-2024-49138-Exploitation-Detected

GitHubbridg3ops/soc335-cve-2024-49138-exploitation-detected

Detailed incident response walkthrough analyzing CVE-2024-49138 exploitation on Windows, covering process tree analysis, IOC identification, and…
digital-forensicseducationincident-response+4
10 months ago
exist preview
Archived

exist

GitHubnict-csl/exist

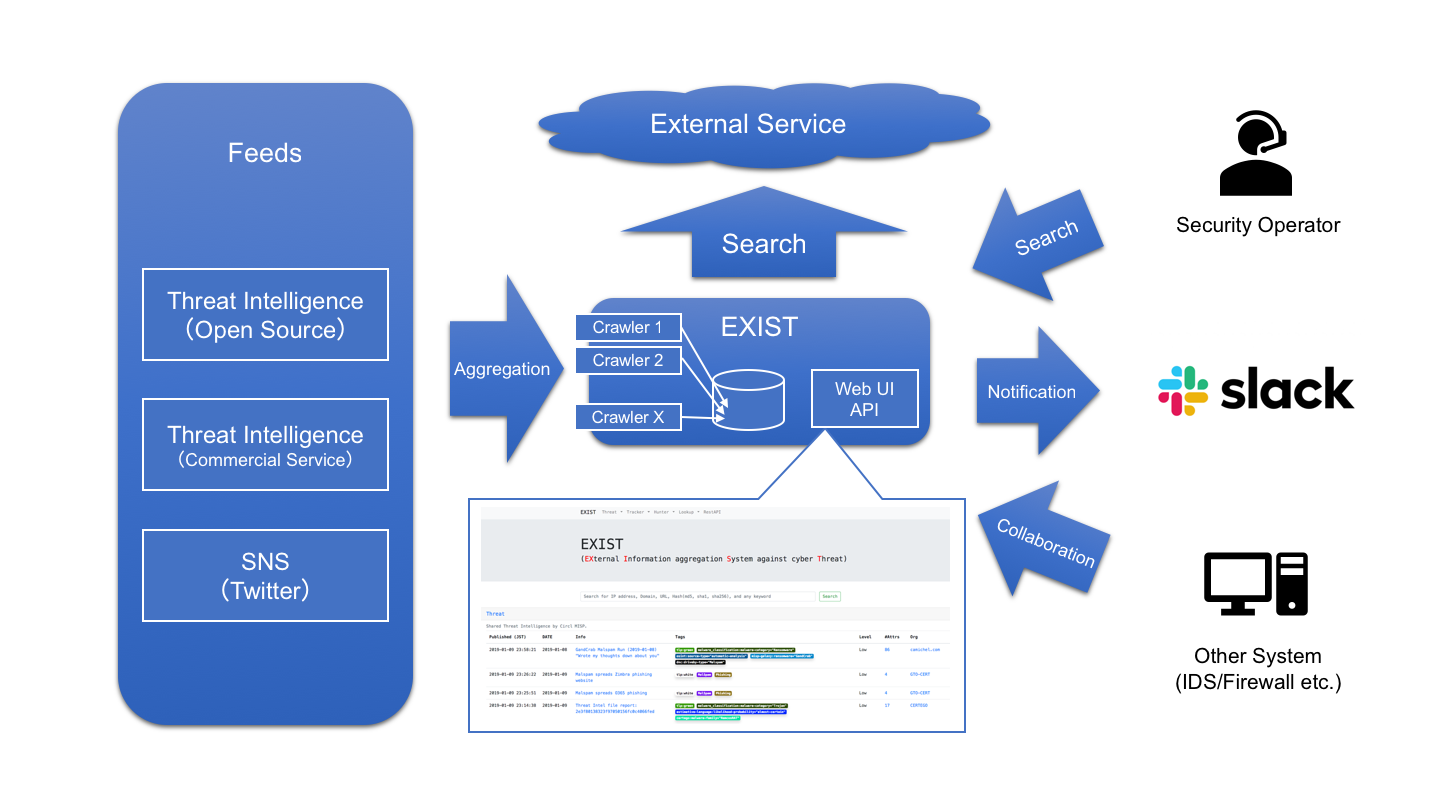
EXIST is a web application for aggregating and analyzing cyber threat intelligence.

educationincident-responseinformation-gathering+6
1526 months ago
Previous12…21Next