

redtail-ioc
 lukeslp/redtail-ioc
IOCs and a read-only triage checklist from a real Linux root compromise: RedTail miner, XorDDoS persistence, MoneroOcean miner, DirtyFrag LPE…
curated-resourcesdigital-forensicseducation+6
2
lukeslp/redtail-iocIOCs and a read-only triage checklist from a real Linux root compromise: RedTail miner, XorDDoS persistence, MoneroOcean miner, DirtyFrag LPE…
 vishvacyber/detection-tool-kit-for-cve-2026-31431
Layered detection toolkit for CVE-2026-31431 (Copy Fail) Linux kernel LPE. Provides eBPF, auditd, Sigma rules, page-cache diff, and IOC guides for…
 ma1am/cve-2022-26134-exploit-detection
This repository contains Yara rule and the method that a security investigator may want to use for CVE-2022-26134 threat hunting on their Linux…
 rxwx/pulse-meter
Parses the System Snapshot from an Ivanti Connect Secure applicance to identify possible IOCs related to CVE-2023-46805, CVE-2024-21887 and…
 maxime288/fragnesia-cve-2026-46300
Educational repository detailing CVE-2026-46300 (Fragnesia), a Linux kernel local privilege escalation vulnerability. Provides technical analysis,…
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 onapsis/onapsis_cve-2025-31324_scanner_tools
Python-based scanner for CVE-2025-31324 that identifies vulnerable SAP NetWeaver Visual Composer instances and detects indicators of compromise from…
 basitsajidsoc/soc-investigation-cve-2024-49138
Investigation and Incident Response report for LetsDefend Alert SOC335 (CVE-2024-49138 Exploitation)

 suominen/cve-2026-53266
Single-page tracker recording which Linux distributions have shipped fixes for the CVE-2026-53266 netfilter ebtables SNAT ARP-rewrite page-cache…
 suominen/cve-2025-39682
Single-page tracker recording per-distribution patch status for CVE-2025-39682, a use-after-free in the Linux kernel kTLS receive path.
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
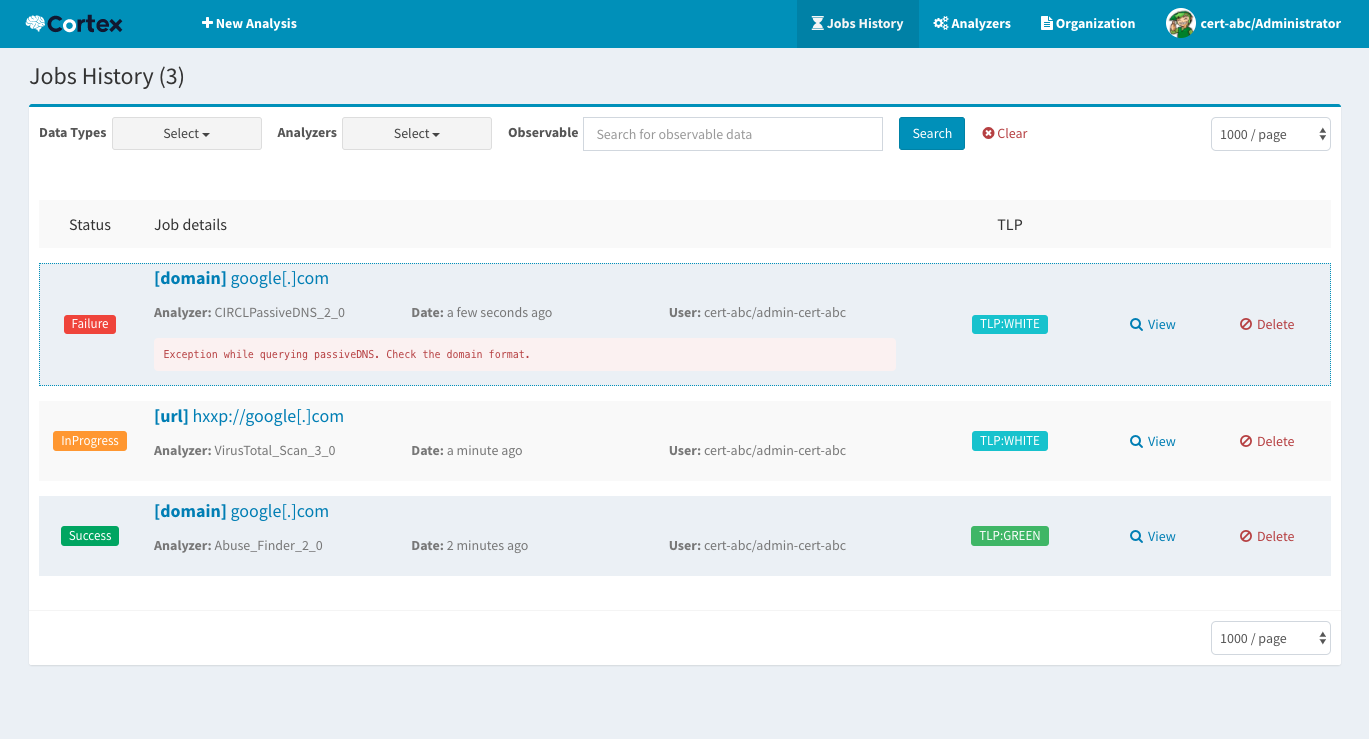 thehive-project/cortex
Cortex: a Powerful Observable Analysis and Active Response Engine
 mgeeky/protectmytooling
Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…
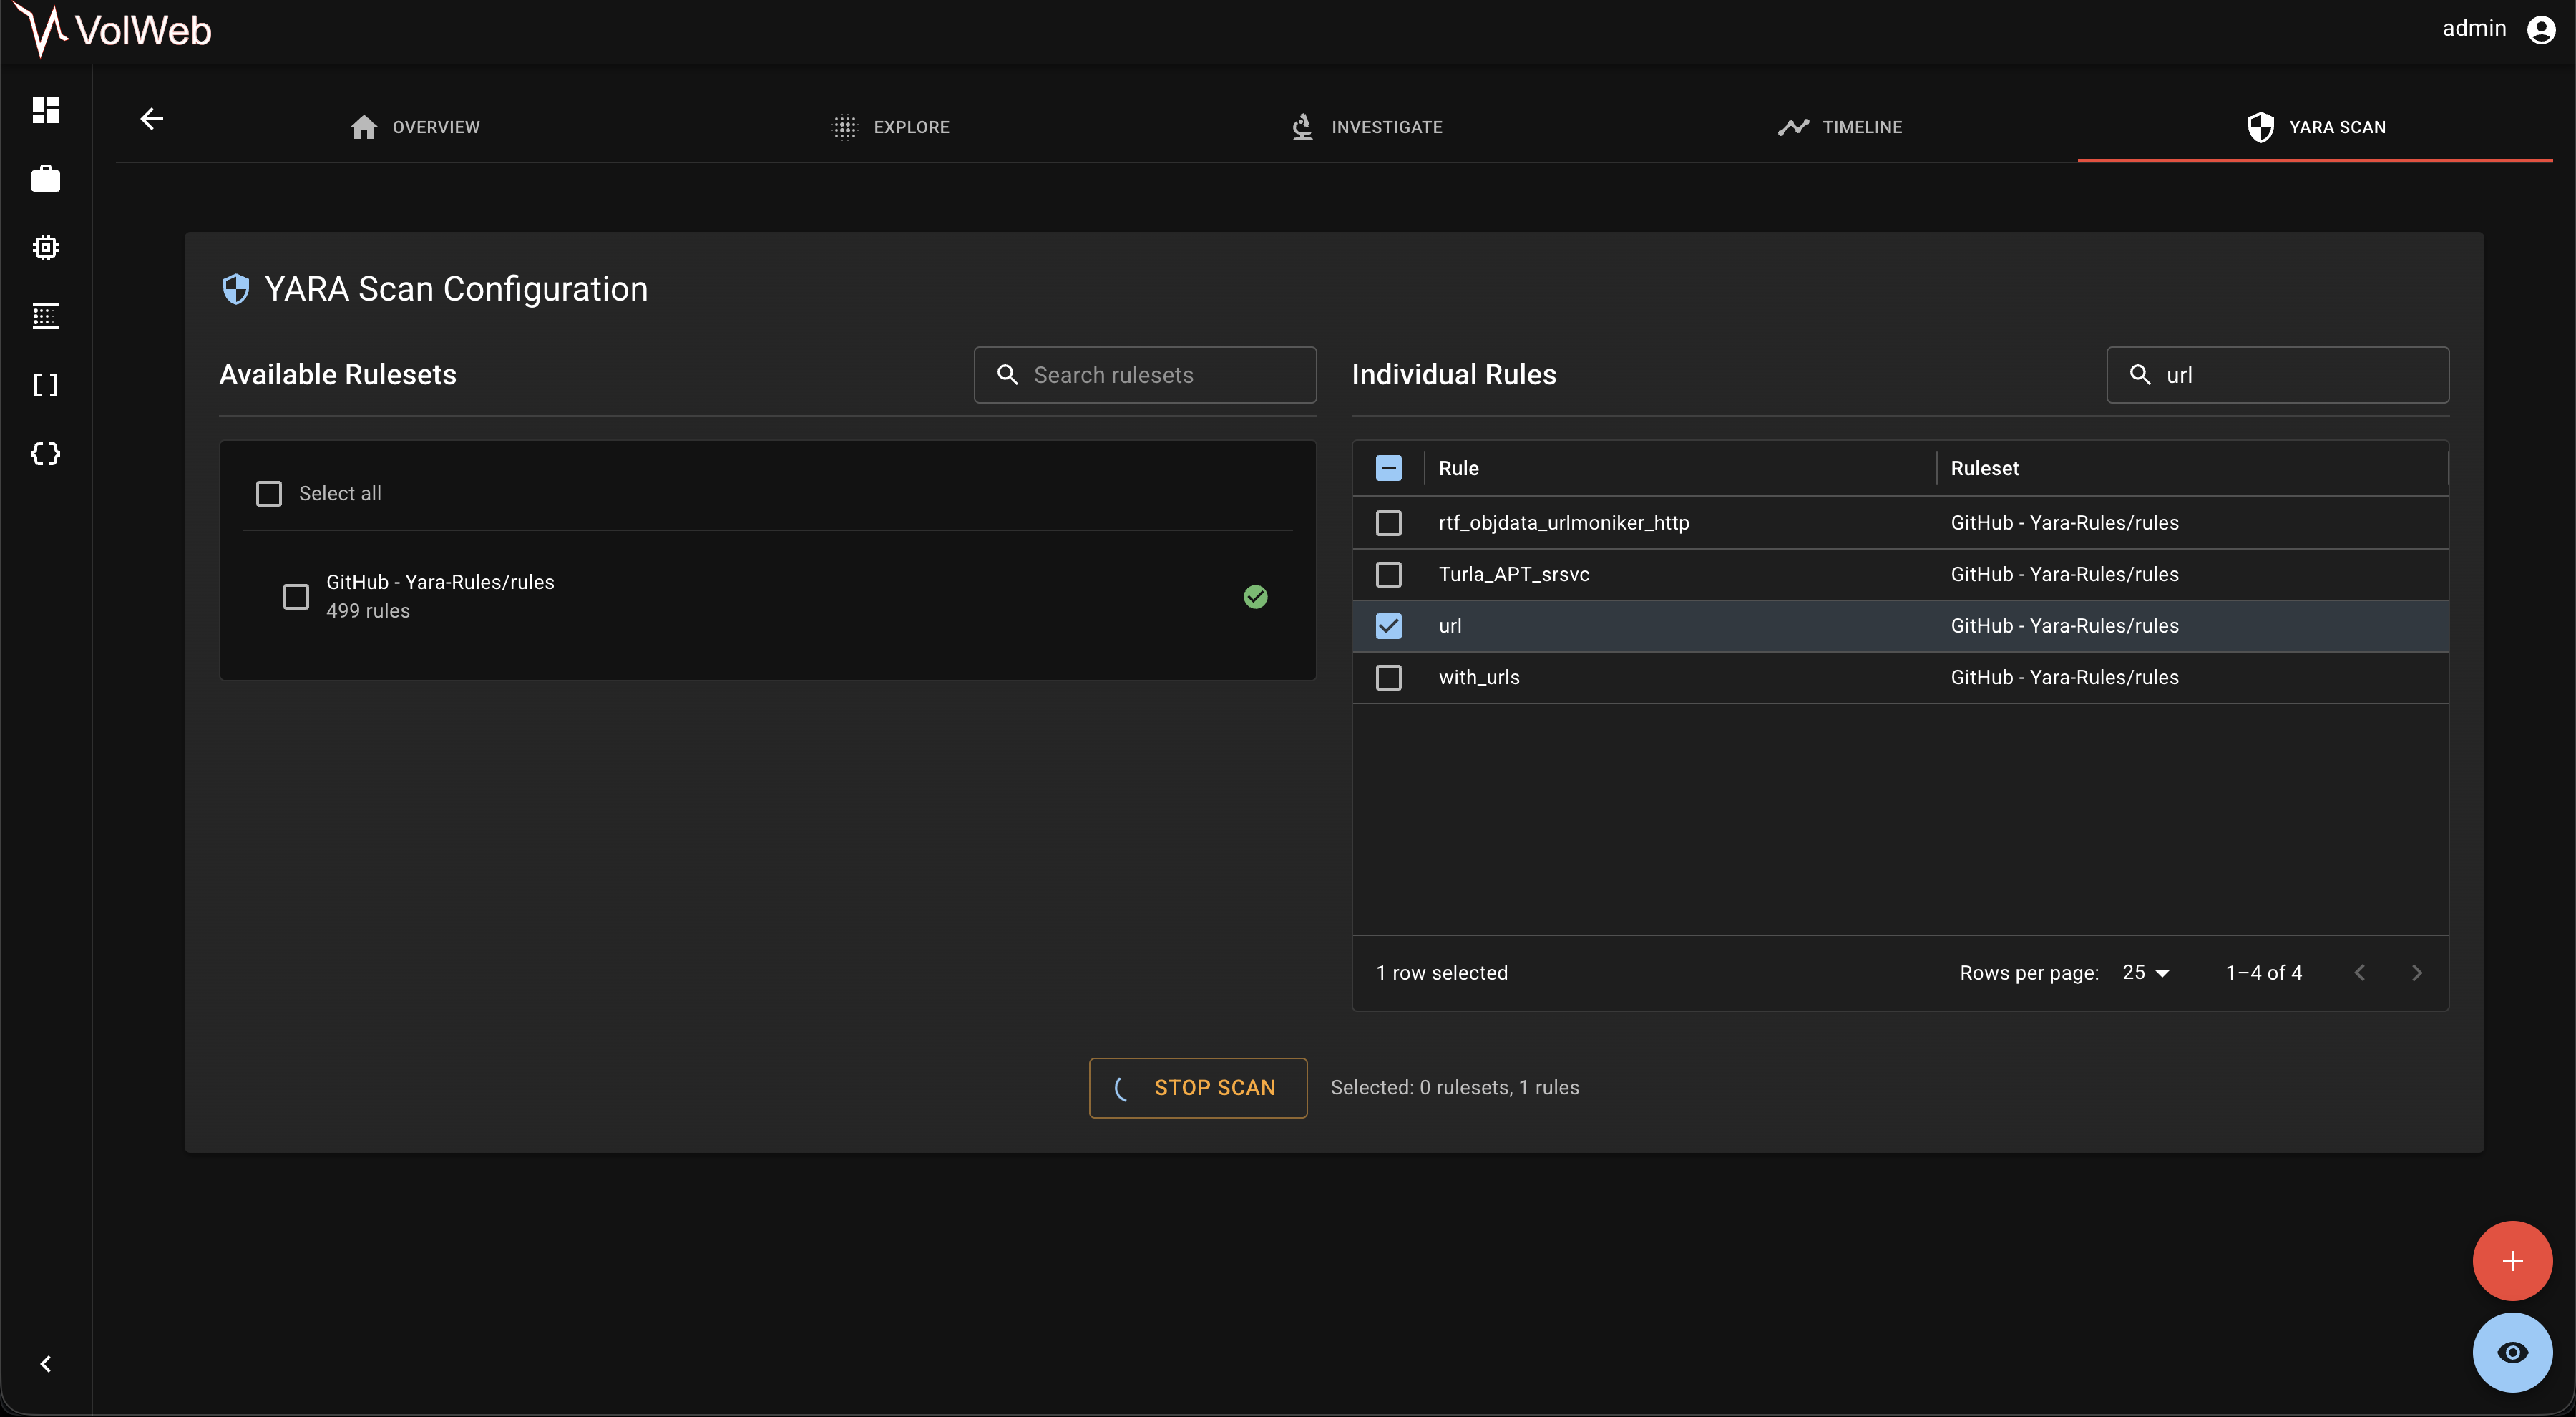 k1nd0ne/volweb
A centralized and enhanced memory analysis platform
 payloadsecurity/sandbox_scryer
Parses public sandbox detonation reports to produce threat hunting intelligence, organizes findings via MITRE ATT&CK, assembles IOCs, and generates…
 opensourcemalware/polinrider
Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…