
Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
36 results
misp-galaxy preview

misp-galaxy

GitHubmisp/misp-galaxy

Clusters and elements to attach to MISP events or attributes (like threat actors)

adversarial-attackcurated-resourcesioc-management+5
64117h 19m ago
capa preview

capa

GitHubmandiant/capa

Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
ai-assisted-reversingbinary-analysiscode-analysis+10
6.2k17 days ago
ThreatIngestor preview

ThreatIngestor

GitHubpedramamini/threatingestor

Automated threat intelligence aggregation tool that extracts and normalizes indicators from multiple sources (OSINT feeds, malware reports) into a…

information-gatheringintrusion-detectionioc-management+3
9314 months ago
Judge-Jury-and-Executable preview

Judge-Jury-and-Executable

GitHubadamwhitehat/judge-jury-and-executable

A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…
database-securitydigital-forensicsdisk-forensics+8
855 months ago
Onapsis-Mandiant-CVE-2025-31324-Vuln-Compromise-Assessment preview

Onapsis-Mandiant-CVE-2025-31324-Vuln-Compromise-Assessment

GitHubonapsis/onapsis-mandiant-cve-2025-31324-vuln-compromise-assessment

CVE-2025-31324 & CVE-2025-42999 vulnerability and compromise assessment tool
cloud-securityforensicsincident-response+4
91 year ago
Windows-Defender-Security-Auditor-CVE-2026-50656- preview

Windows-Defender-Security-Auditor-CVE-2026-50656-

GitHubeh-amish/windows-defender-security-auditor-cve-2026-50656-

Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…

configuration-auditingdefensive-toolsincident-response+8
1 month ago
CVE-2025-57819-ioc-check preview
Archived

CVE-2025-57819-ioc-check

GitHubsucuri-labs/cve-2025-57819-ioc-check

This is repository contains a script to check for current IOCs listed in the freepbx forum topic of the CVE-2025-57819
digital-forensicsforensicsincident-response+3
1 year ago
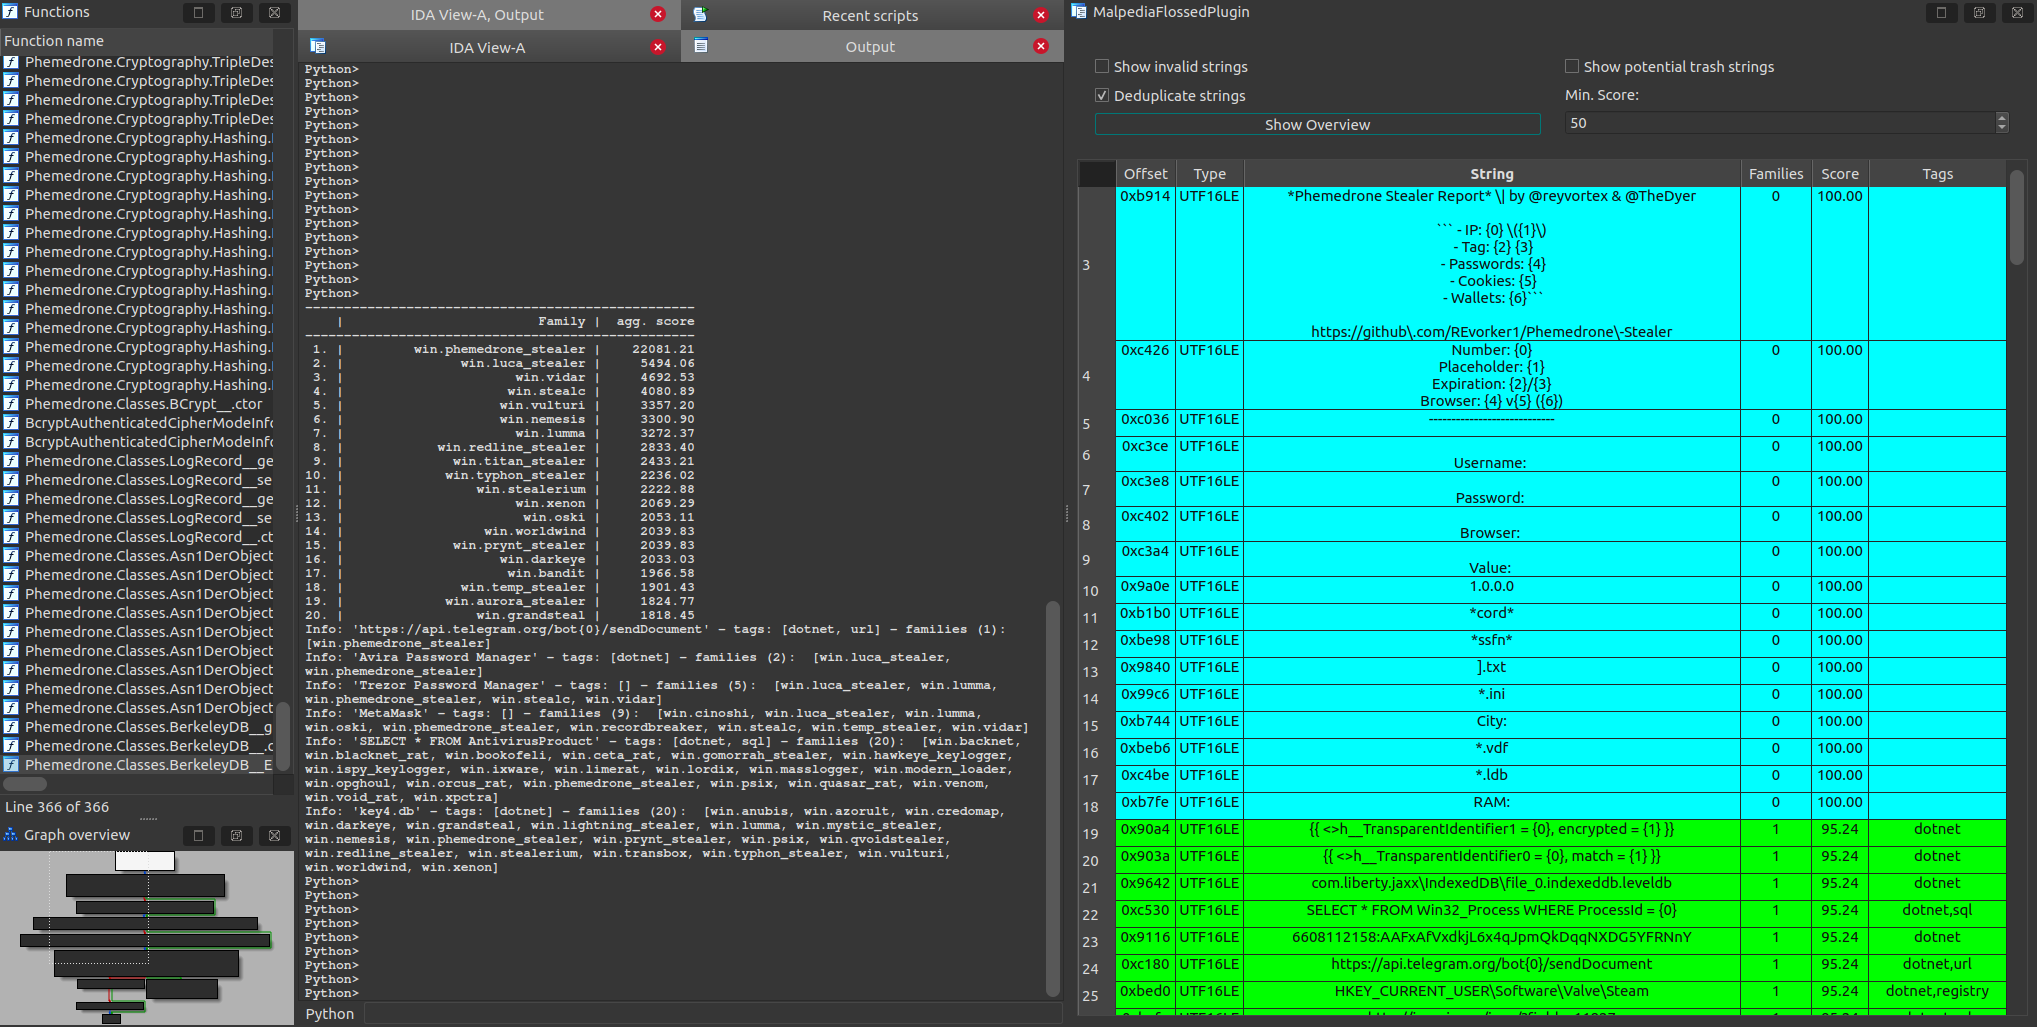
misp-taxonomies preview

misp-taxonomies

GitHubmisp/misp-taxonomies

Taxonomies used in MISP taxonomy system and can be used by other information sharing tool.
curated-resourcesincident-responseioc-management+2
30528 days ago
malpedia-flossed preview

malpedia-flossed

GitHubmalpedia/malpedia-flossed

FLARE floss applied to all unpacked+dumped samples in Malpedia, pre-processed for further use.
binary-analysiscurated-resourcesdynamic-analysis-sandboxing+8
858 months ago
CVE-2022-30190 preview

CVE-2022-30190

GitHubgyaansastra/cve-2022-30190

Comprehensive analysis of CVE-2022-30190 (Follina MSDT vulnerability) with IOCs, detection rules for SIEMs/EDR, YARA signatures, mitigation scripts,…

educationexploitationforensics+5
24 years ago
IPED preview

IPED

GitHubsepinf-inc/iped

IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
data-recoverydigital-forensicsdisk-forensics+9
3.0k1 day ago
ThePhish preview

ThePhish

GitHubemalderson/thephish

ThePhish: an automated phishing email analysis tool
digital-forensicsemail-securityincident-response+5
1.4k2 years ago
RansomCoinPublic preview

RansomCoinPublic

GitHubconcinnity-risks/ransomcoinpublic

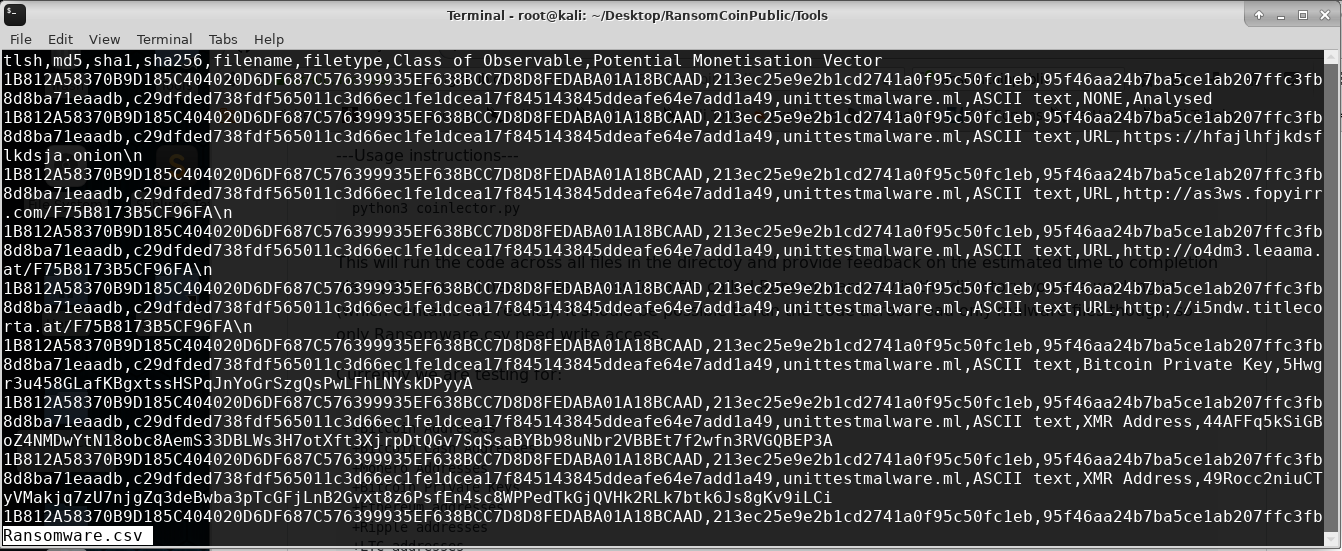
A DFIR tool to extract cryptocoin addresses and other indicators of compromise from binaries.

cryptographydigital-forensicsforensics+3
565 years ago
yara-x preview

yara-x

GitHubvirustotal/yara-x

A rewrite of YARA in Rust.

binary-analysisdata-recoverydefensive-tools+14
1.3k11h 28m ago
hexora preview

hexora

GitHubrushter/hexora

Static analysis of malicious Python code
code-analysisioc-managementmachine-learning+4
17320 days ago
packetsifterTool preview

packetsifterTool

GitHubpacketsifter/packetsiftertool

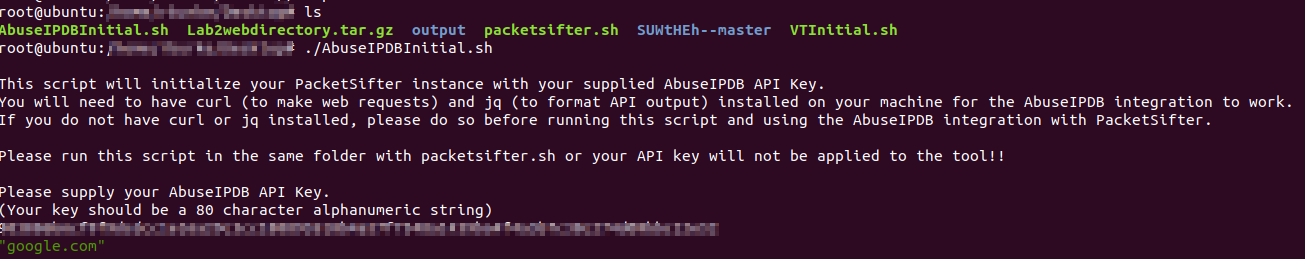
PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…
defensive-toolsdigital-forensicsforensics+5
935 years ago
Kalim_Backdoor preview

Kalim_Backdoor

GitHubsalaheldinfikri/kalim_backdoor

Kalim backdooe Malware Report
command-and-controldigital-forensicsdynamic-analysis-sandboxing+6
45 months ago
darwis-taxii preview

darwis-taxii

GitHubcspf-founder/darwis-taxii

A high-performance TAXII (Trusted Automated eXchange of Indicator Information) server written in Rust.

api-securityauthentication-authorizationioc-management+3
117 months ago
Previous12Next