

Log4Shell-Sandbox-Signature
 captanmoss/log4shell-sandbox-signature
Log4Shell(CVE-2021-45046) Sandbox Signature
dynamic-analysis-sandboxingintrusion-detectionioc-management+3
1
captanmoss/log4shell-sandbox-signatureLog4Shell(CVE-2021-45046) Sandbox Signature
 honeynet/log4shell-data
Data we are receiving from our honeypots about CVE-2021-44228
 pedramamini/awesome-yara
A curated list of awesome YARA rules, tools, and people.
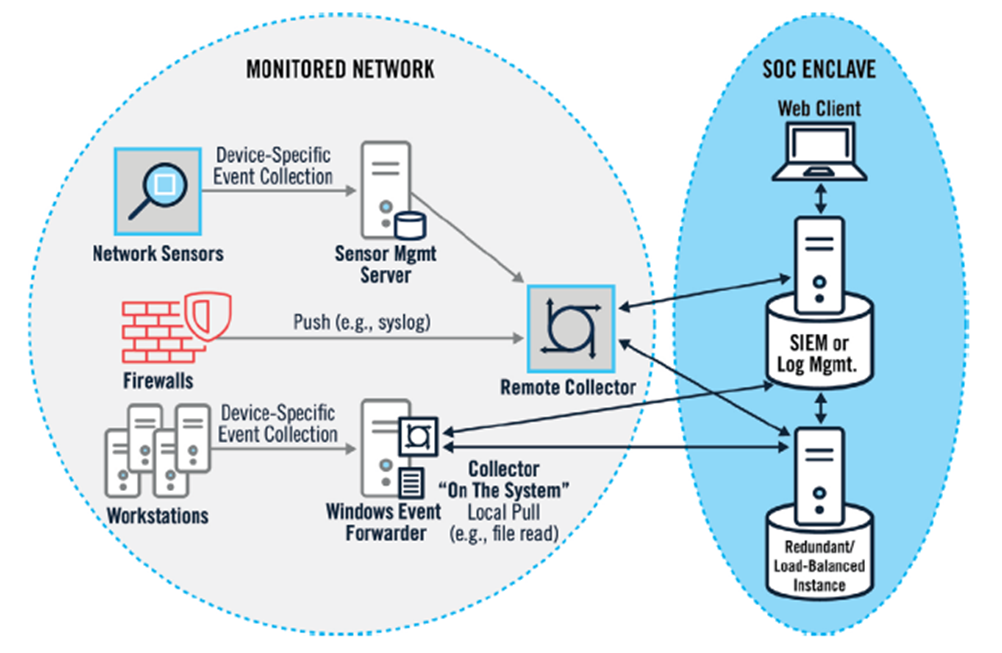 cyb3rxp/awesome-soc
A curated knowledge base to build, run and mature a SOC (including CSIRT).
 binarly-io/supplychainattacks
Curated repository of documented firmware supply chain attacks, featuring IoCs, detection tools, and references to help defenders understand and…
 huntresslabs/threat-intel
This repository contains supplemental items including IOCs, and signatures discussed in Huntress blogposts, and other media.
 infostealers-stats/credential-and-breach-monitoring
This repository provides a practical comparison of breach intelligence, dark web monitoring, and identity exposure services, with a focus on factors…
 demining/log4j-vulnerability
Educational analysis of the Log4Shell (CVE-2021-44228) vulnerability, detailing its exploitation in a cryptocurrency mining campaign with IoCs, MITRE…
 0xsyr0/log4shell
This repository contains all gathered resources we used during our Incident Reponse on CVE-2021-44228 and CVE-2021-45046 aka Log4Shell.
 eris-ths/supply-chain-guard
Detect, assess, and respond to supply chain attacks across npm/yarn and Python (pip/poetry/uv). Claude Code skill + standalone scripts. Built during…
 archanchoudhury/confluence-cve-2022-26134
This repository talks about Zero-Day Exploitation of Atlassian Confluence, it's defense and analysis point of view from a SecOps or Blue Team…
 anonaninda/aninda-security-advisories
Security advisories published by Aninda , including CVE-2025-56608 and future findings.
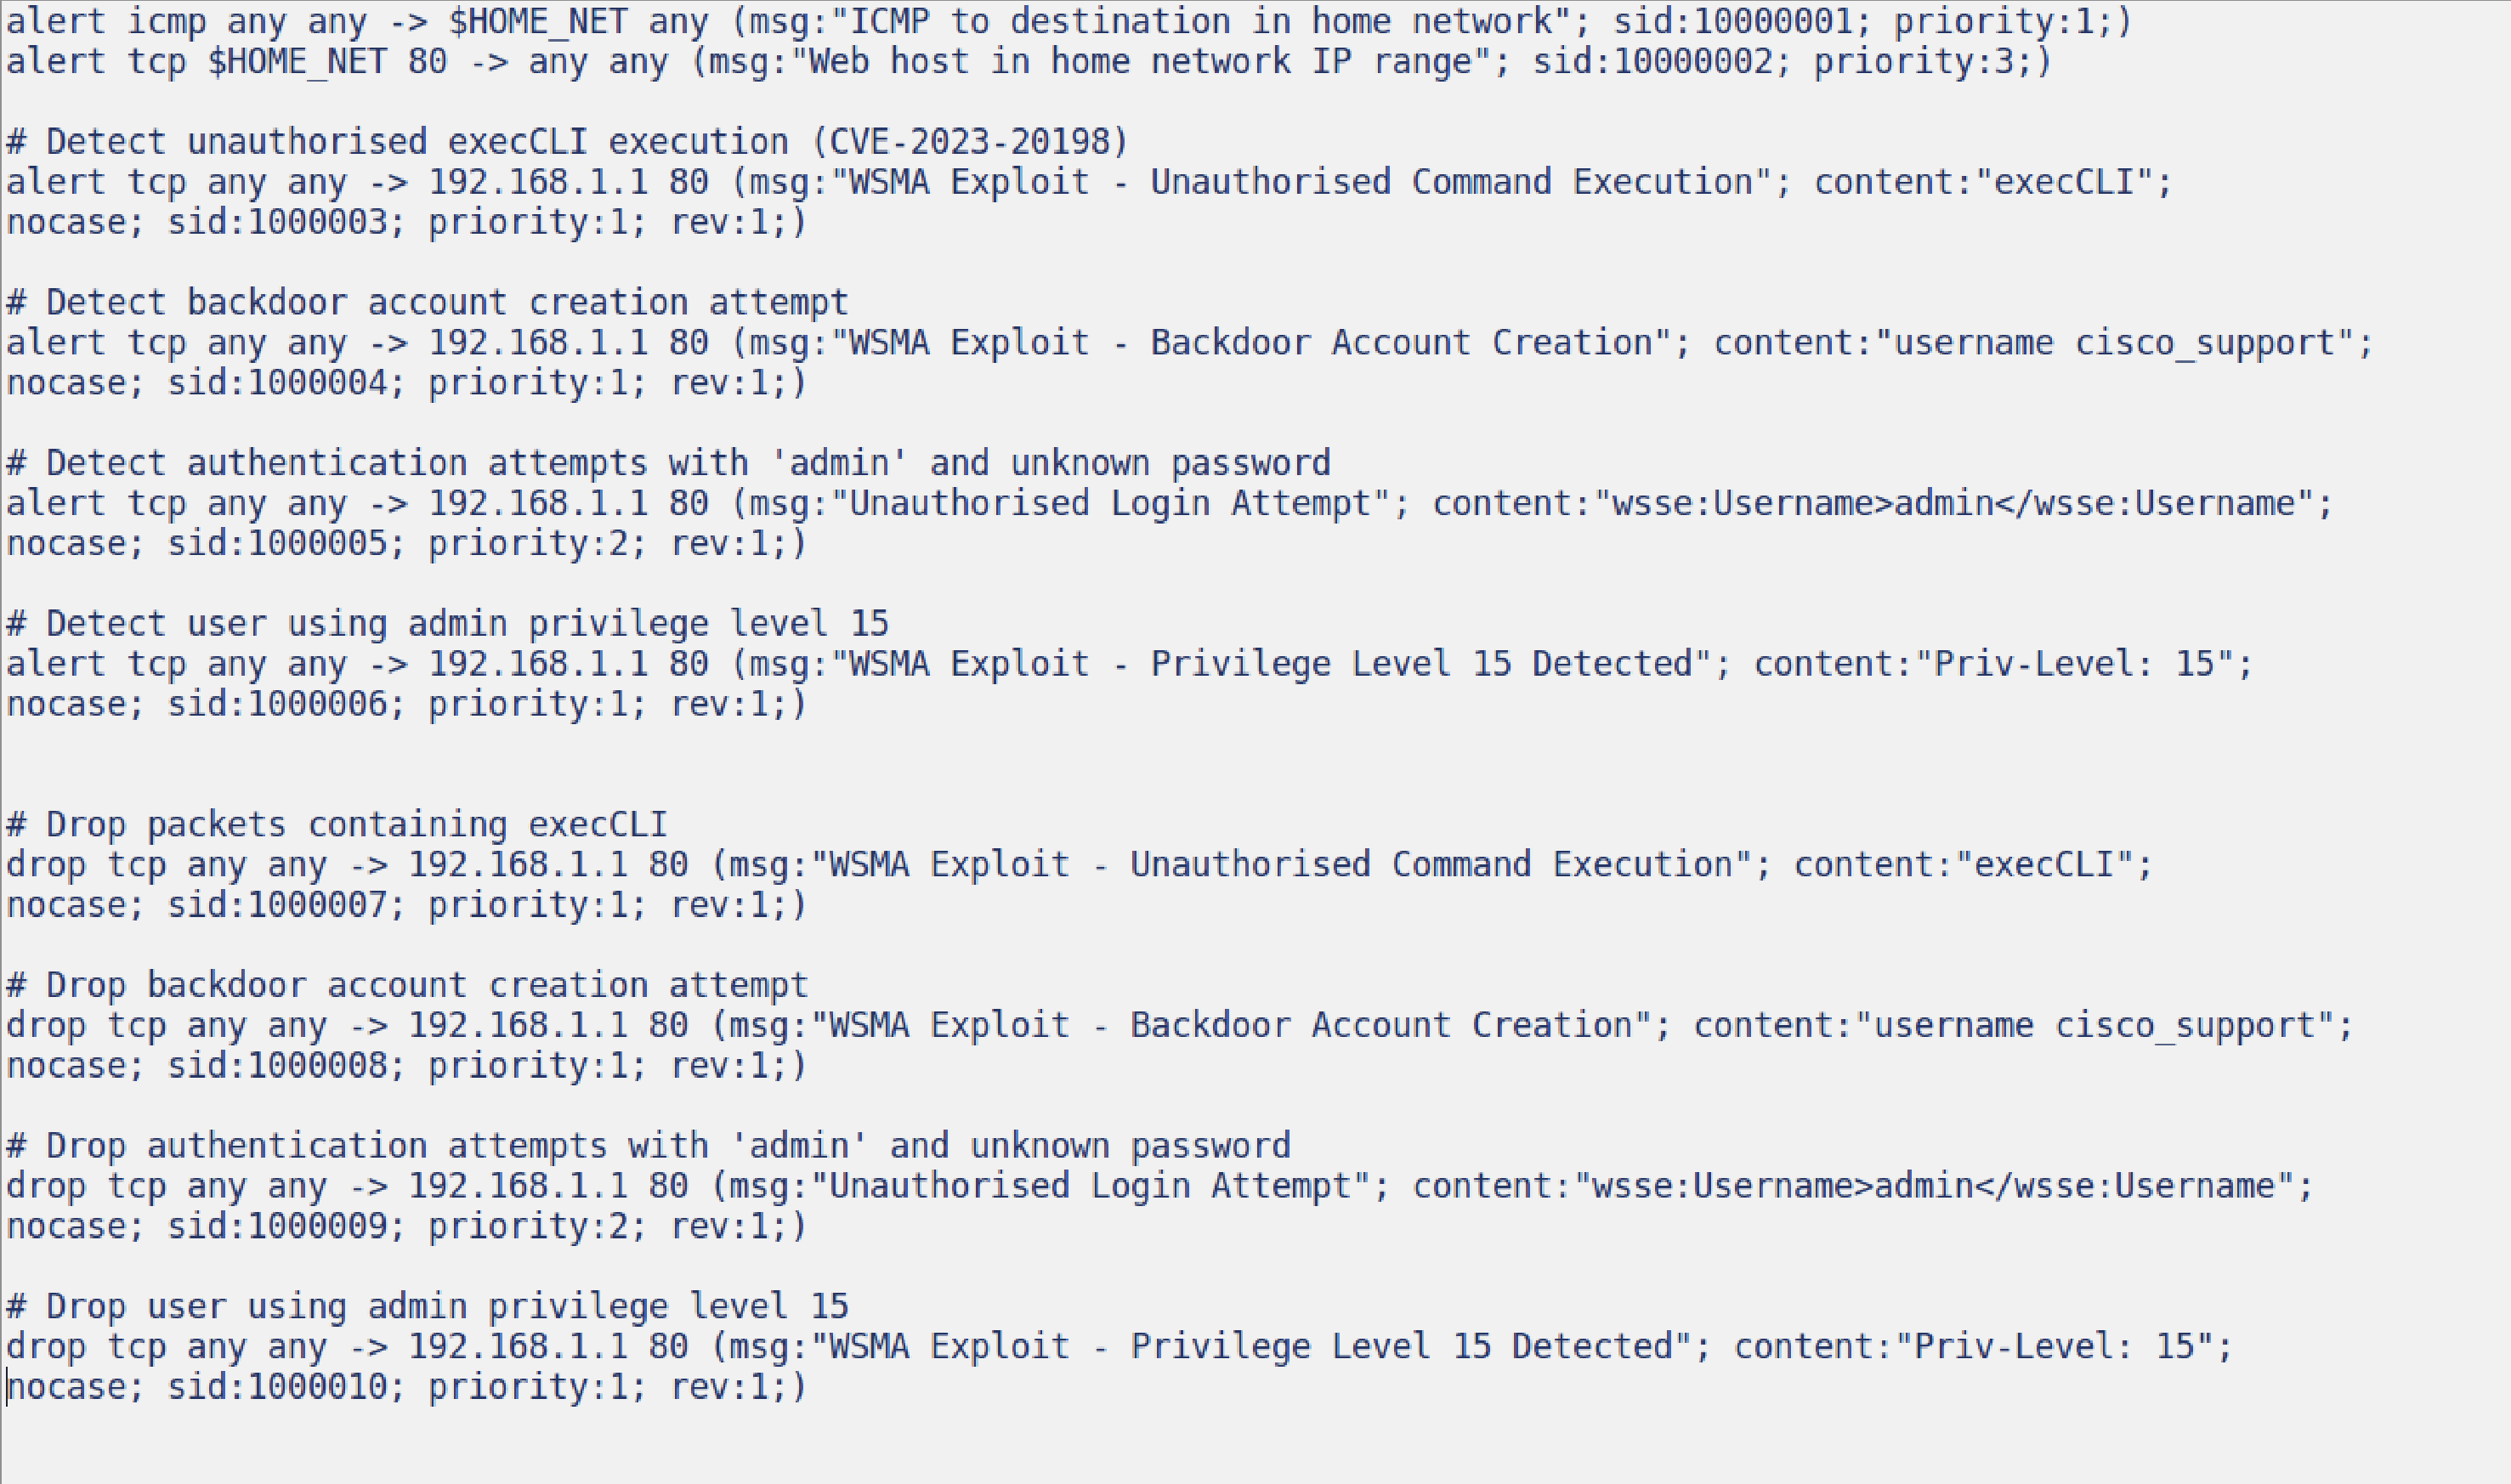 dominic471/qub-network-security-cve-2023-20198
Analysis, detection, and mitigation of CVE-2023-20198 exploitation in Cisco IOS XE – QUB CSC3064 Network Security Assessment
 cyprianatsyor/letsdefend-cve-2022-41082-exploitation-attempt
Detailed incident report and educational analysis of CVE-2022-41082 (ProxyNotShell) exploitation attempt on Microsoft Exchange Server, including…
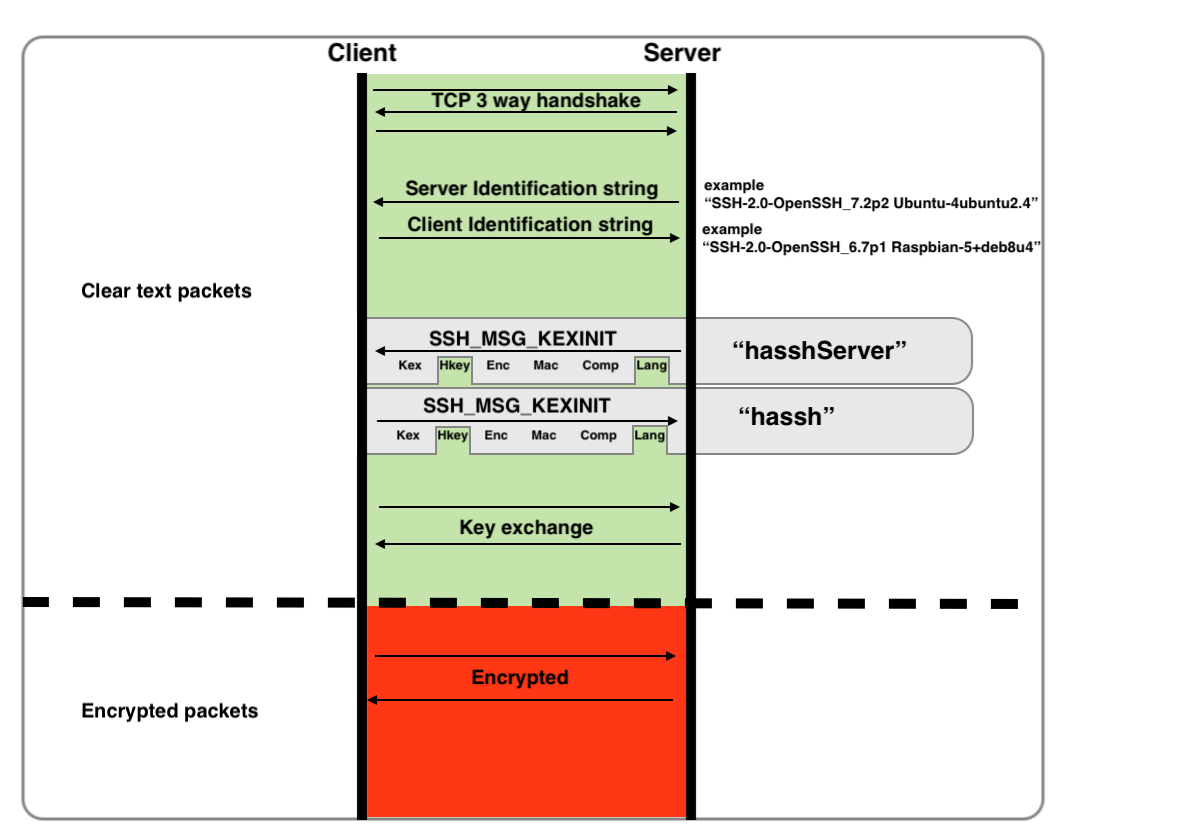 salesforce/hassh
HASSH is a network fingerprinting standard which can be used to identify specific Client and Server SSH implementations. The fingerprints can be…

 kavan00/android-projector-c2-malware
Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis
 rapticore/orenpmguard
Defense Against the Shai-Hulud Supply Chain Attack