

malicious_extension_sentry
 toborrm9/malicious_extension_sentry
Malicious Extension Database
curated-resourcesdefensive-toolseducation+6
206
toborrm9/malicious_extension_sentryMalicious Extension Database
 tracehound/tracehound
Operational security controls with forensic guarantees
 phishdestroy/destroylist
Real-time phishing & scam domain blocklist - 205k+ curated threats, 1M+ community, free API, multiple formats

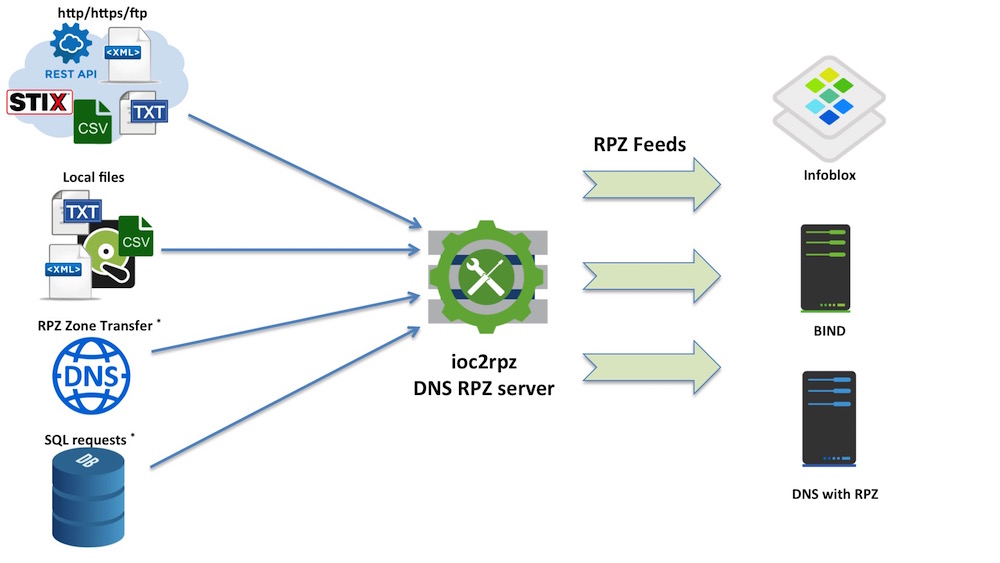 homas/ioc2rpz
ioc2rpz is a place where threat intelligence meets DNS.
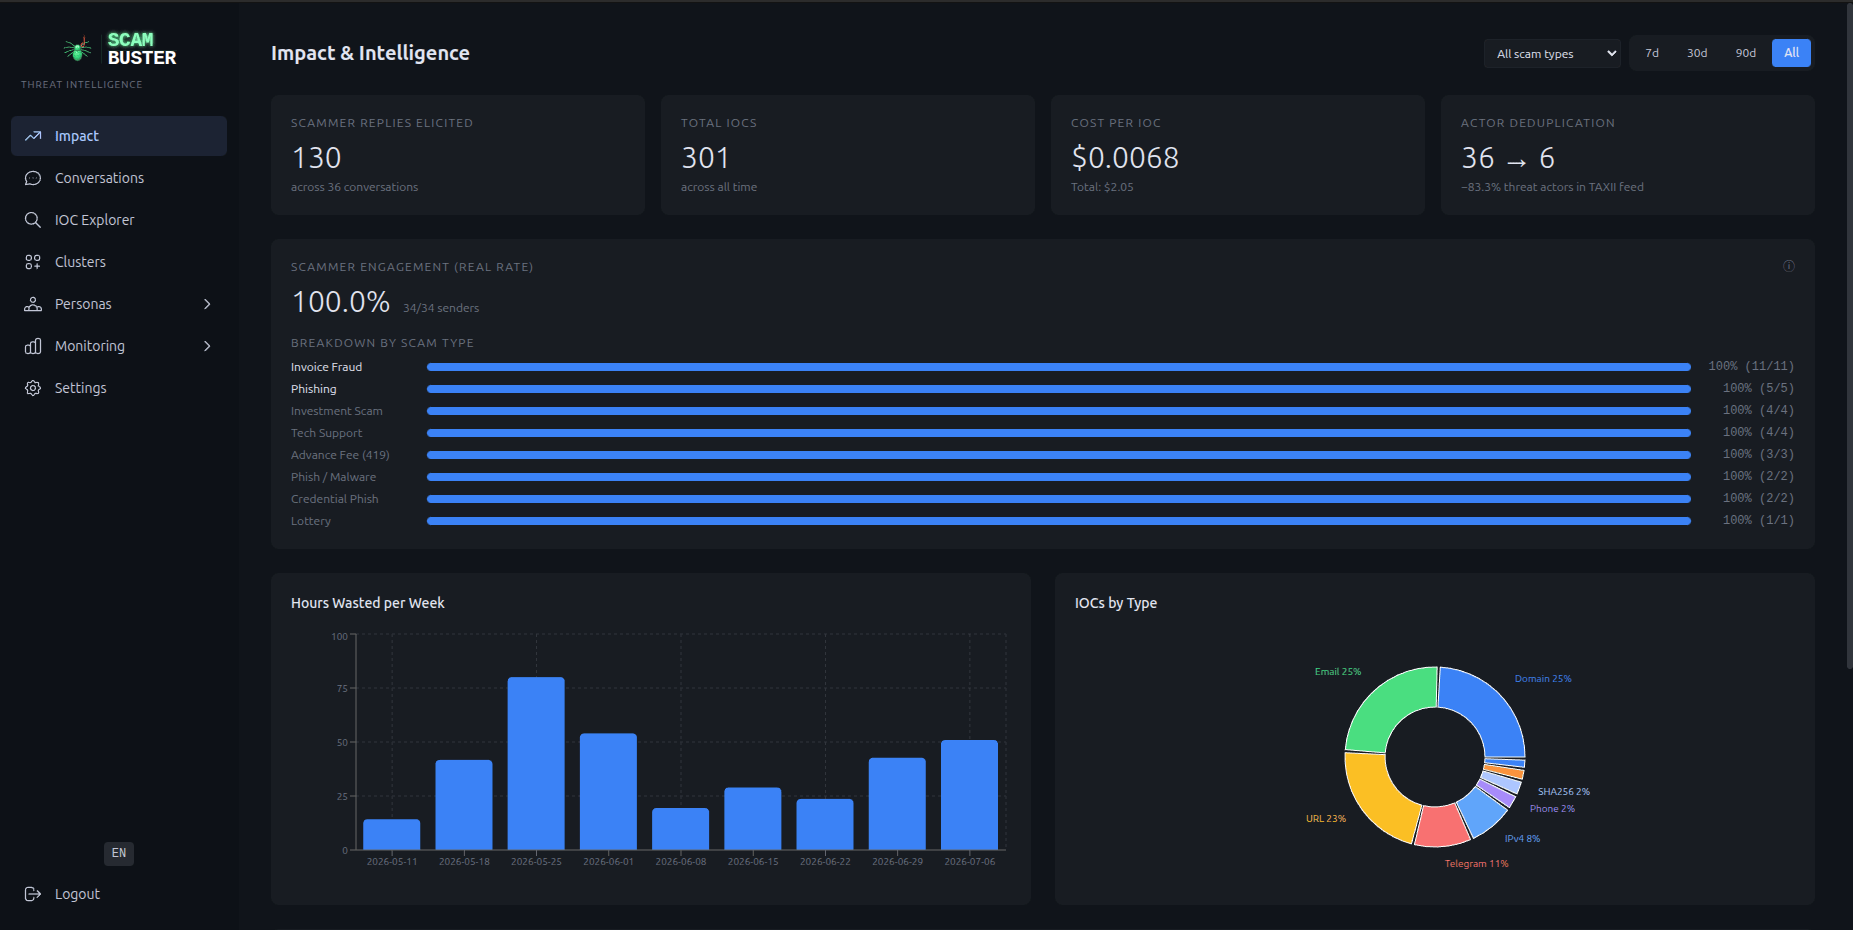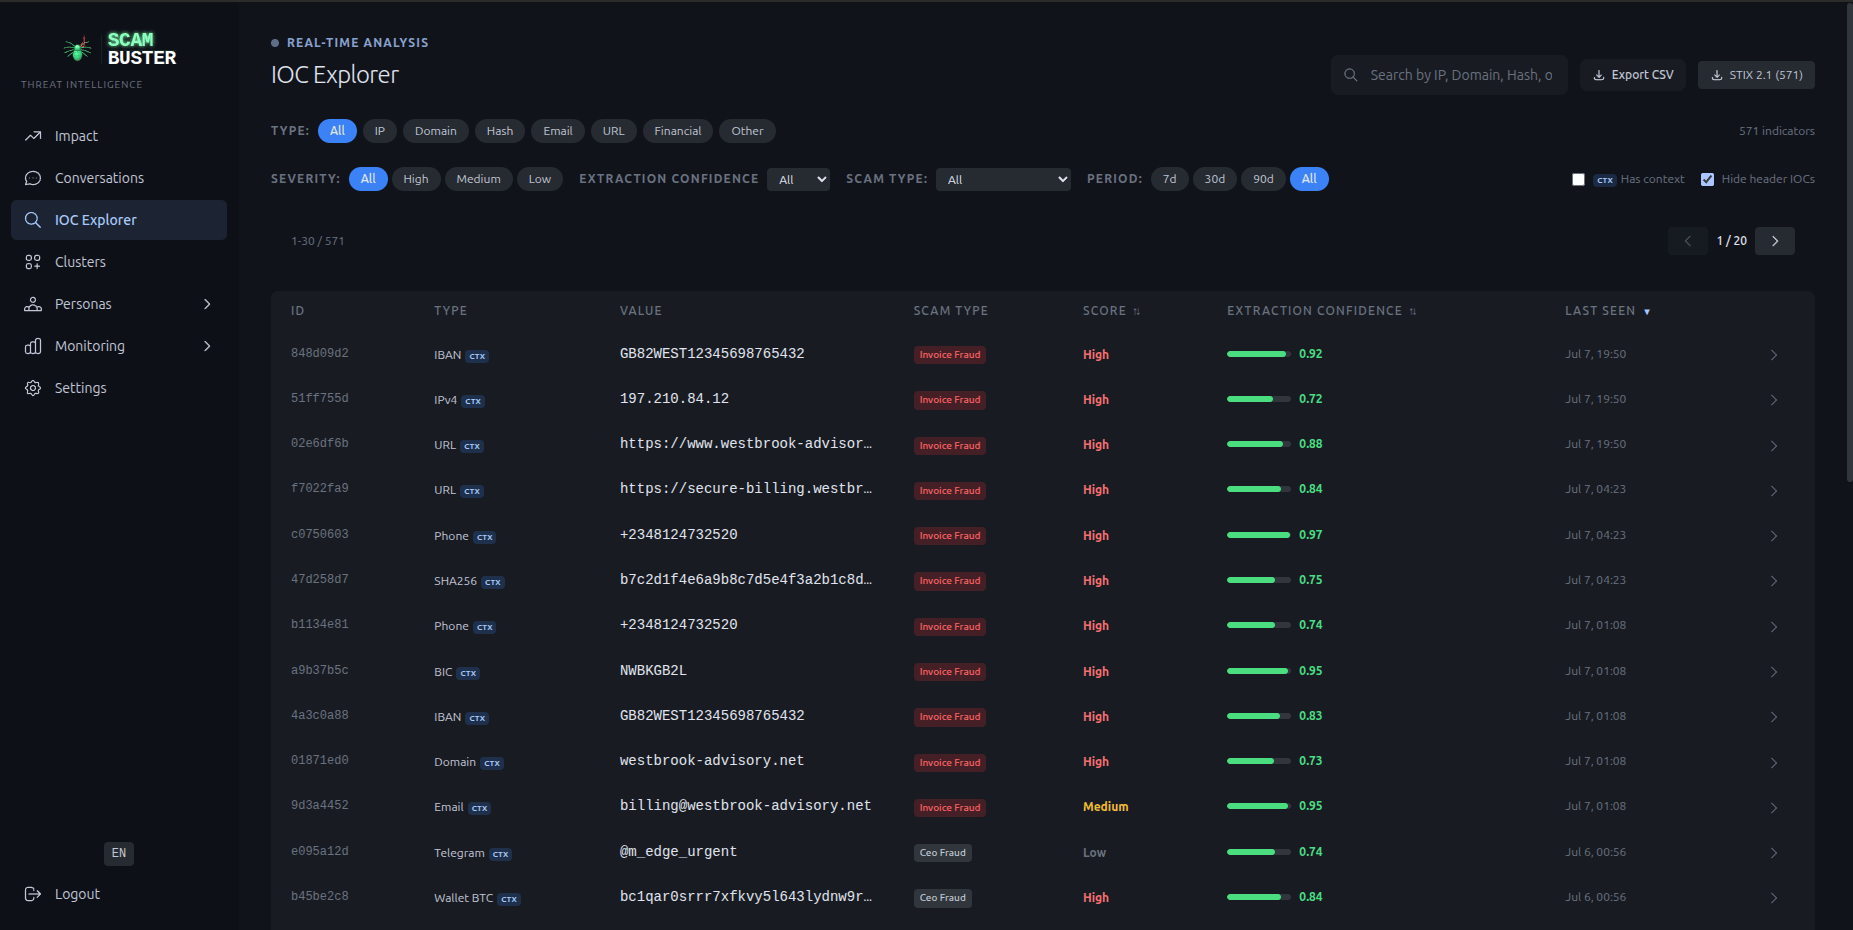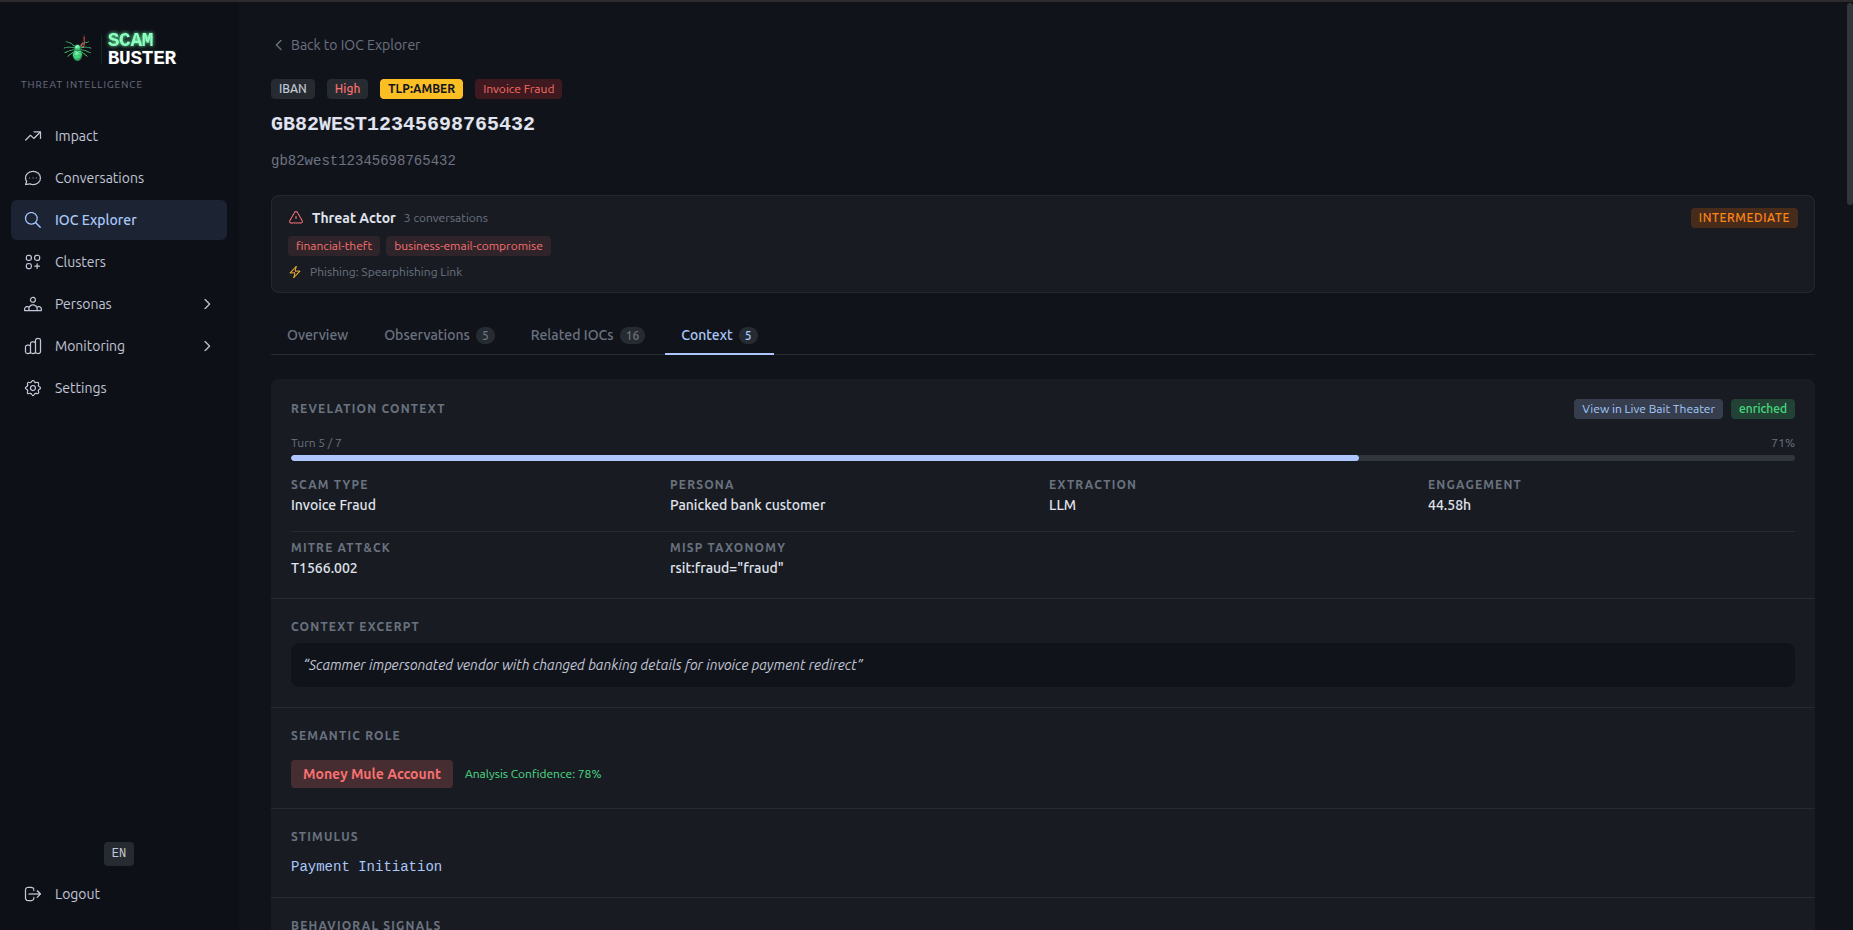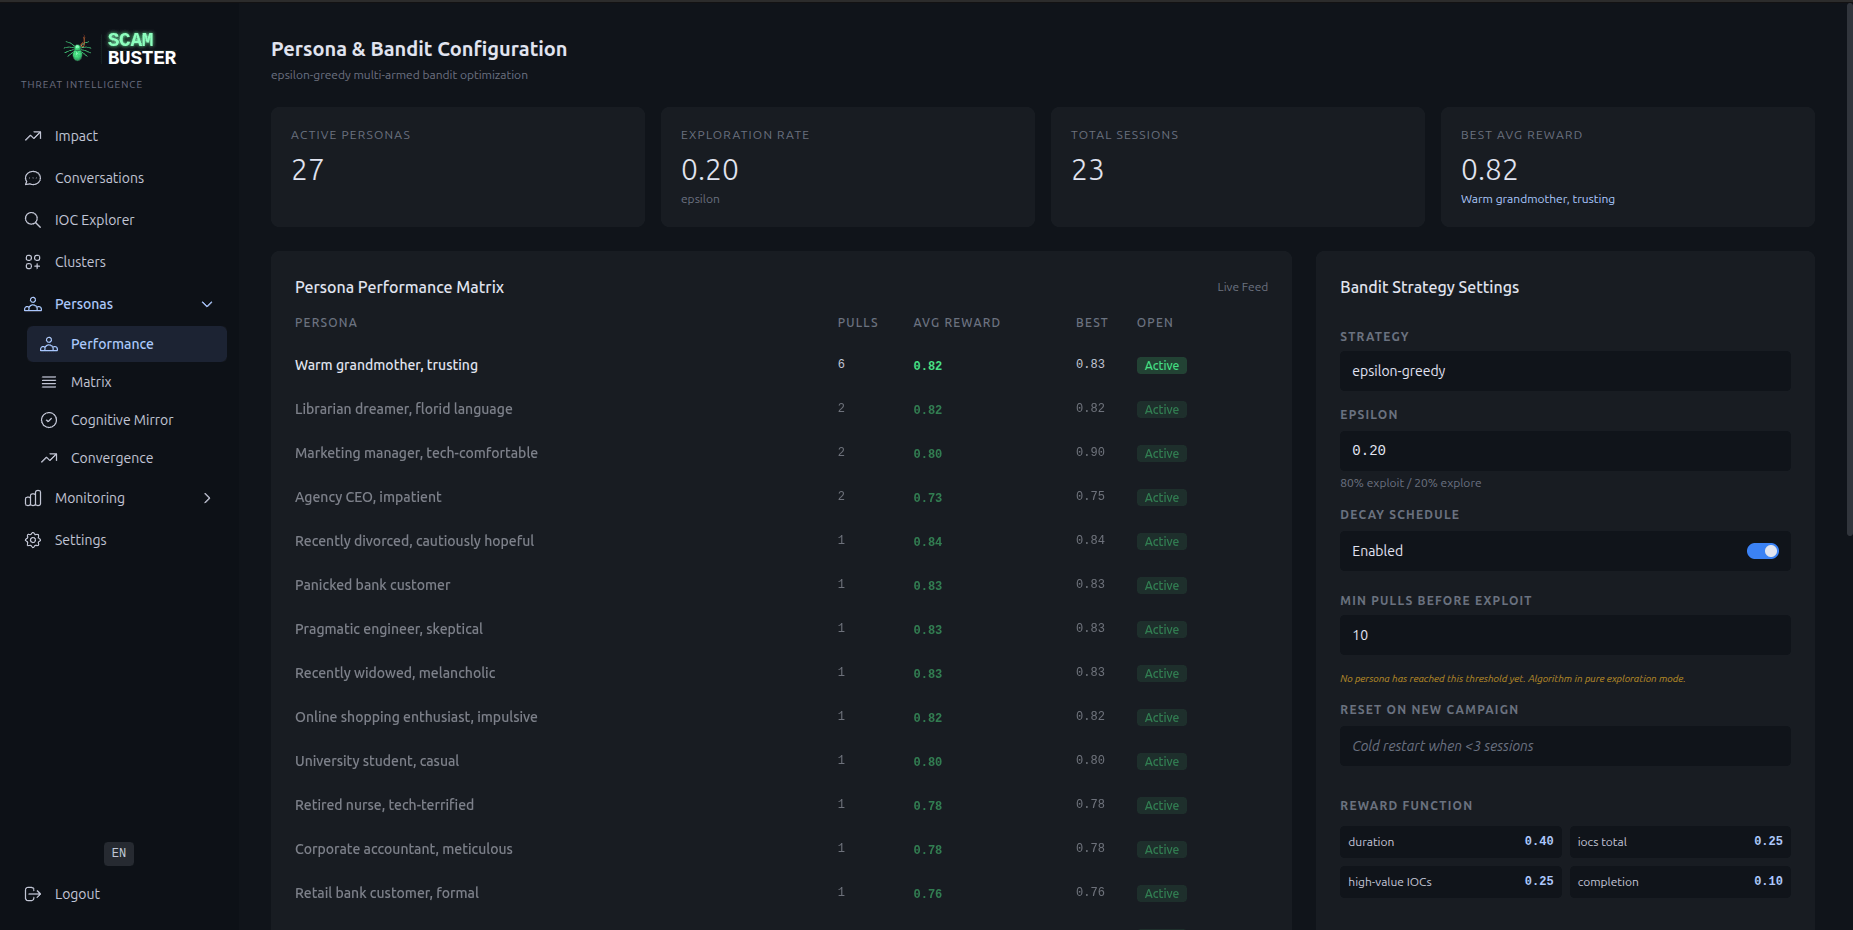 laugiov/scambuster
Defensive engagement & threat intelligence research laboratory. Converts inbound scam emails into actionable IOCs through controlled, policy-driven…
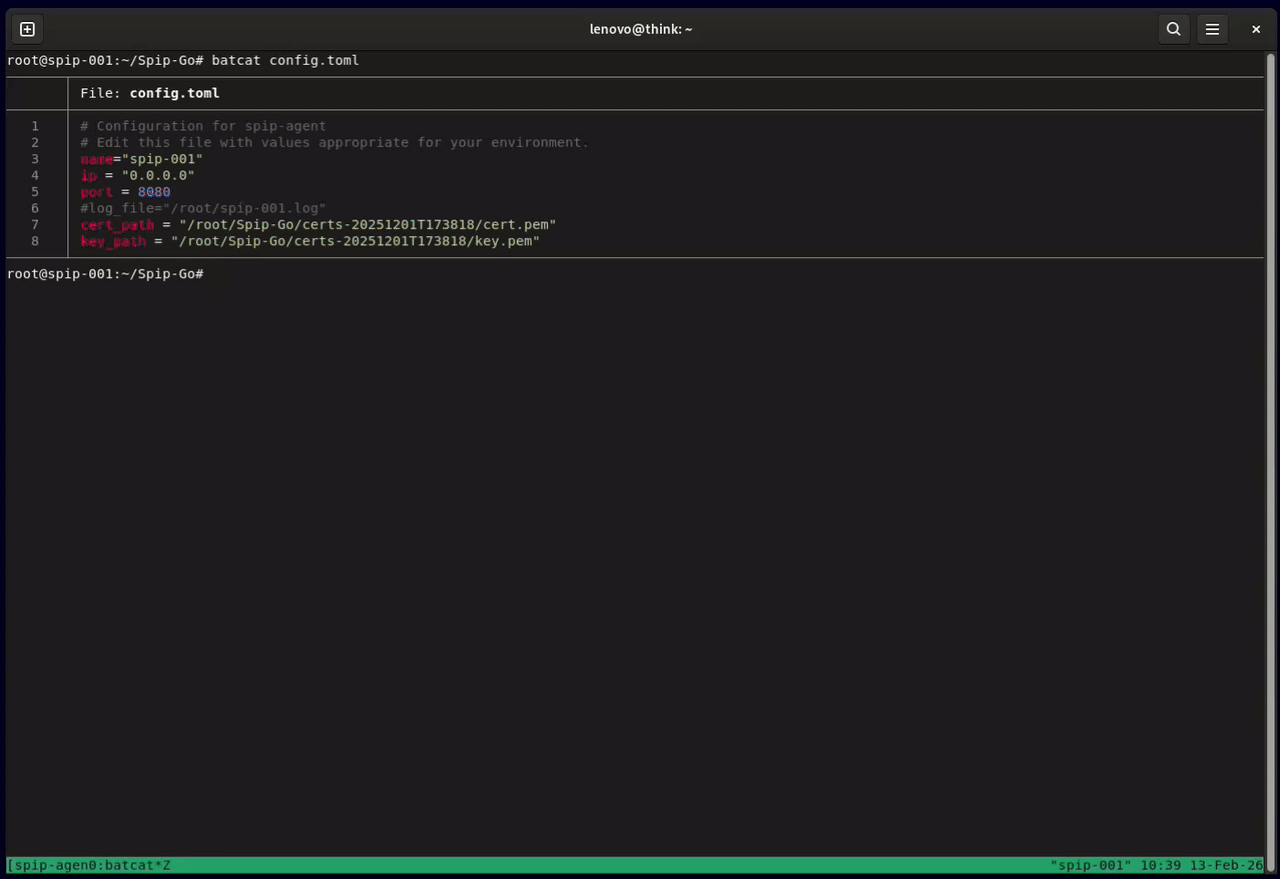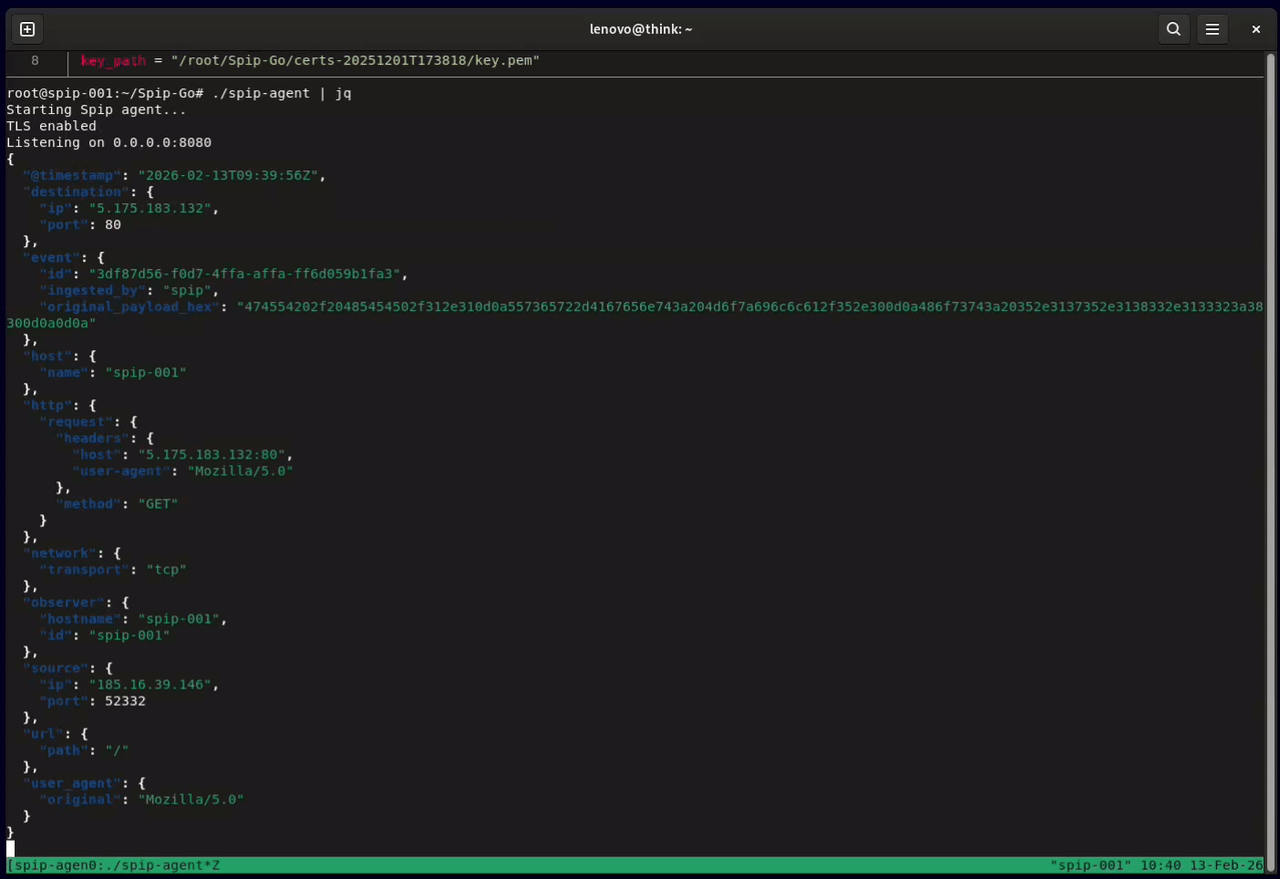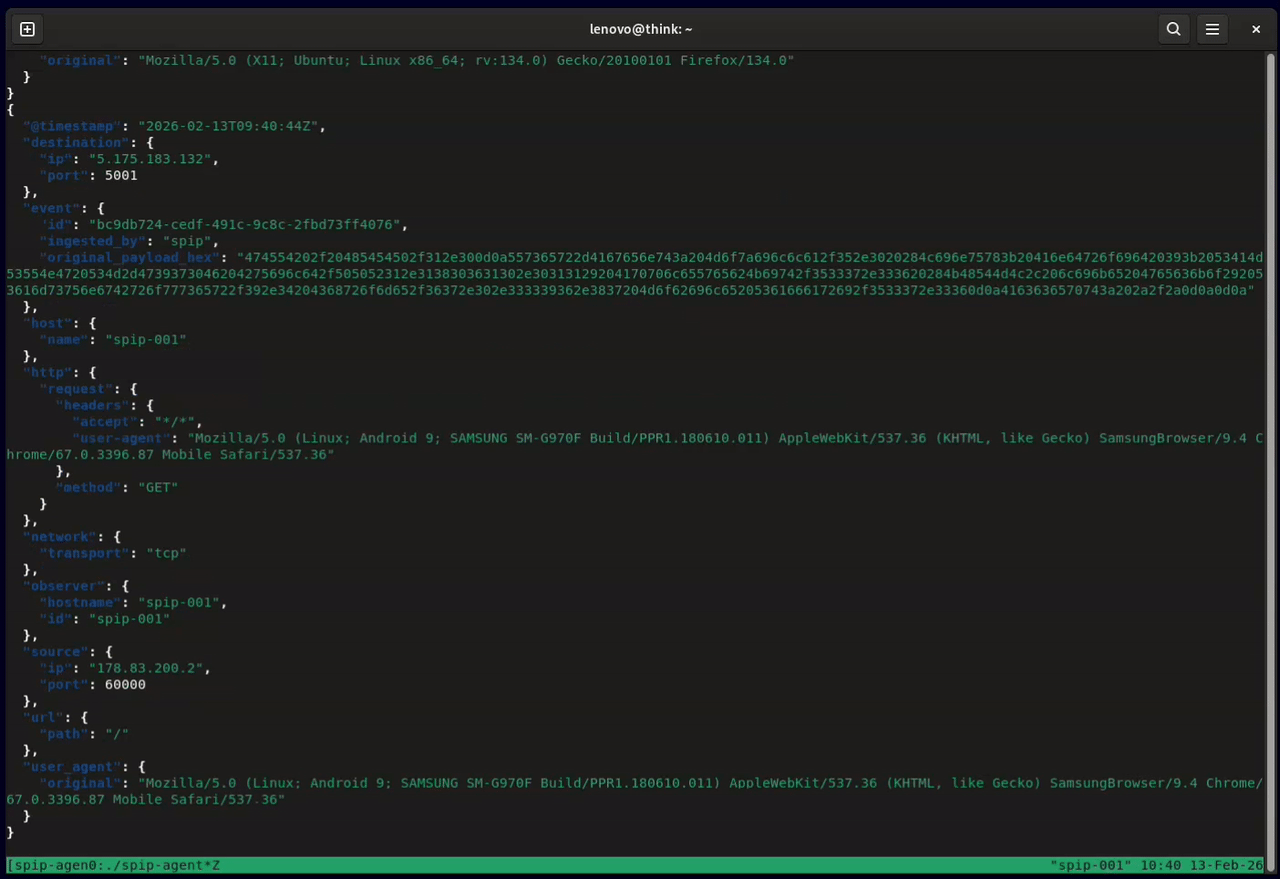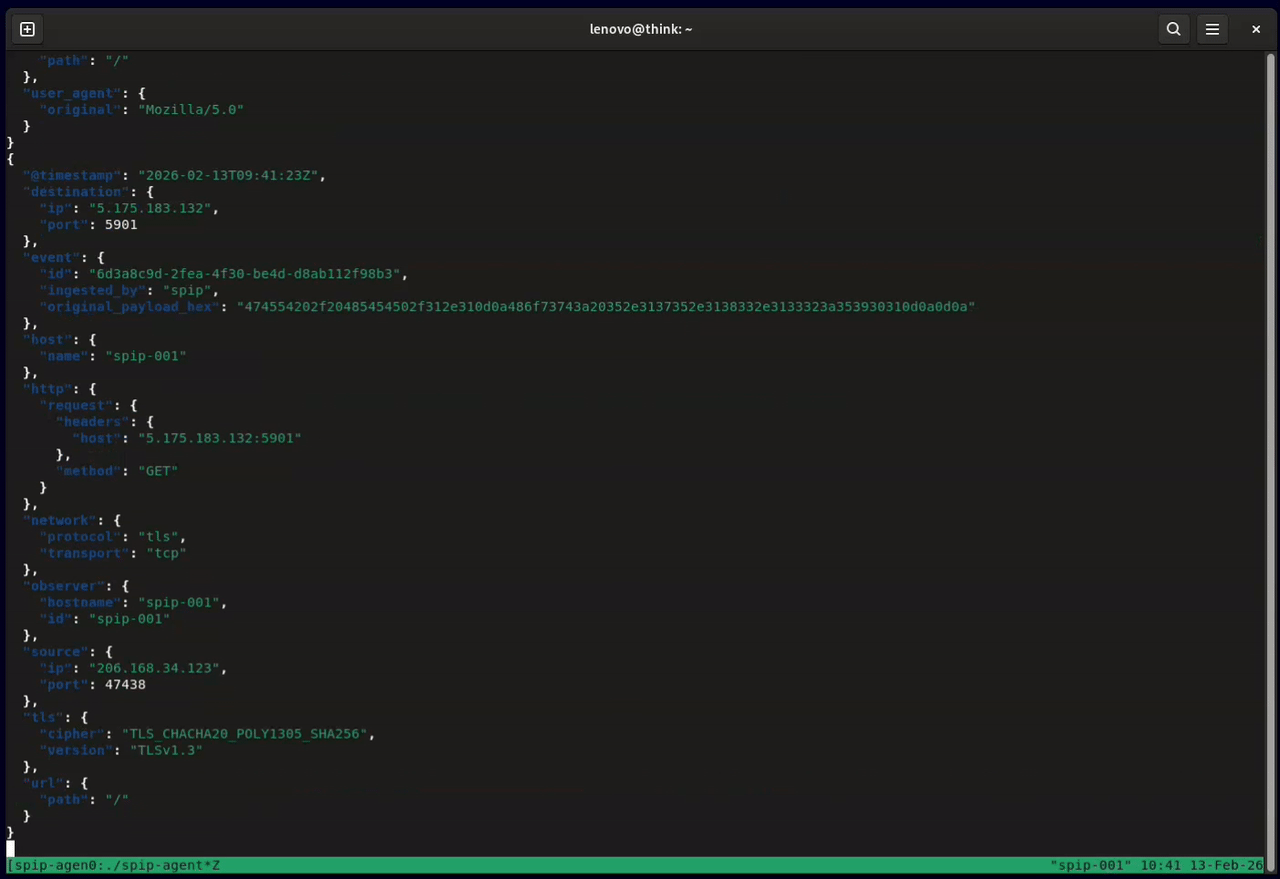 honeylabshq/spip-go
Spip network sensor written in Go
 abhinavbom/threat-intelligence-hunter
TIH is an intelligence tool that helps you in searching for IOCs across multiple openly available security feeds and some well known APIs. The idea…
 cronup/malware-iocs
Collects and organizes malware indicators of compromise (IOCs) for rapid threat detection, incident response, and actionable intelligence sharing.
 ctrlaltint3l/intelligence
Centralized repository for malware samples, threat intelligence, IOCs, and security tooling logs to support threat research and incident response…
 gyaansastra/cve-2022-30190
Comprehensive analysis of CVE-2022-30190 (Follina MSDT vulnerability) with IOCs, detection rules for SIEMs/EDR, YARA signatures, mitigation scripts,…
 limo57640-crypto/wp-user-registration-vuln-checker
Read-only WordPress User Registration CVE-2026-1492 checker for hidden admins, plugin version, uploads PHP, cron, and compromise IOCs.
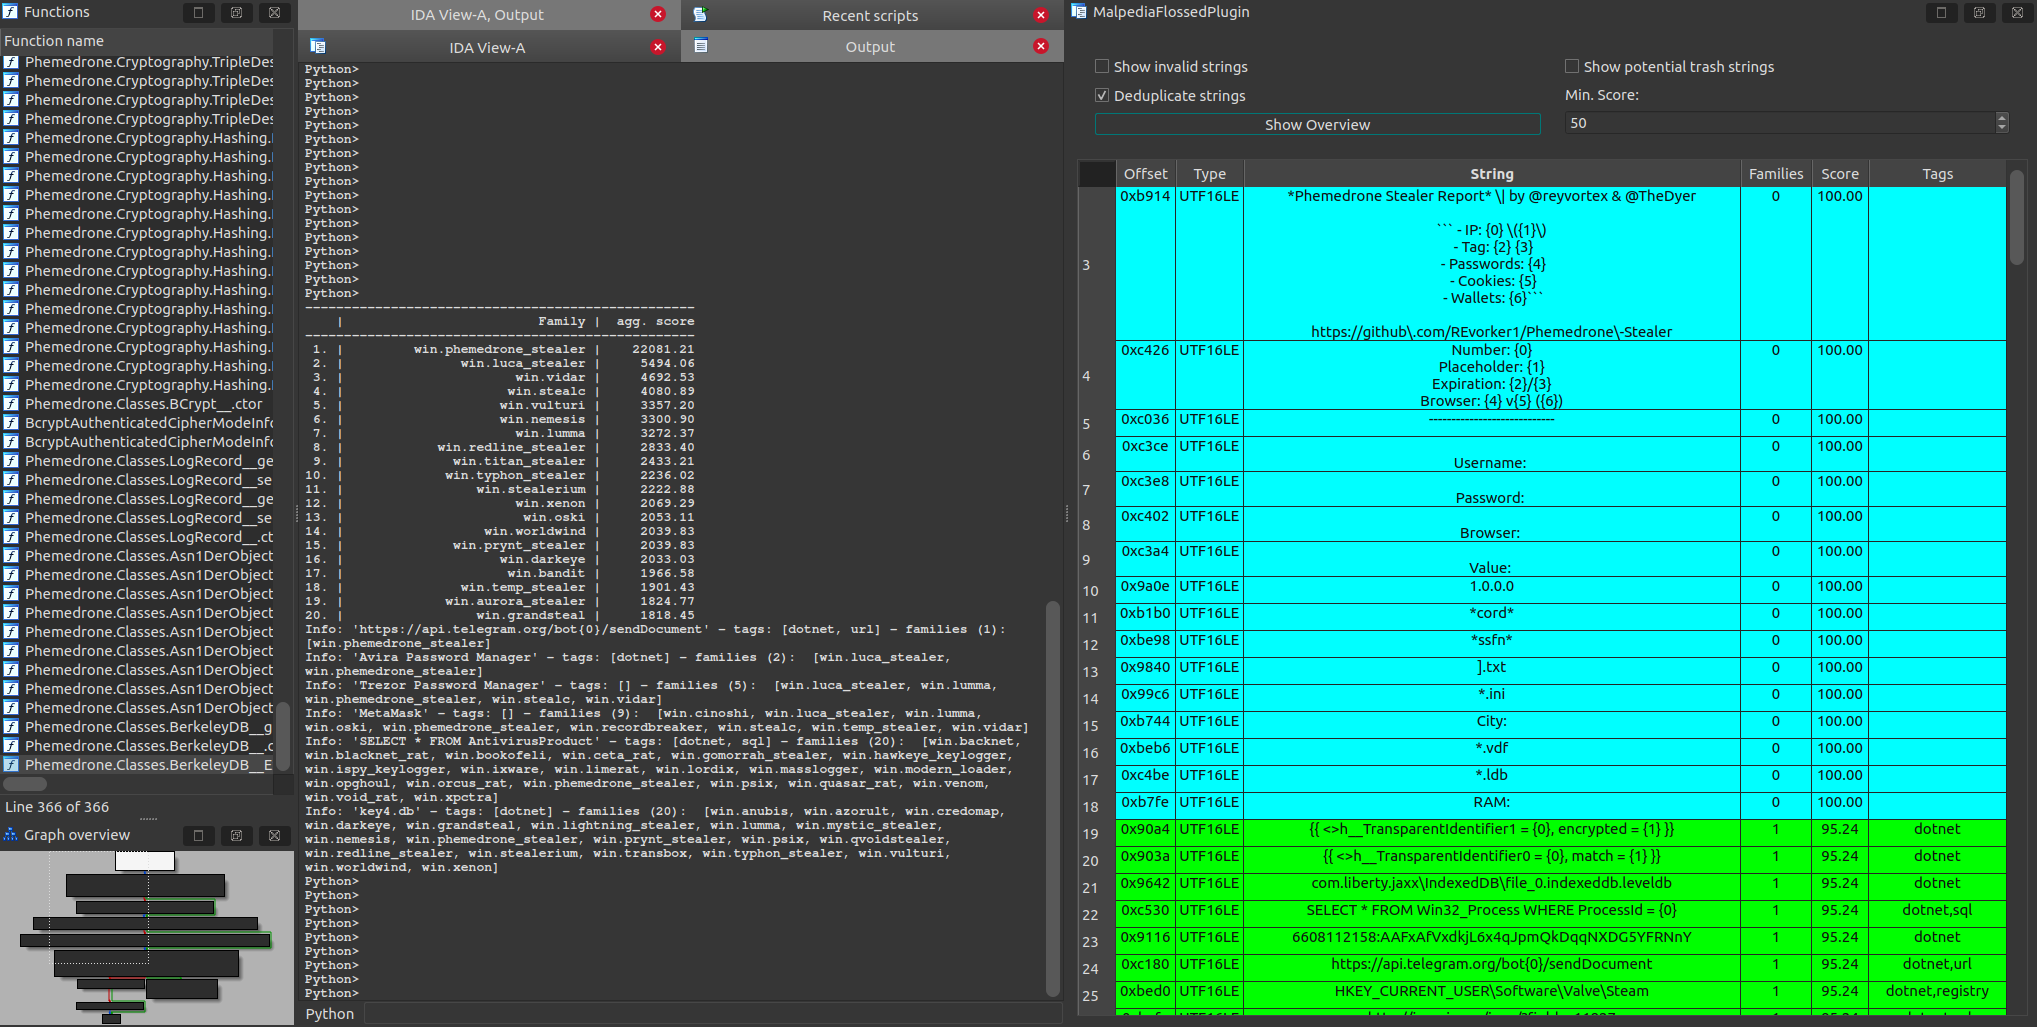 malpedia/malpedia-flossed
FLARE floss applied to all unpacked+dumped samples in Malpedia, pre-processed for further use.
 google/threat-team
No longer maintained. Please refer to Google Threat Intelligence / Virus Total collections.
 expel-io/expel-intel
This is the home of the Expel Intel Team. Here, we will share IOCs and other information that is either not suitable for fitting into other mediums…
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 jonathanstross/cve-2025-31324
A Python-based security scanner for identifying the CVE-2025-31324 vulnerability in SAP Visual Composer systems, and detecting known Indicators of…
 alexandreborges/malwoverview
Malwoverview is a first response tool for threat hunting across VirusTotal, Hybrid Analysis, URLHaus, Polyswarm, Malshare, Alien Vault, Malpedia,…