Open-Source-Threat-Intel-Feeds

A curated collection of free and publicly available Open Source Threat Intelligence feeds, covering IP addresses, domains, URLs, file hashes, CVEs,…

A curated collection of free and publicly available Open Source Threat Intelligence feeds, covering IP addresses, domains, URLs, file hashes, CVEs,…

Curated IPv4 blocklist of malicious addresses, refreshed every 6 hours for firewall and WAF ingestion, with split lists and CTI-ready formats for…

Automatically generated C2 threat intelligence feeds of IPs, domains, URL paths, and implant configuration metadata, derived from internet scanning…

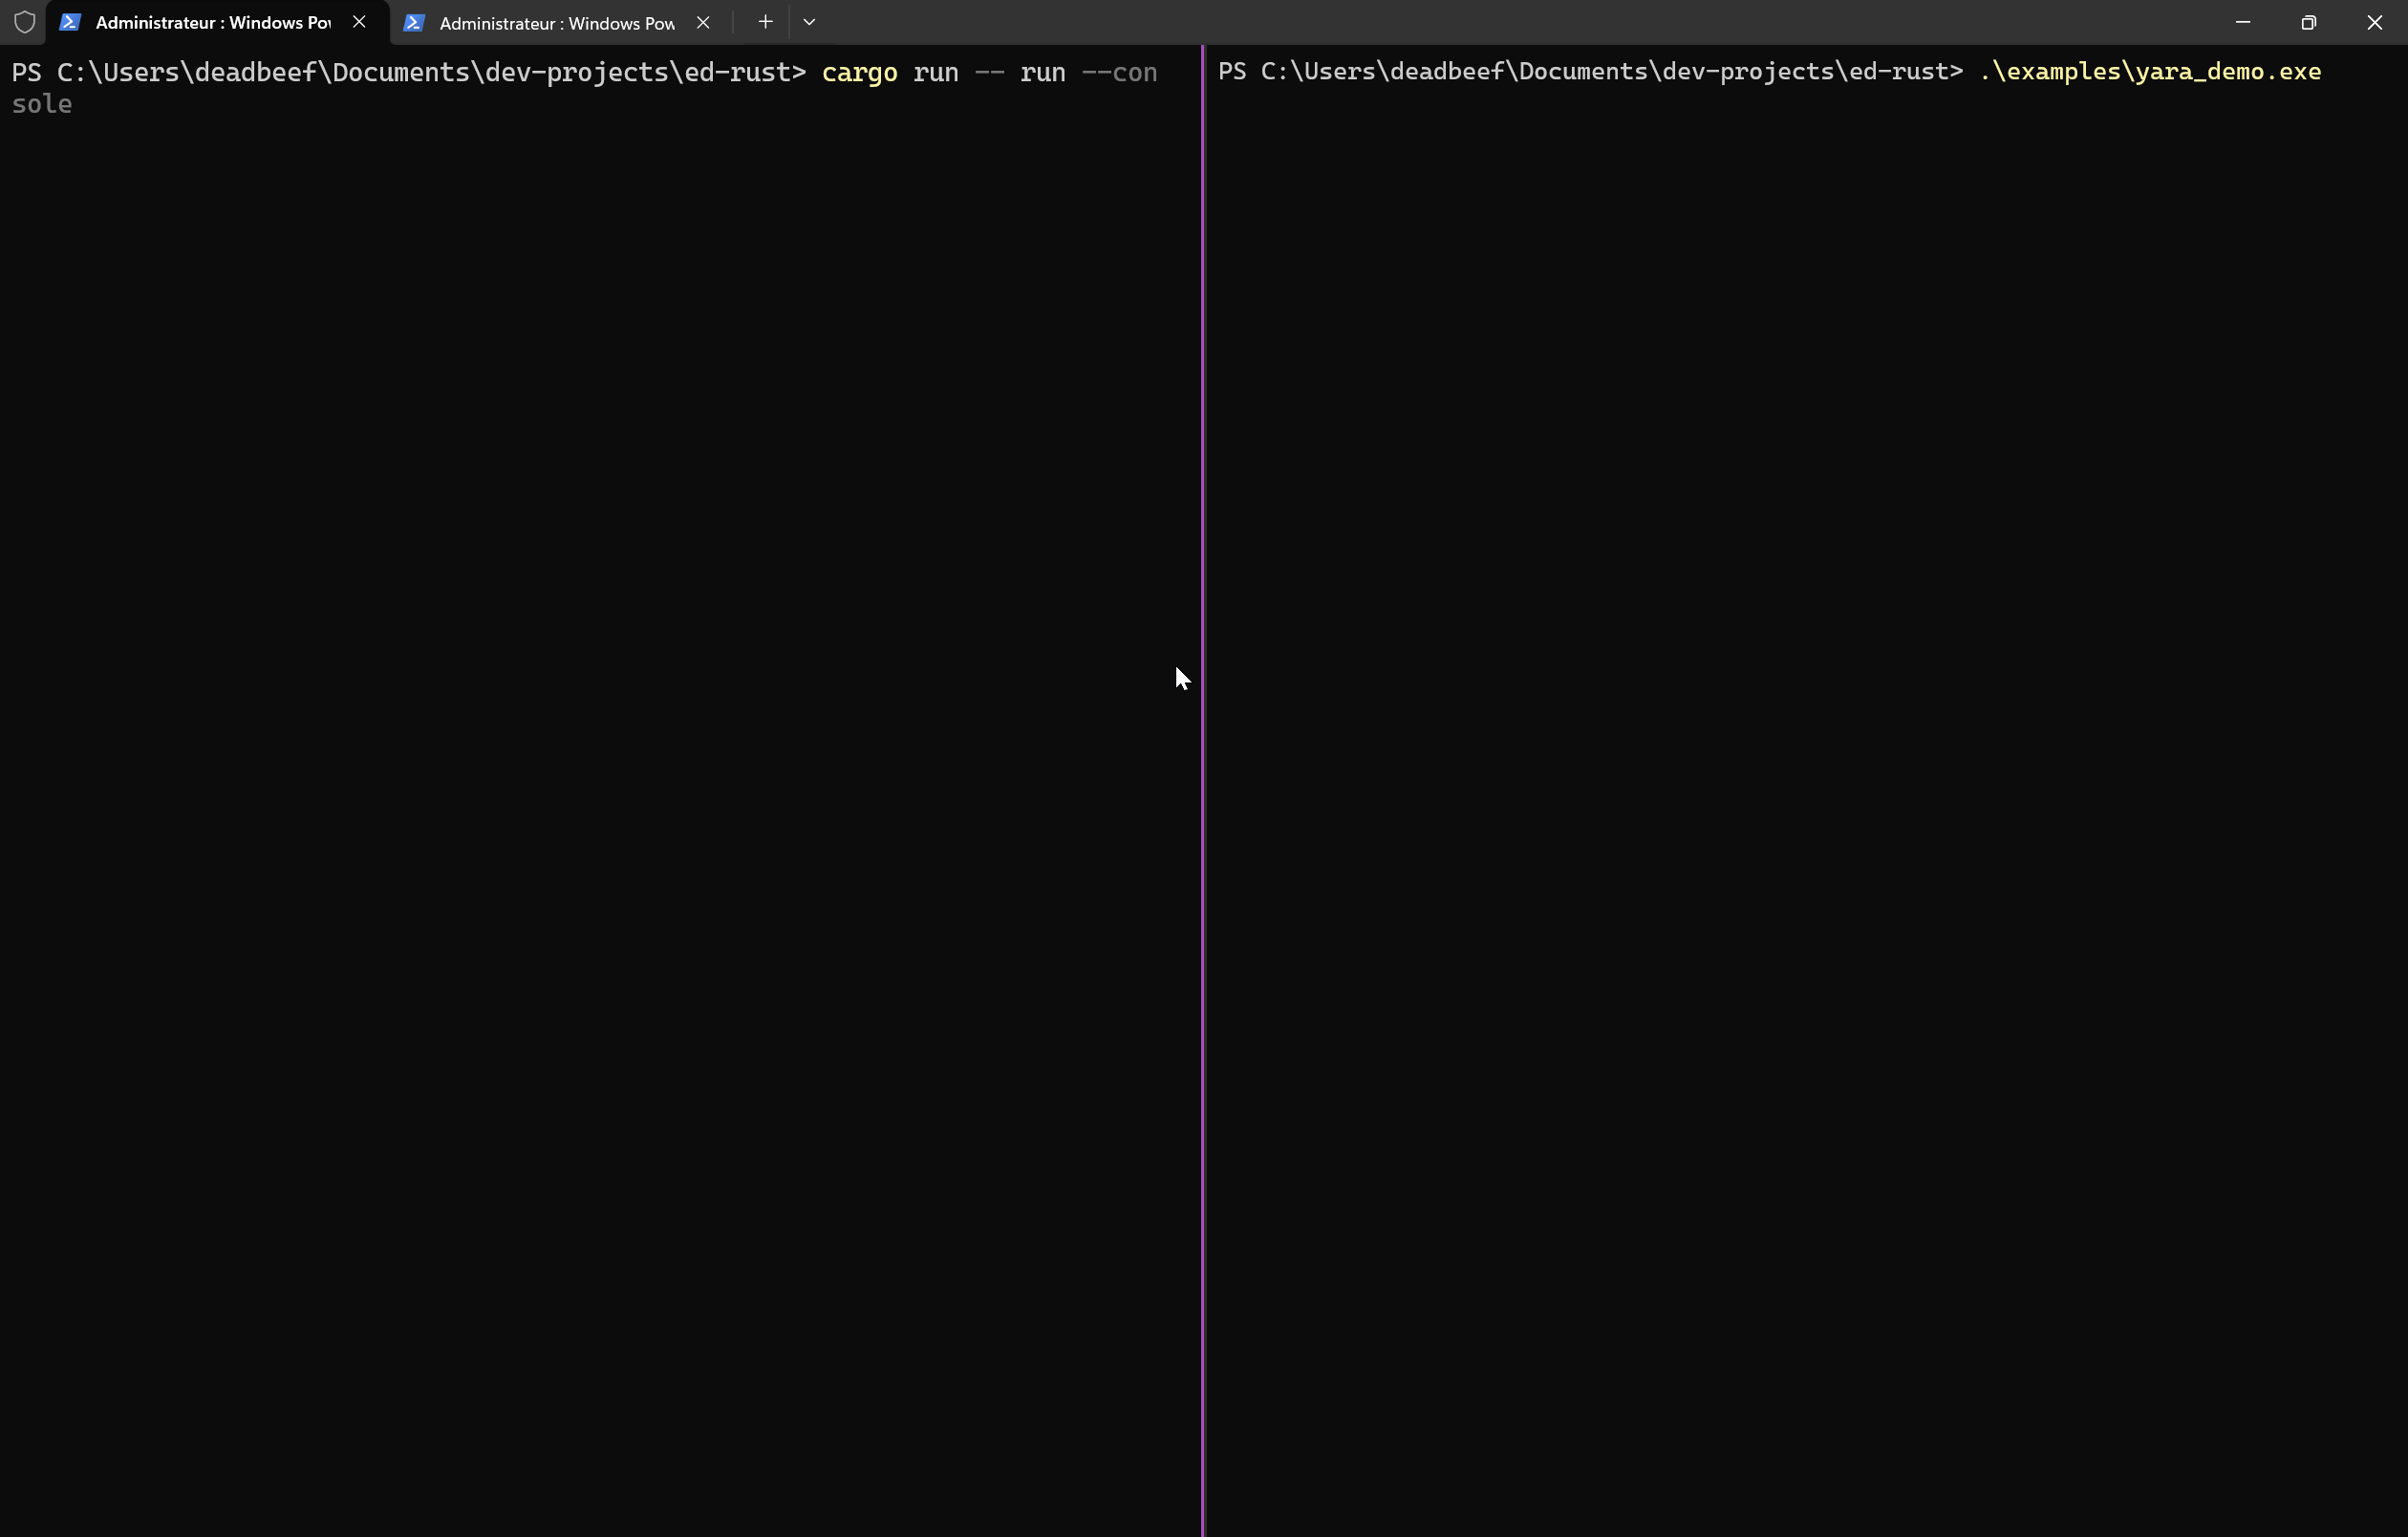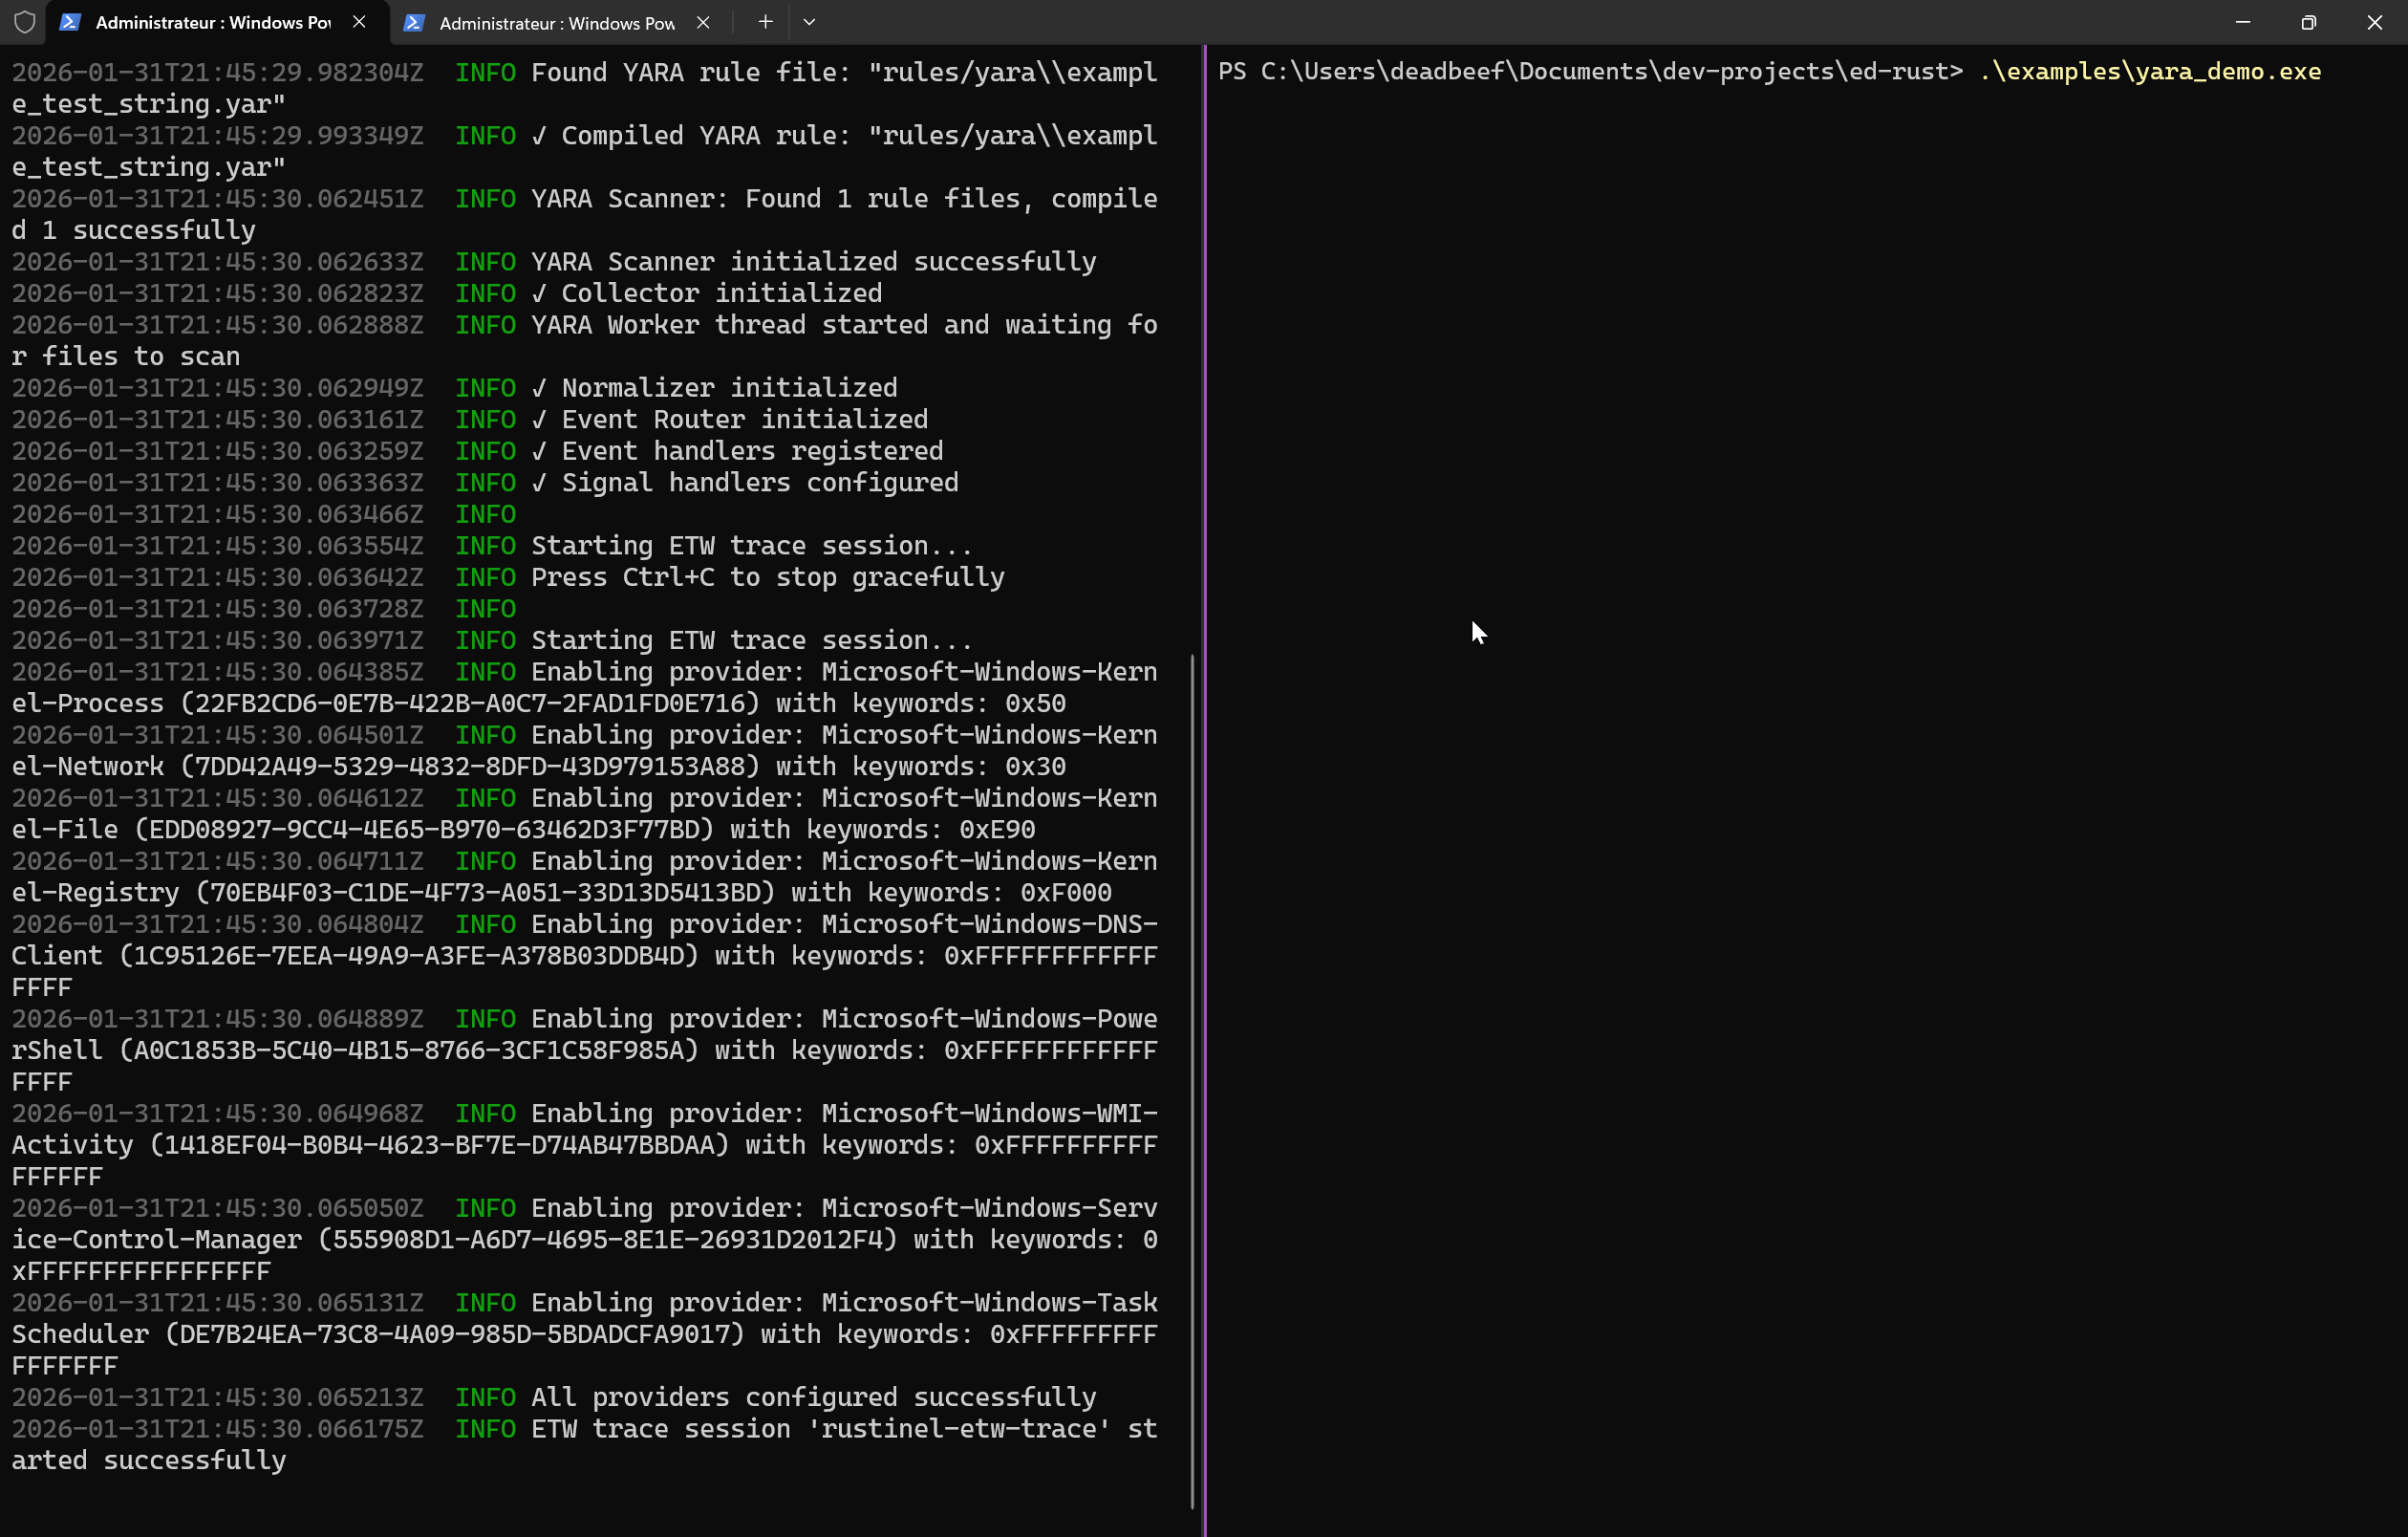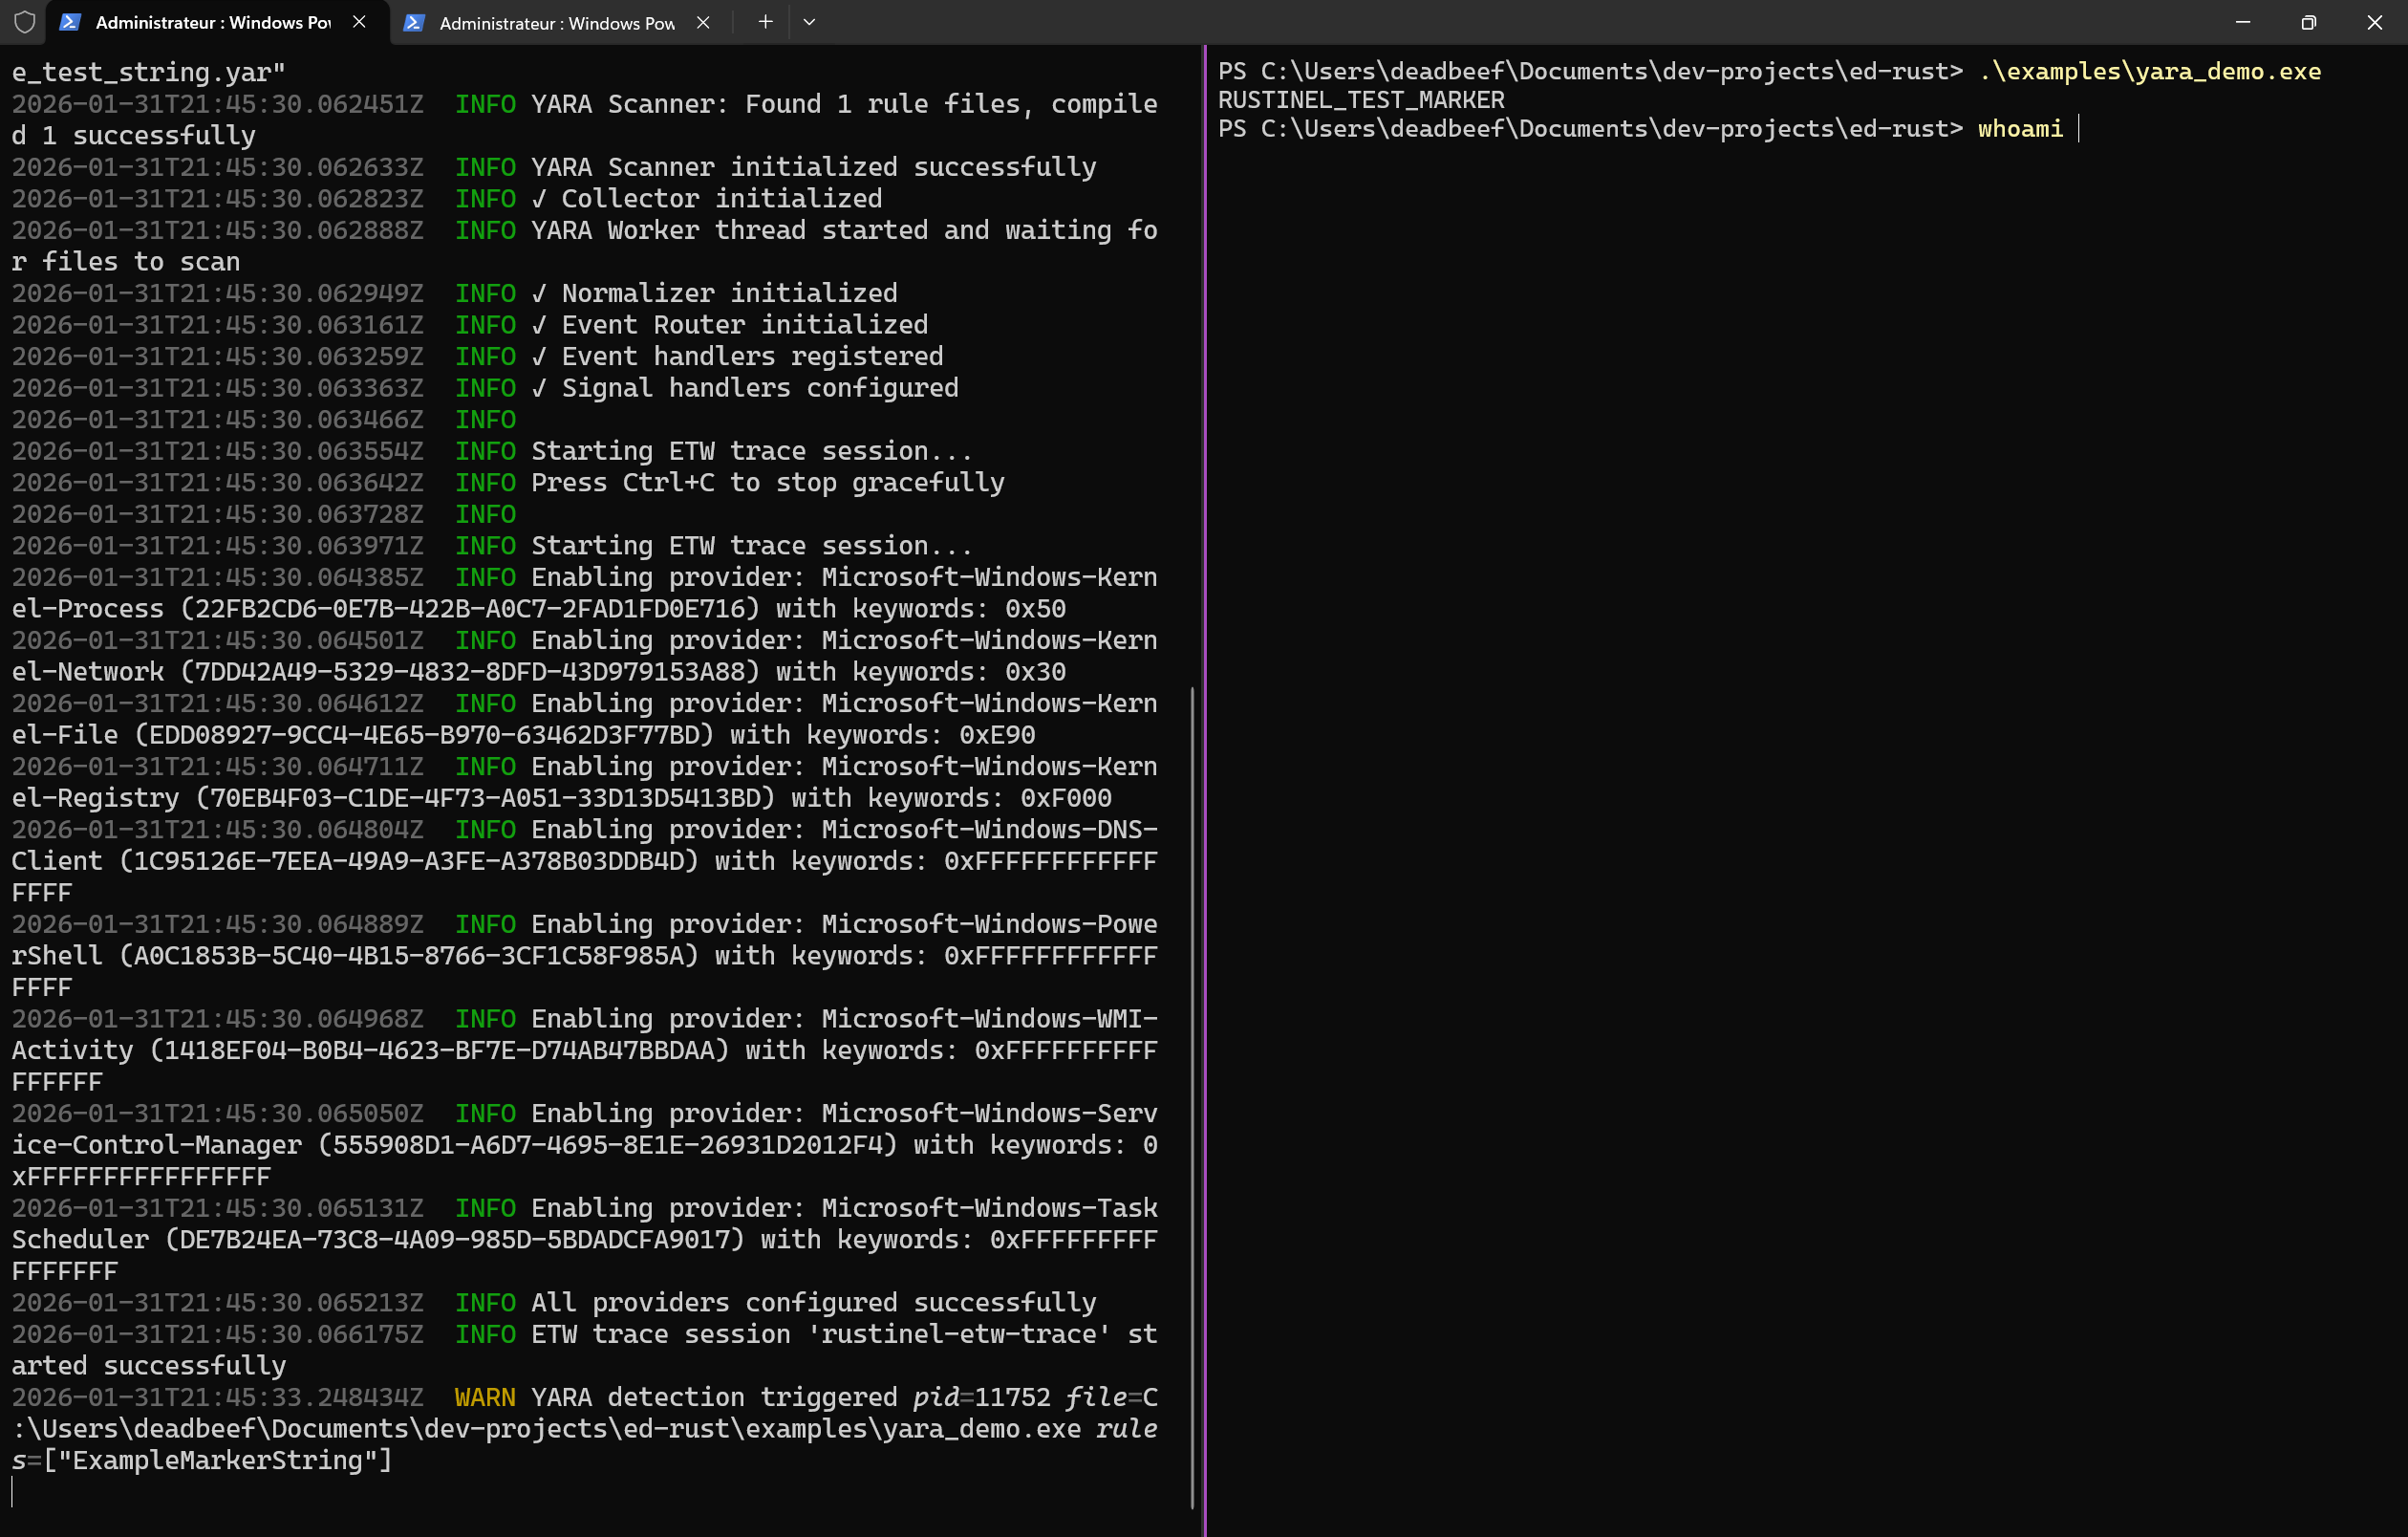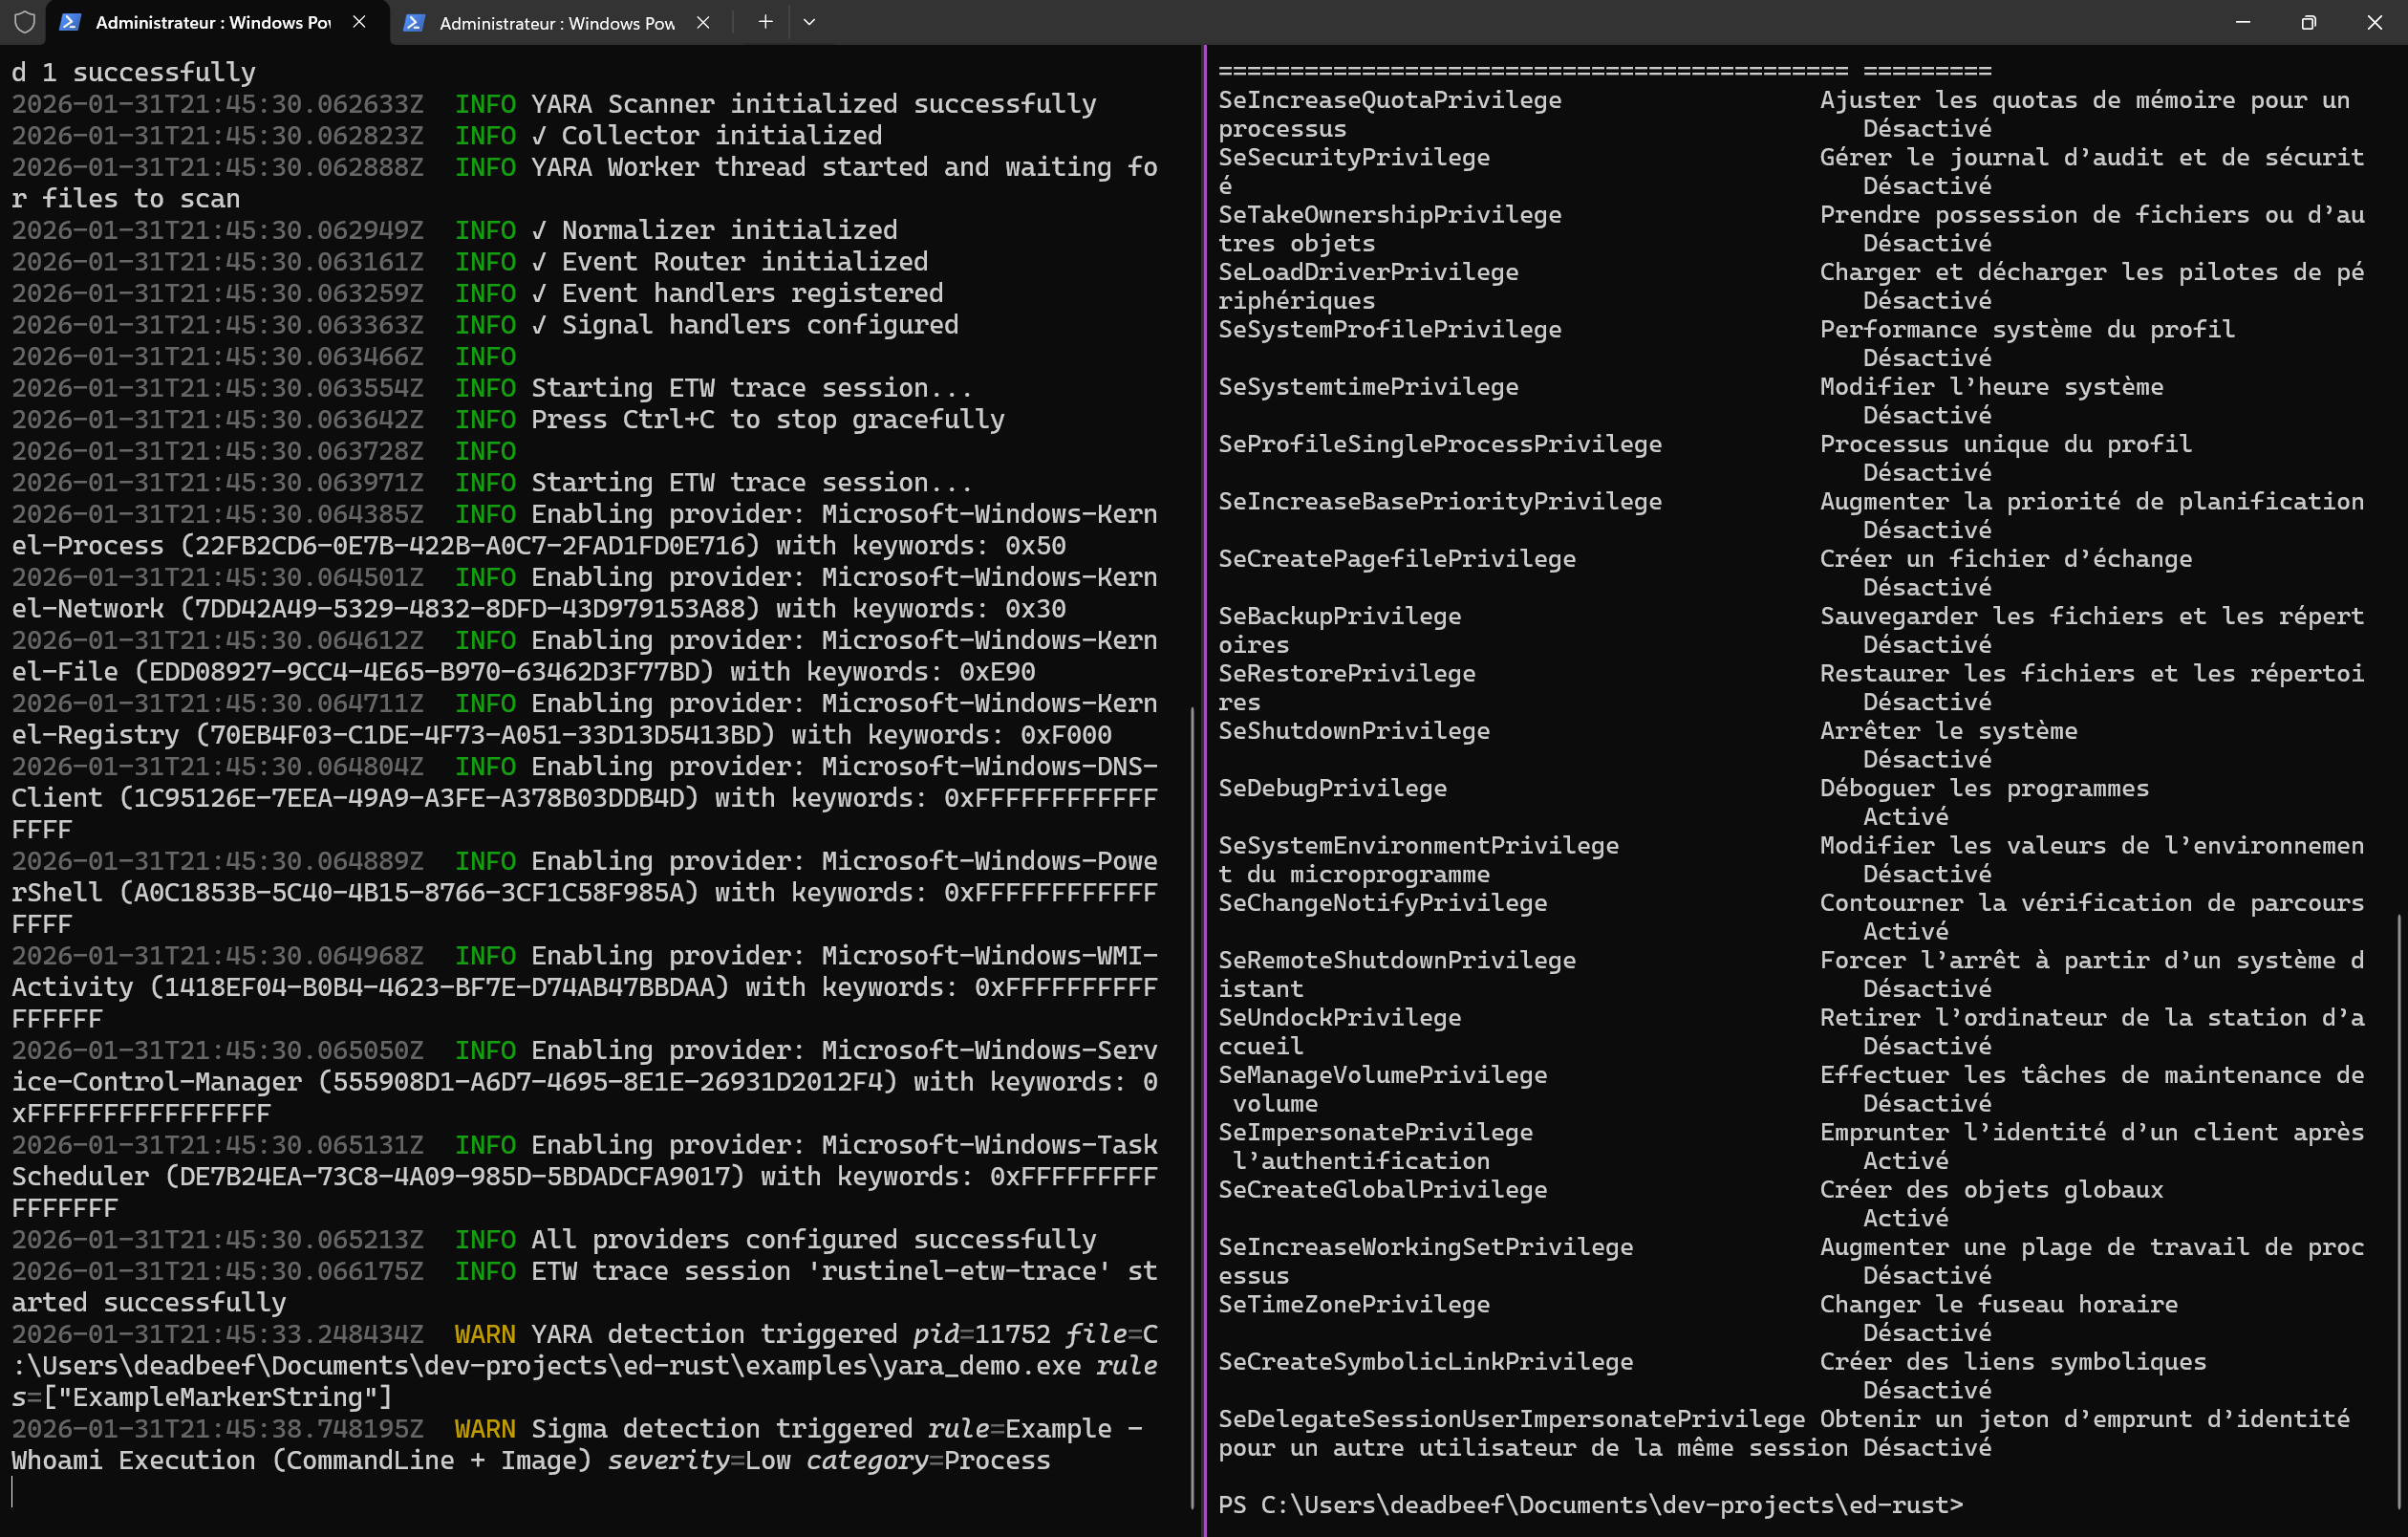
Endpoint detection for Windows, Linux, and macOS. Sigma, YARA, and IOC rules on native telemetry. Written in Rust. No cloud account required.

IoCs and YARA rules from Threatray's Threat Research

Indicators of Compromise for malware documented in whitepapers.


Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…

Curated Indicators of Compromise (IOCs) from Doctor Web malware investigations, published for threat intelligence, detection engineering, and…

Indicators of compromise from to analysis and research by Nextron Threat Research team

Collection of defensive security advisories and malware-analysis writeups covering developer-targeted malware, RCE backdoors, and vulnerability…

Read-only scanner for the backdoored Claude Code 2.1.313 extension (Cursor marketplace, Oct 2026): SSH key, persistence, reverse tunnel. macOS +…

This repository is for Indicators of Compromise (IOCs) from Zscaler ThreatLabz public reports


Plex2Shell (CVE-2026-96652/54/55/56) IOC/IOA dossier and read-only Windows hunt script

Read-only Linux check for Plex2Shell (CVE-2026-96652/-96654/-96655/-96656) exploitation and the XMRig/proxy payloads seen in the wild

Cortex: a Powerful Observable Analysis and Active Response Engine

Incident write-up: unsigned .so in the Plex Media Server codec cache executes a dropper on every transcode (CVE-2026-96656) — IOCs, STIX, YARA