

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
17 results
maltrail preview

maltrail

GitHubstamparm/maltrail

Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…

anomaly-detectionanti-botdefensive-tools+11
8.6k
22h 18m ago
mvt preview

mvt

GitHubmvt-project/mvt

Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…

android-securitydigital-forensicsdisk-forensics+7
15.5k1 day ago
cyberbro preview

cyberbro

GitHubstanfrbd/cyberbro

A simple application that extracts your IoCs from garbage input and checks their reputation using multiple CTI services.

defensive-toolsdns-analysiseducation+9
6953 days ago
ThreatLens preview

ThreatLens

GitHubabdaullahag/threatlens

Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…

defensive-toolsincident-responseinformation-gathering+7
251 month ago
IntelOwl preview

IntelOwl

GitHubintelowlproject/intelowl

Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…

curated-resourcesdigital-forensicsdynamic-analysis-sandboxing+14
4.8k1 month ago
windows-malware-behavioral-analysis preview

windows-malware-behavioral-analysis

GitHub0x0allenace/windows-malware-behavioral-analysis

Behavioral Malware Analysis of a Simulated Multi-Stage Windows Malware Sample using FLARE-VM and REMnux. Evidence-driven DFIR investigation with IOC…

digital-forensicsdynamic-analysis-sandboxingeducation+8
22 months ago
SPiCa preview

SPiCa

GitHub0xkirisame/spica

eBPF-based Linux rootkit detector using multi-channel cross-view analysis (sched_switch, NMI, /proc) to detect DKOM, tracepoint tampering, and…
anomaly-detectionbinary-analysisdefensive-tools+7
1053 months ago
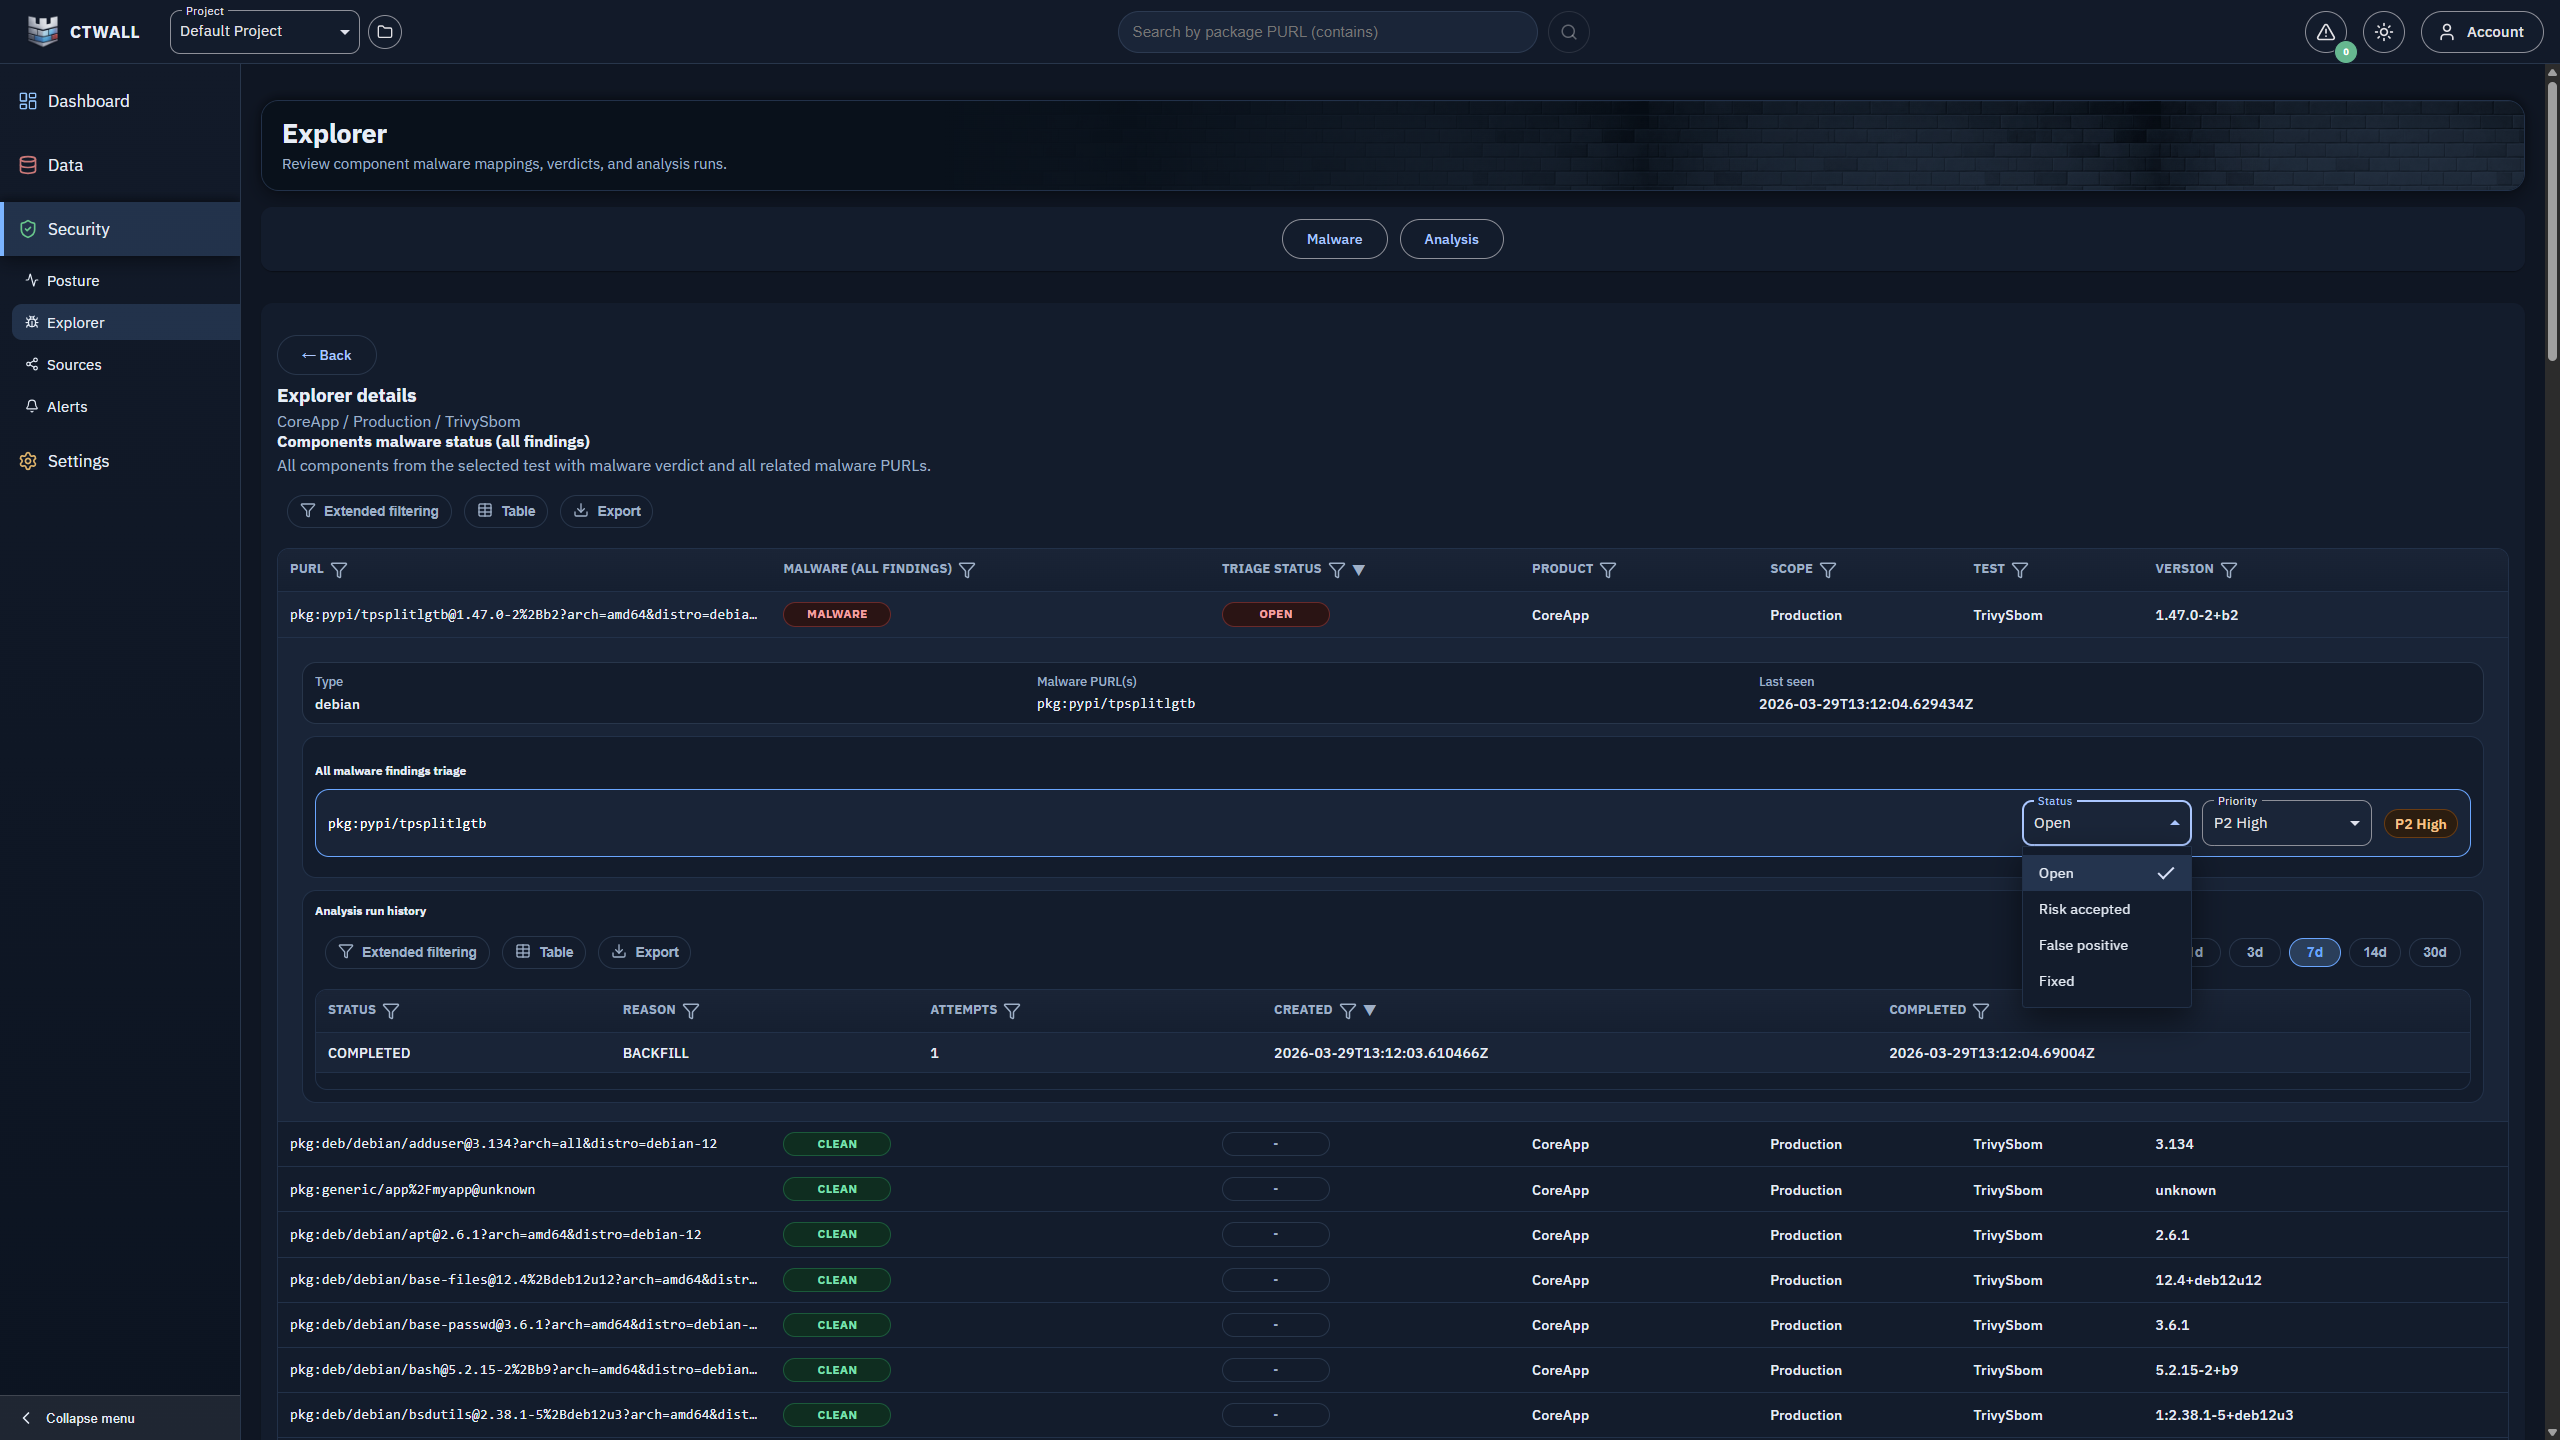
CTWall preview

CTWall

GitHubcybergabisoft/ctwall

CTWall (ChainThreatWall) platform helps Security, DevOps, and Product teams make risk decisions faster by using SBOM/BOM data to identify malware in…

cloud-securitycontainer-securitydevsecops+6
13 months ago
intelmq preview

intelmq

GitHubcerttools/intelmq

IntelMQ is a solution for IT security teams for collecting and processing security feeds using a message queuing protocol.
incident-responseinformation-gatheringintrusion-detection+6
1.1k6 months ago
SharePoint-ToolShell-CVE-2025-53770-Incident-Analysis preview

SharePoint-ToolShell-CVE-2025-53770-Incident-Analysis

GitHubzedocun/sharepoint-toolshell-cve-2025-53770-incident-analysis

Technical analysis of a SharePoint ToolShell (CVE-2025-53770) exploitation attempt involving RCE, webshell deployment, and MachineKey extraction.
digital-forensicseducationexploitation+7
16 months ago
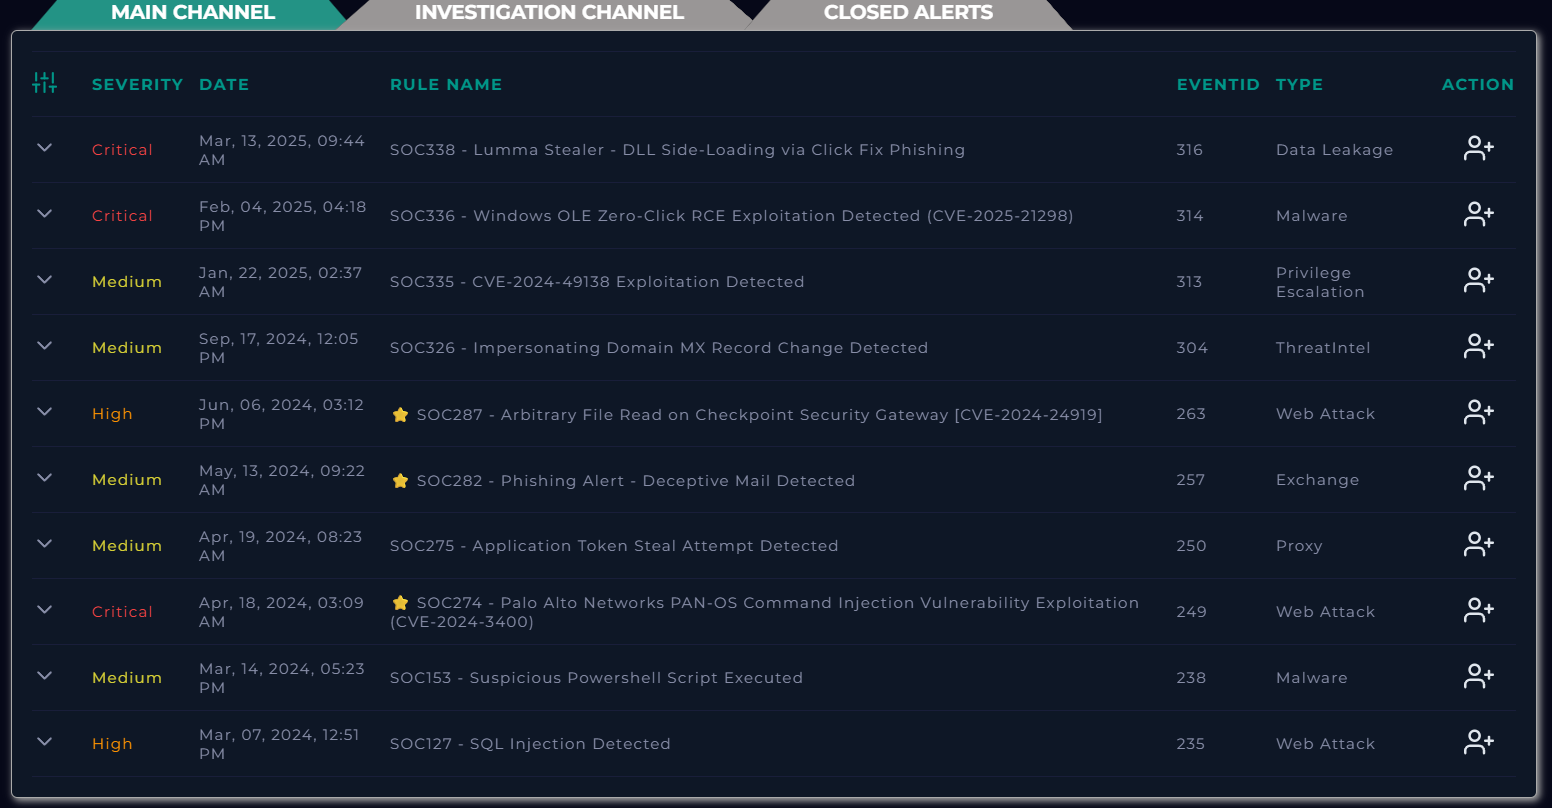
Zero-Click-RCE-Incident-Response-CVE-2025-21298 preview

Zero-Click-RCE-Incident-Response-CVE-2025-21298

GitHubtarunbharathe/zero-click-rce-incident-response-cve-2025-21298

Technical investigation and host containment of a Critical-severity Zero-Click RCE exploit (CVE-2025-21298) using EDR telemetry and static malware…
command-and-controldigital-forensicseducation+6
7 months ago
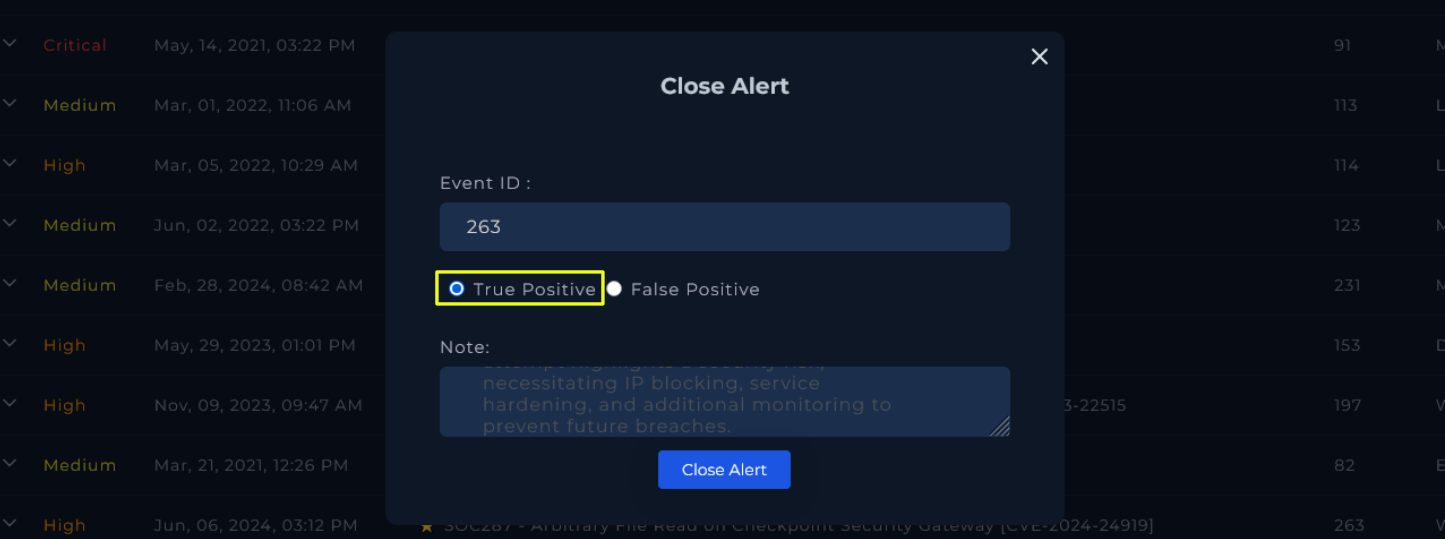
Detecting-and-Analyzing-CVE-2024-24919-Exploitation preview

Detecting-and-Analyzing-CVE-2024-24919-Exploitation

GitHubmacuchegit/detecting-and-analyzing-cve-2024-24919-exploitation

Step-by-step walkthrough of detecting and analyzing CVE-2024-24919 exploitation using a SIEM platform, including traffic analysis, IOC documentation,…
digital-forensicseducationincident-response+5
1 year ago
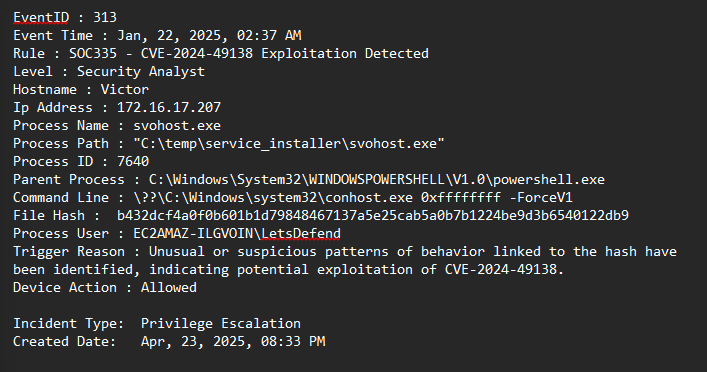
letsdefend-cve-2024-49138-investigation preview

letsdefend-cve-2024-49138-investigation

GitHubcyprianatsyor/letsdefend-cve-2024-49138-investigation

Hands-on SOC investigation of CVE-2024-49138 using LetsDefend, VirusTotal, Hybrid Analysis, TrueFort, and ChatGPT.
binary-exploitationdigital-forensicseducation+7
1 year ago
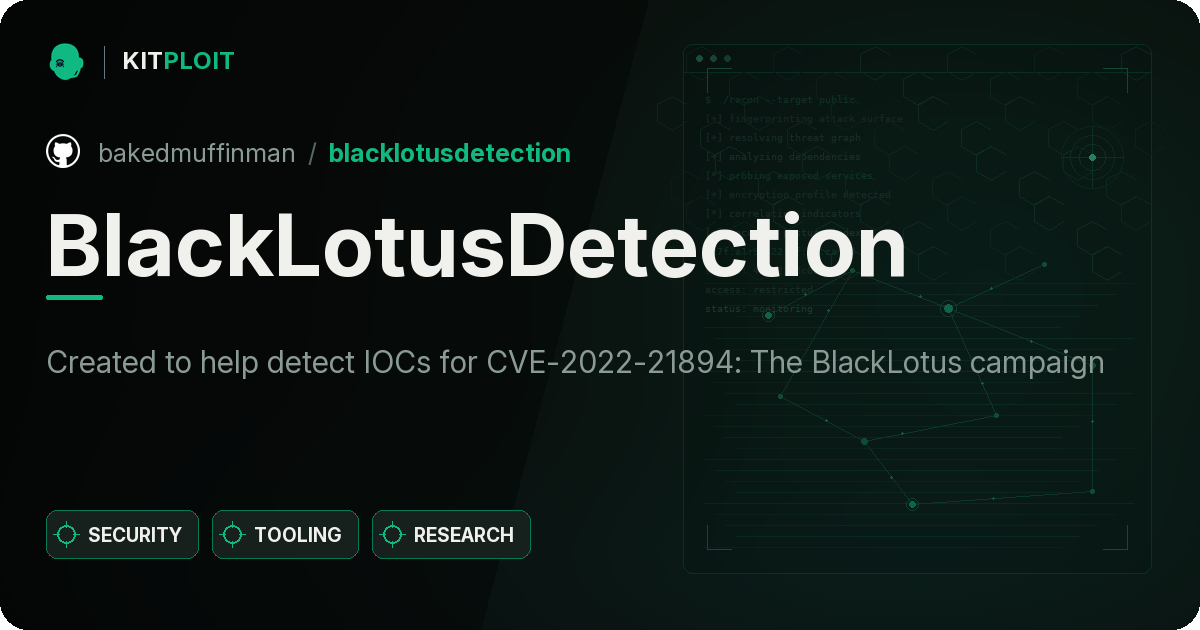
associated-threat-analyzer preview

associated-threat-analyzer

GitHubosmankandemir/associated-threat-analyzer

Detects malicious IPv4 addresses and domain names associated with a web application by comparing against local threat intelligence lists of known…
information-gatheringioc-managementreconnaissance+1
413 years ago
BlackLotusDetection preview

BlackLotusDetection

GitHubbakedmuffinman/blacklotusdetection

Created to help detect IOCs for CVE-2022-21894: The BlackLotus campaign
forensicsincident-responseioc-management+2
3 years ago
CVE-2022-26134-Exploit-Detection preview

CVE-2022-26134-Exploit-Detection

GitHubma1am/cve-2022-26134-exploit-detection

This repository contains Yara rule and the method that a security investigator may want to use for CVE-2022-26134 threat hunting on their Linux…

forensicsincident-responseioc-management+3
14 years ago
artillery preview

artillery

GitHubtrustedsec/artillery

Open-source blue team tool that protects Linux and Windows systems using multiple host and network defense and detection methods.

anomaly-detectiondefensive-toolshardware-iot-security+5
3396 years ago