
CAPEsolo
 capesandbox/capesolo
Standalone Windows VM malware sandbox running capemon, with GUI triage viewer, YARA signatures, IOC extraction, network analysis, and…
defensive-toolsdynamic-analysis-sandboxingforensics+7
28
capesandbox/capesoloStandalone Windows VM malware sandbox running capemon, with GUI triage viewer, YARA signatures, IOC extraction, network analysis, and…
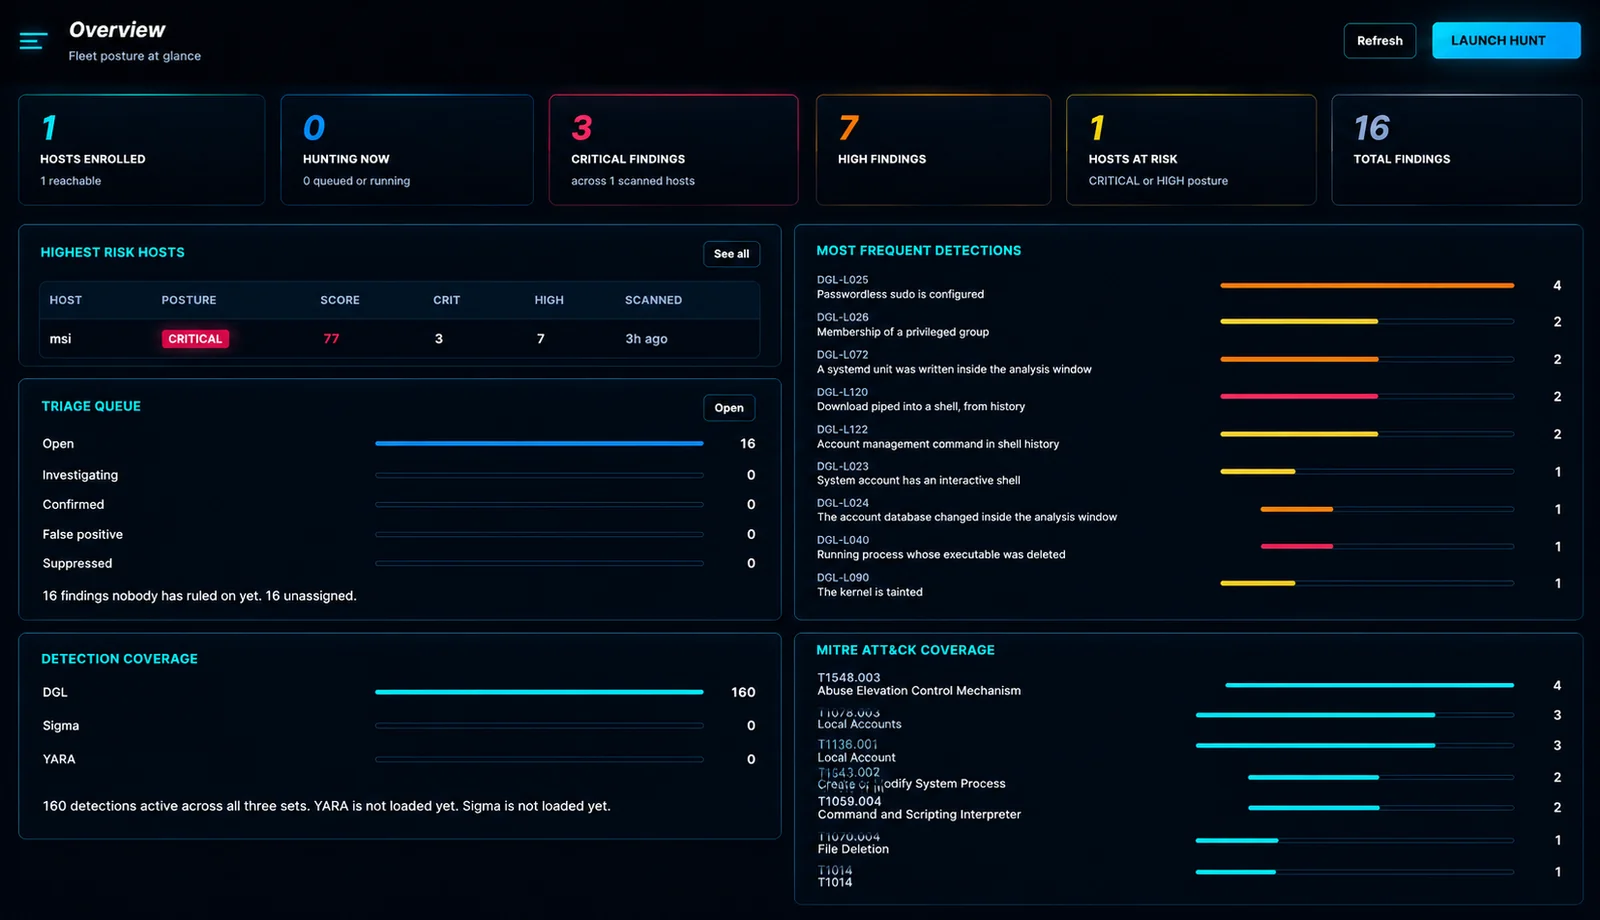 douglas-042/douglas-042-hq
Central console for Douglas-042 HEADQUARTERS collectors. Sweeps a fleet, correlates results across hosts, and manages IOC feeds and SIEM delivery…
 ethan-andrews/threatintel-aggregator
Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…
 duggytuxy/data-shield_ipv4_blocklist
Curated IPv4 blocklist of malicious addresses, refreshed every 6 hours for firewall and WAF ingestion, with split lists and CTI-ready formats for…
 fevar54/cve-2026-76461-detection-kit-
Defensive detection kit for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway, with Sigma and YARA rules, IOCs, and remediation…
 graphworlok/cve-2021-35394-ecosystem
Tracking the family of unrelated IoT botnets sharing CVE-2021-35394 as a delivery vector — findings, relationships, methodology.
 karim852/kage-dfir-toolkit
Windows host DFIR triage console that chains artefact collection, Sigma-correlated timelines, YARA scans, socket and account inspection, indicator…
 kaandemir993/stealc-stealer-runtimebroker-hollowing-c2-extraction-payload-extraction-analysis
Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…
 badchars/darknet-mcp-server
66-tool MCP server for dark web intelligence — breach data, ransomware tracking, Tor .onion access, malware analysis, blockchain intel, exploit…
 v-pun215/tourmaline
Reverse engineering notes, deobfuscated source, IOCs, and YARA rules for the Tourmaline ClickFix Python RAT, covering its DNS tunnel and blockchain…
 jithinkrishnanrs/cve-2026-86218-n-central-ioc-toolkit
Defensive IOC and detection toolkit for CVE-2026-86218, a critical pre-auth RCE in N-able N-central. Includes IOCs, log scanner, Sigma, Splunk,…
 jithinkrishnanrs/gitlab-cve-2026-85706-ioc
CVE-2026-85706 — GitLab Path Traversal IOC Scanner & Detection Toolkit. Detect and hunt for exploitation of the critical unauthenticated GitLab CE/EE…
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 zerodayvpn/cve-2026-41089-netlogon
🛡️ Official AI Security Tool diagnostic module for CVE-2026-41089 (Windows Netlogon Stack Buffer Overflow RCE). Features technical writeup, attack…
 svdwi/bluebox
Open-source threat intelligence platform for malware and observable analysis. Enriches IPs, domains, URLs, and hashes with external sources, performs…
 jithinkrishnanrs/stylesmuggler-ioc-toolkit
StyleSmuggler (CVE-2026-75650) IOC toolkit for Magento Open Source and Adobe Commerce. Detect compromised stores, Rust implants, PHP web shells,…
 fox-it/citrix-netscaler-triage
Forensic triage toolkit for Citrix NetScaler devices, featuring a Dissect-based IOC scanner for webshells, timestomping, and suspicious binaries,…
 dahnutz/zimbra-cve-2026-73570-ir
Detection-first incident-response toolkit for Zimbra administrators investigating CVE-2026-73570. Searches logs for exploit indicators, examines…