
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
26 results
plex2shell-check preview

plex2shell-check

GitHubchrislpjones/plex2shell-check

Read-only Linux check for Plex2Shell (CVE-2026-96652/-96654/-96655/-96656) exploitation and the XMRig/proxy payloads seen in the wild
defensive-toolsforensicsincident-response+5
116 days ago
netscaler_threat_hunt_helper preview

netscaler_threat_hunt_helper

GitHuborjanj/netscaler_threat_hunt_helper

NetScaler CTX697096 Threat Hunt Helper (IoC scanner) - CVE-2026-88771, CVE-2026-88772, CVE-2026-88779

defensive-toolsforensicsincident-response+7
7 days ago
claude-code-backdoor-check preview

claude-code-backdoor-check

GitHubhappyhackingspace/claude-code-backdoor-check

Read-only scanner for the backdoored Claude Code 2.1.313 extension (Cursor marketplace, Oct 2026): SSH key, persistence, reverse tunnel. macOS +…

defensive-toolsdigital-forensicsincident-response+4
15 days ago
C2IntelFeeds preview

C2IntelFeeds

GitHubdrb-ra/c2intelfeeds

Automatically generated C2 threat intelligence feeds of IPs, domains, URL paths, and implant configuration metadata, derived from internet scanning…
command-and-controldefensive-toolsincident-response+6
7491 day ago
Exploit-Index preview

Exploit-Index

GitHubsecurewithumer/exploit-index

Zero-API aggregator indexing 150k+ CVE exploits and PoCs from Exploit-DB, Nuclei, Metasploit, and CISA KEV, with EPSS/CVSS risk scoring for threat…
curated-resourcesexploitationinformation-gathering+8
1026h 42m ago
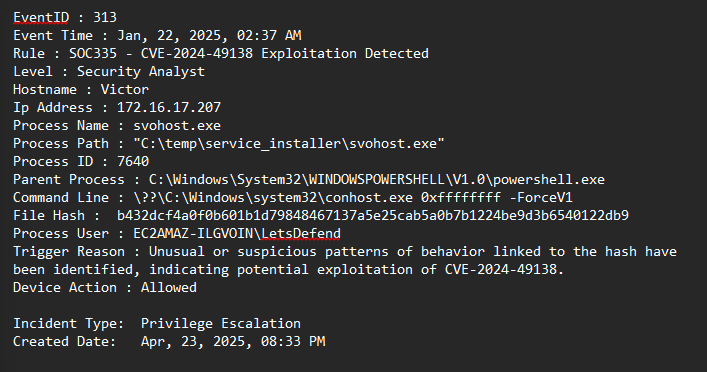
SOC335---CVE-2024-49138-Exploitation-Detected preview

SOC335---CVE-2024-49138-Exploitation-Detected

GitHubfabianch20/soc335---cve-2024-49138-exploitation-detected

SOC335 incident response walkthrough for CVE-2024-49138 CLFS privilege escalation, covering alert triage, threat intel enrichment, process tree…
digital-forensicseducationincident-response+7
1 month ago
ubuntils preview

ubuntils

GitHubasmitdesai/ubuntils

Python CLI/TUI for forensic triage of Ubuntu systems — detects and remediates persistence mechanisms with artifact collection, timeline correlation,…
configuration-auditingdefensive-toolsdigital-forensics+7
420 days ago
Windows-Defender-Security-Auditor-CVE-2026-50656- preview

Windows-Defender-Security-Auditor-CVE-2026-50656-

GitHubeh-amish/windows-defender-security-auditor-cve-2026-50656-

Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…

configuration-auditingdefensive-toolsincident-response+8
12 months ago
PayloadAutomation preview

PayloadAutomation

GitHubemcghee/payloadautomation

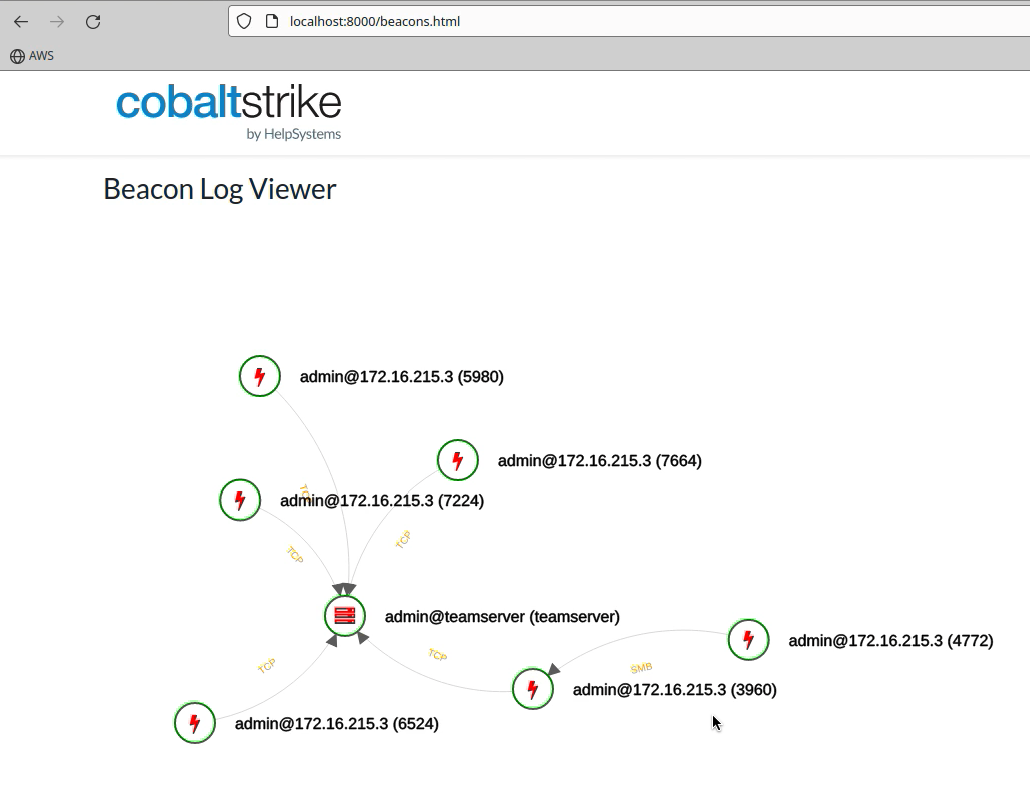
Automates Cobalt Strike payload development, testing, and deployment via a Python-to-Sleep bridge; includes artifact inspection, IoC tracking, and…
command-and-controlioc-managementpayload-development+3
1204 years ago
sleep_python_bridge preview

sleep_python_bridge

GitHubcobalt-strike/sleep_python_bridge

This project is 'bridge' between the sleep and python language. It allows the control of a Cobalt Strike teamserver through python without the need…
command-and-controlioc-managementlog-analysis+3
1881 year ago
ncentral-compromise-ioc-triage preview

ncentral-compromise-ioc-triage

GitHubcreamyg31337/ncentral-compromise-ioc-triage

Read-only N-able N-central CVE-2026-18556/CVE-2026-18577 post-exploitation IoC hunter for Windows endpoints

defensive-toolsdigital-forensicsincident-response+4
3 months ago
CVE-2026-60206 preview

CVE-2026-60206

GitHub0xblackash/cve-2026-60206

CVE-2026-60206

authenticationeducationincident-response+4
23 months ago
letsdefend-cve-2024-49138-investigation preview

letsdefend-cve-2024-49138-investigation

GitHubcyprianatsyor/letsdefend-cve-2024-49138-investigation

Hands-on SOC investigation of CVE-2024-49138 using LetsDefend, VirusTotal, Hybrid Analysis, TrueFort, and ChatGPT.
binary-exploitationdigital-forensicseducation+7
1 year ago
tanstack-compromise-checker preview

tanstack-compromise-checker

GitHubry-allan/tanstack-compromise-checker

Detects CVE-2026-45321 (TanStack supply chain compromise) and Mini Shai-Hulud worm artifacts. Scans node_modules, lockfiles, persistence hooks…
command-and-controlforensicsincident-response+6
5 months ago
mini-shai-hulud-scanner preview

mini-shai-hulud-scanner

GitHubintrudify/mini-shai-hulud-scanner

Scanner for the Mini Shai-Hulud npm/PyPI supply chain worm (NHS CC-4781 · CVE-2026-45321). Detects gh-token-monitor persistence, payload artefacts,…
forensicsincident-responseioc-management+6
25 months ago
LockBit-Ransomware-Analysis preview

LockBit-Ransomware-Analysis

GitHubvignesh-hp/lockbit-ransomware-analysis

Threat intelligence and incident response case study on LockBit ransomware exploiting CVE-2023-4966 (Citrix Bleed).
data-exfiltrationdigital-forensicseducation+8
8 months ago
litespeed-cpanel-cve-2026-54420-fix preview

litespeed-cpanel-cve-2026-54420-fix

GitHubmahfuzreham/litespeed-cpanel-cve-2026-54420-fix

Defensive remediation and auditing toolkit for CVE-2026-54420 in LiteSpeed cPanel Plugin. Automates patching, detects suspicious symlinks, hunts…
cloud-securityconfiguration-auditingdefensive-tools+7
14 months ago
notepadpp-supply-chain-iocs preview

notepadpp-supply-chain-iocs

GitHubrenat0z3r0/notepadpp-supply-chain-iocs

IoCs and detection rules for the Notepad++ supply chain attack (CVE-2025-15556) — Lotus Blossom APT, June–December 2025. Includes Falcon LogScale…

educationforensicsincident-response+6
18 months ago
Previous12Next