
OmniTriage
 prox0959/omnitriage
Zero-dependency, sub-second Windows live digital forensics & incident response (DFIR) triage engine for USB responders.
defensive-toolsdigital-forensicsforensics+8
1
prox0959/omnitriageZero-dependency, sub-second Windows live digital forensics & incident response (DFIR) triage engine for USB responders.
 asmitdesai/ubuntils
Python CLI/TUI for forensic triage of Ubuntu systems — detects and remediates persistence mechanisms with artifact collection, timeline correlation,…
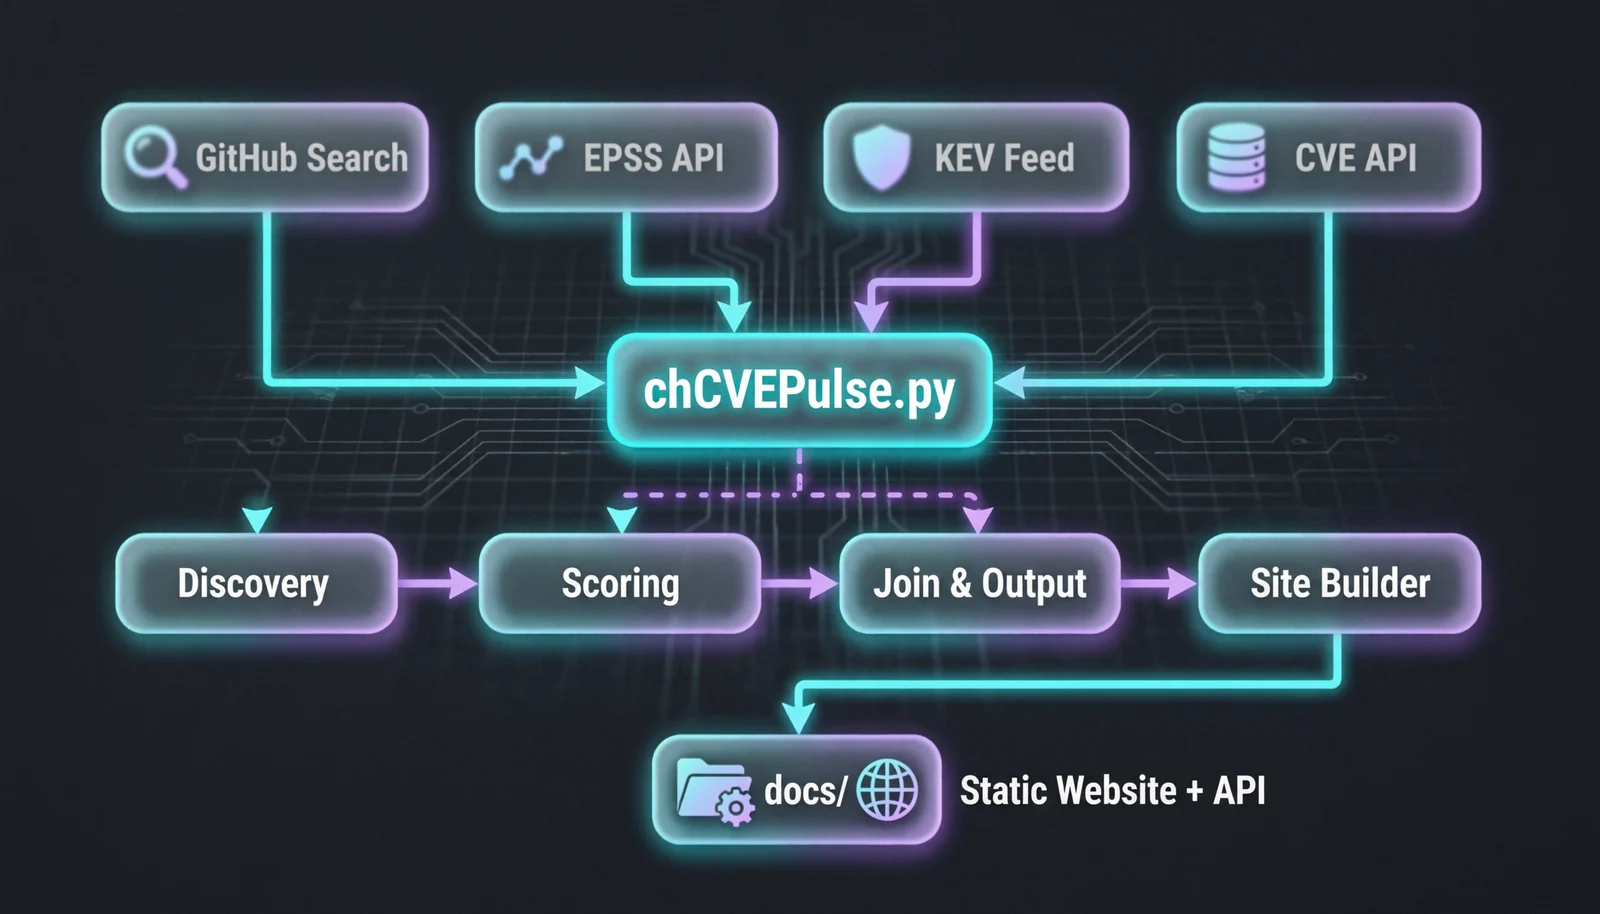 ch4120n/ch4120n-cve-pulse
Live CVE PoC (Proof-of-Concepts) Aggregator with Smart Search & Threat Intelligence
 wadesweaponshed/cve-2026-93616_checks
Shell and SmartDashboard scripts that check Check Point management servers for indicators of compromise tied to CVE-2026-93616, including rogue…
 soc-irdoc/irdoc-app
Incident Response Documentation Platform
 capesandbox/capesolo
Standalone Windows VM malware sandbox running capemon, with GUI triage viewer, YARA signatures, IOC extraction, network analysis, and…
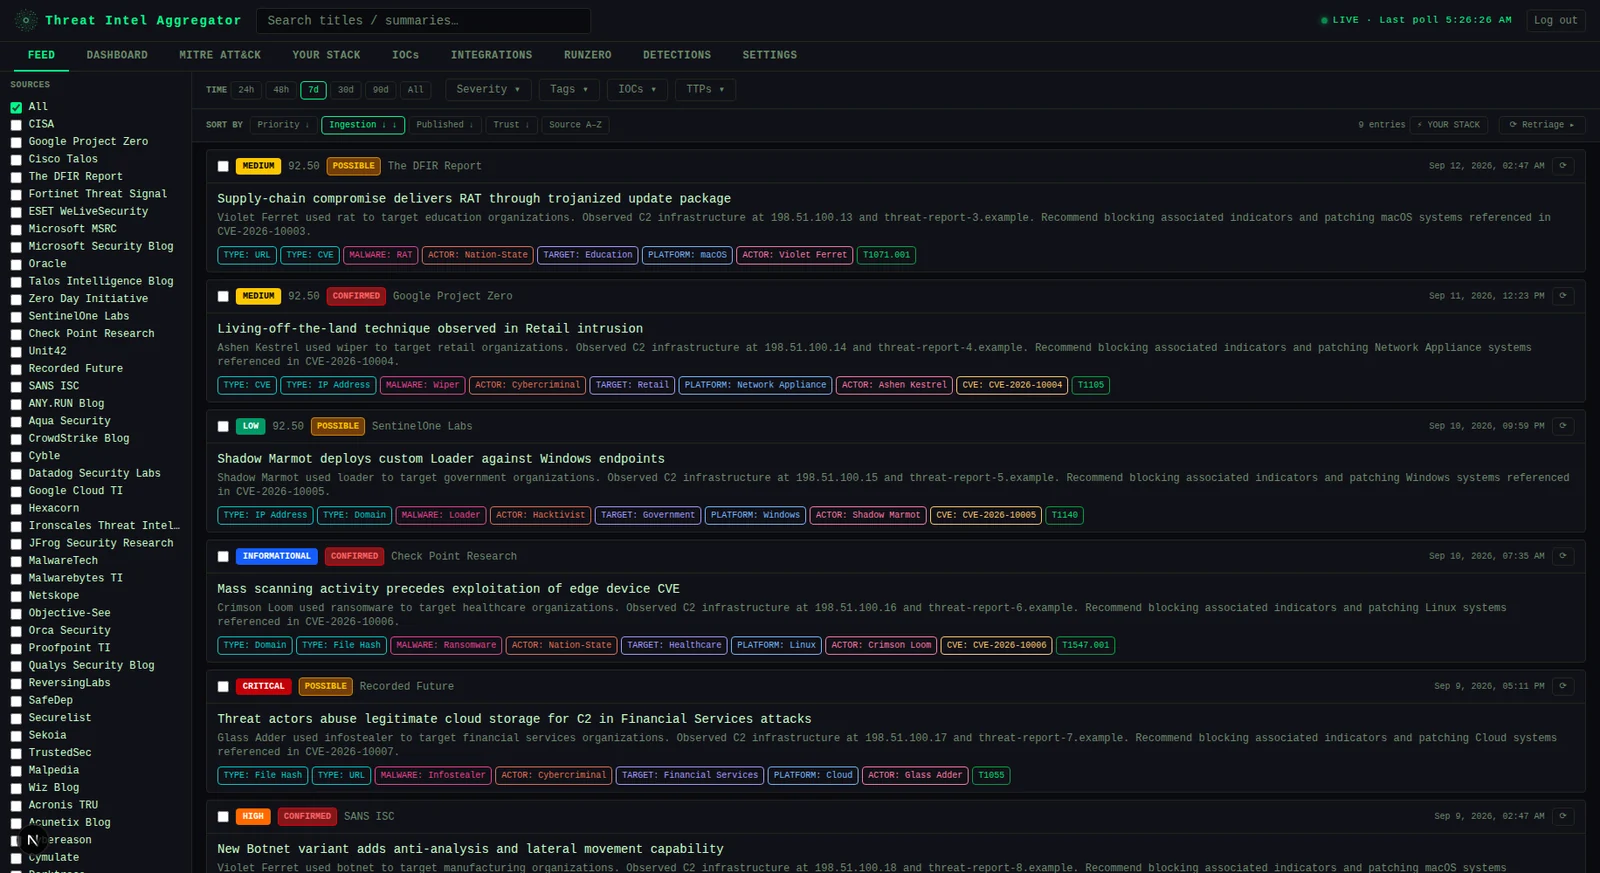 ethan-andrews/threatintel-aggregator
Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…
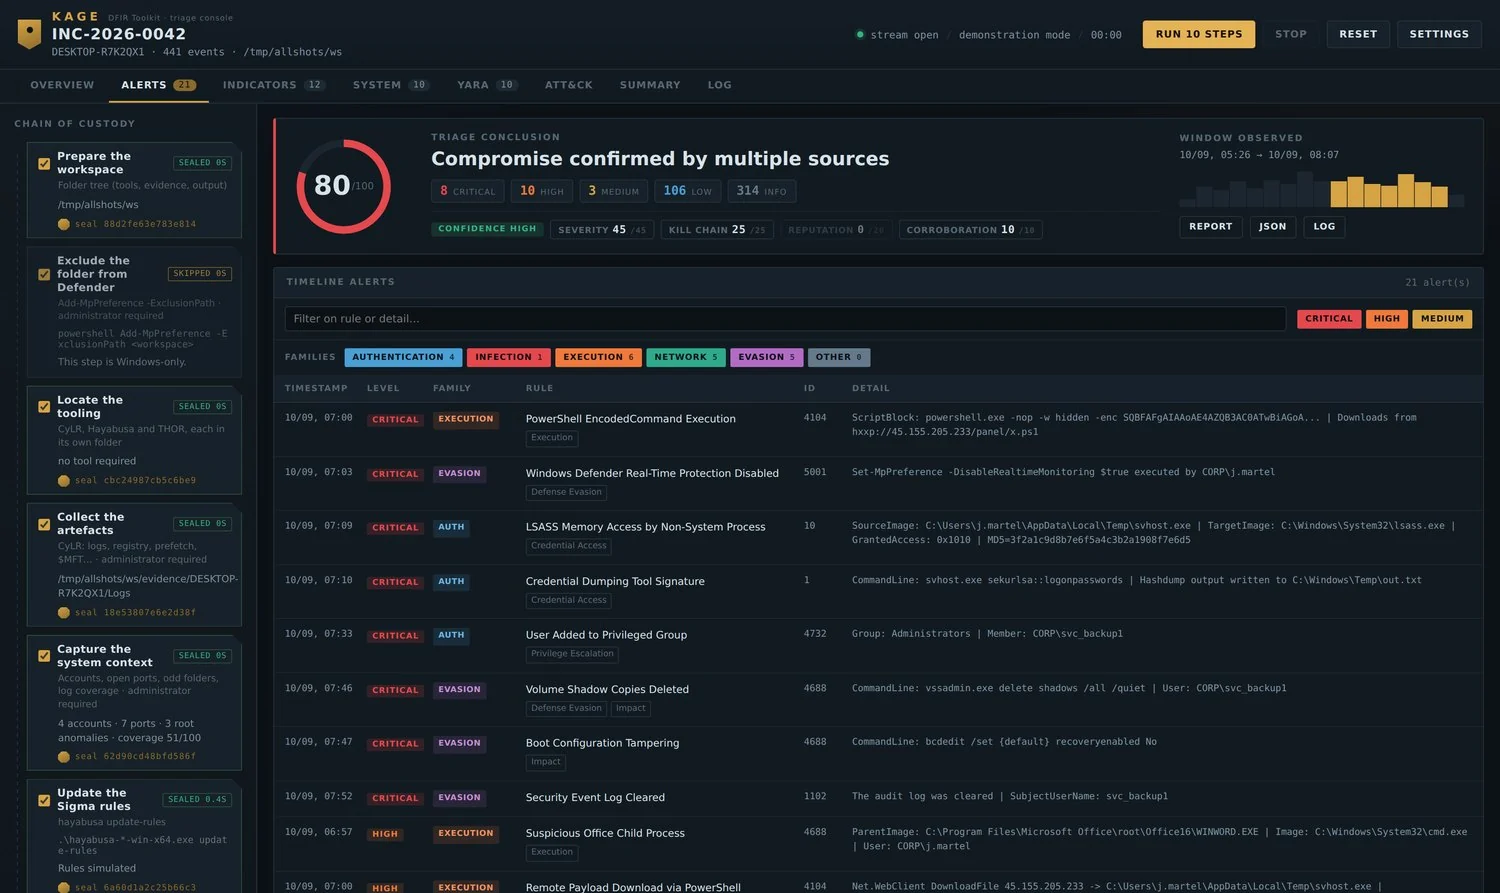 karim852/kage-dfir-toolkit
Windows host DFIR triage console that chains artefact collection, Sigma-correlated timelines, YARA scans, socket and account inspection, indicator…
 v-pun215/tourmaline
Reverse engineering notes, deobfuscated source, IOCs, and YARA rules for the Tourmaline ClickFix Python RAT, covering its DNS tunnel and blockchain…
 jithinkrishnanrs/gitlab-cve-2026-85706-ioc
CVE-2026-85706 — GitLab Path Traversal IOC Scanner & Detection Toolkit. Detect and hunt for exploitation of the critical unauthenticated GitLab CE/EE…
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 jithinkrishnanrs/stylesmuggler-ioc-toolkit
StyleSmuggler (CVE-2026-75650) IOC toolkit for Magento Open Source and Adobe Commerce. Detect compromised stores, Rust implants, PHP web shells,…
 log2timeline/plaso
Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
 facebook/threatexchange
Trust & Safety tools for working together to fight digital harms.
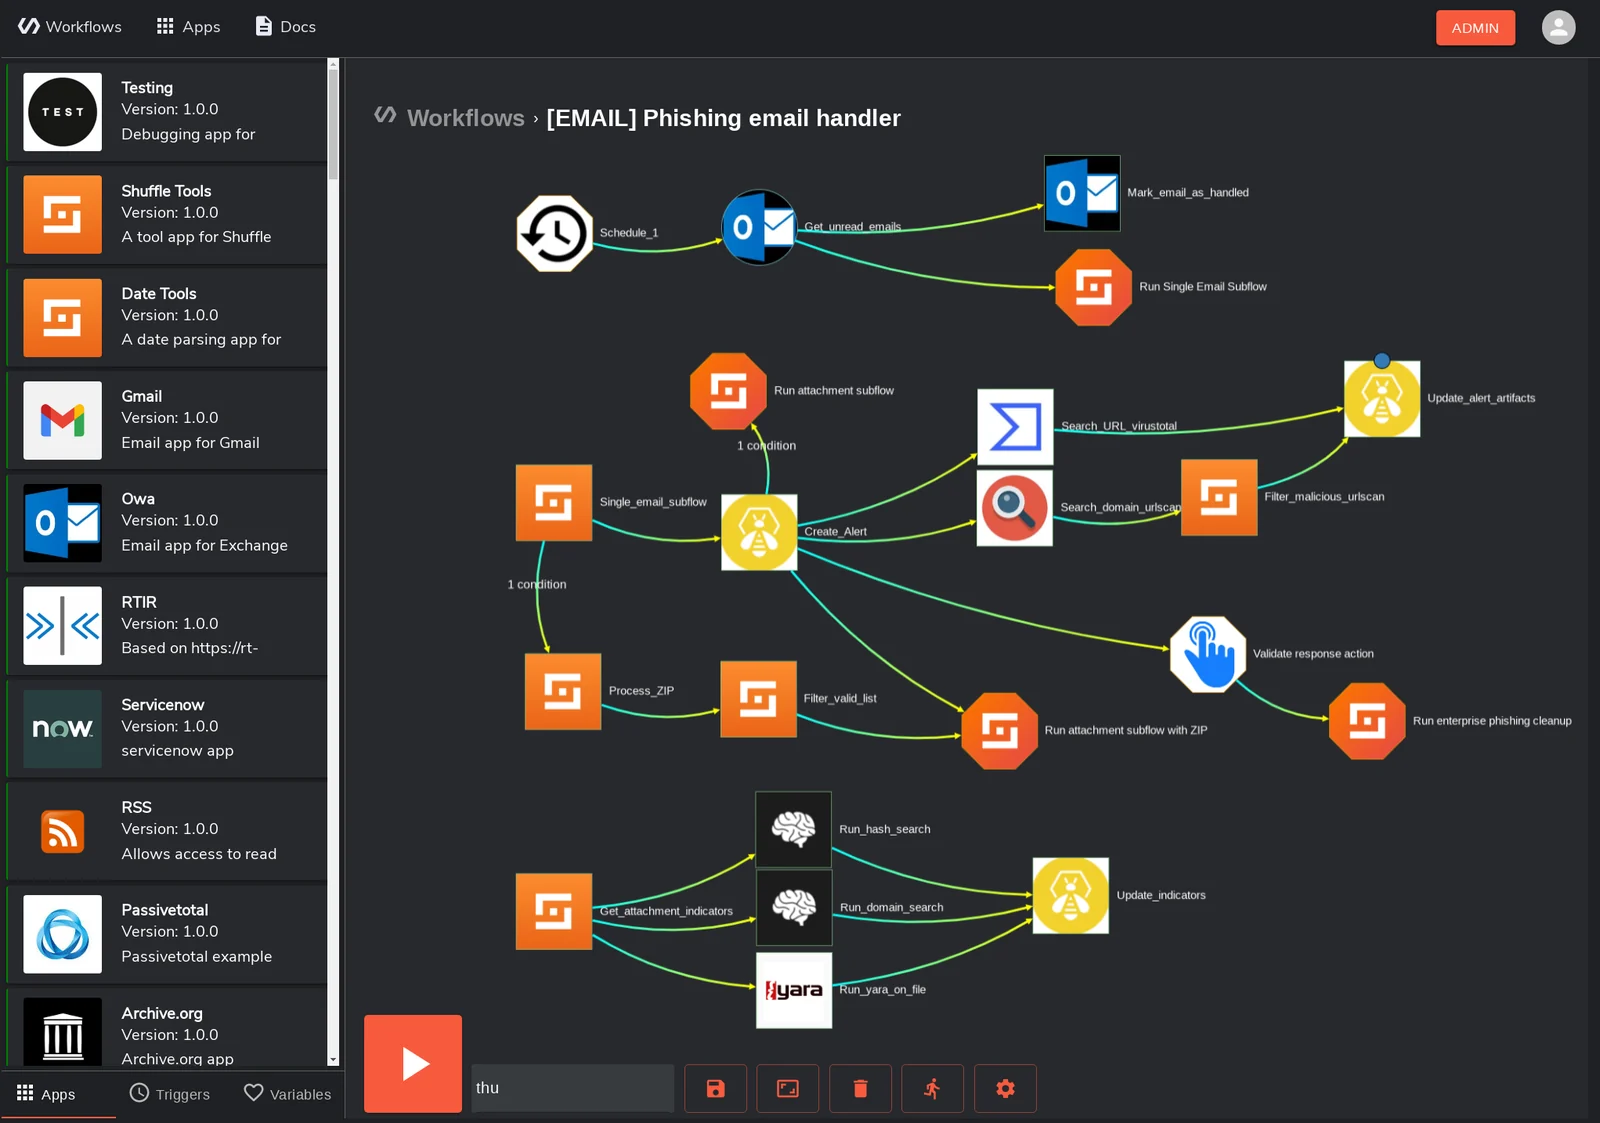 shuffle/shuffle
Open-source security orchestration, automation, and response (SOAR) platform with a visual workflow editor, prebuilt security app integrations, and…
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 soldier0x0/briefr
Open Vulnerability Intelligence platform, aggregated intel in one dashboard, with correlation and IOC lookups, completely self hosted. All resources…
 emcghee/payloadautomation
Automates Cobalt Strike payload development, testing, and deployment via a Python-to-Sleep bridge; includes artifact inspection, IoC tracking, and…