

OsintCase
 emrekybs/osintcase
An OSINT investigation case mapping tool for organizing entities, relationships, evidence, and intelligence.
curated-resourcesdata-recoverydigital-forensics+6
3
emrekybs/osintcaseAn OSINT investigation case mapping tool for organizing entities, relationships, evidence, and intelligence.
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 forrest-orr/moneta
Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs
 mthcht/awesome-lists
Curated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.
 vulncheck-oss/cli
VulnCheck's official command line tool
 adamwhitehat/judge-jury-and-executable
A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…

 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 abhinavbom/threat-intelligence-hunter
TIH is an intelligence tool that helps you in searching for IOCs across multiple openly available security feeds and some well known APIs. The idea…
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
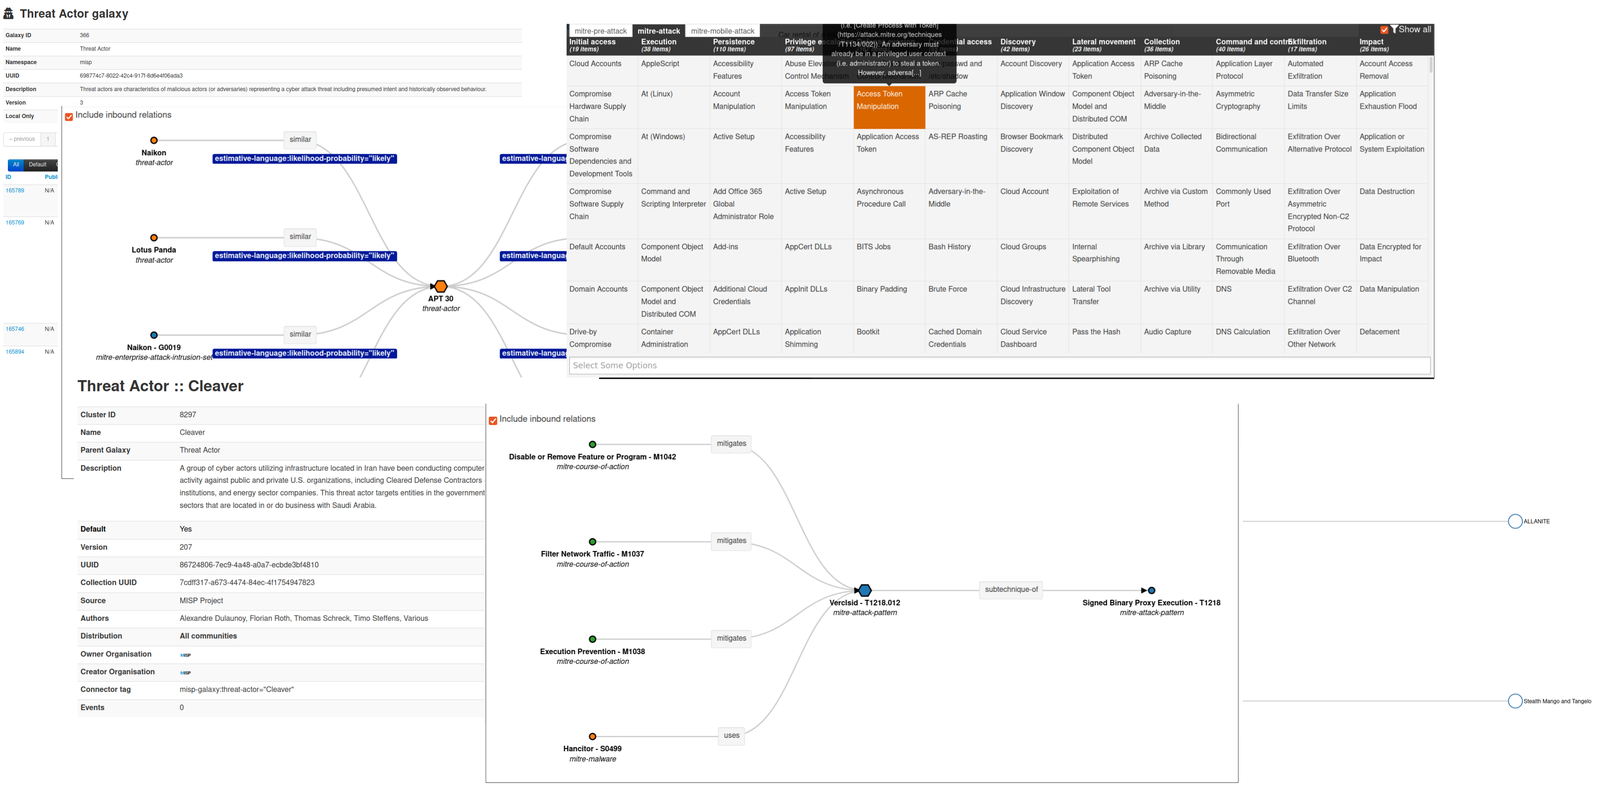 misp/misp-galaxy
Clusters and elements to attach to MISP events or attributes (like threat actors)

 byinarie/zirconium
Tool to search for IOCs related to HAFNIUM: CVE-2021-26855 CVE-2021-26857 CVE-2021-26858 CVE-2021-27065
 archanchoudhury/msdt_cve-2022-30190
This Repository Talks about the Follina MSDT from Defender Perspective
 cyberdudebivash/cyberdudebivash-cisco-asyncos-cve-2025-20393-scanner
This tool helps identify exposure to CVE-2025-20393 by checking for open TCP/6025 ports, responsive Spam Quarantine interfaces, and known…
 alexandreborges/malwoverview
Malwoverview is a first response tool for threat hunting across VirusTotal, Hybrid Analysis, URLHaus, Polyswarm, Malshare, Alien Vault, Malpedia,…
 misp/misp-taxonomies
Taxonomies used in MISP taxonomy system and can be used by other information sharing tool.