

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
77 results
maltrail preview

maltrail

GitHubstamparm/maltrail

Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…

anomaly-detectionanti-botdefensive-tools+11
8.6k
12h 1m ago
c2detect preview

c2detect

GitHubcognis-digital/c2detect

C2 server fingerprinter — Cobalt Strike, Sliver, Mythic, Havoc, Brute Ratel
command-and-controldefensive-toolsfingerprint-spoofing+8
421 month ago
citrix-netscaler-triage preview

citrix-netscaler-triage

GitHubfox-it/citrix-netscaler-triage

Forensic triage toolkit for Citrix NetScaler devices, featuring a Dissect-based IOC scanner for webshells, timestomping, and suspicious binaries,…

digital-forensicsincident-responseioc-management+3
751 month ago
LOLRMM preview

LOLRMM

GitHubmagicsword-io/lolrmm

Curated catalog of Remote Monitoring and Management tools abused by threat actors, with YAML profiles, Sigma detection rules, and API access for…
curated-resourcesdefensive-toolseducation+6
4114 days ago
kev-data preview

kev-data

GitHubcisagov/kev-data

Mirrors CISA's Known Exploited Vulnerabilities (KEV) catalog as CSV and JSON with a JSON schema, enabling programmatic access and commit-history…

curated-resourcesdefensive-toolsinformation-gathering+5
1362 days ago
Incident-Response-Powershell preview

Incident-Response-Powershell

GitHubbert-janp/incident-response-powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

digital-forensicsdisk-forensicsforensics+6
8075 months ago
Open-Source-Threat-Intel-Feeds preview

Open-Source-Threat-Intel-Feeds

GitHubbert-janp/open-source-threat-intel-feeds

This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…

intrusion-detectionioc-managementnetwork-security+3
97010h 56m ago
capa preview

capa

GitHubmandiant/capa

Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
ai-assisted-reversingbinary-analysiscode-analysis+10
6.1k3 days ago
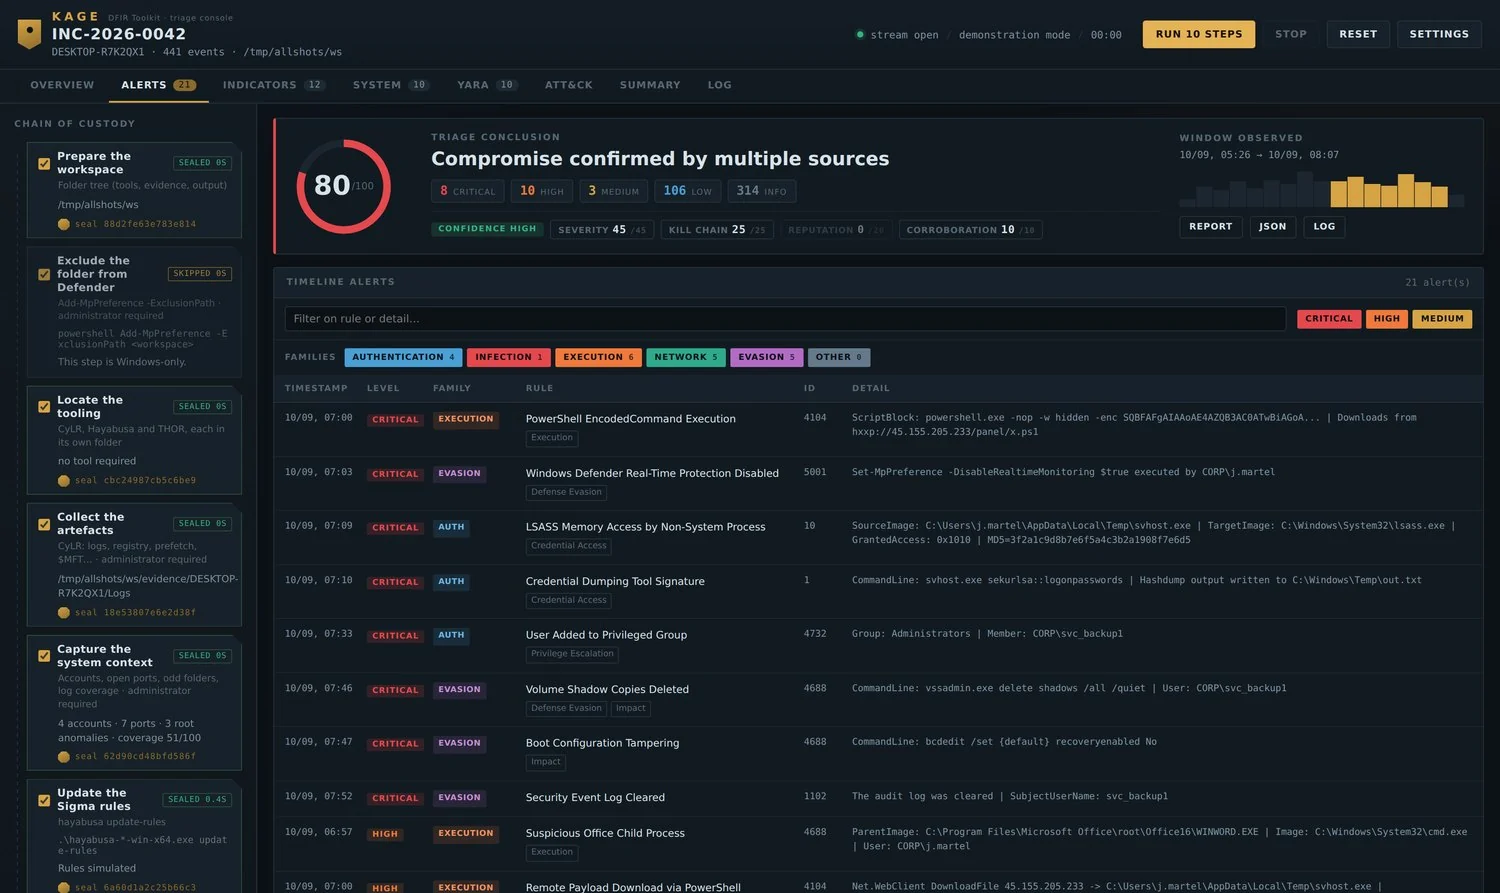
Kage-DFIR-toolkit preview

Kage-DFIR-toolkit

GitHubkarim852/kage-dfir-toolkit

Windows host DFIR triage console that chains artefact collection, Sigma-correlated timelines, YARA scans, socket and account inspection, indicator…

defensive-toolsdigital-forensicsforensics+8
4323 days ago
IntelOwl preview

IntelOwl

GitHubintelowlproject/intelowl

Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…

curated-resourcesdigital-forensicsdynamic-analysis-sandboxing+14
4.7k2 months ago
connectors preview

connectors

GitHubopencti-platform/connectors

Collection of OpenCTI connectors that ingest and synchronize threat intelligence, IOCs, and CTI data from external sources like MISP and MITRE ATT&CK…
defensive-toolsincident-responseinformation-gathering+5
5912 days ago
HAFNIUM-IOC preview
Archived

HAFNIUM-IOC

GitHubsoteria-security/hafnium-ioc

A PowerShell script to identify indicators of exploitation of CVE-2021-26855, CVE-2021-26857, CVE-2021-26858, and CVE-2021-26865

digital-forensicsforensicsincident-response+3
225 years ago
opencve preview

opencve

GitHubopencve/opencve

Aggregate, filter, and track CVEs from multiple sources with team collaboration, custom dashboards, alerts, and AI-powered analysis for vulnerability…

incident-responseioc-managementthreat-intelligence+2
2.8k9 days ago
ndaal_public_SBOM_Auditor preview

ndaal_public_SBOM_Auditor

GitLabvpierre/ndaal_public_sbom_auditor

Offline single-binary web app that ingests CycloneDX, SPDX and syft SBOMs, runs an ensemble of CVE scanners, enriches findings with EPSS, CISA-KEV…

configuration-auditingdefensive-toolsdevsecops+7
7 days ago
data-breach preview

data-breach

GitHubinfostealers-stats/data-breach

A continuously updated resource that catalogs confirmed data breaches from across the globe. Each entry includes the breach name, usually aligned…

curated-resourcesdata-exfiltrationinformation-gathering+3
661 day ago
sigma preview

sigma

GitHubsigmahq/sigma

Main Sigma Rule Repository

anomaly-detectioncurated-resourcesdefensive-tools+9
10.9k12 days ago
IPED preview

IPED

GitHubsepinf-inc/iped

IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
data-recoverydigital-forensicsdisk-forensics+9
2.7k9 days ago
SigLens preview

SigLens

GitHubst0rn/siglens

Windows artifact analysis toolkit that maps AV detections to PE offsets, sections, RVA/VA and strings, with YARA, AMSI, capa and multi-engine…

binary-analysisdefensive-toolsdigital-forensics+7
444 days ago
Previous12345Next