
Archived
BearFTP
 kolya5544/bearftp
Honeypot FTP server written in .NET Core (C#) for both Linux and Windows.
defensive-toolsincident-responseinformation-gathering+4
14
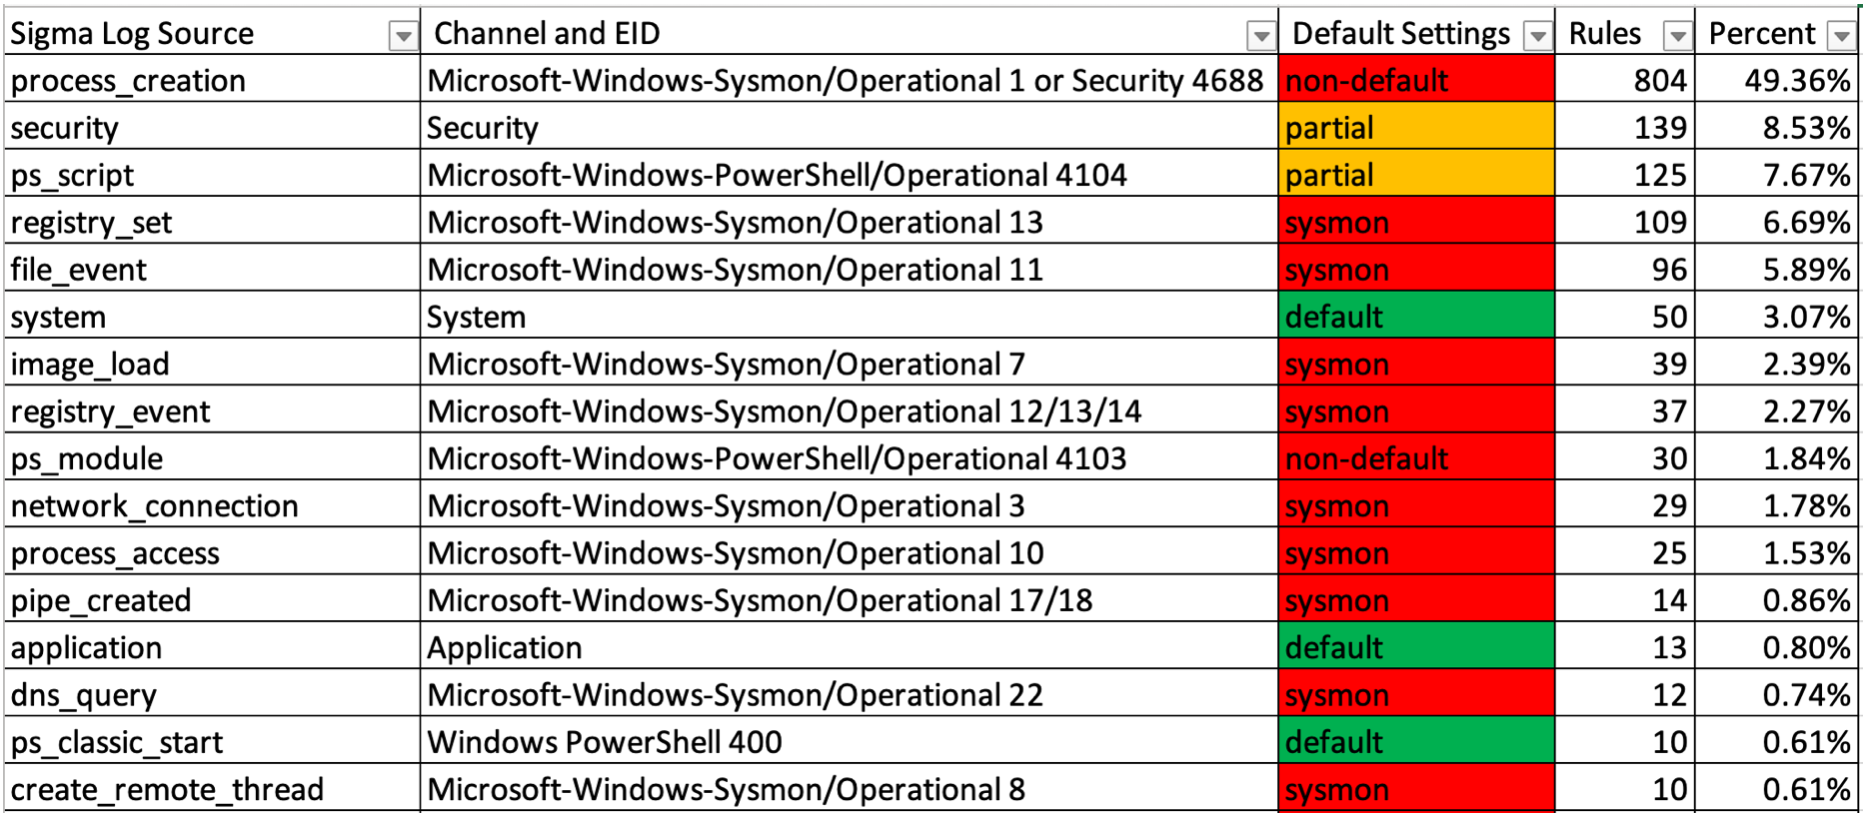 yamato-security/enablewindowslogsettings
Documentation and scripts to properly enable Windows event logs.
 alloysecuregroup/phantomfs
Windows honeypot using ProjFS to project decoy files that trigger Event Log and desktop alerts when accessed, with SMB remote session logging for…
 withsecurelabs/doublepulsar-detection-script
A python2 script for sweeping a network to find windows systems compromised with the DOUBLEPULSAR implant.
 sans-blue-team/deepbluecli
PowerShell-based threat hunting tool that analyzes Windows Event Logs to detect malicious activity including credential attacks, obfuscated commands,…
 bruneaug/dshield-siem
DShield Sensor Log Collection with ELK
 digitalruby/ipban
Automated IP ban service that detects failed login attempts from event logs and files, blocking attackers on Windows and Linux via firewall…
 withsecurelabs/lazarus-sigma-rules
Sigma rules for detecting Lazarus Group TTPs, covering malicious document execution, PowerShell abuse, scheduled tasks, and credential access,…
 theflink/hunt-weird-syscalls
ETW based POC to identify direct and indirect syscalls
 mthcht/purpleteam
Purpleteam scripts simulation & Detection - trigger events for SOC detections
 corelight/pingback
A Zeek package to detect the Pingback malware ICMP tunnel command and control (C2) network traffic.
 sigmahq/sigma-cli
The Sigma command line interface based on pySigma
 sigmahq/pysigma-backend-opensearch
pySigma OpenSearch backend
 blackhillsinfosec/eventlogging
Automation scripts to deploy Windows Event Forwarding, Sysmon, and custom audit policies in an Active Directory environment.
 corelight/cve-2022-30216
Zeek package detecting CVE-2022-30216 NTLM relay attacks against Windows Server. Raises notices for exploit attempts and successful exploitation via…
 mckinnonit/zabbix-template-cve-2020-1472
Zabbix Template to monitor for Windows Event Viewer event's related to Netlogon Elevation of Privilege Vulnerability - CVE-2020-1472. Monitors event…
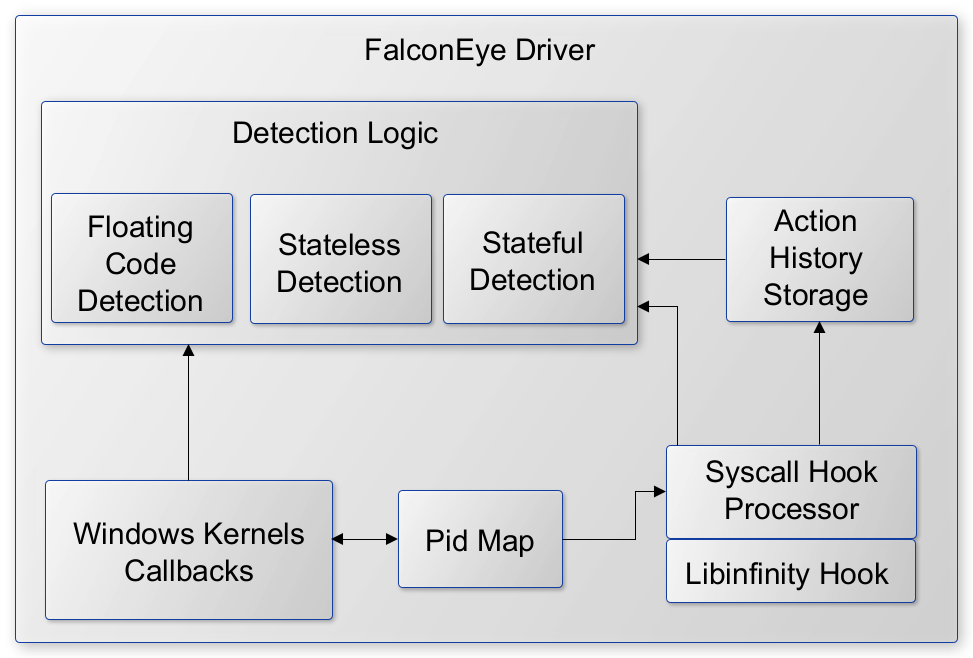 rajiv2790/falconeye
Kernel-mode Windows driver for real-time detection of process injection techniques, including shellcode, DLL, and reflective injection, with syscall…
 corelight/sigred
Zeek package for detecting CVE-2020-1350 (SIGRed) Windows DNS server exploit attempts via large DNS SIG/KEY response analysis with configurable…