

libpcap
 the-tcpdump-group/libpcap
System-independent library for user-level packet capture and filtering. Provides a portable framework for low-level network monitoring, security…
dns-analysisinformation-gatheringintrusion-detection+3
3.2k
the-tcpdump-group/libpcapSystem-independent library for user-level packet capture and filtering. Provides a portable framework for low-level network monitoring, security…
 stamparm/tsusen
Network traffic sensor
 stratosphereips/aip
Generates efficient IPv4 blocklists from Zeek network flows using multiple prioritization models (new, consistent, random forest) to identify…
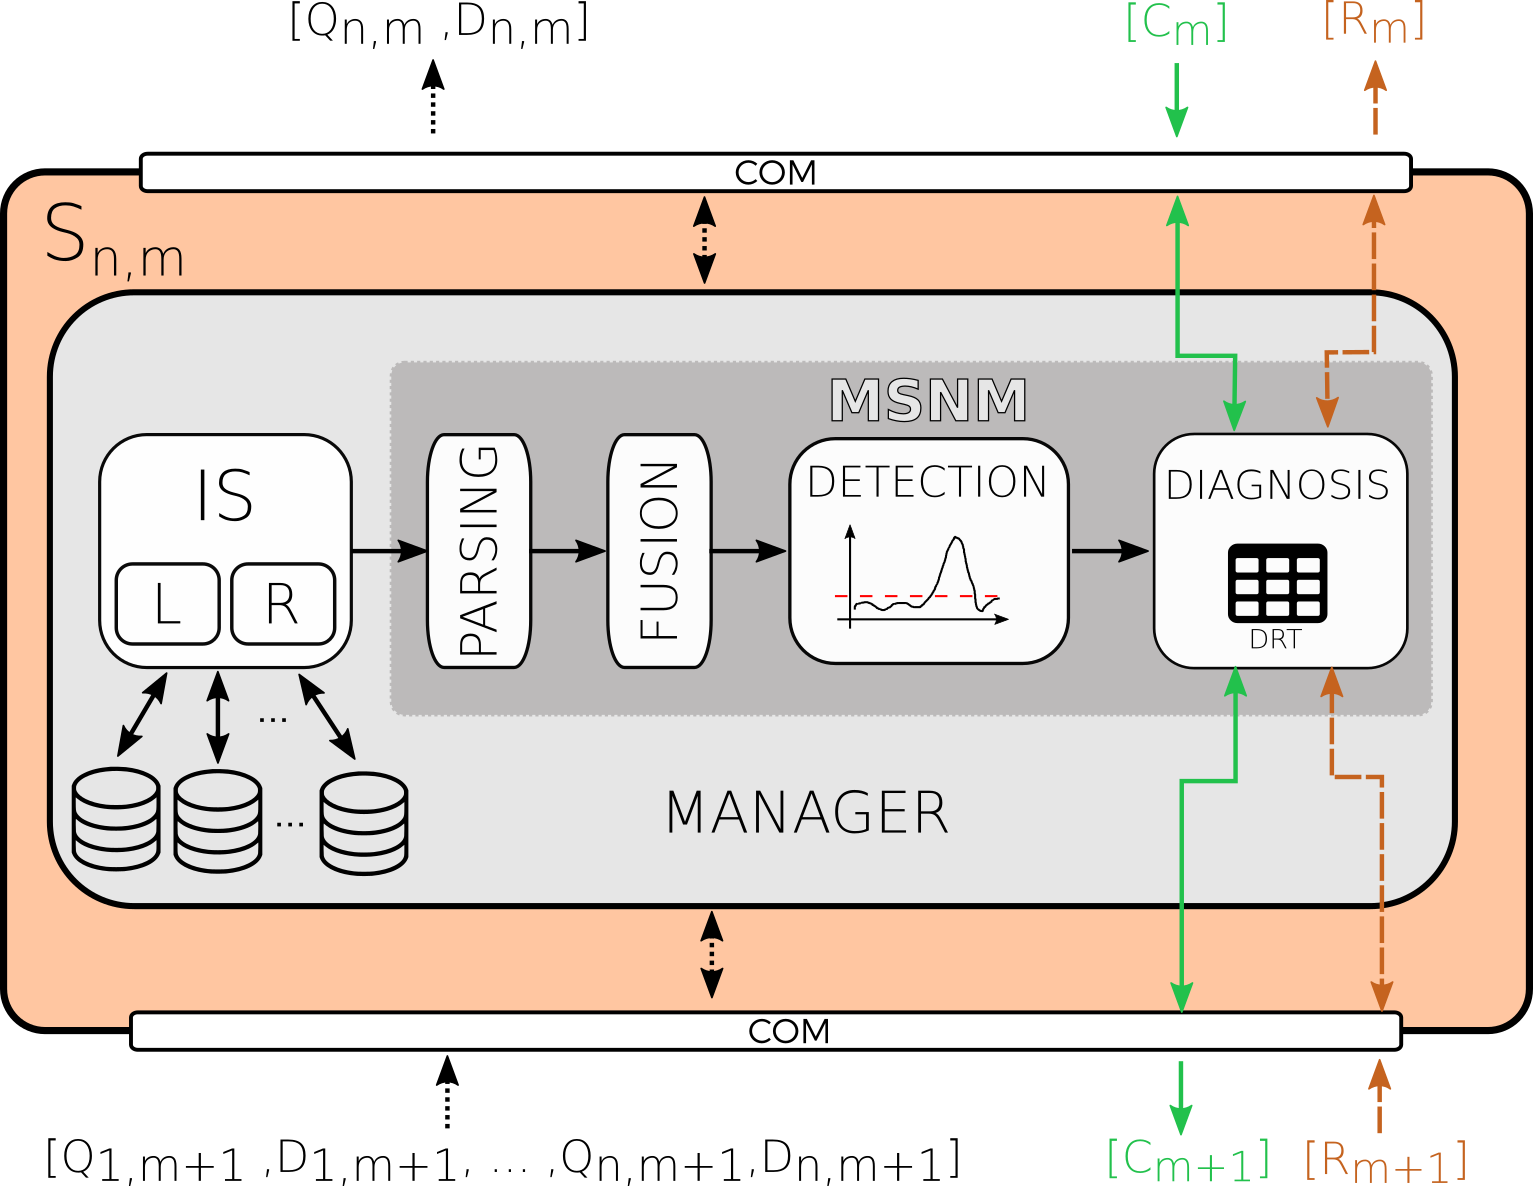 nesg-ugr/msnm-sensor
Multivariate statistical network monitoring sensor that detects anomalies using PCA-based techniques, aggregating lightweight statistics from…
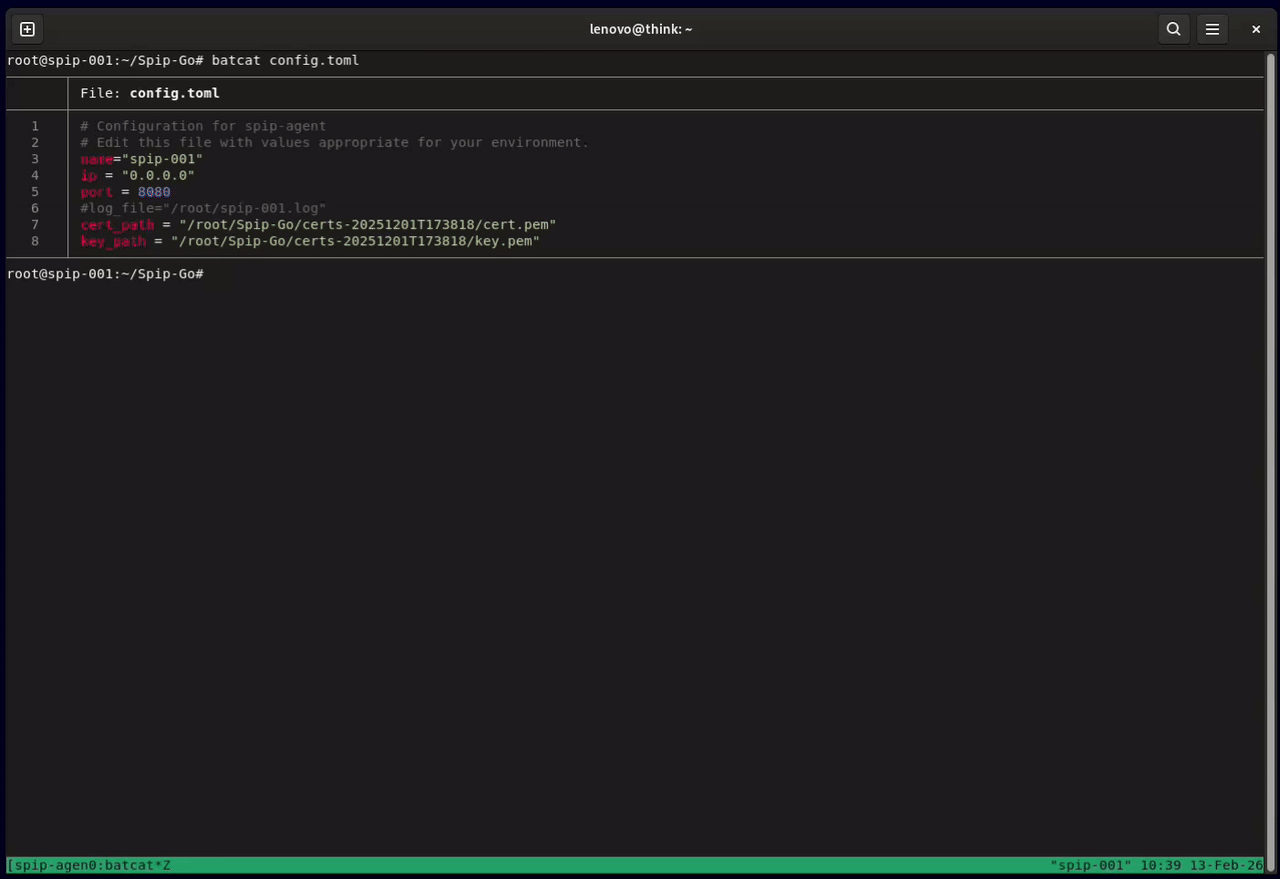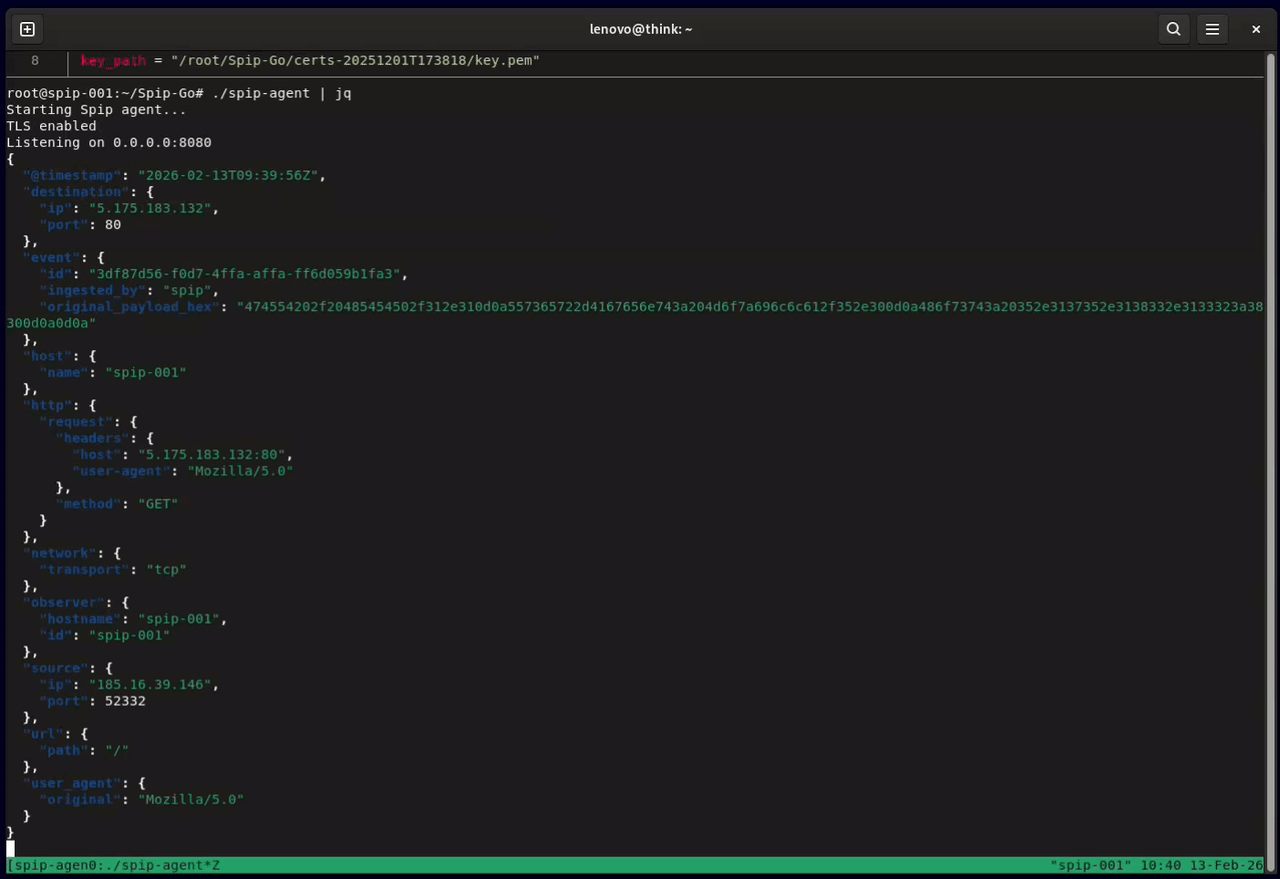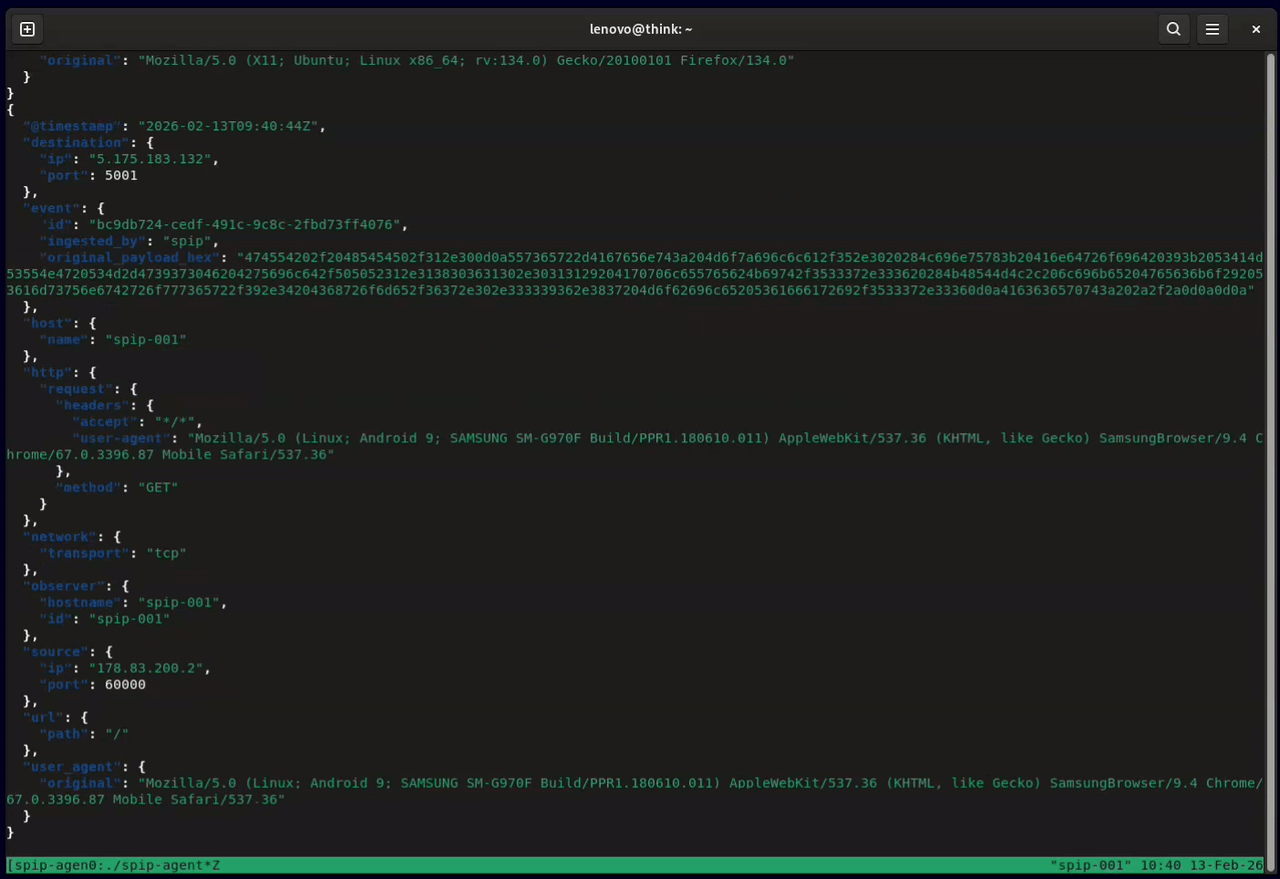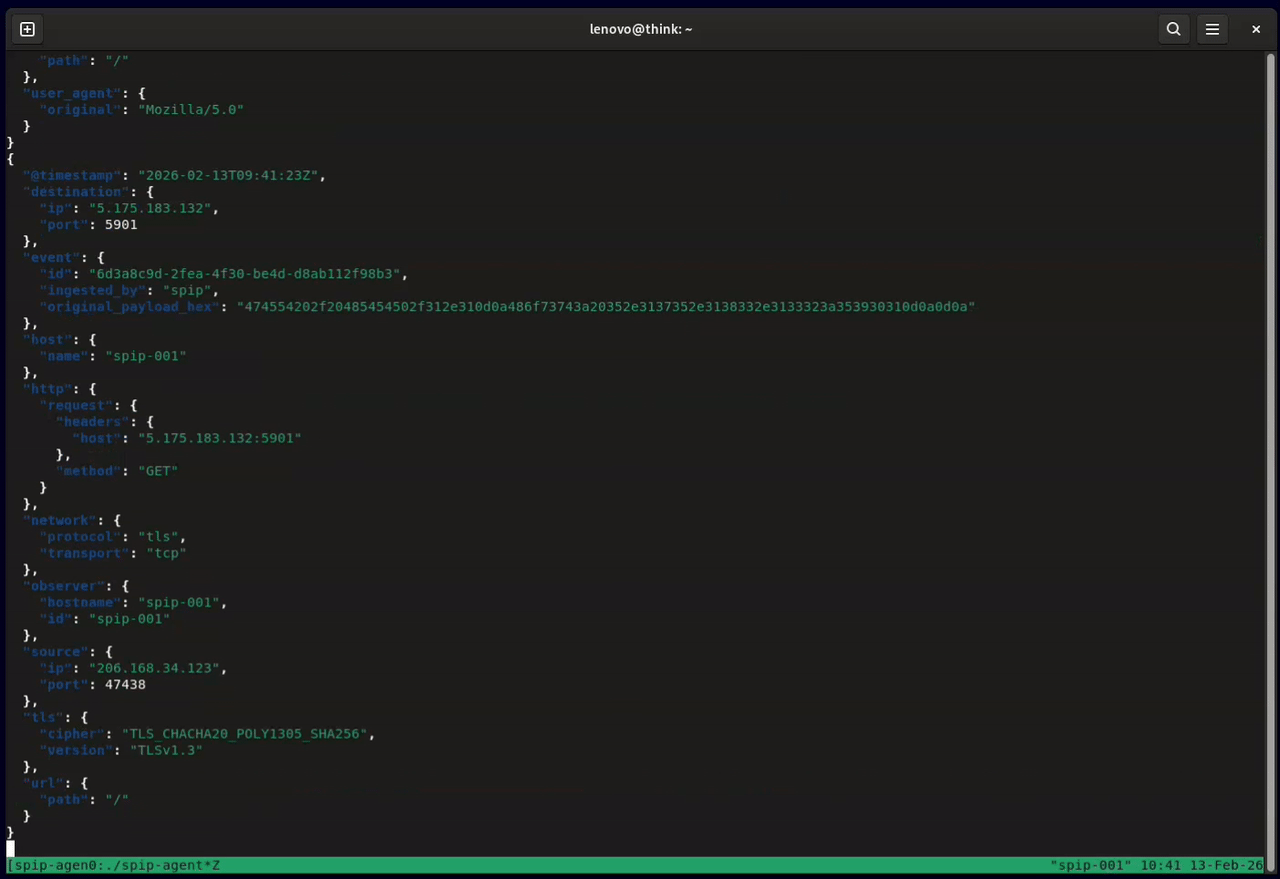 honeylabshq/spip-go
Spip network sensor written in Go
 d0n601/wp-mhn
Integrates your Modern Honeypot Network Server and Wordpress Blog via MHN's REST API and WP's shortcodes
 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
 mushorg/buttinsky
Botnet monitoring is a crucial part in threat analysis and often neglected due to the lack of proper open source tools. Our tool will provide an open…
 rushyo/vindicatetool
LLMNR/NBNS/mDNS Spoofing Detection Toolkit
 logisek/baconsampler
Sniffs outbound traffic for suspicious, beacon-like callbacks, because if it keeps coming back on schedule, it's probably not breakfast.
 microlaser/dns_watchdog_windows2
PowerShell script that monitors Windows DNS traffic via pktmon to detect poisoning, spoofing, rogue resolver responses, and gateway MAC changes,…
 kismetwireless/kismet
Github mirror of official Kismet repository
 dshield-isc/dshield
Installs and configures a DShield honeypot sensor on Raspberry Pi or Ubuntu, running Cowrie SSH and HTTP honeypots and forwarding firewall logs to…
 certtools/intelmq
IntelMQ is a solution for IT security teams for collecting and processing security feeds using a message queuing protocol.
 jaksi/sshesame
An easy to set up and use SSH honeypot, a fake SSH server that lets anyone in and logs their activity
 pedramamini/threatingestor
Automated threat intelligence aggregation tool that extracts and normalizes indicators from multiple sources (OSINT feeds, malware reports) into a…
 gbrindisi/wordpot
A Wordpress Honeypot