How-To-Secure-A-Linux-Server

Step-by-step guide for hardening a Linux server, covering SSH security, firewalls, intrusion detection, auditing, and system configuration to reduce…

Step-by-step guide for hardening a Linux server, covering SSH security, firewalls, intrusion detection, auditing, and system configuration to reduce…

SQL powered operating system instrumentation, monitoring, and analytics.

Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…

Open-source IDS/IPS and WAF engine that analyzes logs and HTTP requests to detect and block malicious IPs, leveraging a crowdsourced community…

ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…

MISP (core software) - Open Source Threat Intelligence and Sharing Platform

Centralized log management platform for collecting, indexing, and analyzing streaming logs, with alerting and event correlation for security…

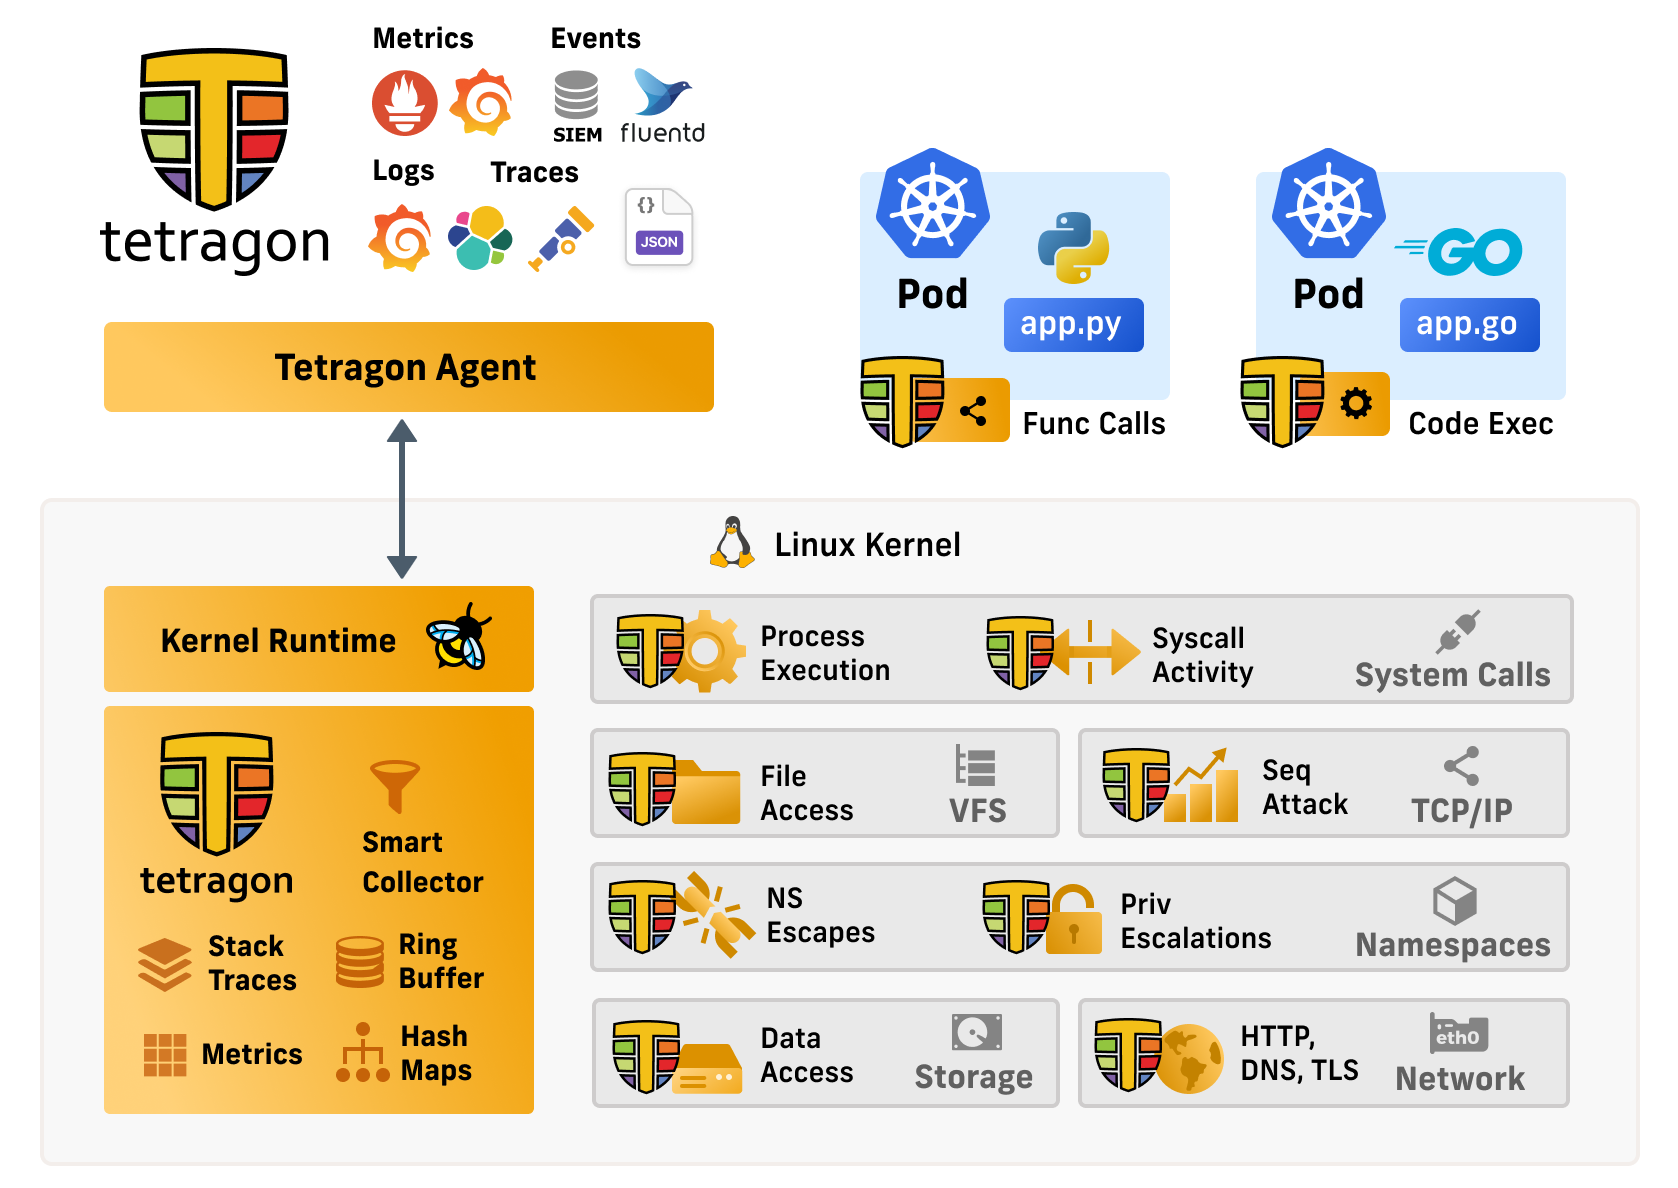
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…

Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…

Open-source network IDS/IPS/NSM engine for real-time traffic inspection, intrusion detection and prevention, protocol analysis, and rule-based threat…

Arkime is an open source, large scale, full packet capturing, indexing, and database system.

Web-based Traffic and Cybersecurity Network Traffic Monitoring

ZoneMinder is a free, open source Closed-circuit television software application developed for Linux which supports IP, USB and Analog cameras.

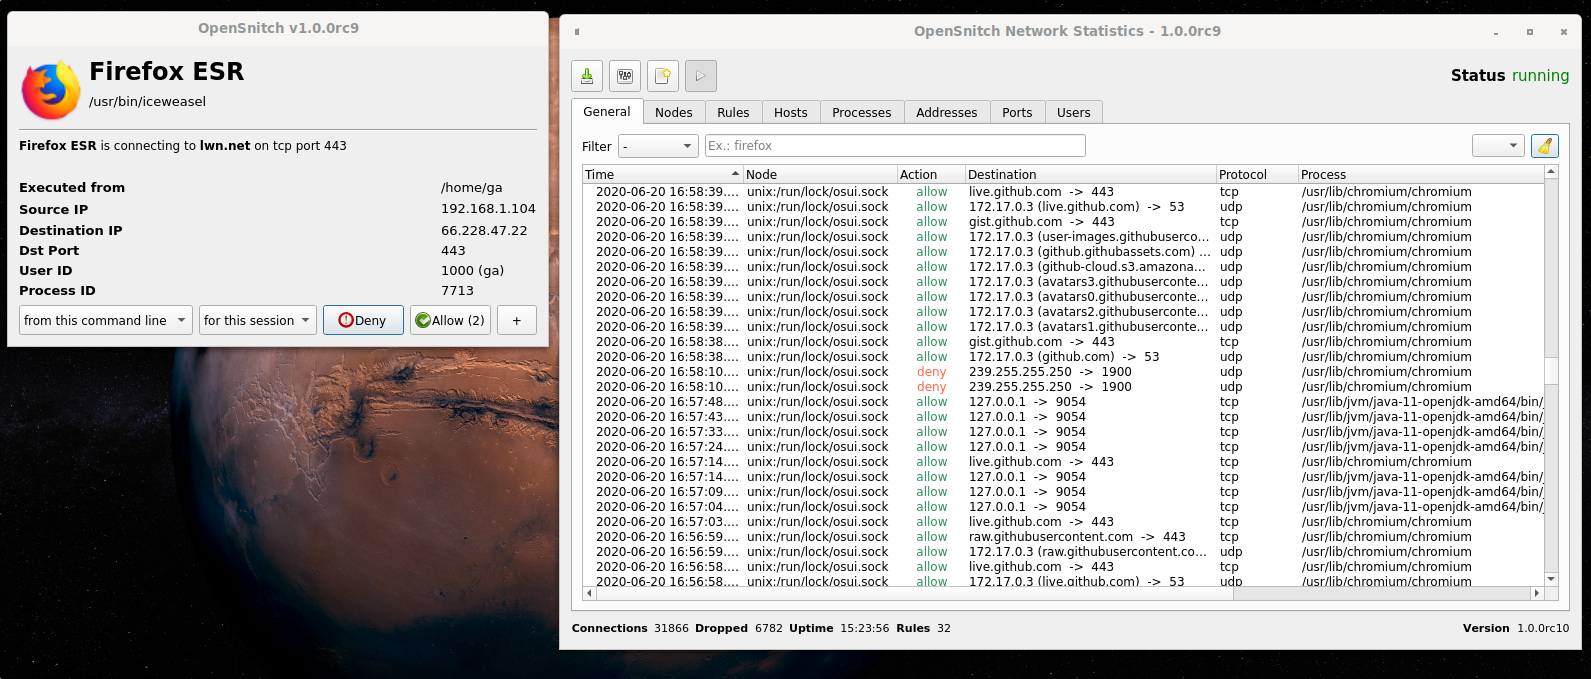
Interactive GNU/Linux application firewall that filters outbound connections, blocks ads and malware domains, manages system firewall rules via GUI,…

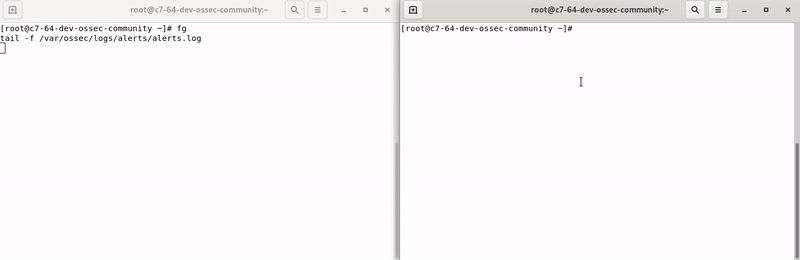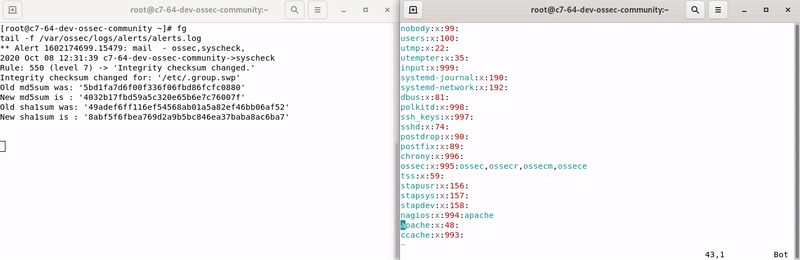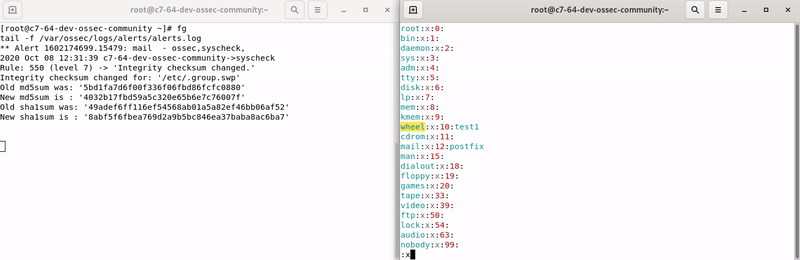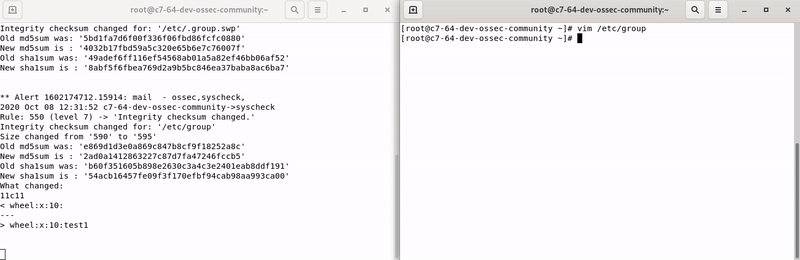
OSSEC is an Open Source Host-based Intrusion Detection System that performs log analysis, file integrity checking, policy monitoring, rootkit…

eBPF-based Security Observability and Runtime Enforcement

Centralized network visibility and continuous asset discovery. Monitor devices, detect change, and stay aware across distributed networks.

Automate the creation of a lab environment complete with security tooling and logging best practices