

cve-2021-1675-printnightmare
 initconf/cve-2021-1675-printnightmare
Zeek package to detect CVE-2021-1675 (PrintNightmare) by monitoring named pipes and RPC operations for spoolss exploitation attempts.
exploitationids-ips-evasionintrusion-detection+2
initconf/cve-2021-1675-printnightmareZeek package to detect CVE-2021-1675 (PrintNightmare) by monitoring named pipes and RPC operations for spoolss exploitation attempts.
 tranqtruong/detect-bluekeep
a simple tool to detect the exploitation of BlueKeep vulnerability (CVE-2019-0708)
 nicholasadamou/minipwner
A script to configure a TP-Link MR3040 running OpenWRT into a simple, yet powerful penetration-testing "dropbox".
 imthenachoman/how-to-secure-a-linux-server
Step-by-step guide for hardening a Linux server, covering SSH security, firewalls, intrusion detection, auditing, and system configuration to reduce…
 adarkst/honeypot_smart_infrastructure
This Repository Includes Kubernetes manifest files for configuration of Honeypot system and Falco IDS in K8s environment. There are also Demo…
 wazuh/wazuh
Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
 netalertx/netalertx
Centralized network visibility and continuous asset discovery. Monitor devices, detect change, and stay aware across distributed networks.
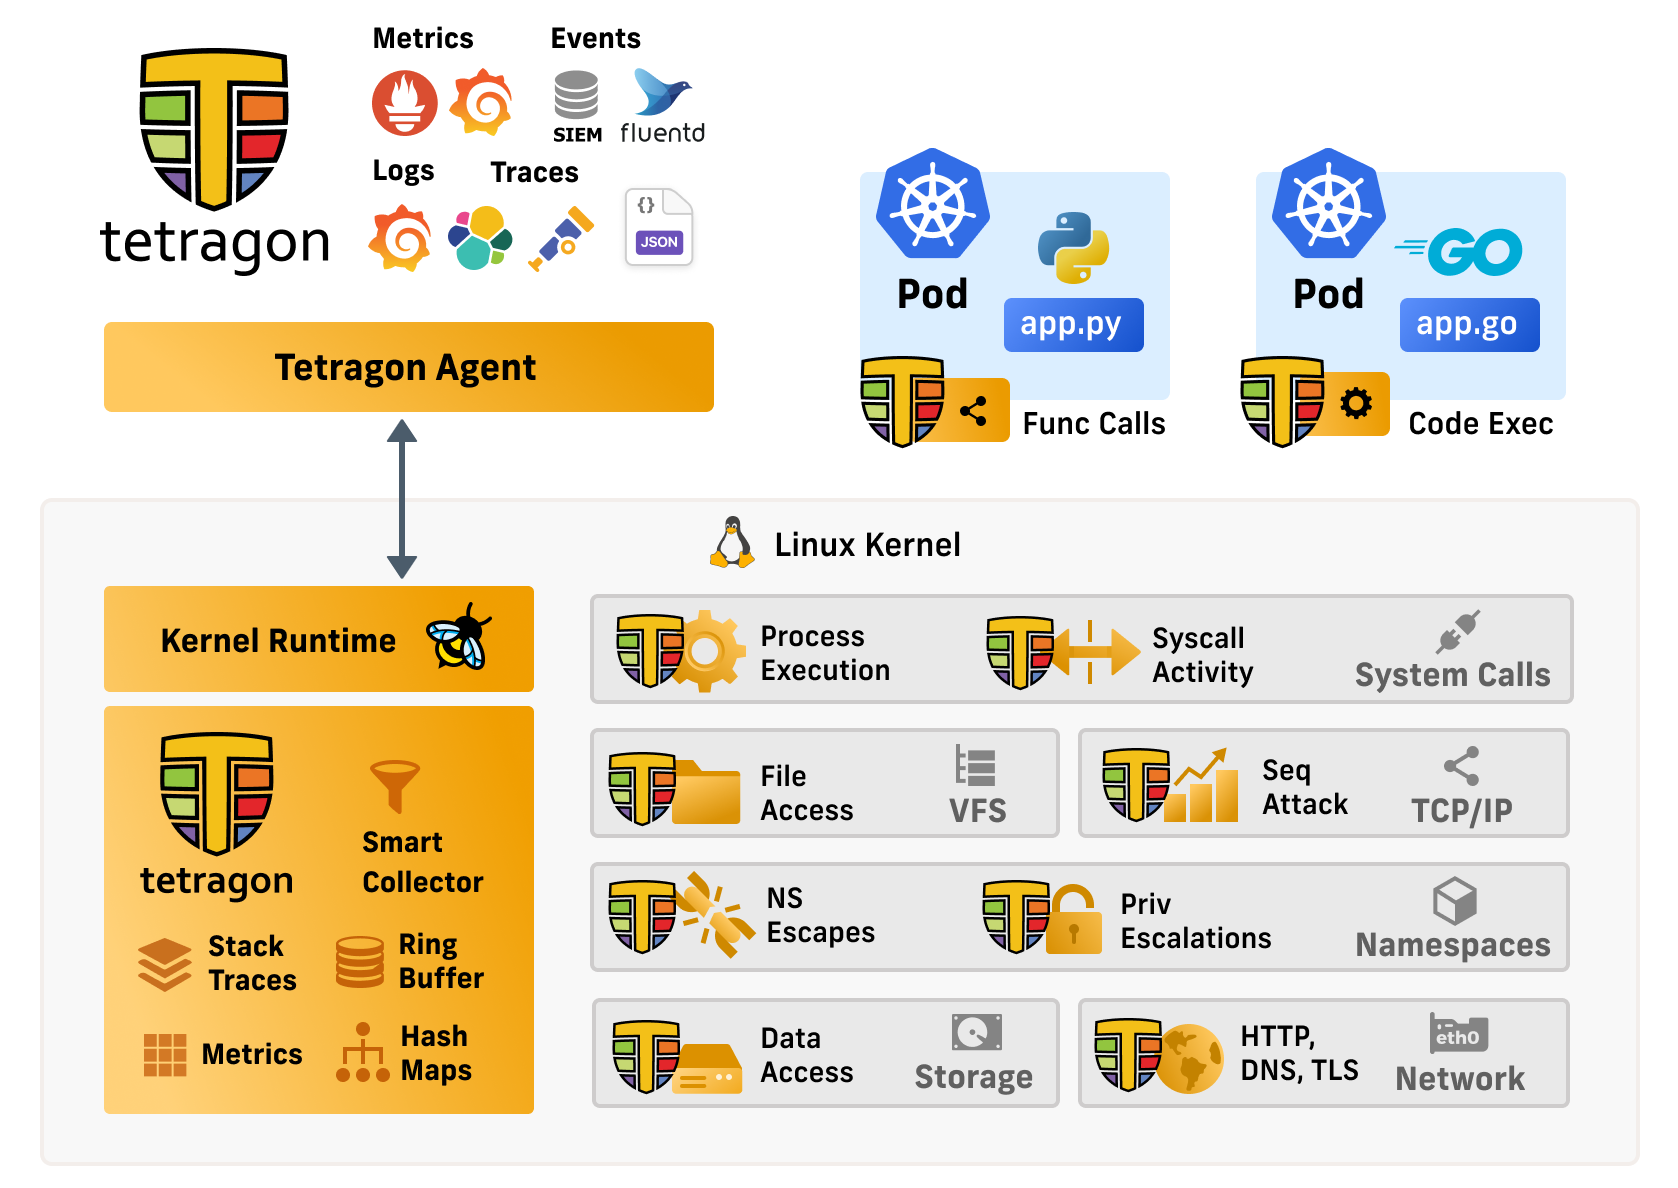 cilium/tetragon
eBPF-based Security Observability and Runtime Enforcement
 clong/detectionlab
Automate the creation of a lab environment complete with security tooling and logging best practices
 bytedance/elkeid
Elkeid is an open source solution that can meet the security requirements of various workloads such as hosts, containers and K8s, and serverless. It…
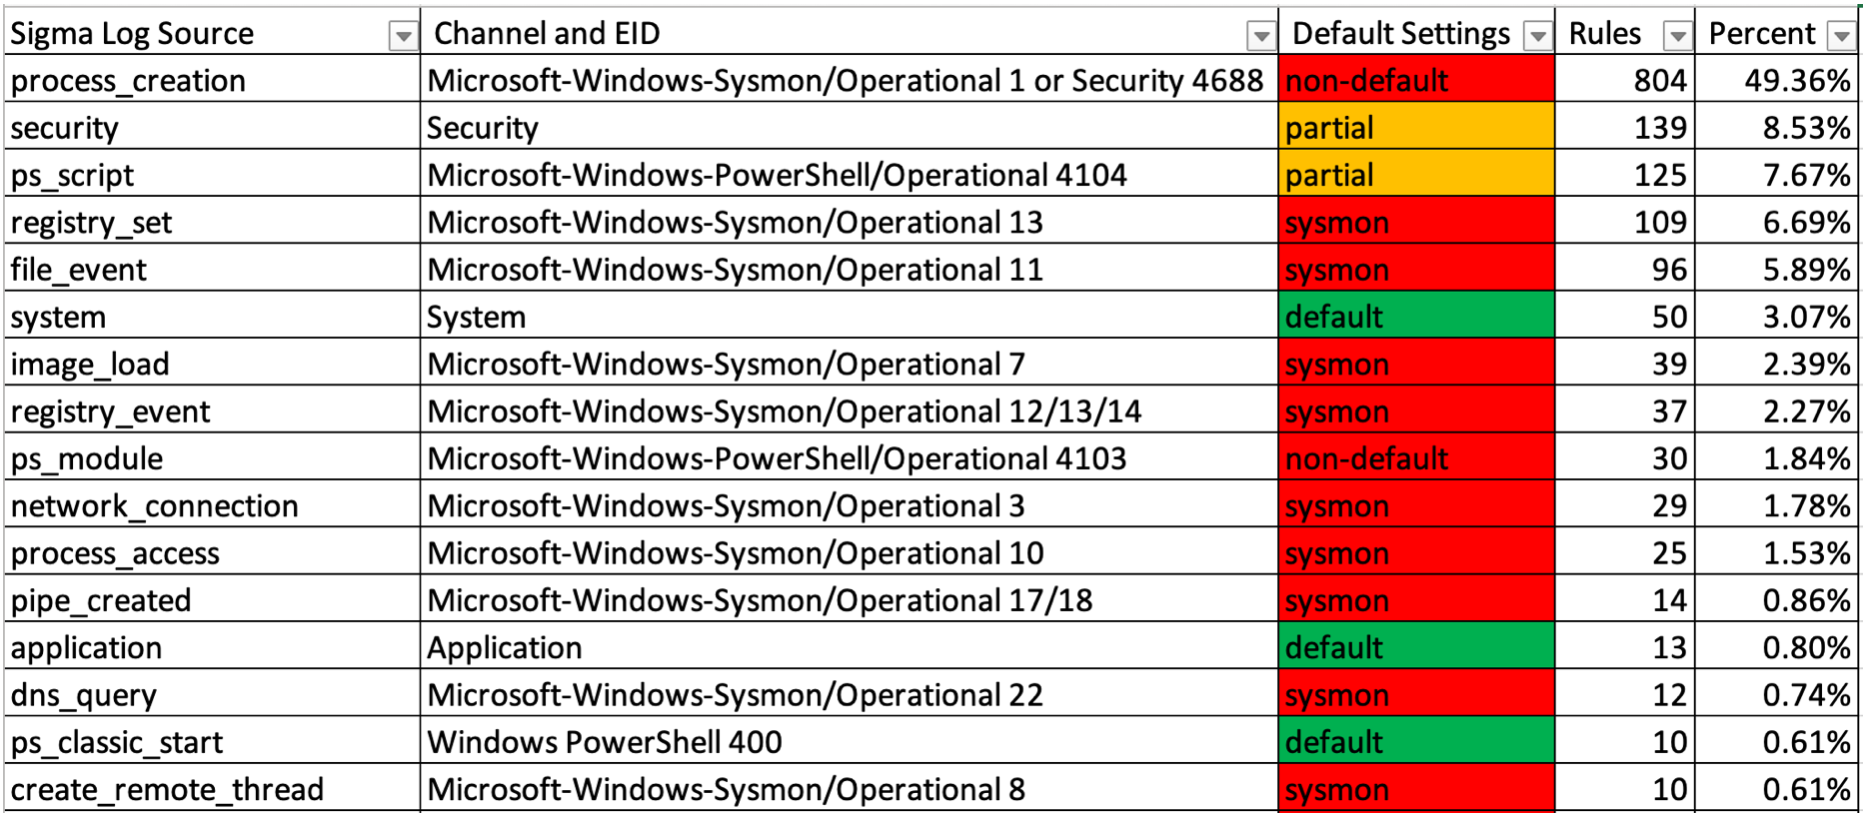 yamato-security/enablewindowslogsettings
Documentation and scripts to properly enable Windows event logs.
 duggytuxy/syswarden
Host-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…
 shirkdog/pulledpork
Pulled Pork for Snort and Suricata rule management (from Google code)
 op7ic/blueteam.lab
Blue Team detection lab created with Terraform and Ansible in Azure.
 fksvs/siper
XDP Based Lightweight and Fast Firewall
 osbornepro/btps-secpack
PowerShell-based security toolkit for small-to-medium enterprises, providing automated alerts, Active Directory hardening, Windows Event Forwarding,…
 safeagent-beihang/clawguard
Enterprise AI agent security toolkit providing pre-flight auditing, configuration hardening, runtime threat detection, and active defense against…