
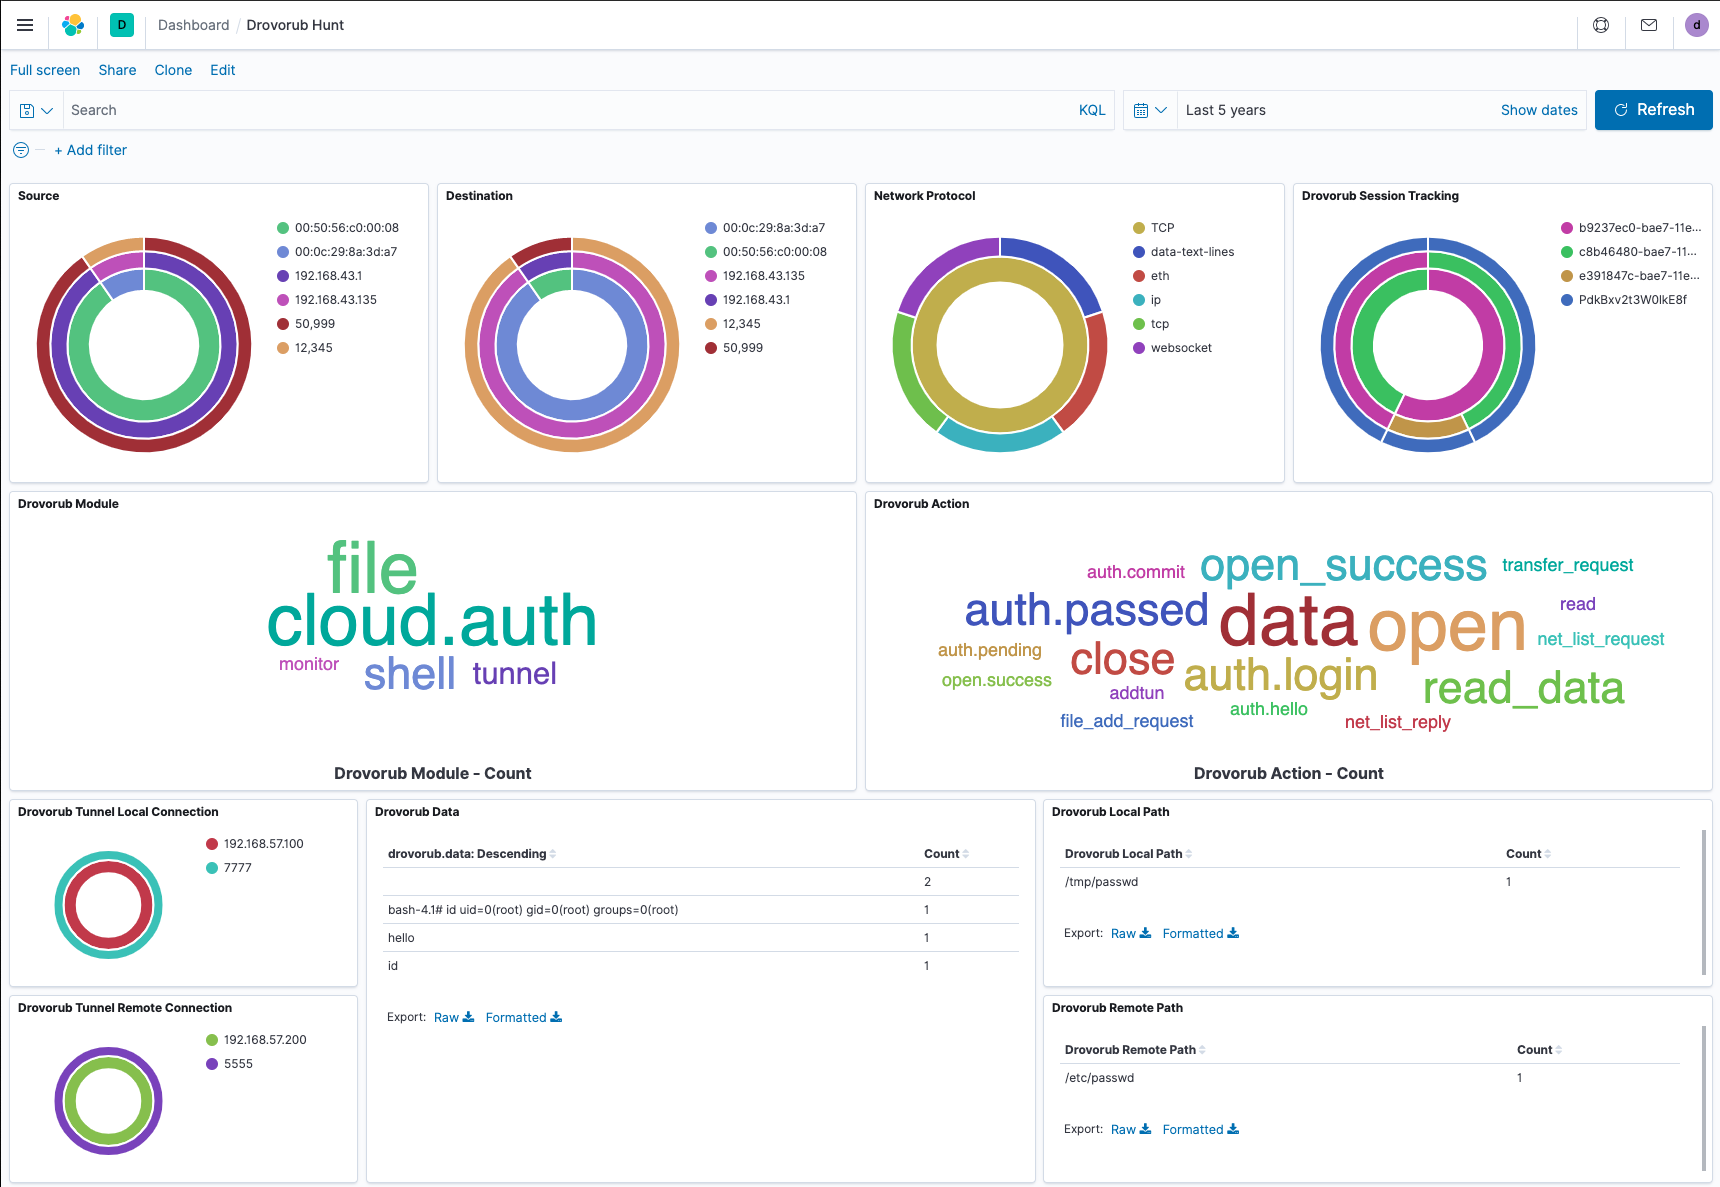
drovorub-hunt
 insane-forensics/drovorub-hunt
A tool to assist with network-based hunting for GRU's Drovorub malware c2
incident-responseintrusion-detectionmalware-analysis+3
25
insane-forensics/drovorub-huntA tool to assist with network-based hunting for GRU's Drovorub malware c2
 yojiwatanabe/networkalarm
A tool to monitor local network traffic for possible security vulnerabilities. Warns user against possible nmap scans, Nikto scans, credentials sent…
 0x0v1/audix
Audix is a PowerShell tool to quickly configure the Windows Event Audit Policies for security monitoring
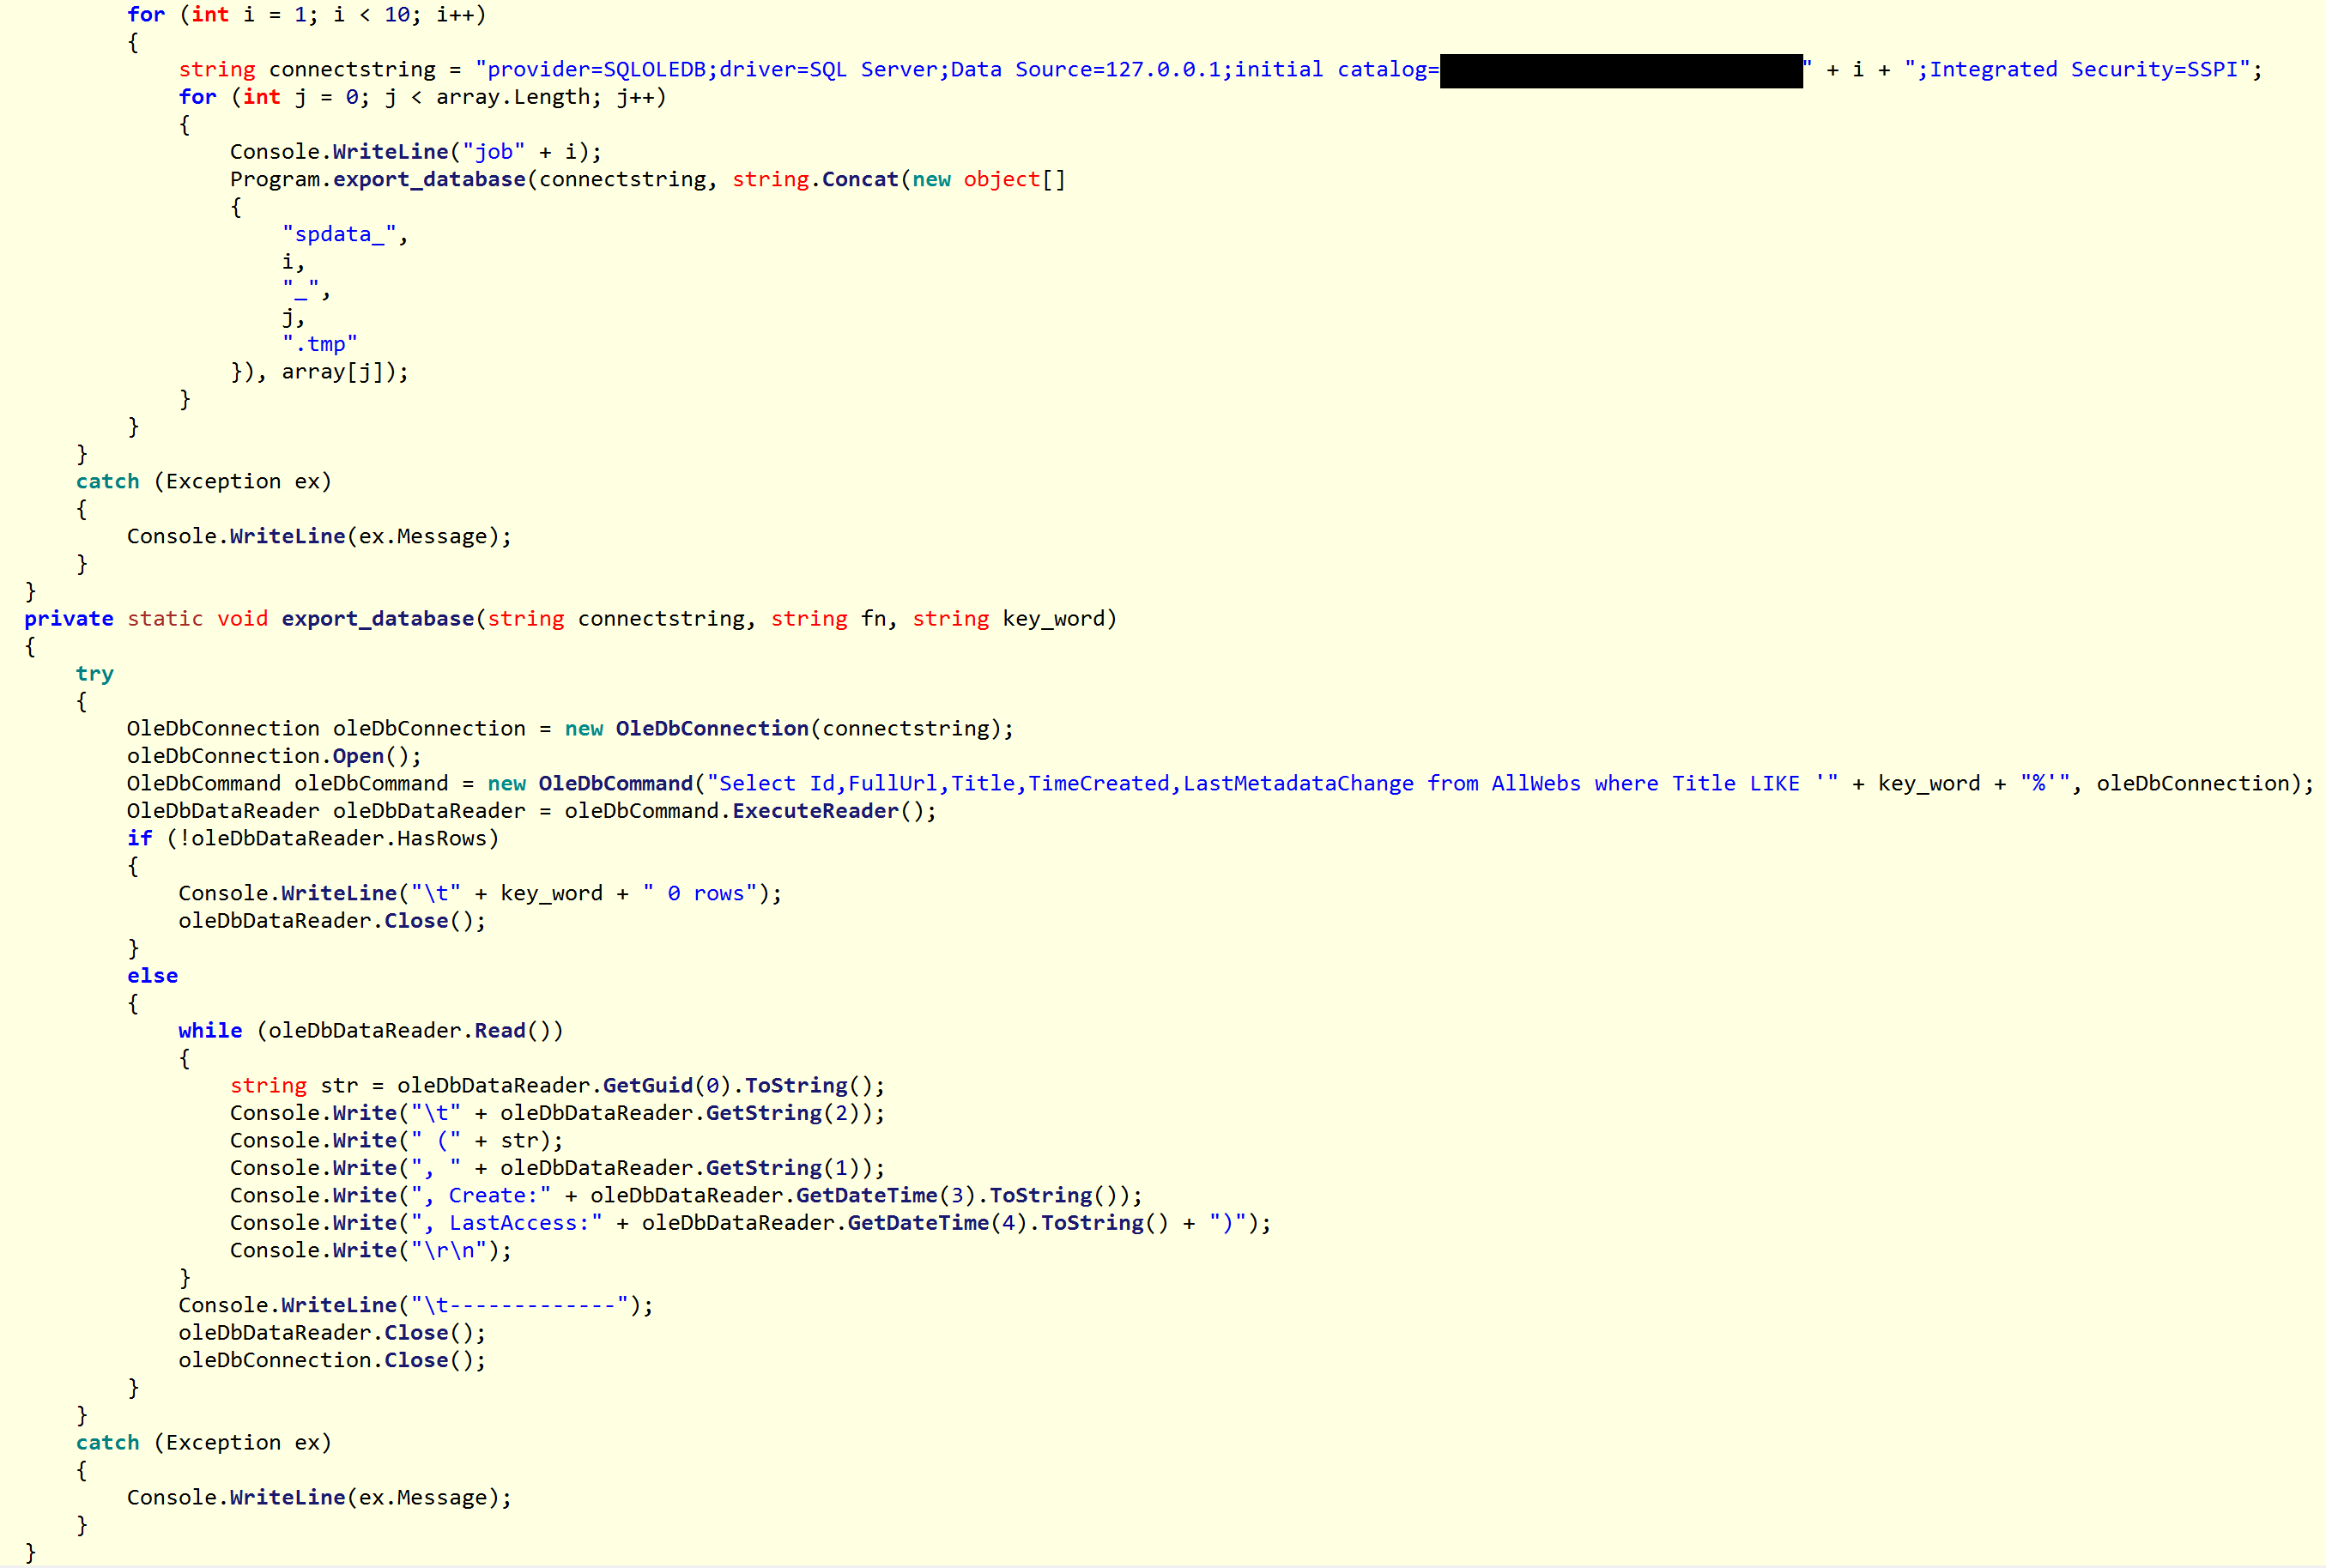 nccgroup/royal_apt
Royal APT - APT15 - Related Information from NCC Group Cyber Defense Operations Research
 ait-aecid/logdata-anomaly-miner
This tool parses log data and allows to define analysis pipelines for anomaly detection. It was designed to run the analysis with limited resources…
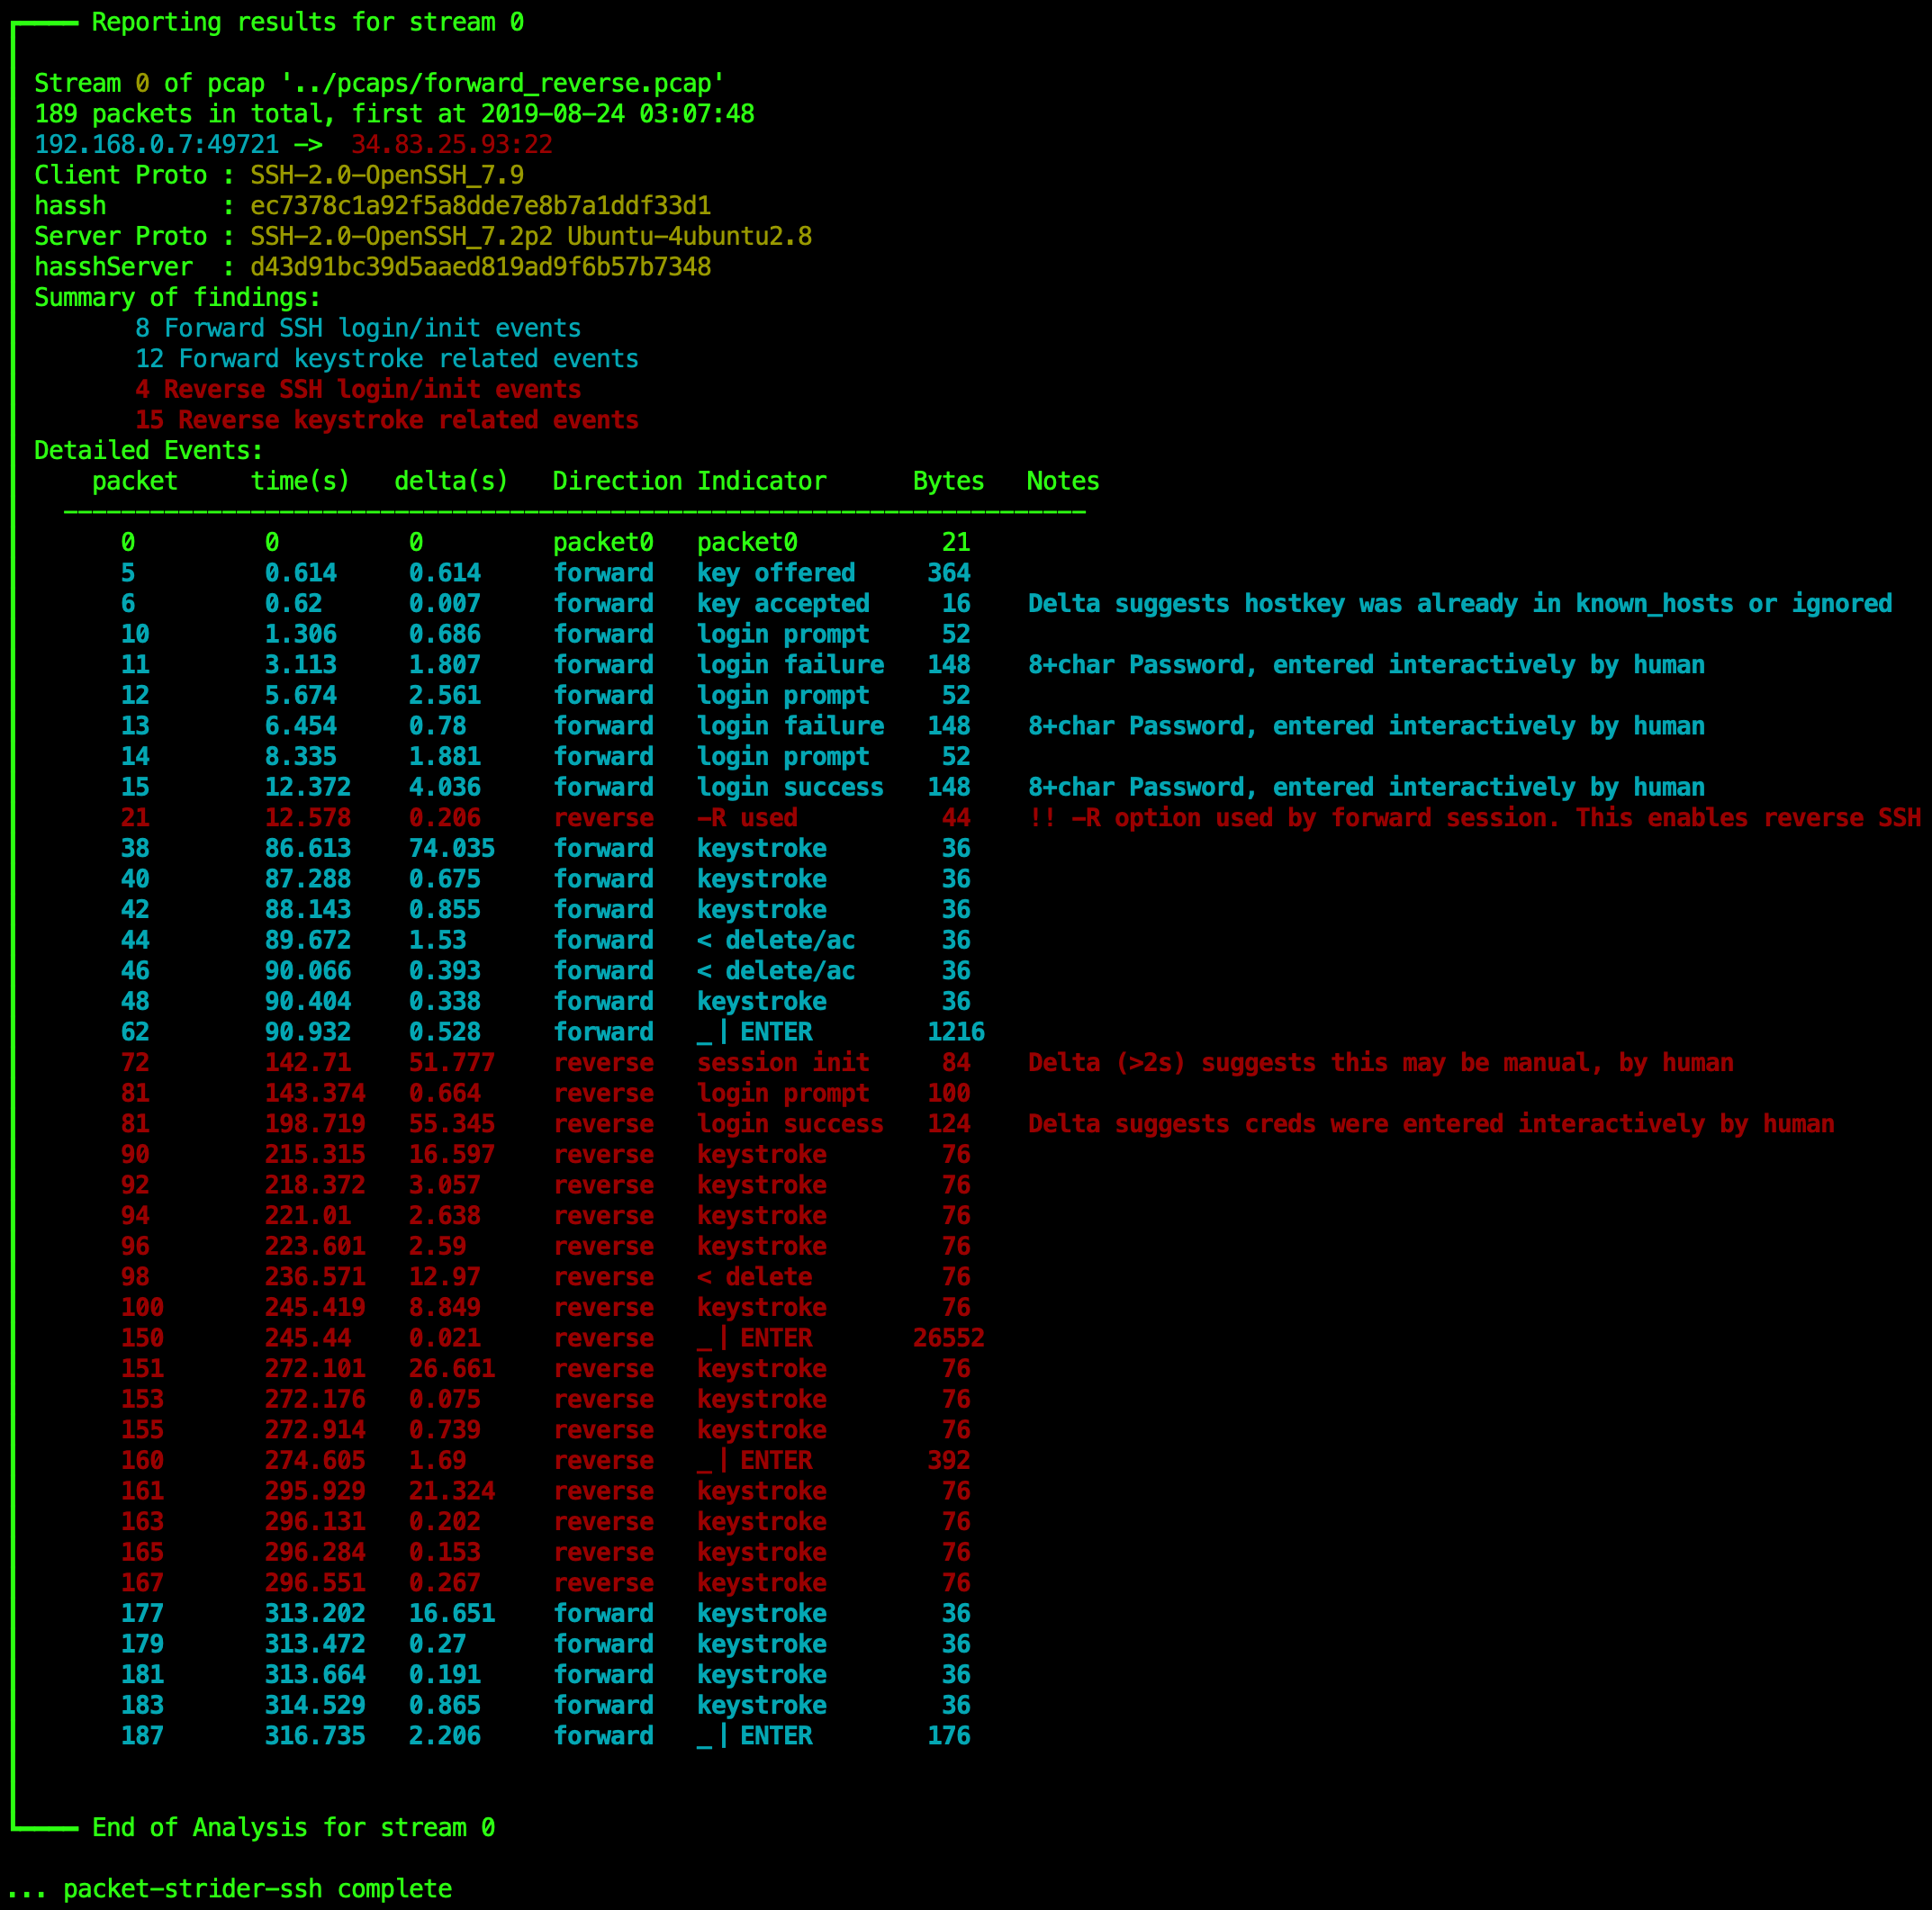 benjeems/packetstrider
A network packet forensics tool for SSH
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
 efforg/rayhunter
Rust tool to detect cell site simulators on an orbic mobile hotspot
 rnehra01/arp-validator
Security Tool to detect arp poisoning attacks
 stratosphereips/aip
Generates efficient IPv4 blocklists from Zeek network flows using multiple prioritization models (new, consistent, random forest) to identify…
 barghest-ngo/mesh
Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…
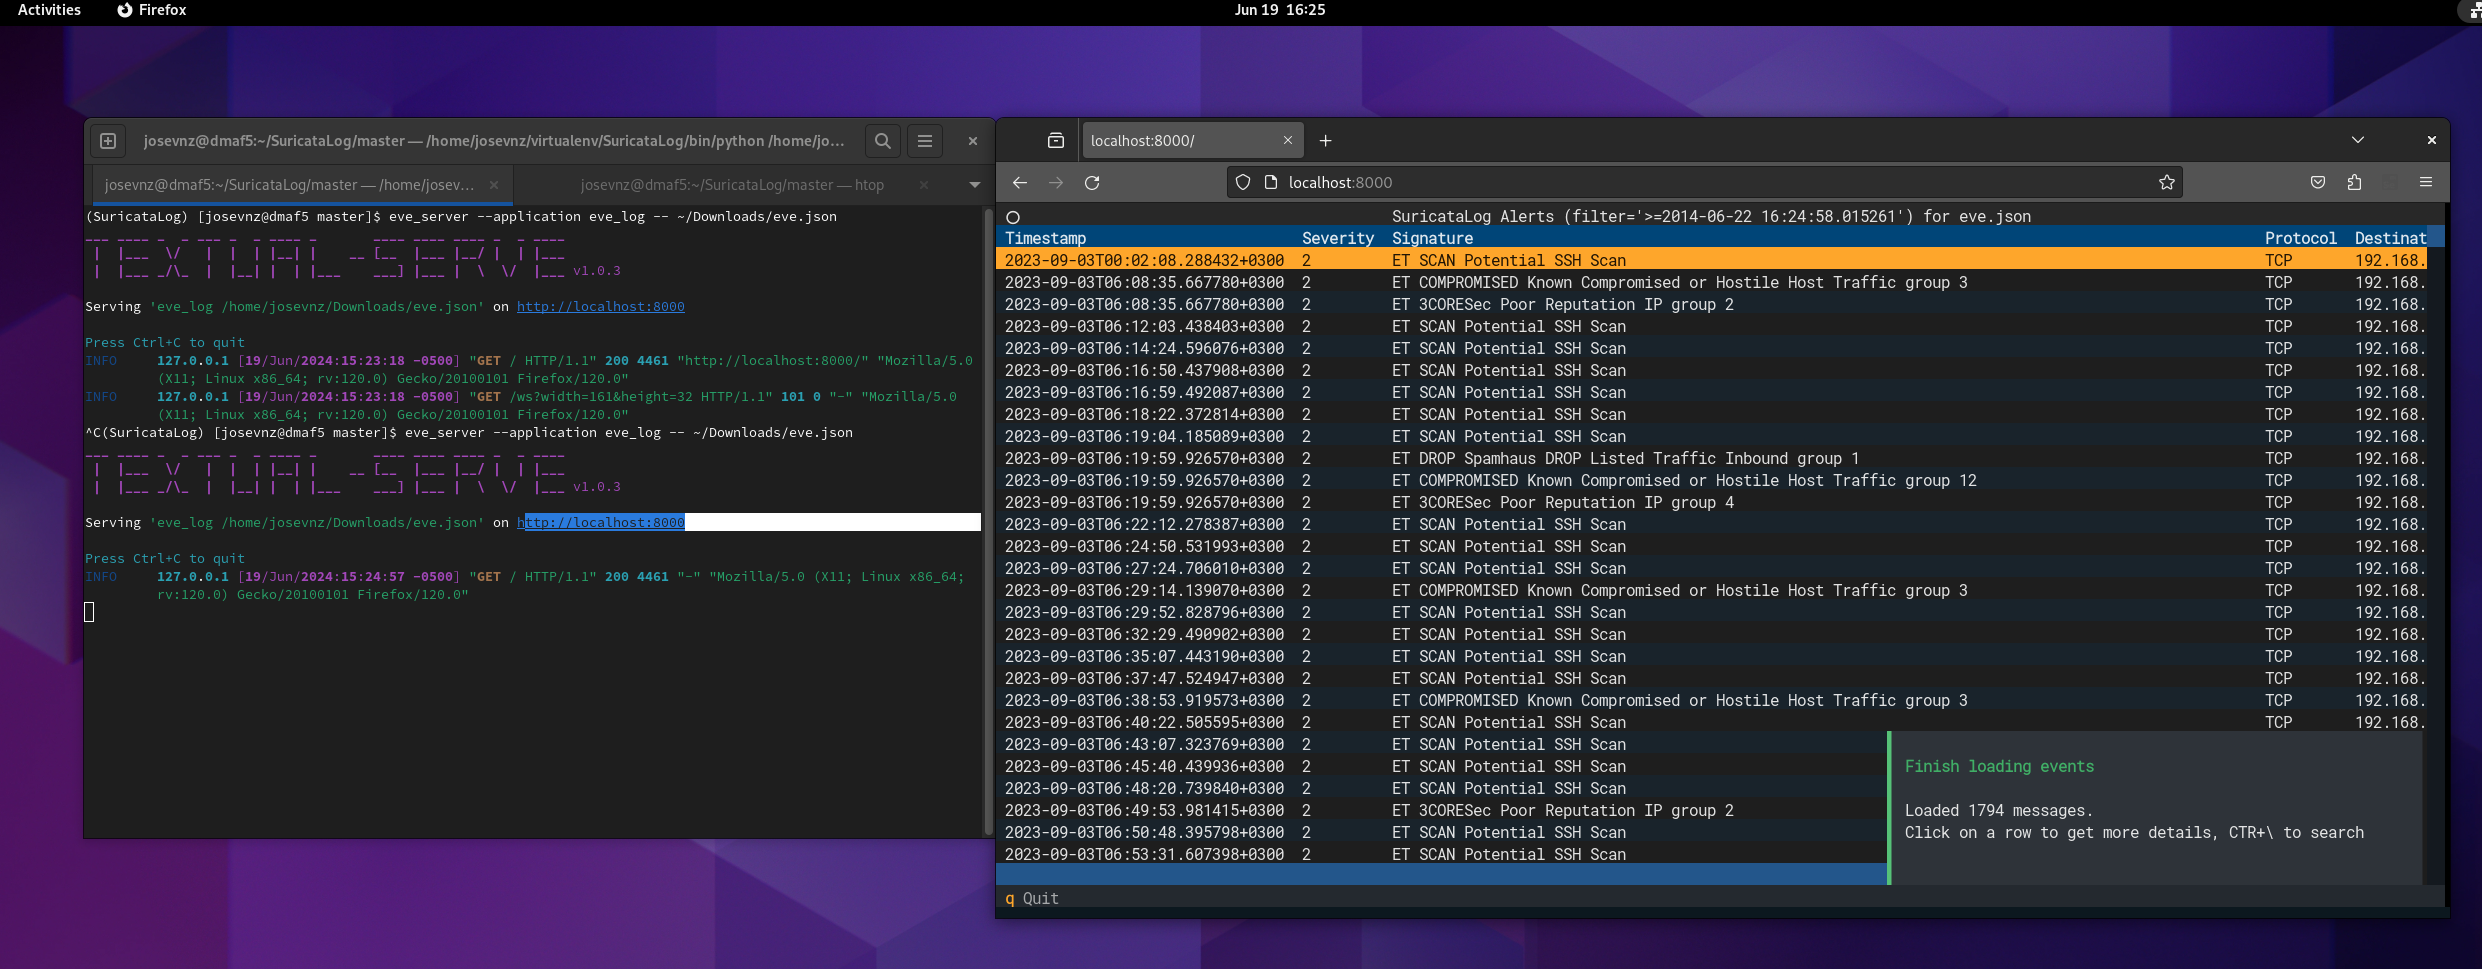 josevnz/suricatalog
Parse, filter, and visualize Suricata eve.json logs with CLI tools for alerts, flows, DNS, and payloads. Includes a tutorial for learning Suricata…
 hullabrian/eventhorizon
Tool that gathers a customizable set of ETW telemetry and generates user-defined detections
 ncsc-nl/citrix-2025
Digital forensics and incident response tool using YARA rules to scan Citrix NetScaler core dumps, disk images, and live hosts for signs of…
 pedramamini/threatingestor
Automated threat intelligence aggregation tool that extracts and normalizes indicators from multiple sources (OSINT feeds, malware reports) into a…
 j-dahl7/mcp-attack-detection-sentinel
Sentinel detection lab for MCP attack chains: CVE-2026-26118 SSRF token theft, tool poisoning, cross-server exfiltration, identity post-exploitation.…
 sans-blue-team/deepbluecli
PowerShell-based threat hunting tool that analyzes Windows Event Logs to detect malicious activity including credential attacks, obfuscated commands,…
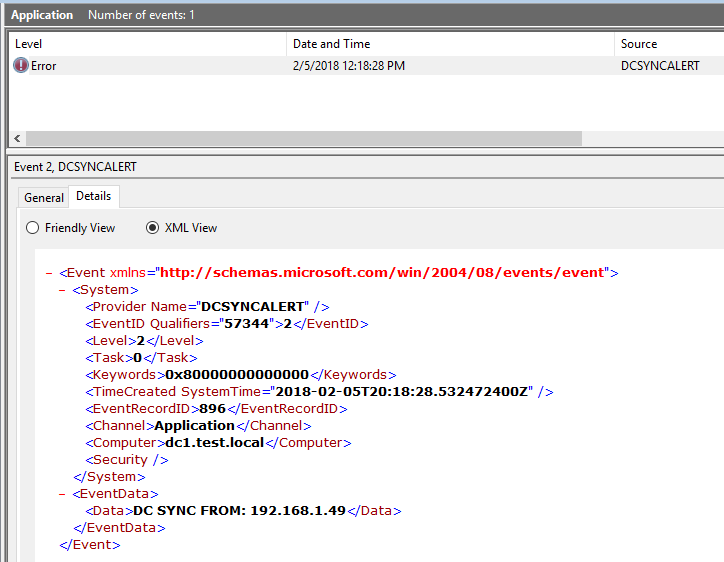 shellster/dcsyncmonitor
Monitors for DCSYNC and DCSHADOW attacks and create custom Windows Events for these events.