
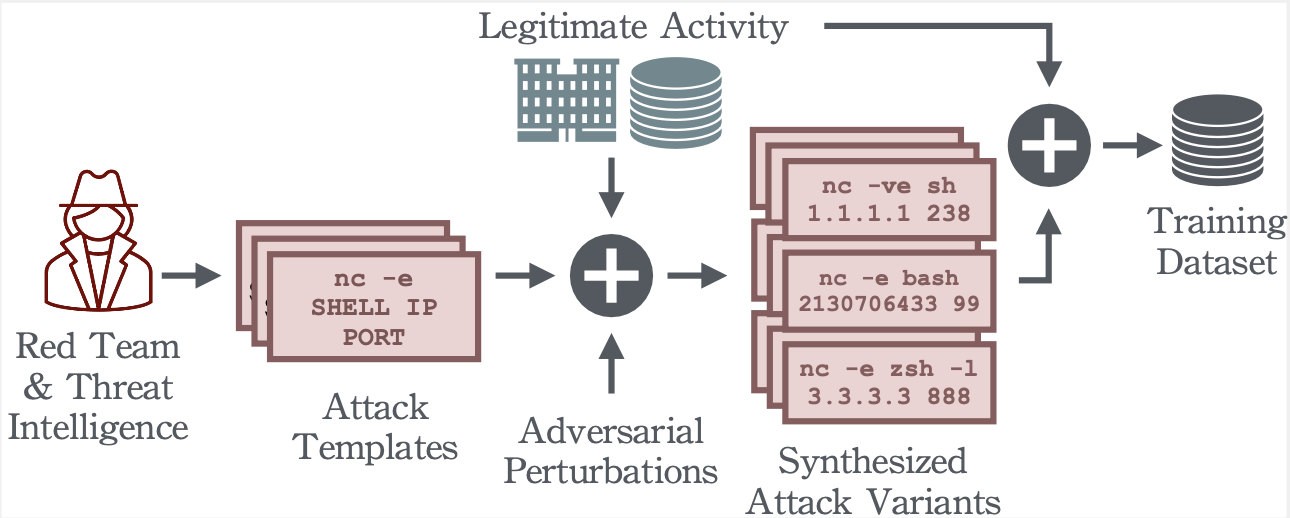
QuasarNix
 dtrizna/quasarnix
Reverse Shell Detection with Machine Learning
adversarial-attackanomaly-detectiondefensive-tools+6
7
dtrizna/quasarnixReverse Shell Detection with Machine Learning
 joertx07/printnightmare-detection-lab
Splunk SIEM lab simulating and detecting CVE-2021-34527 (PrintNightmare) exploitation using Sysmon, Windows Event logs, and custom SPL detection…
 harshiys/cve-2007-2447-exploitation-siem-detection-lab
Isolated AD/Linux attack lab: exploited CVE-2007-2447 via Metasploit, detected with Wazuh SIEM mapped to MITRE ATT&CK (T1190, T1059)
 rvazarkar/antipwny
A host based IDS written in C# Targetted at Metasploit
 sans-blue-team/deepbluecli
PowerShell-based threat hunting tool that analyzes Windows Event Logs to detect malicious activity including credential attacks, obfuscated commands,…
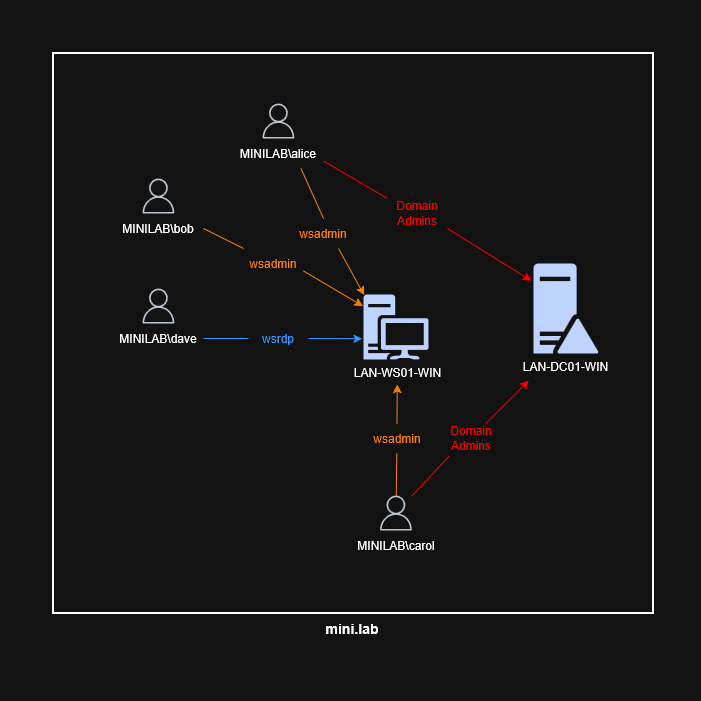 0xmr007/lab4purplesec
Lab4PurpleSec is a modular Purple Team homelab combining a vulnerable Active Directory environment (GOAD), a Docker-based web DMZ, pfSense +…
 travisbgreen/hunting-rules
Suricata rules for network anomaly detection
 thomaspatzke/log4pot
A honeypot for the Log4Shell vulnerability (CVE-2021-44228).
 malwaretech/log4jtools
Tools for investigating Log4j CVE-2021-44228
 rushyo/vindicatetool
LLMNR/NBNS/mDNS Spoofing Detection Toolkit
 agentshield-ai/sigma-ai
Sigma detection rules for AI agent security monitoring
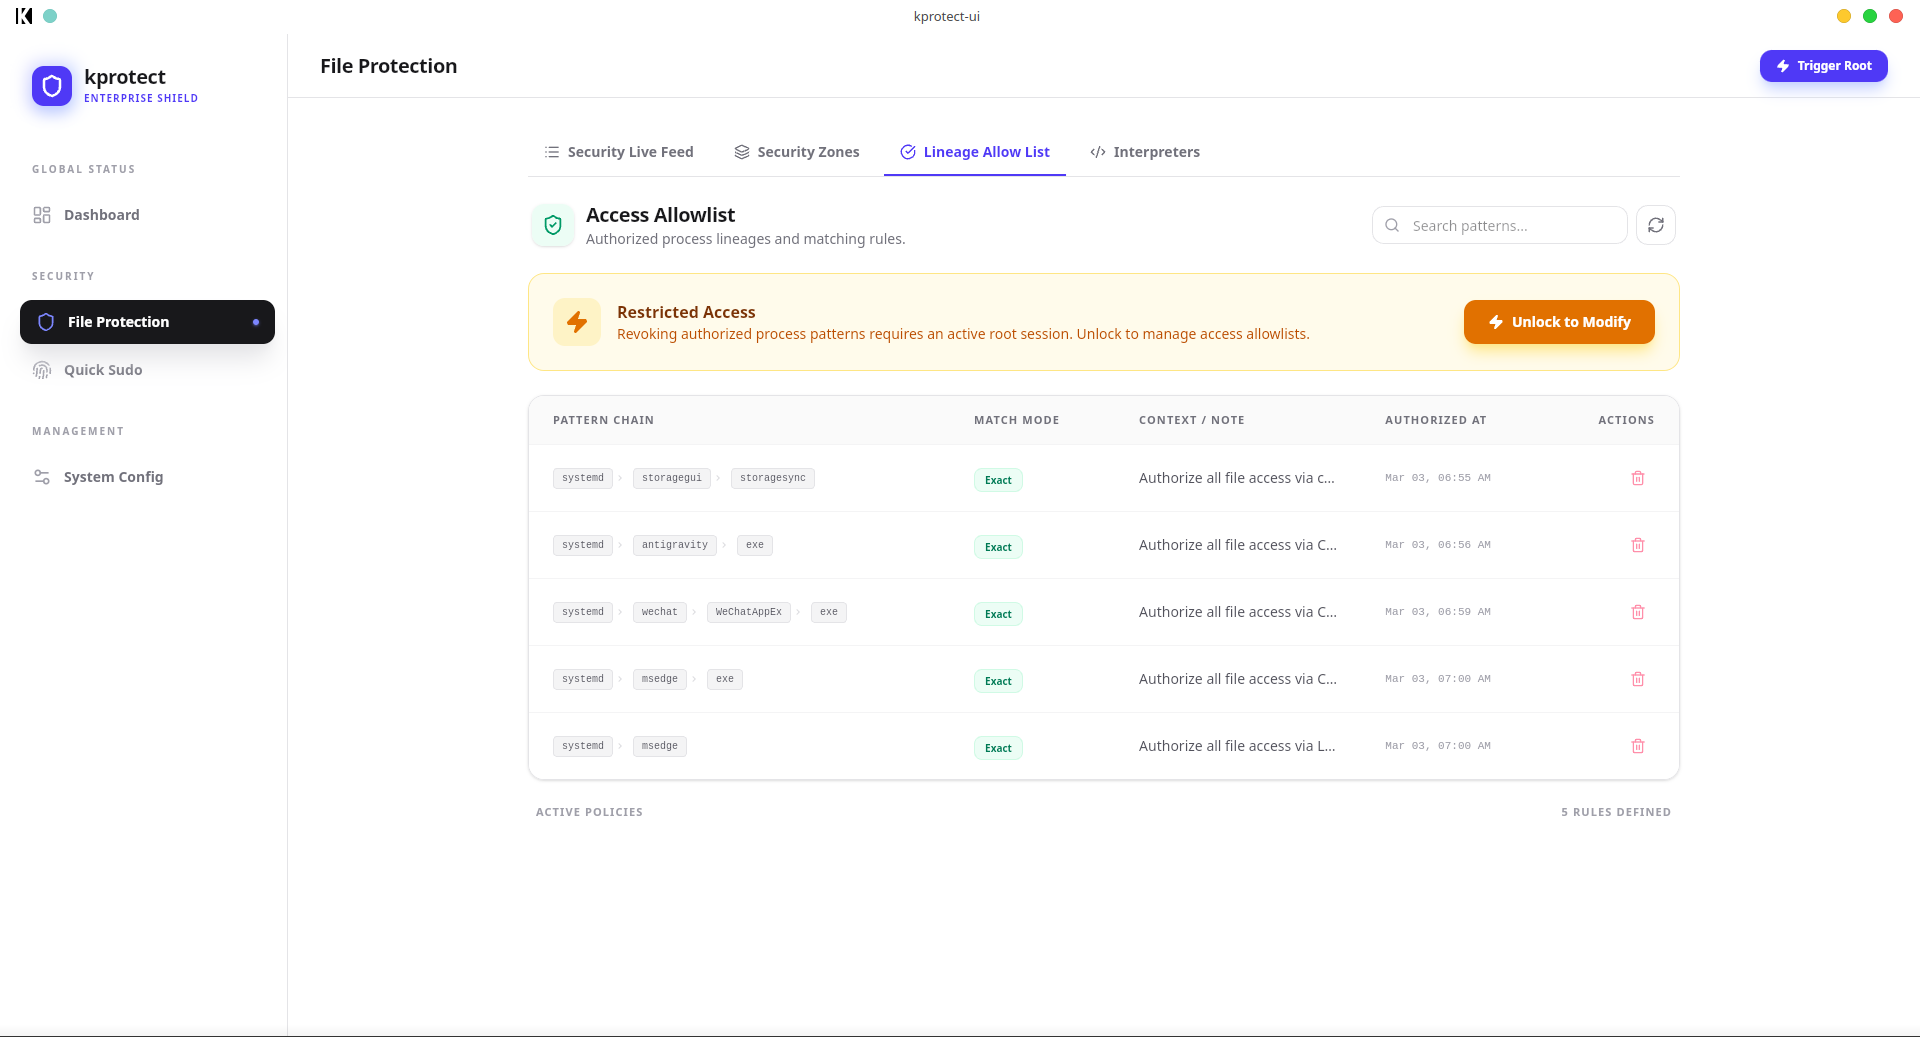 khoinp1012/kprotect
Kernel-level security engine using eBPF-LSM to enforce file access policies based on process lineage, protecting sensitive data from supply-chain…
 arpsyndicate/suricata-vedas
VEDAS-Driven Autonomous Generation of Suricata Rules for CVEs
 corelight/zerologon
Zeek package to detect Zerologon
 mandiant/vcsa-hardening-tool
Automated Zero Trust hardening and forensic auditing for VMware vCenter Server Appliance (VCSA)
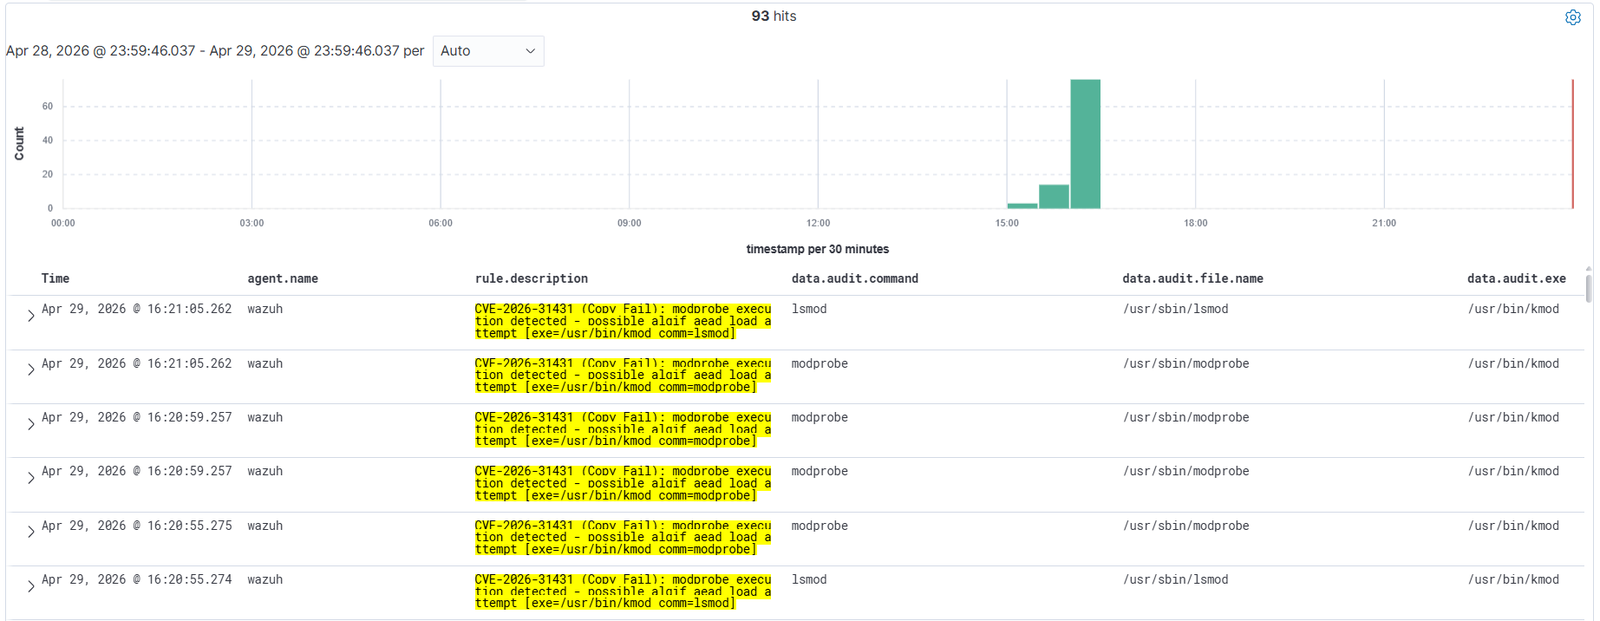 mym0us3r/copy-fail-detection-with-wazuh-4.14.4
Wazuh 4.14.4 detection rules for CVE-2026-31431 (Copy Fail) - Linux Local Privilege Escalation via authencesn page cache write
 kuniyal08/dirty-frag-cve-2026-43284
A report on Dirty Frag, which is a Linux Local Privilege Escalation (LPE) vulnerability chain that allows an unprivileged user to gain root access