
Malcolm
 idaholab/malcolm
Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
defensive-toolsdigital-forensicsforensics+8
488
idaholab/malcolmMalcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
 codextf2/cobaltstrike-sleepmask-yara
Just a git repo for the sleepmask detection rule i found in https://codex-7.gitbook.io/codexs-terminal-window/blue-team/detecting-cobalt-strike/sleep-…
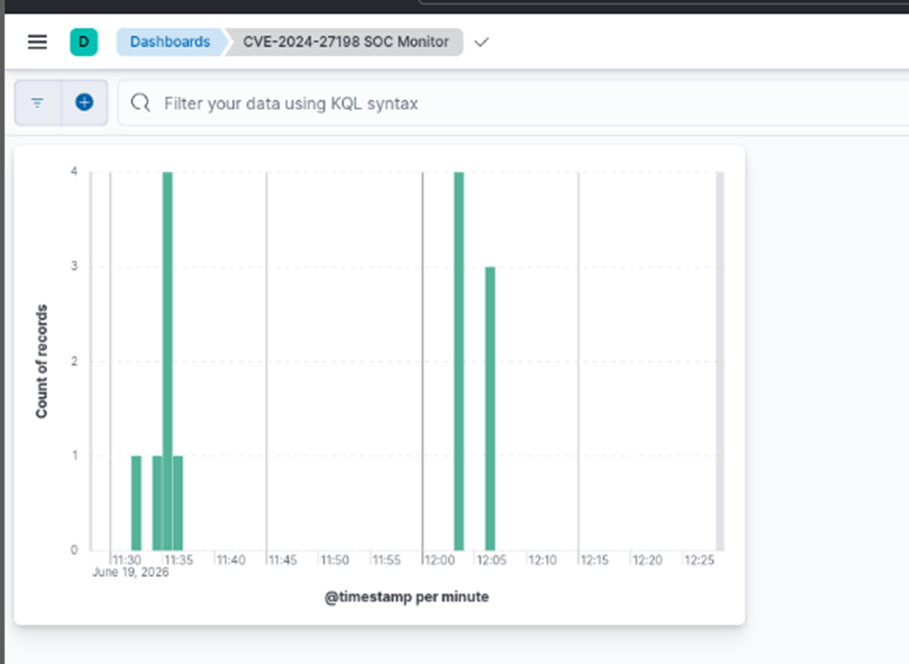 ptd200110/cve-2024-27198-soc-lab
SOC detection and incident response lab simulating CVE-2024-27198 authentication bypass in JetBrains TeamCity. Includes ELK SIEM, Suricata IDS, Sigma…
 google/stenographer
Stenographer is a packet capture solution which aims to quickly spool all packets to disk, then provide simple, fast access to subsets of those…
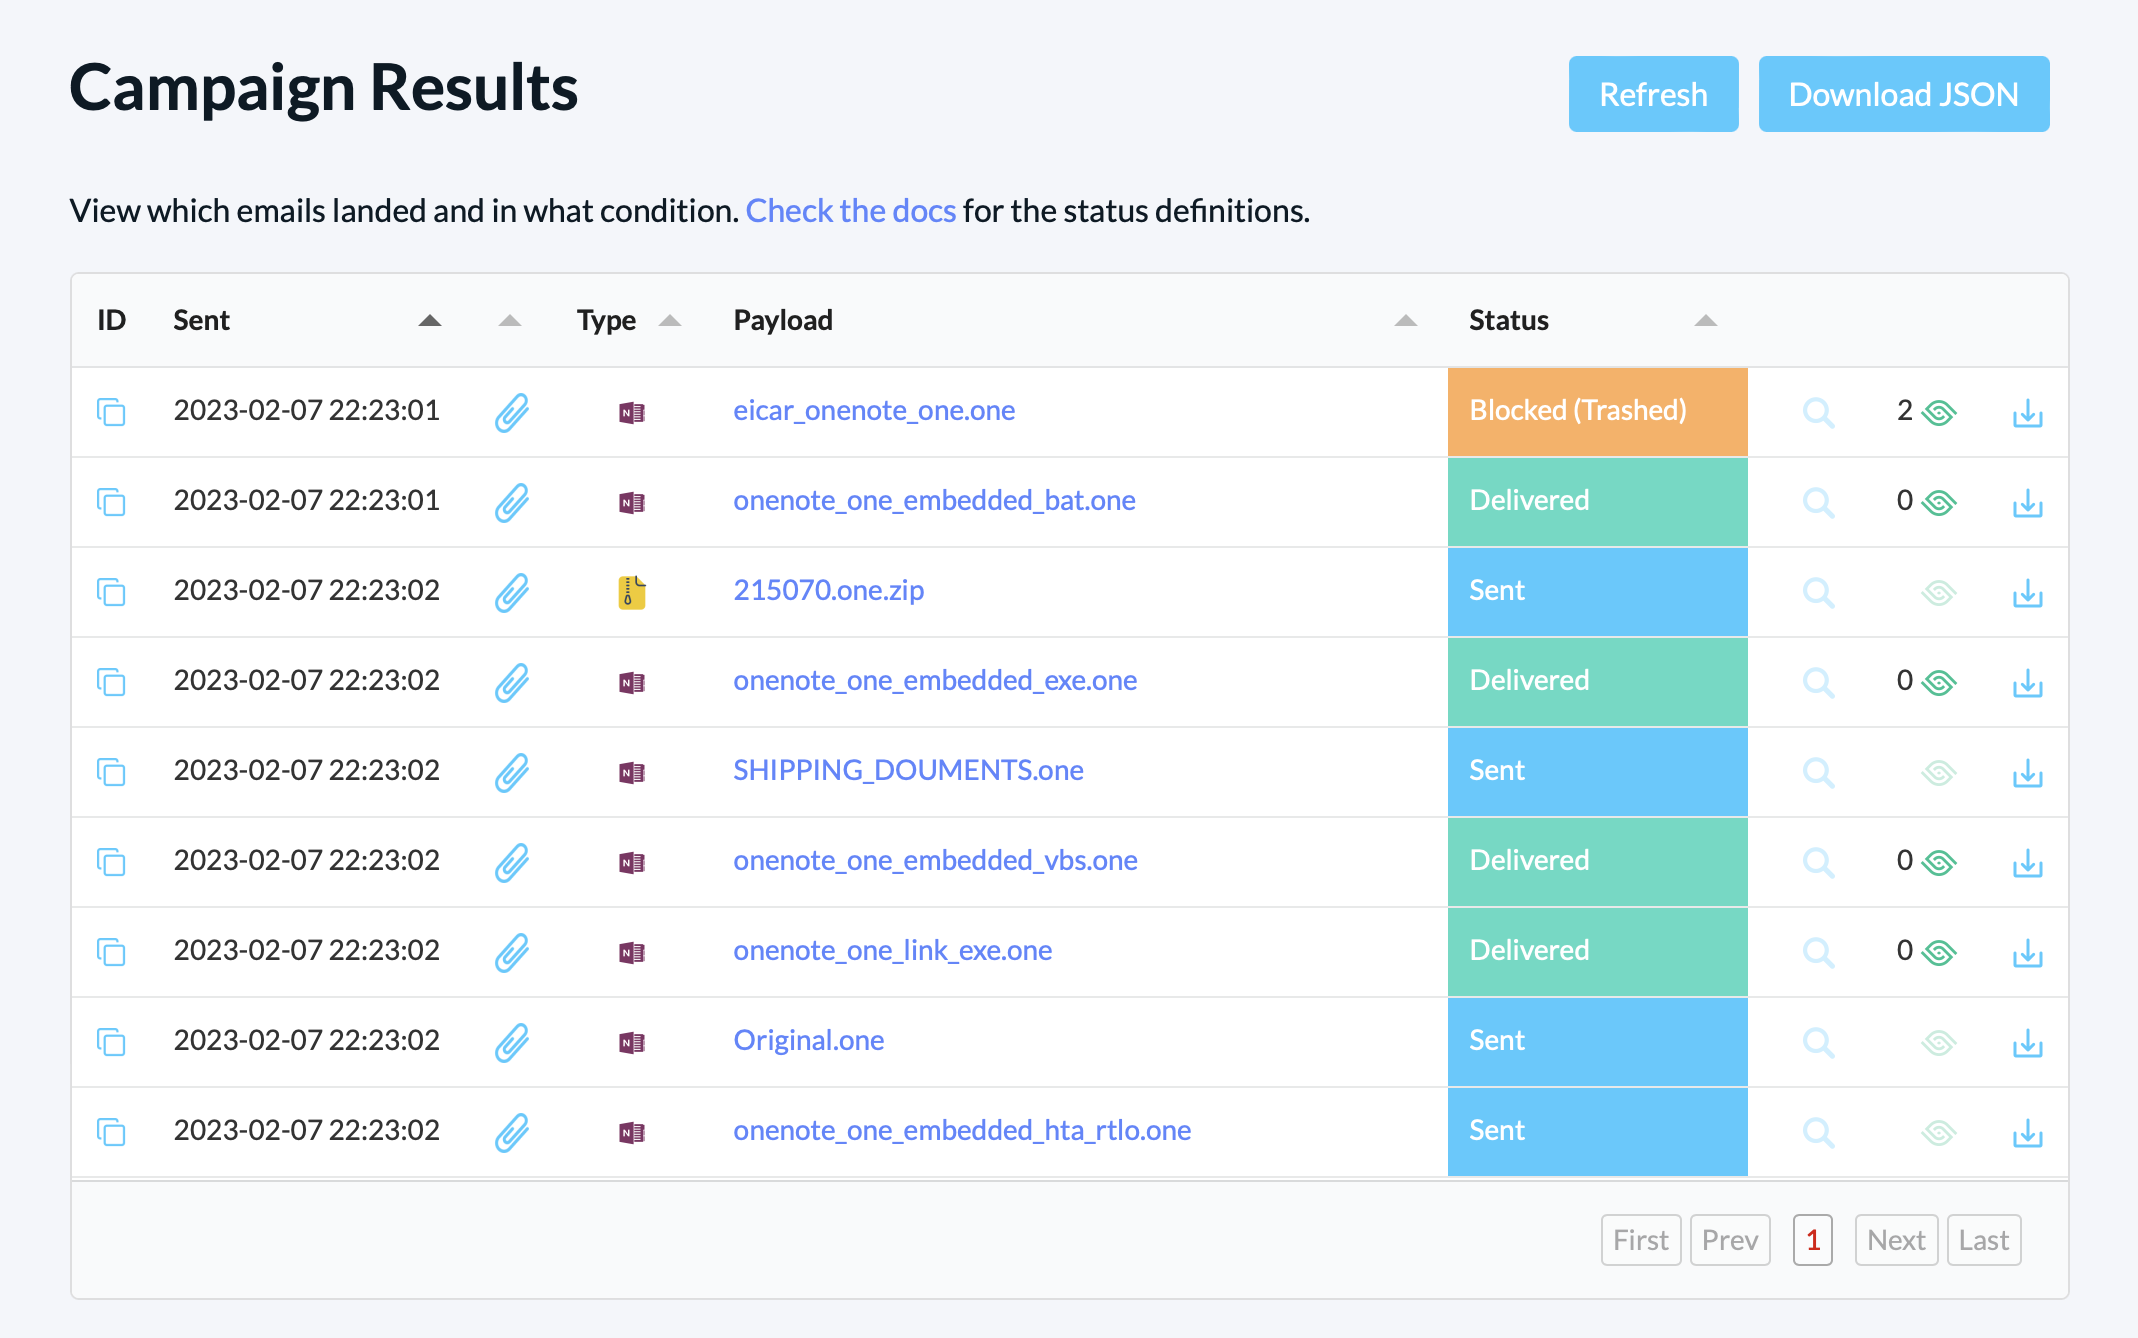 delivr-to/detections
A home for detection content developed by the delivr.to team
 u1tr0nex/cve-2022-30190-follina-lab
Full exploit chain lab and Suricata IDS detection for CVE-2022-30190 (Follina) - MSDT RCE
 mushorg/buttinsky
Botnet monitoring is a crucial part in threat analysis and often neglected due to the lack of proper open source tools. Our tool will provide an open…
 adnansiyat/how-to-patch-cve-2025-32709
Real-world patching workflow for CVE-2025-32709. From hotfix install to SIEM alert validation—this repo documents every step with screenshots,…
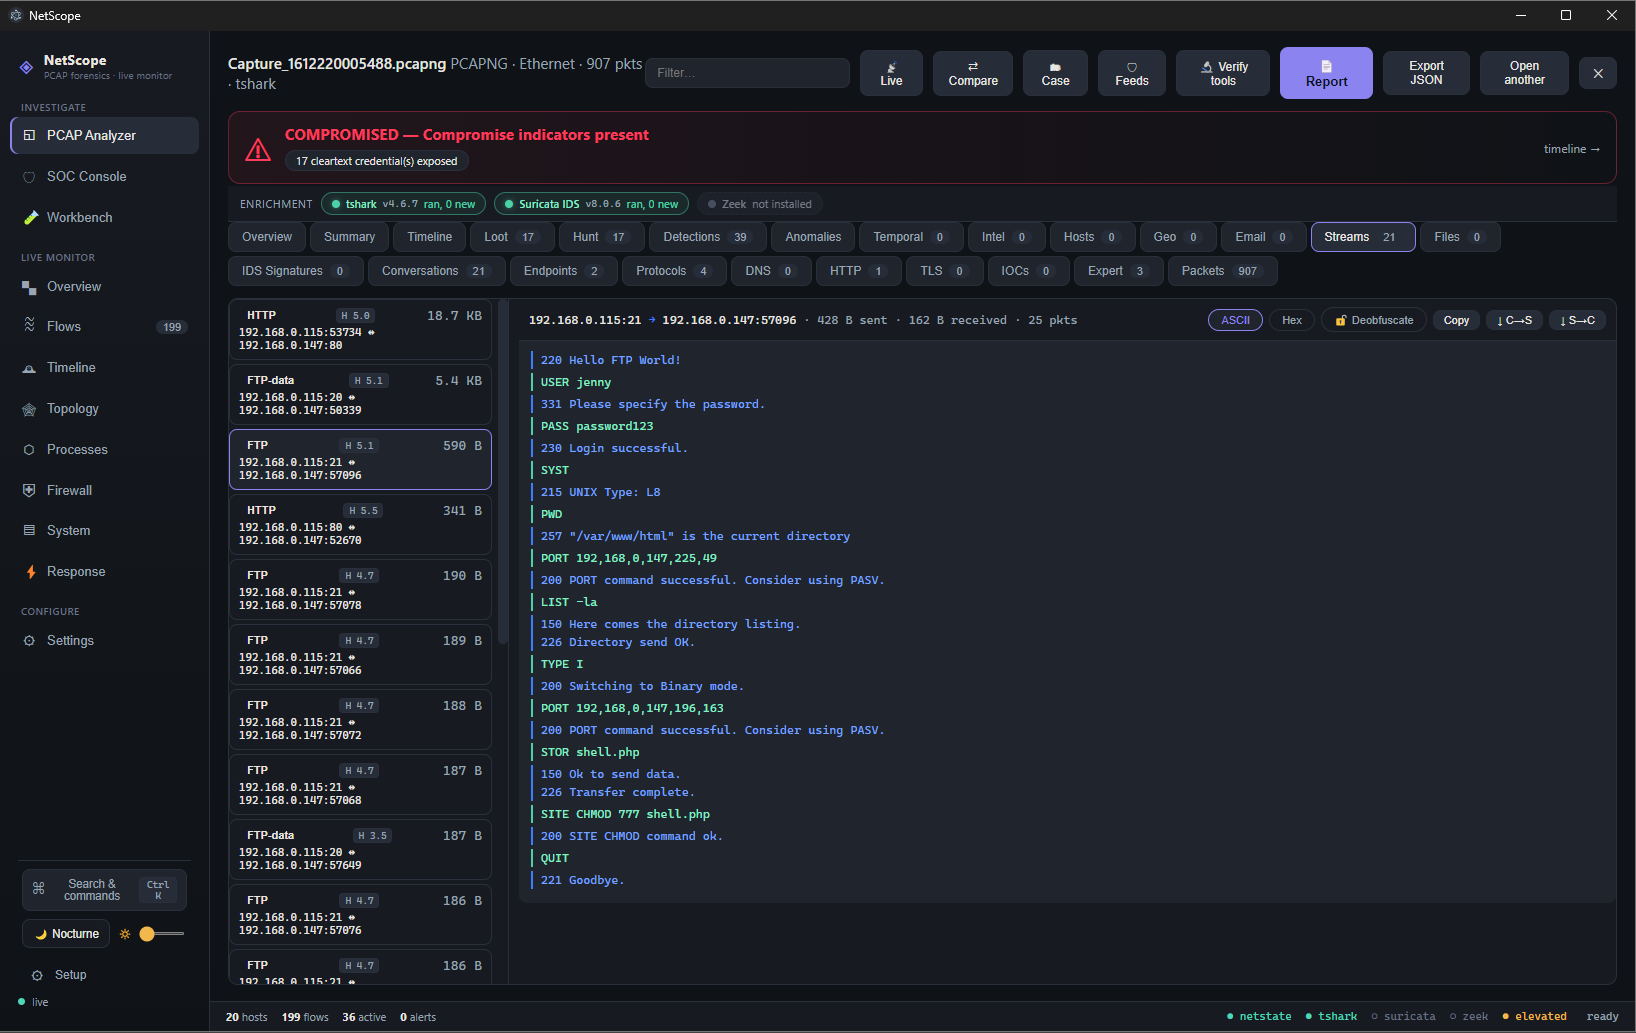 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
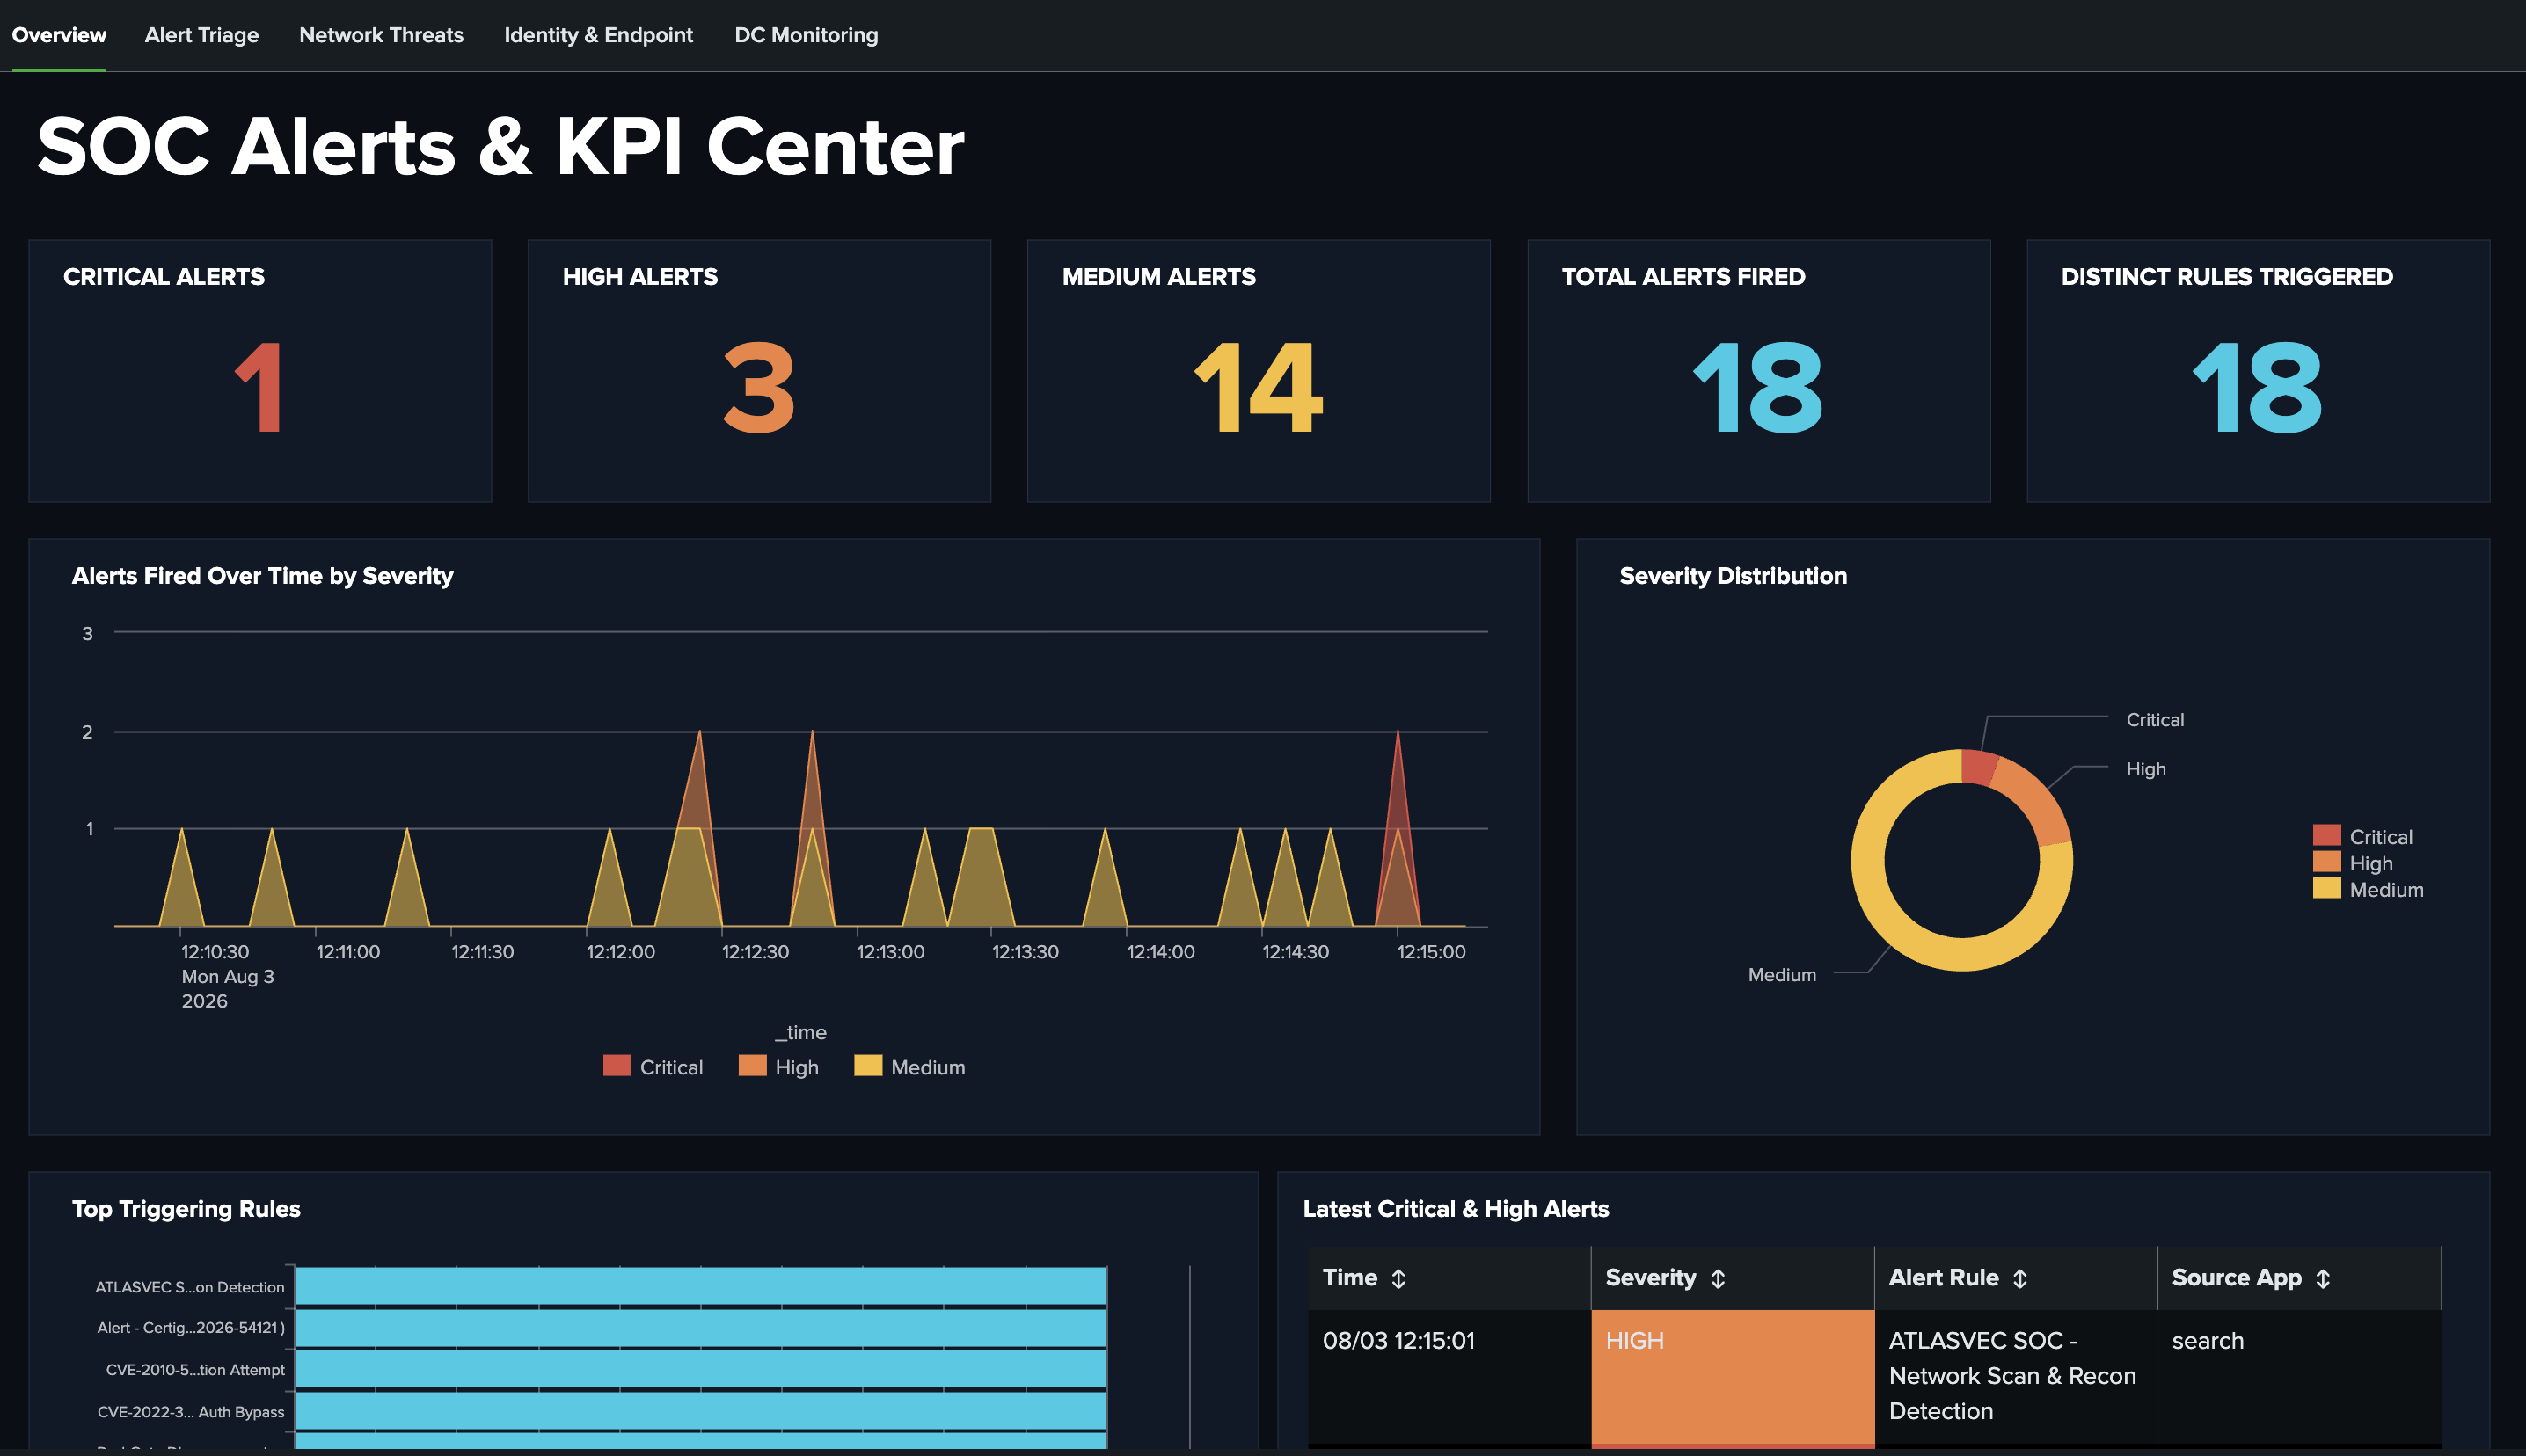 atlasvector/certighost-cve-2026-54121
Splunk detection writeup for CVE-2026-54121 (CertiGhost): AD CS certificate chase abuse leading to full domain compromise. Lab-validated detection,…
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
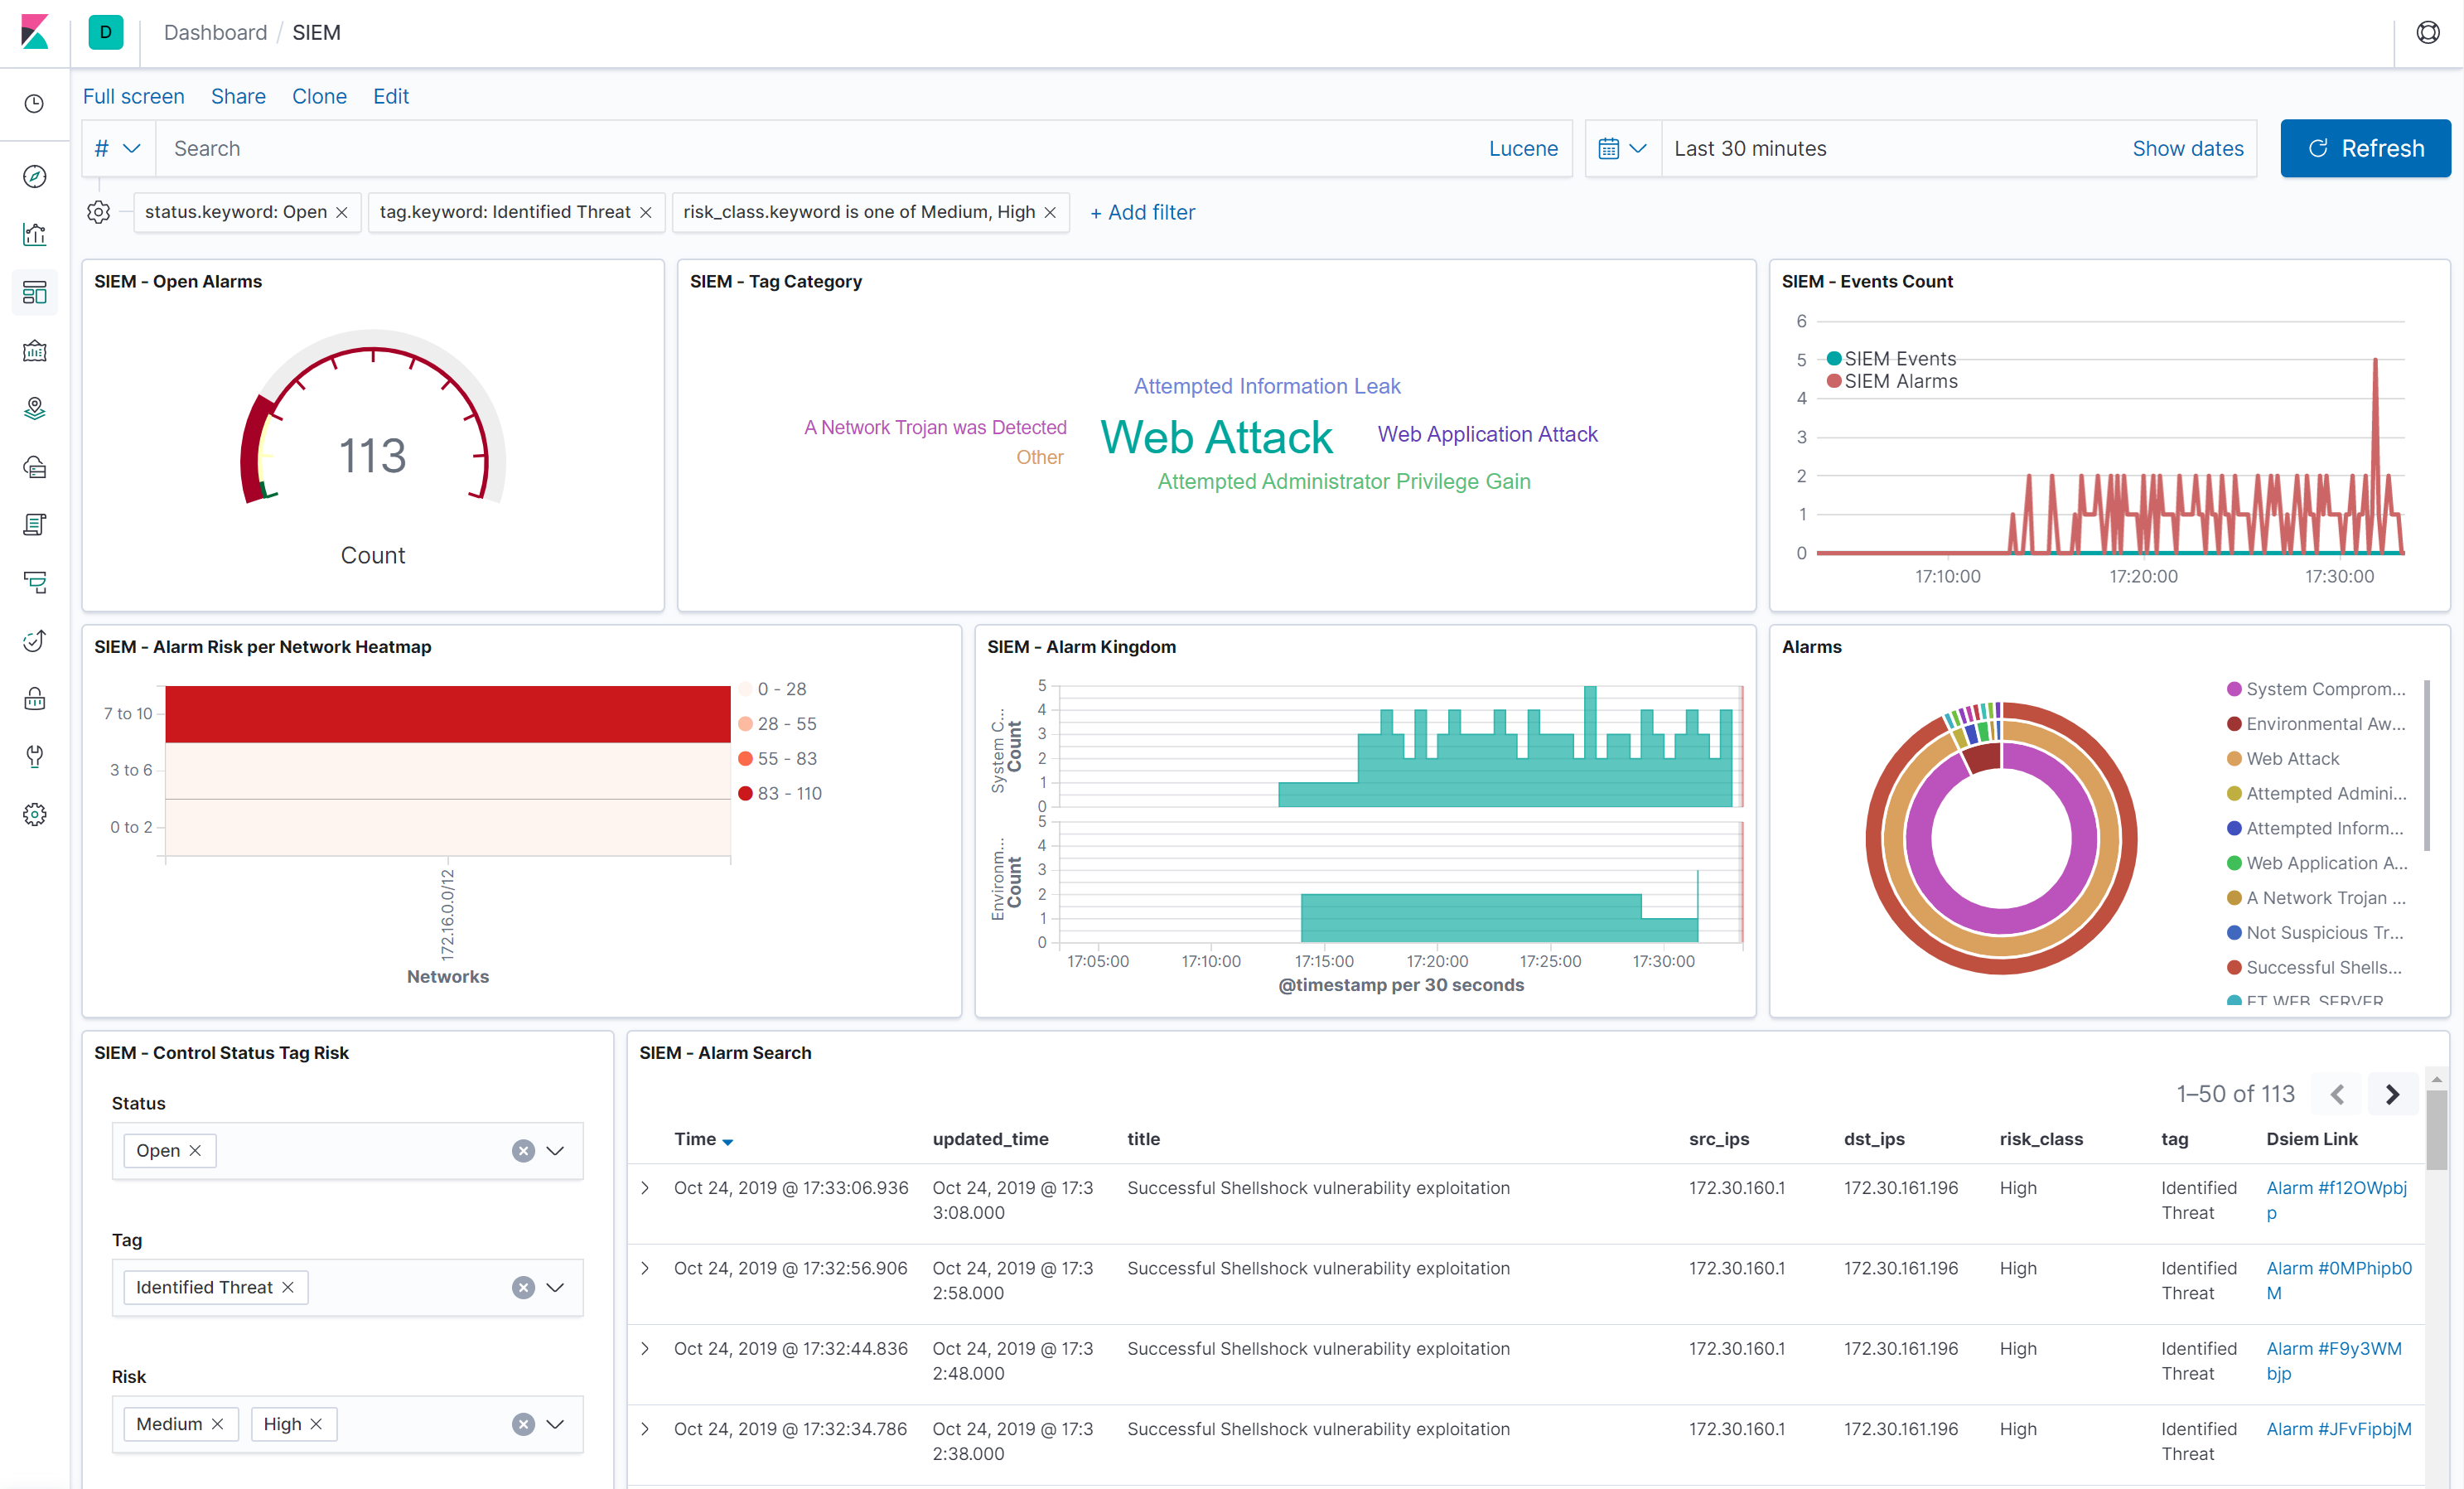 defenxor/dsiem
Security event correlation engine for ELK stack
 backbay-labs/thrunt-god
Threat hunting command system for agentic IDEs
 security-onion-solutions/security-onion
Security Onion 16.04 - Linux distro for threat hunting, enterprise security monitoring, and log management
 tungduongnt/cve-2014-0160.
Docker-based lab environment for exploiting CVE-2014-0160 (Heartbleed) to leak sensitive memory from nginx web servers, with Snort IDS detection…
 22imer/cve-2014-0160
Dockerized training lab for exploiting Heartbleed (CVE-2014-0160) via TLS heartbeat to leak nginx memory, plus Snort rule to detect attacks.
 cisc0-gif/netcrackpi
RPi3+ Network Cracker Setup Tool
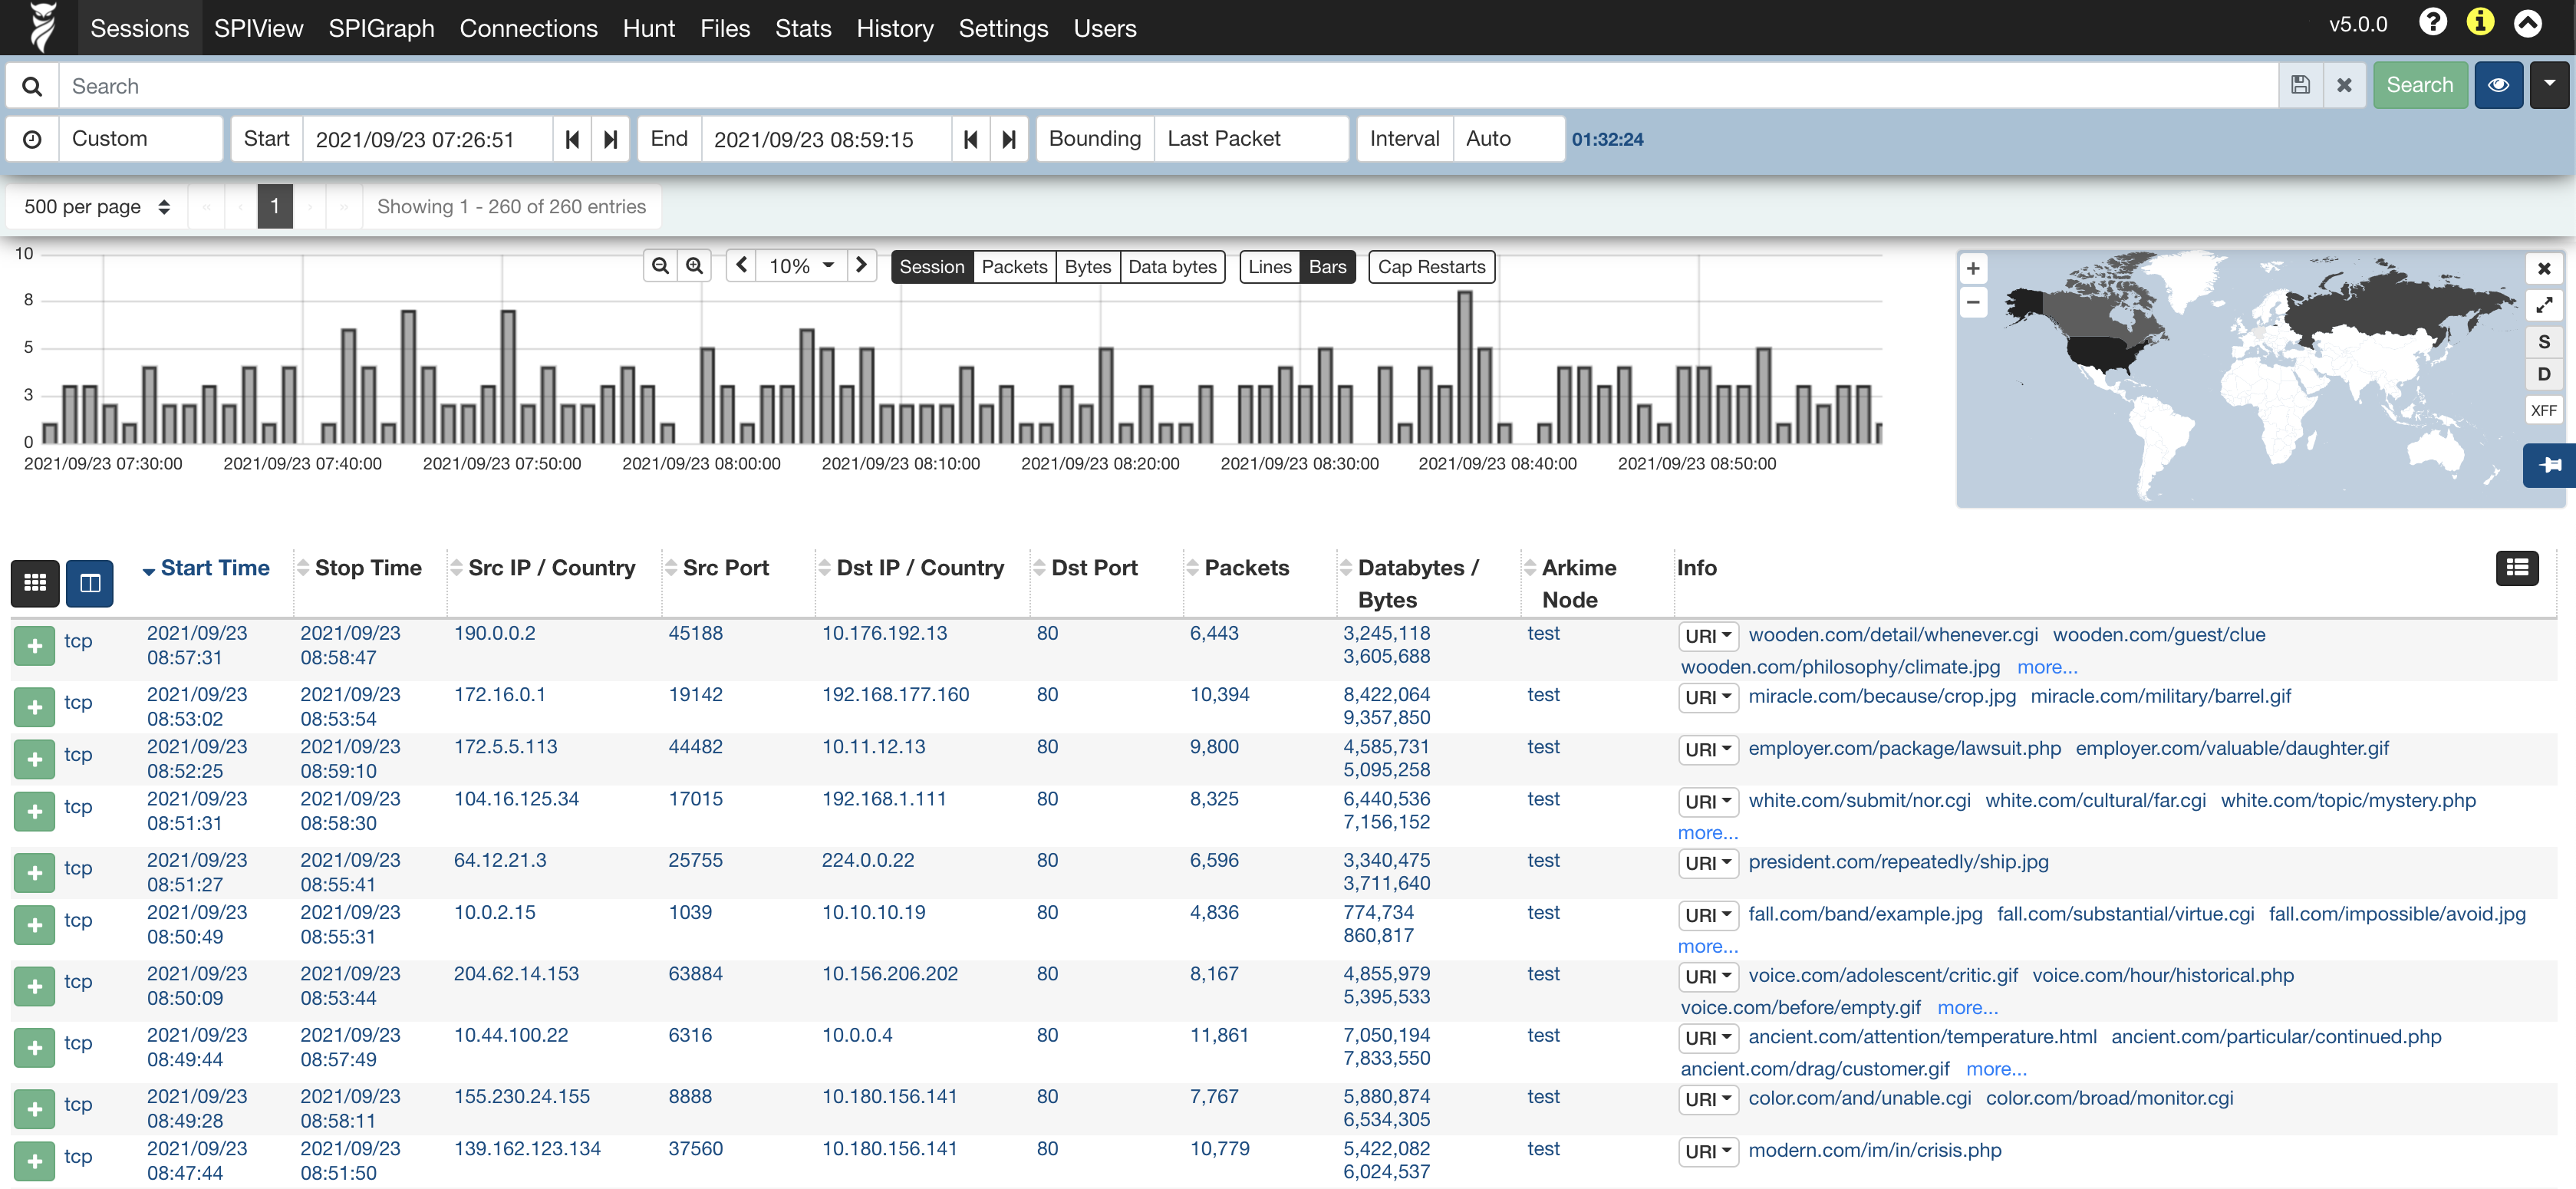 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.