logdata-anomaly-miner

This tool parses log data and allows to define analysis pipelines for anomaly detection. It was designed to run the analysis with limited resources…

This tool parses log data and allows to define analysis pipelines for anomaly detection. It was designed to run the analysis with limited resources…

A collection of Tools and Rules for decoding Brute Ratel C4 badgers

An eBPF-powered Active Defense system that turns your Linux server into a deceptive honeypot. Features transparent traffic redirection, OS…

Machine Learning based Intrusion Detection Systems are difficult to evaluate due to a shortage of datasets representing accurately network traffic…

Rust tool to detect cell site simulators on an orbic mobile hotspot

PowerShell-based threat hunting tool that analyzes Windows Event Logs to detect malicious activity including credential attacks, obfuscated commands,…

File integrity monitoring tool that detects unauthorized changes to monitored files and directories using attribute checks, multiple hash algorithms,…

Automated threat intelligence aggregation tool that extracts and normalizes indicators from multiple sources (OSINT feeds, malware reports) into a…

Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…

Open-source blue team tool that protects Linux and Windows systems using multiple host and network defense and detection methods.

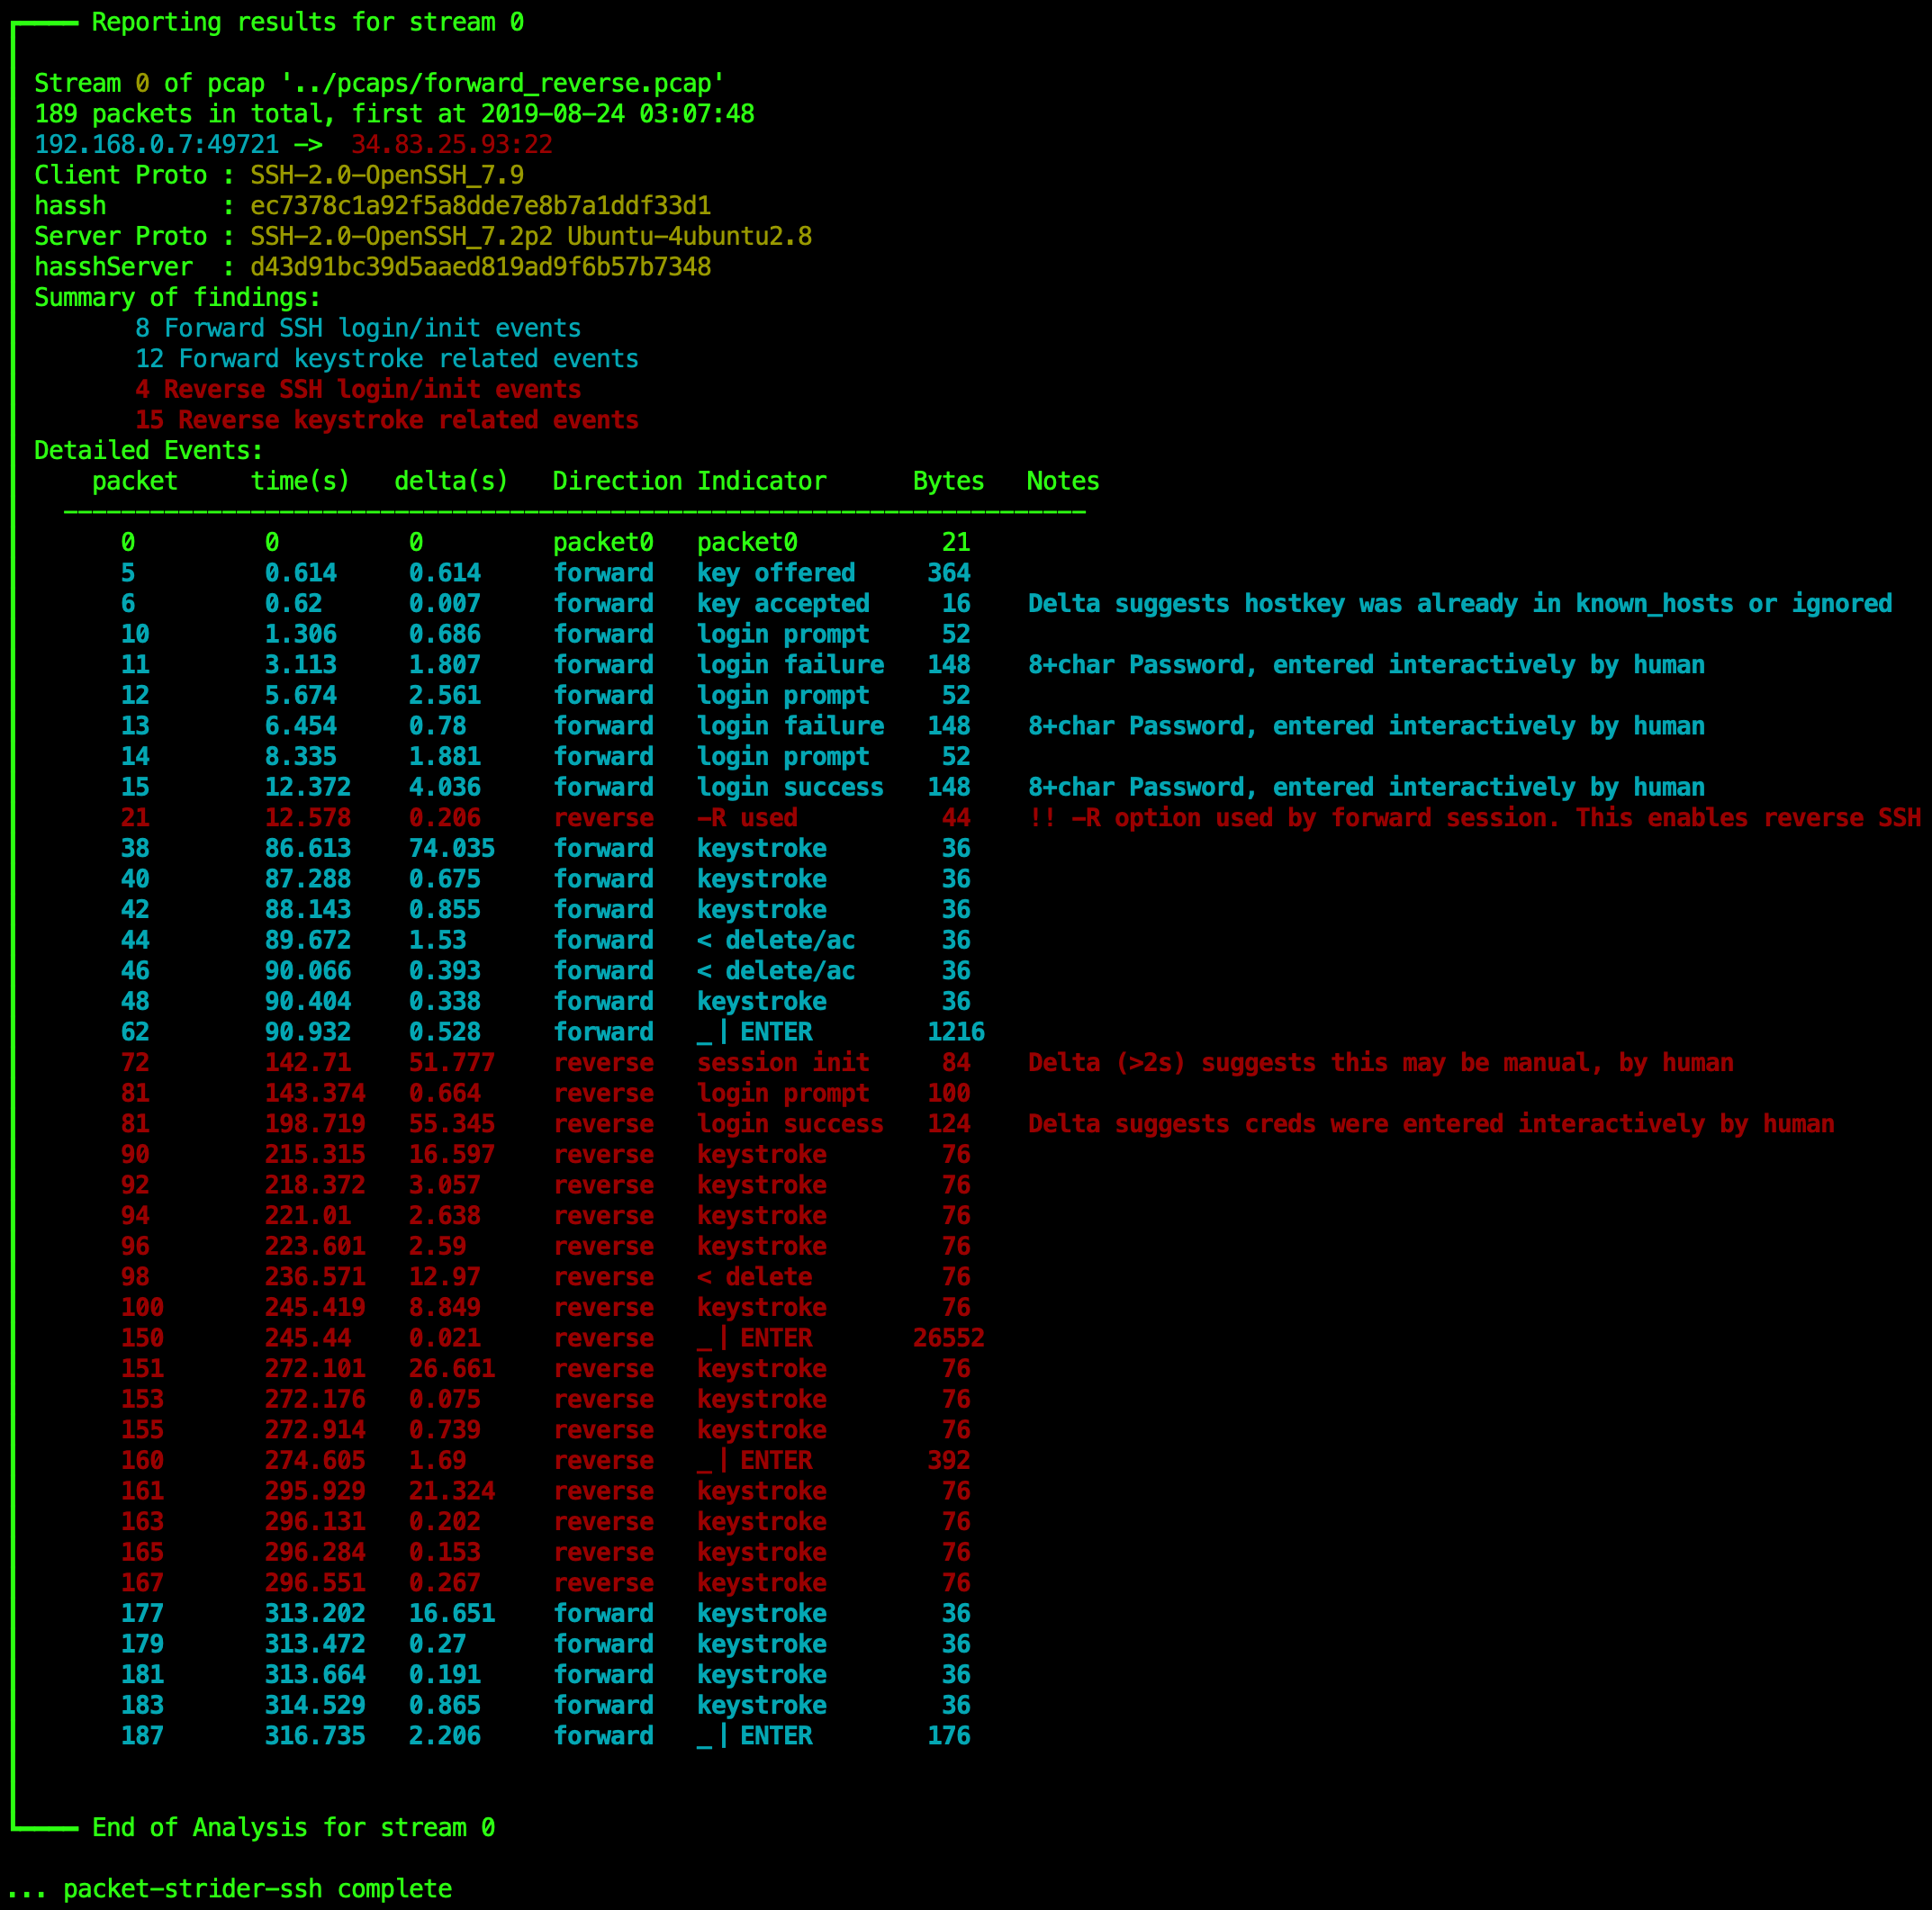
A network packet forensics tool for SSH

Botnet monitoring is a crucial part in threat analysis and often neglected due to the lack of proper open source tools. Our tool will provide an open…

Kernel-level eBPF sandbox for securing LLM agent tool calls made through the Model Context Protocol (MCP)

A tool for malicious behavior detection in IoT devices

A process monitoring tool that tries to detect exploitation

Conveigh is a Windows PowerShell LLMNR/NBNS spoofer detection tool


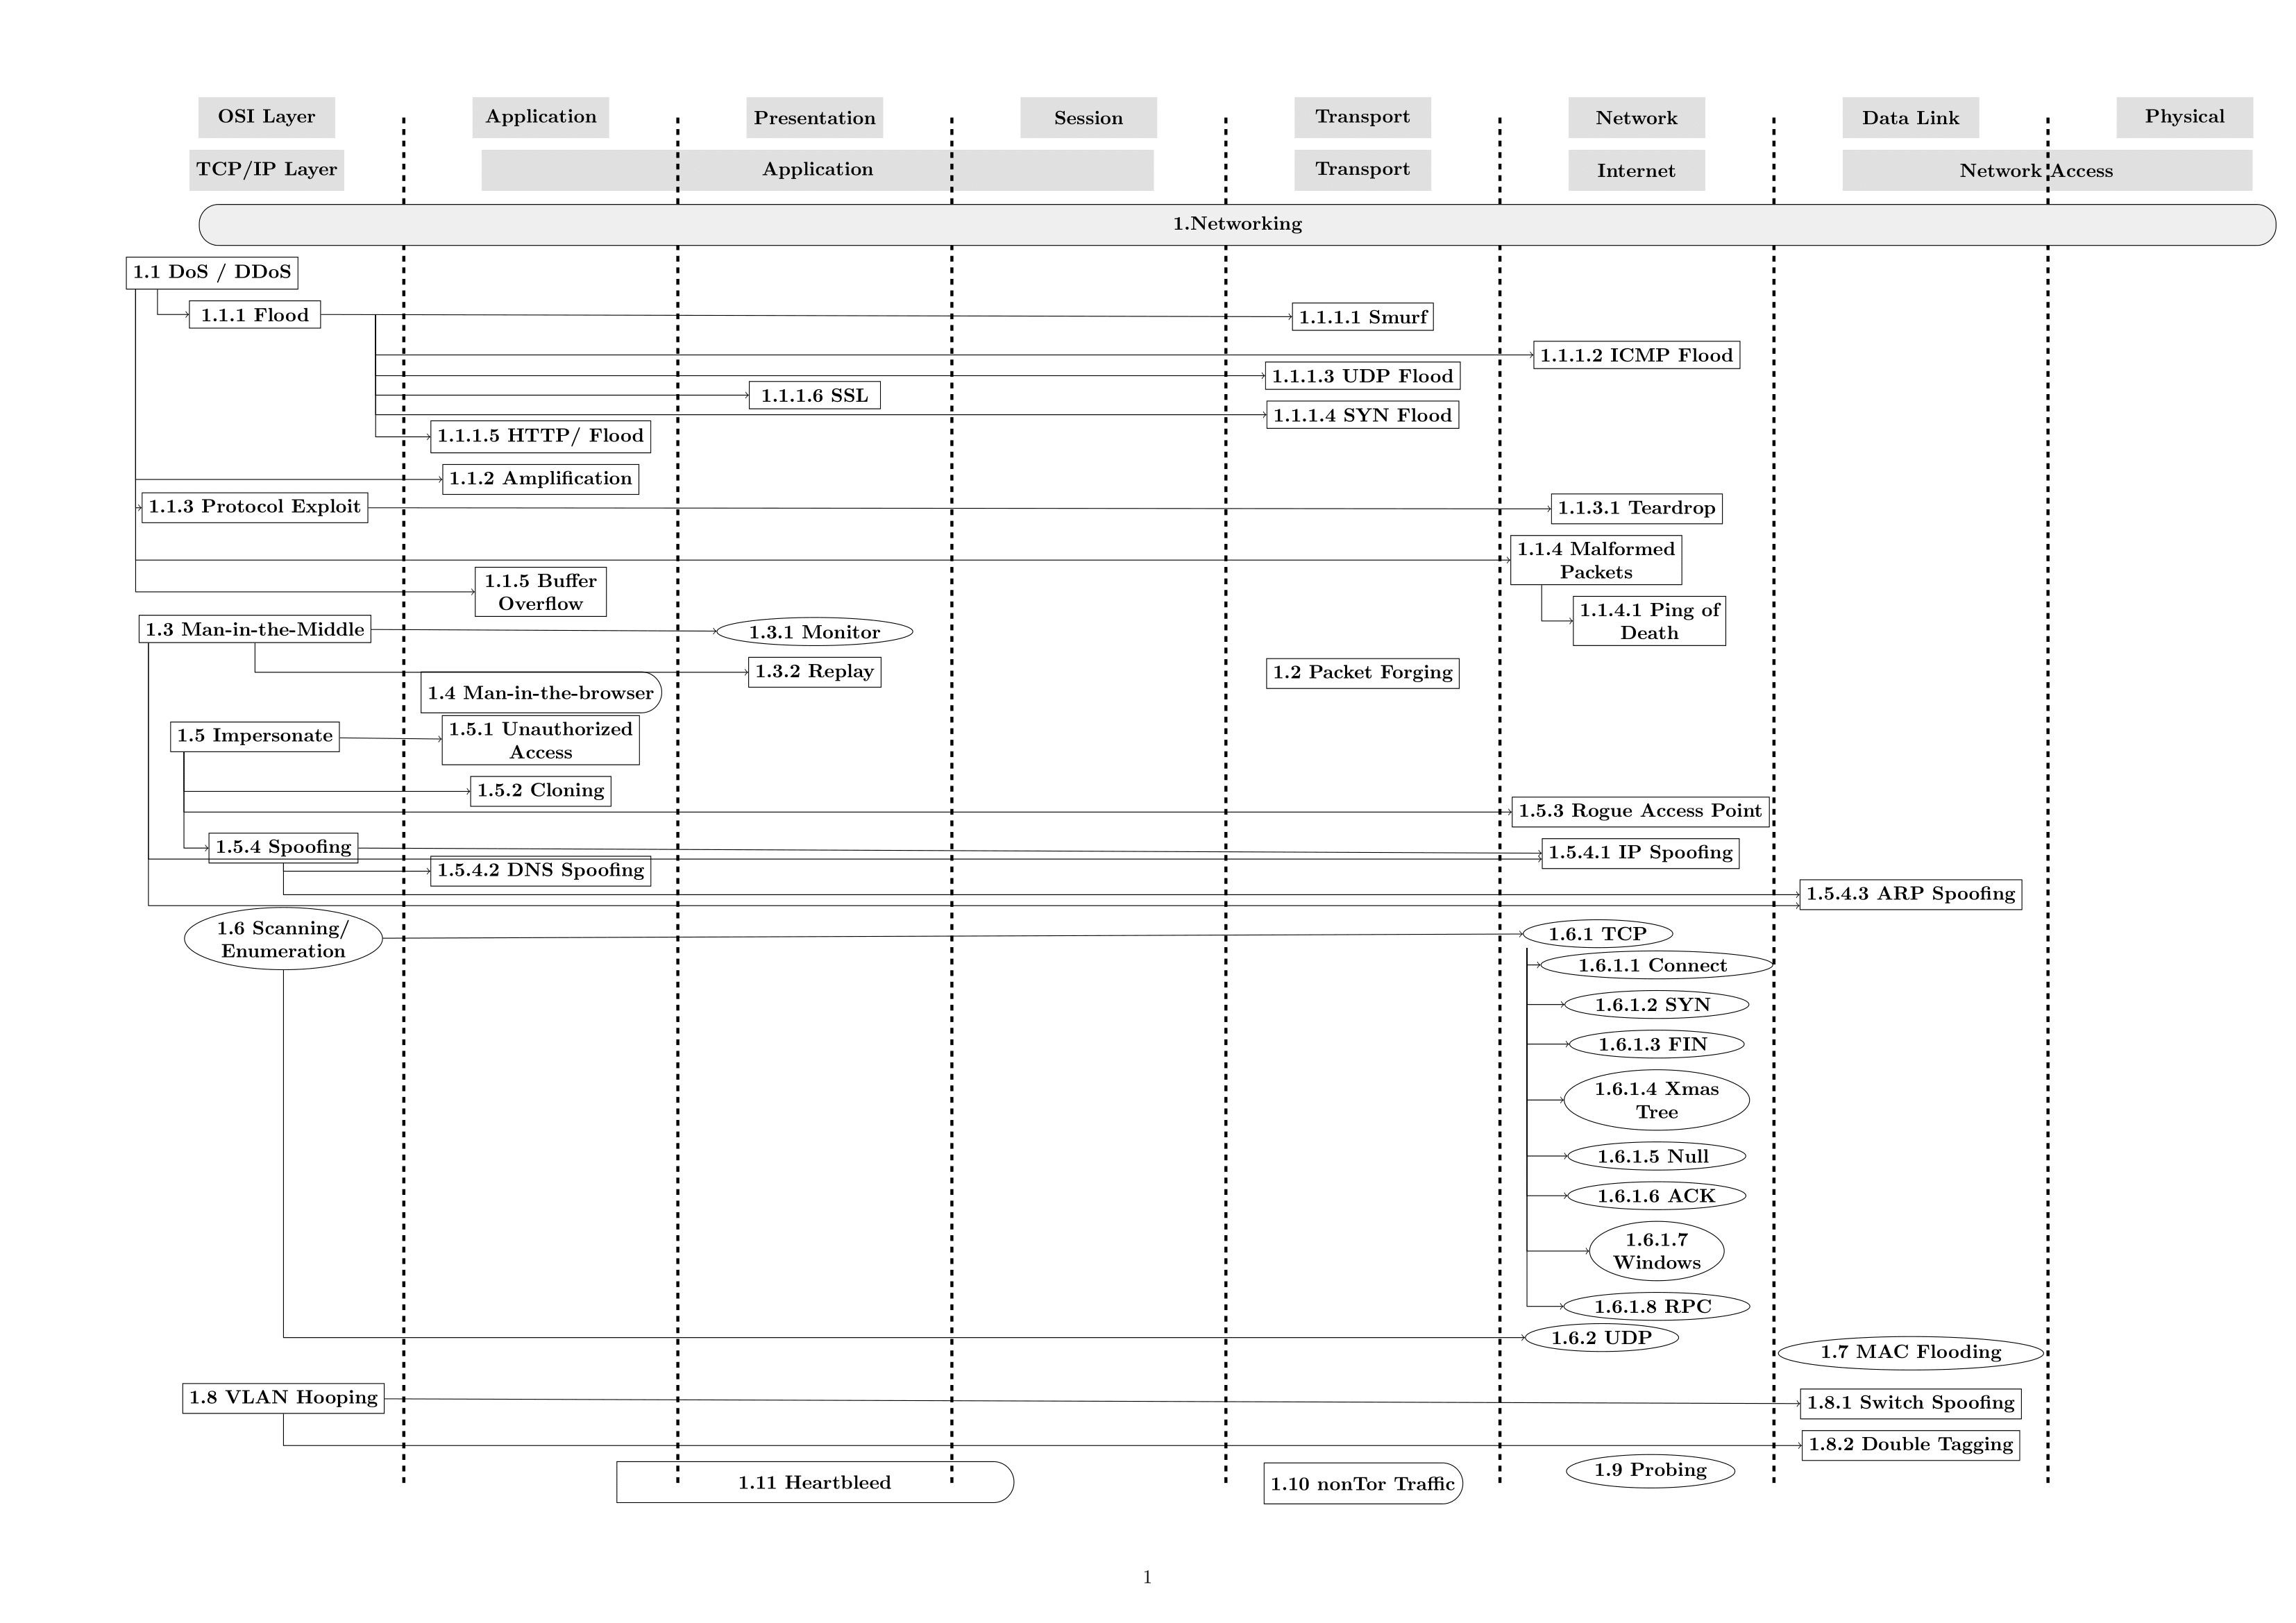
Security Tool to detect arp poisoning attacks