
OSTE-Web-Log-Analyzer
 ostesayed/oste-web-log-analyzer
OSTE WLA automate the process of analyzing web server logs with the Python Web Log Analyzer.
anomaly-detectionintrusion-detectionlog-analysis+2
43
ostesayed/oste-web-log-analyzerOSTE WLA automate the process of analyzing web server logs with the Python Web Log Analyzer.
 elastic/detection-rules
Develop, validate, and publish SIEM detection rules for Elastic Security, with Python CLI tooling, KQL parsing, Kibana integration, and packaged…
 nfstream/nfstream
NFStream: a Flexible Network Data Analysis Framework.
 sigmahq/pysigma
Python library to parse and convert Sigma rules into queries (and whatever else you could imagine)
 sonitbahl/sshintel
Self-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.
 tinashelorenzi/cve-2025-55182
Proof-of-concept exploit for CVE-2025-55182, a critical unauthenticated RCE in React Server Components. Includes automated Python exploit, technical…
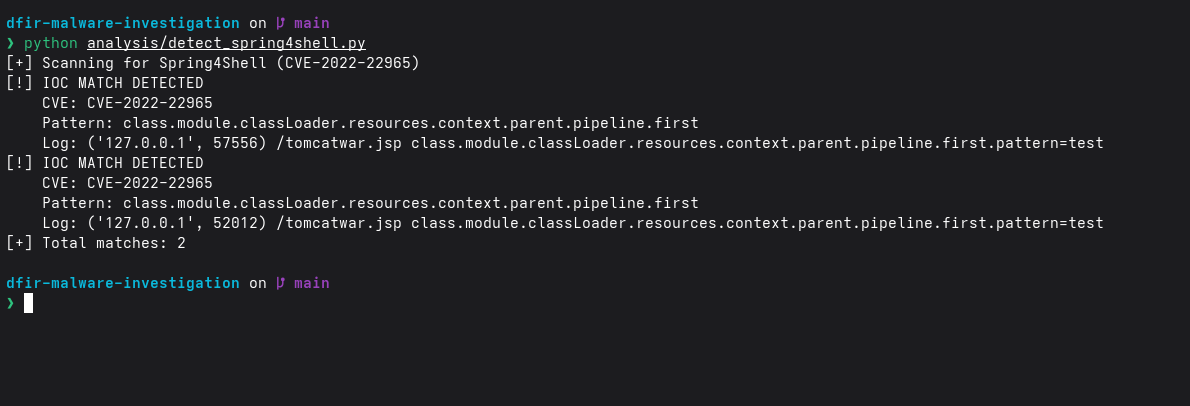 suyash-r-k/dfir-malware-investigation
Spring4Shell (CVE-2022-22965) DFIR lab with exploit simulation, Python WAF, IOC-based detection, and PCAP analysis.
 hackura/xz-cve-2024-3094
Python demo simulating CVE-2024-3094: a supply chain backdoor in XZ Utils with a trigger-based stealth activation.
 quynhold/detect-cve-2017-0144-attack
Chương trình theo dõi, giám sát lưu lượng mạng được viết bằng Python, nó sẽ đưa ra cảnh báo khi phát hiện tấn công CVE-2017-0144
 fail2ban/fail2ban
Daemon to ban hosts that cause multiple authentication errors
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
 certtools/intelmq
IntelMQ is a solution for IT security teams for collecting and processing security feeds using a message queuing protocol.
 dinotools/dionaea
Low-interaction honeypot that emulates vulnerable network services to capture malware, shellcode, and exploit attempts, with IPv6 and TLS support.
 stamusnetworks/scirius
Web interface for Suricata ruleset management, threat hunting, and rule tuning with multi-source feed aggregation, transformation, and activity…
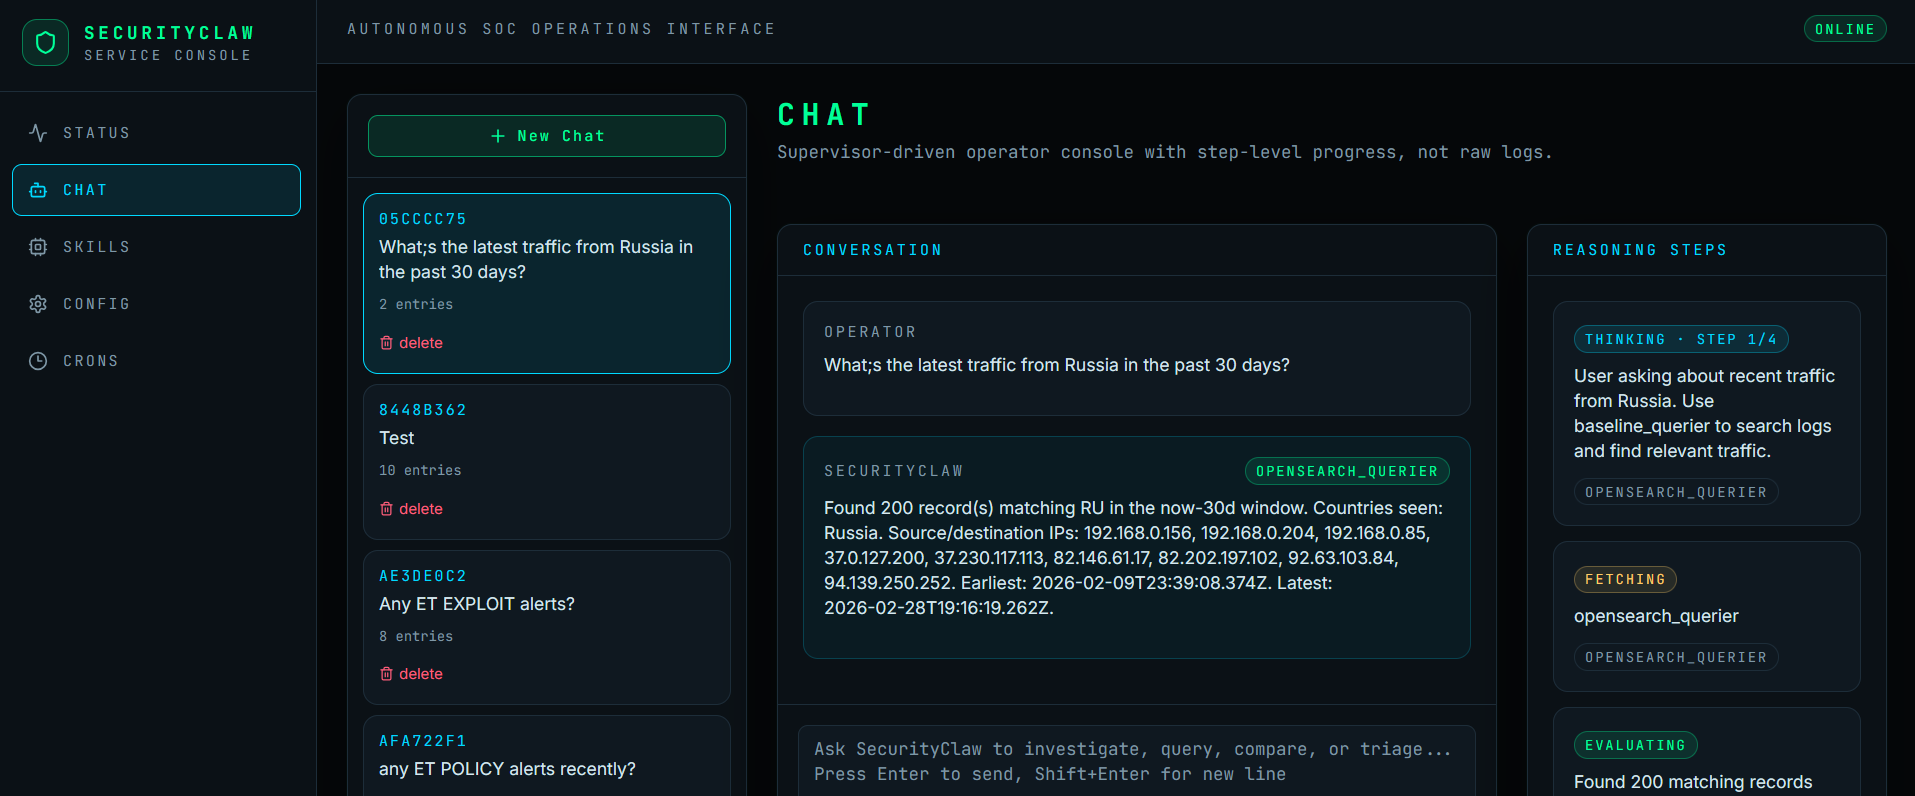 securityclaw/securityclaw
A modular, skill-based autonomous Security Operations Center (SOC) agent that monitors OpenSearch/Elasticsearch data, builds RAG-based behavioral…
 syworks/wireless-ids
Ability to detect suspicious activity such as (WEP/WPA/WPS) attack by sniffing the air for wireless packets.
 ait-aecid/logdata-anomaly-miner
This tool parses log data and allows to define analysis pipelines for anomaly detection. It was designed to run the analysis with limited resources…