

ModSecurity
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
anti-botapi-securitydefensive-tools+7
9.8k
owasp-modsecurity/modsecurityModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
 owasp/honeypot-project
Deploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…
 zecure/shadowd
The Shadow Daemon web application firewall server
 snorby/snorby
Ruby On Rails Application For Network Security Monitoring
 jsitech/jshielder
Hardening Script for Linux Servers/ Secure LAMP-LEMP Deployer/ CIS Benchmark
 dougburks/so-crates
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!
 mthbernardes/artlas
Apache Real Time Logs Analyzer System
 rbidou/pyrasp
Runtime Application Self Protection for Python web servers, serverless functions and MCP servers, detecting attacks, prompt injection and data leaks…
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring
 zoneminder/zoneminder
ZoneMinder is a free, open source Closed-circuit television software application developed for Linux which supports IP, USB and Analog cameras.
 baidu/openrasp
Runtime application self-protection engine that hooks into application servers to monitor and block malicious database queries, file operations, and…
 jithinkrishnanrs/stylesmuggler-ioc-toolkit
StyleSmuggler (CVE-2026-75650) IOC toolkit for Magento Open Source and Adobe Commerce. Detect compromised stores, Rust implants, PHP web shells,…
 garethmsheldon/cve-2026-22557-unifi-detection
Detection content for CVE-2026-22557 — UniFi Network Application unauthenticated path traversal (CVSS 10.0). Includes YARA, Sigma, KQL, Splunk SPL,…
 adarkst/honeypot_smart_infrastructure
This Repository Includes Kubernetes manifest files for configuration of Honeypot system and Falco IDS in K8s environment. There are also Demo…
 ma111e/melody
Melody is a transparent internet sensor built for threat intelligence. Supports custom tagging rules and vulnerable application simulation.
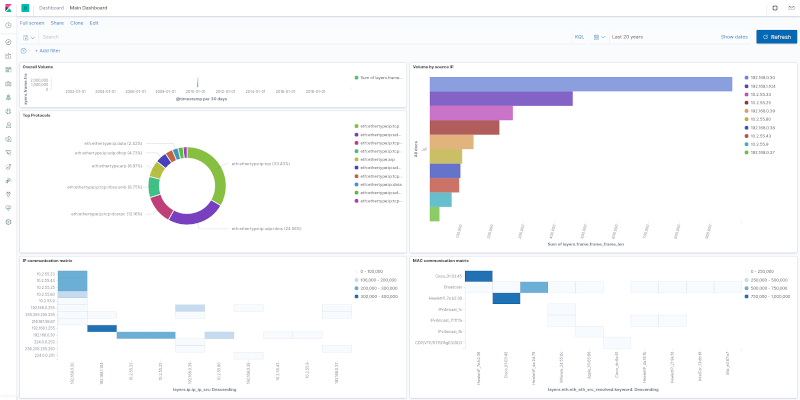 h21lab/tsharkvm
tshark + ELK analytics virtual machine
 corelight/raspi-corelight
Corelight@Home script
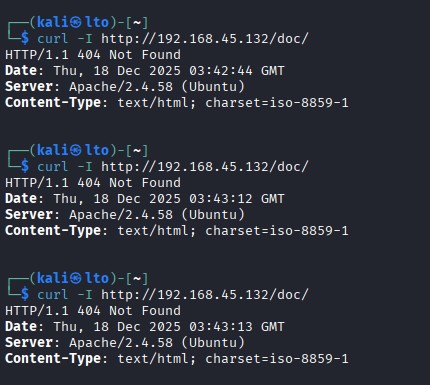 lto7777777/cve-1999-0678
CVE-1999-0678- /doc directory browsable