
tpotce
 telekom-security/tpotce
🍯 T-Pot - The All In One Multi Honeypot Platform 🐝
defensive-toolseducationinformation-gathering+7
telekom-security/tpotce🍯 T-Pot - The All In One Multi Honeypot Platform 🐝
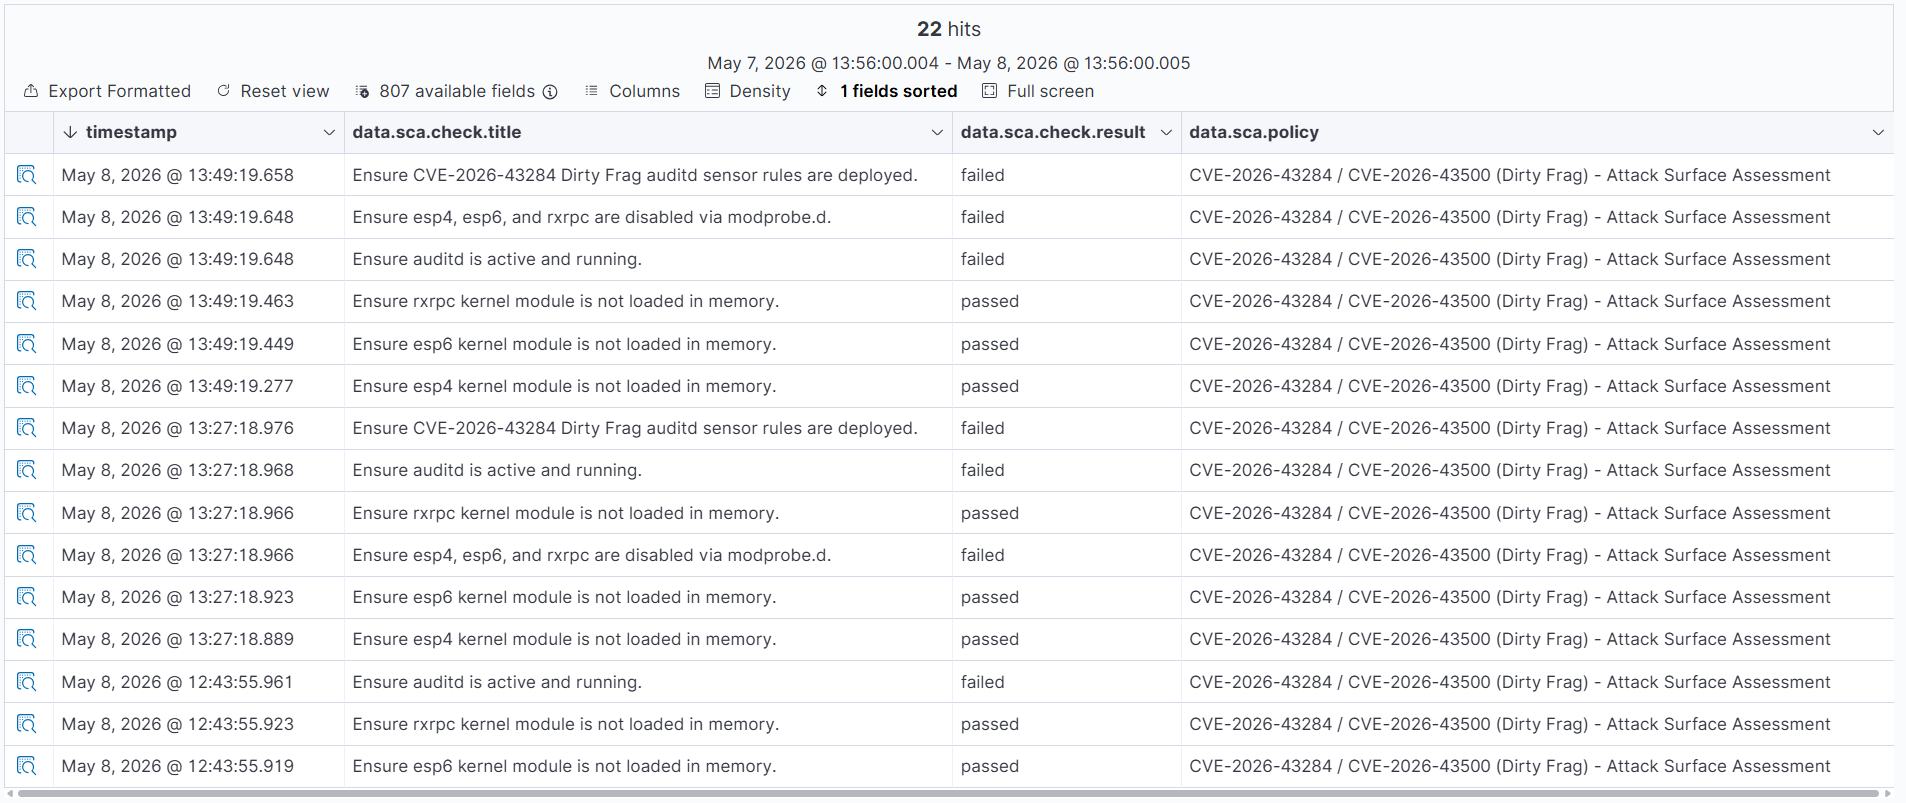 mym0us3r/dirty-frag-detection-with-wazuh-4.14.4
Wazuh 4.14.4 detection rules for CVE-2026-43284 / CVE-2026-43500 (Dirty Frag) - Linux Local Privilege Escalation via page cache write
 sumidcyber/zeroscout
🦅 ZeroScout: The Autonomous Local & Cloud Threat Hunter. Visualize attacks in a live War Room, identify APT groups via Genetic Analysis, and…
 corelight/redxor
Detection of Linux Malware C2 RedXOR - demonstration
 kuniyal08/dirty-frag-cve-2026-43284
A report on Dirty Frag, which is a Linux Local Privilege Escalation (LPE) vulnerability chain that allows an unprivileged user to gain root access
 yili-soc/vm-homelab-log4shell-assessment
Full-lifecycle vulnerability management on a live Log4Shell (CVE-2021-44228) target — scan, manual exploitation, network detection, and remediation…
 insomnisec/detections-cve-2026-31431
Detection rules, YARA signatures, auditd/Wazuh rules, and MISP event templates for CVE-2026-31431 Linux kernel LPE vulnerability (Copy Fail).…
 vishvacyber/detection-tool-kit-for-cve-2026-31431
Layered detection toolkit for CVE-2026-31431 (Copy Fail) Linux kernel LPE. Provides eBPF, auditd, Sigma rules, page-cache diff, and IOC guides for…
 g0thamrabb1t/cve-2026-43284-dirtyfrag-detection
Lab validation report and detection artifacts for CVE-2026-43284 (DirtyFrag) Linux LPE. Provides auditd telemetry, event correlation rules, and…
 rauljvc8/cve-2025-68616-detecting-and-patching-an-ssrf-in-weasyprint-with-wazuh
Hands-on vulnerability management case study: how Wazuh flagged a real SSRF (CVE-2025-68616) in WeasyPrint, and how I reproduced and patched it.
 g0thamrabb1t/cve-2026-46331-pedit-cow-detection
Defensive validation of CVE-2026-46331 / pedit COW with auditd, AppArmor, mitigation comparison and detection logic.
 daryllundy/cve-2025-32463
Detection framework for CVE-2025-32463 sudo privilege escalation vulnerability. Provides real-time monitoring, forensic analysis, and SIEM…
 nfstream/nfstream
NFStream: a Flexible Network Data Analysis Framework.
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
 ait-aecid/rootkit-detection-ebpf-time-trace
Detection of rootkit file hiding activities through analysis of shifts in kernel function execution times.
 umidguluzada/cyberdefense-lab
A complete Blue Team Cybersecurity Lab featuring pfSense, Suricata, and ELK Stack for network monitoring and threat detection.
 cisc0-gif/netcrackpi
RPi3+ Network Cracker Setup Tool
 harshiys/cve-2007-2447-exploitation-siem-detection-lab
Isolated AD/Linux attack lab: exploited CVE-2007-2447 via Metasploit, detected with Wazuh SIEM mapped to MITRE ATT&CK (T1190, T1059)