

santa
 northpolesec/santa
A binary and file access authorization system for macOS.
authentication-authorizationbinary-analysisdefensive-tools+2
792
northpolesec/santaA binary and file access authorization system for macOS.
 singe/yellow
A simple binary wrapper for DNS canarytokens.
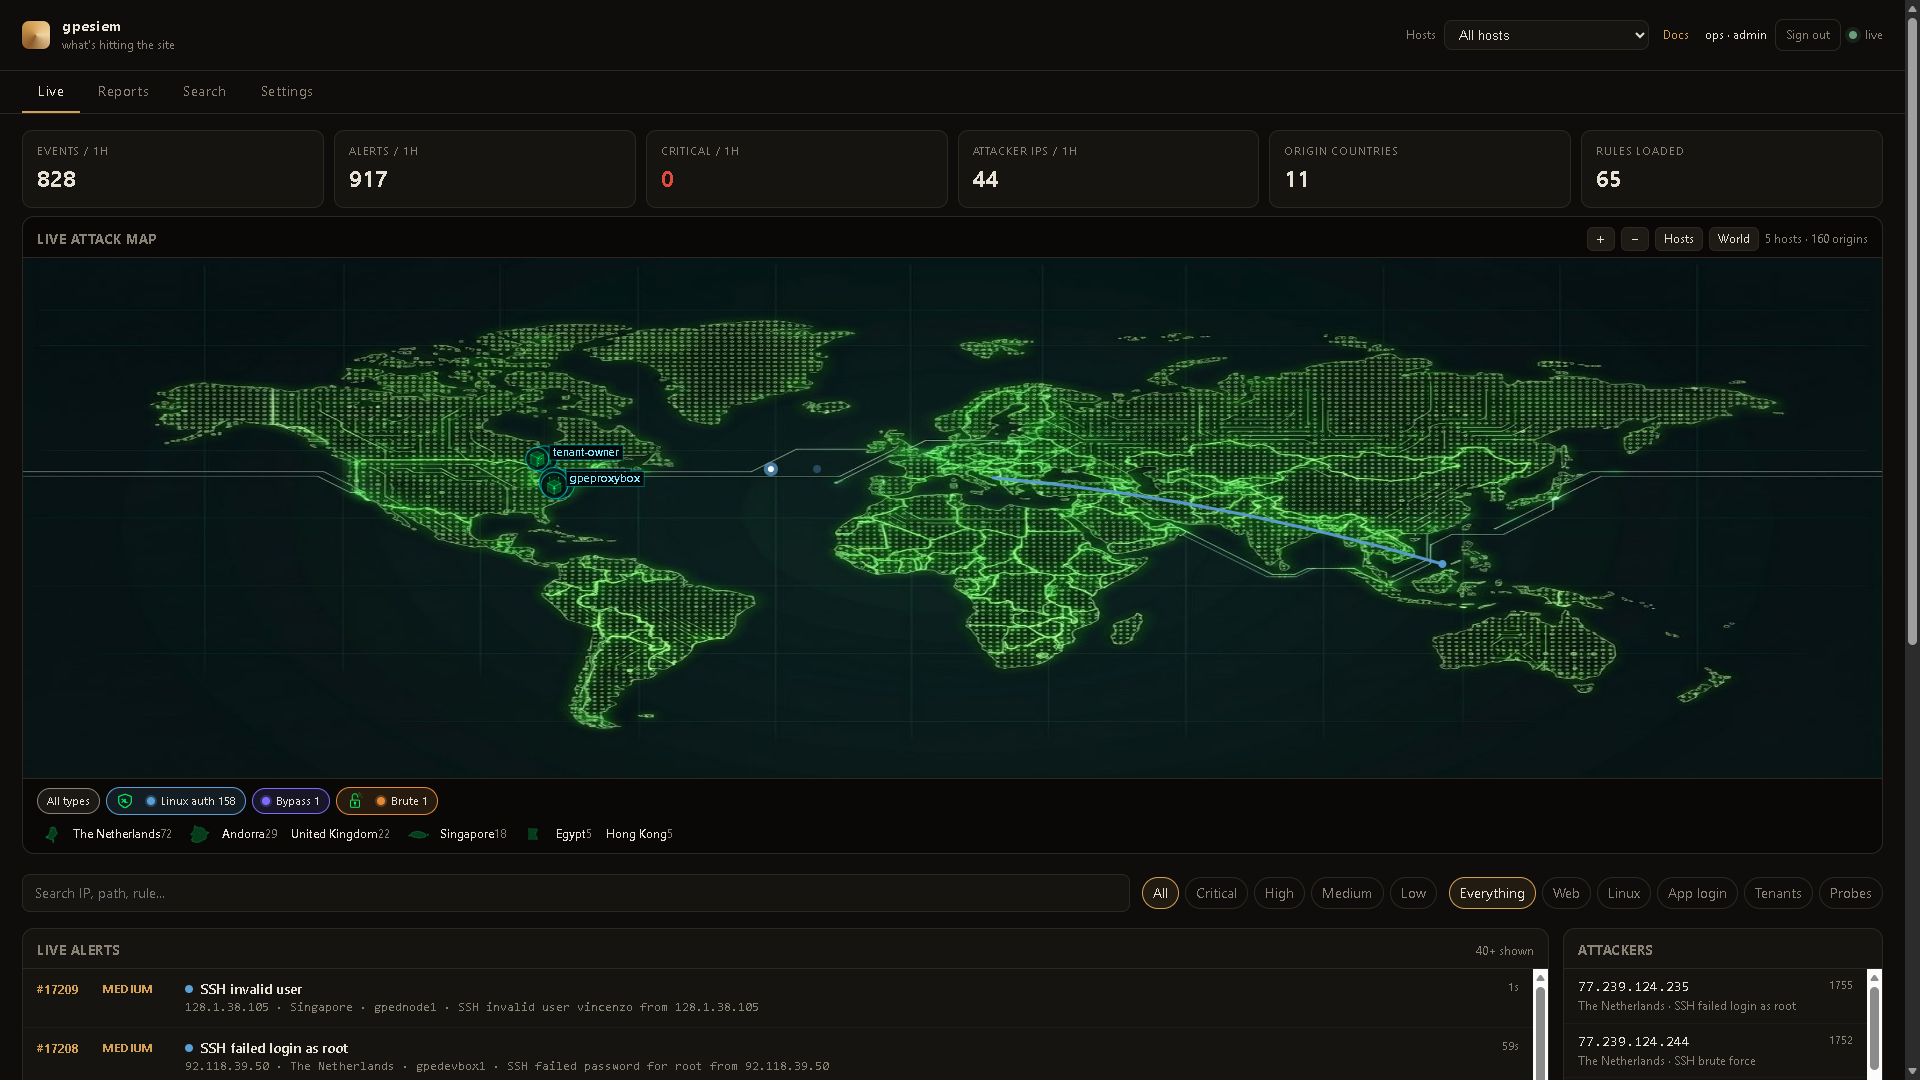 theretardedelon/gpewebdefender
Lightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.
 dougburks/so-crates
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!
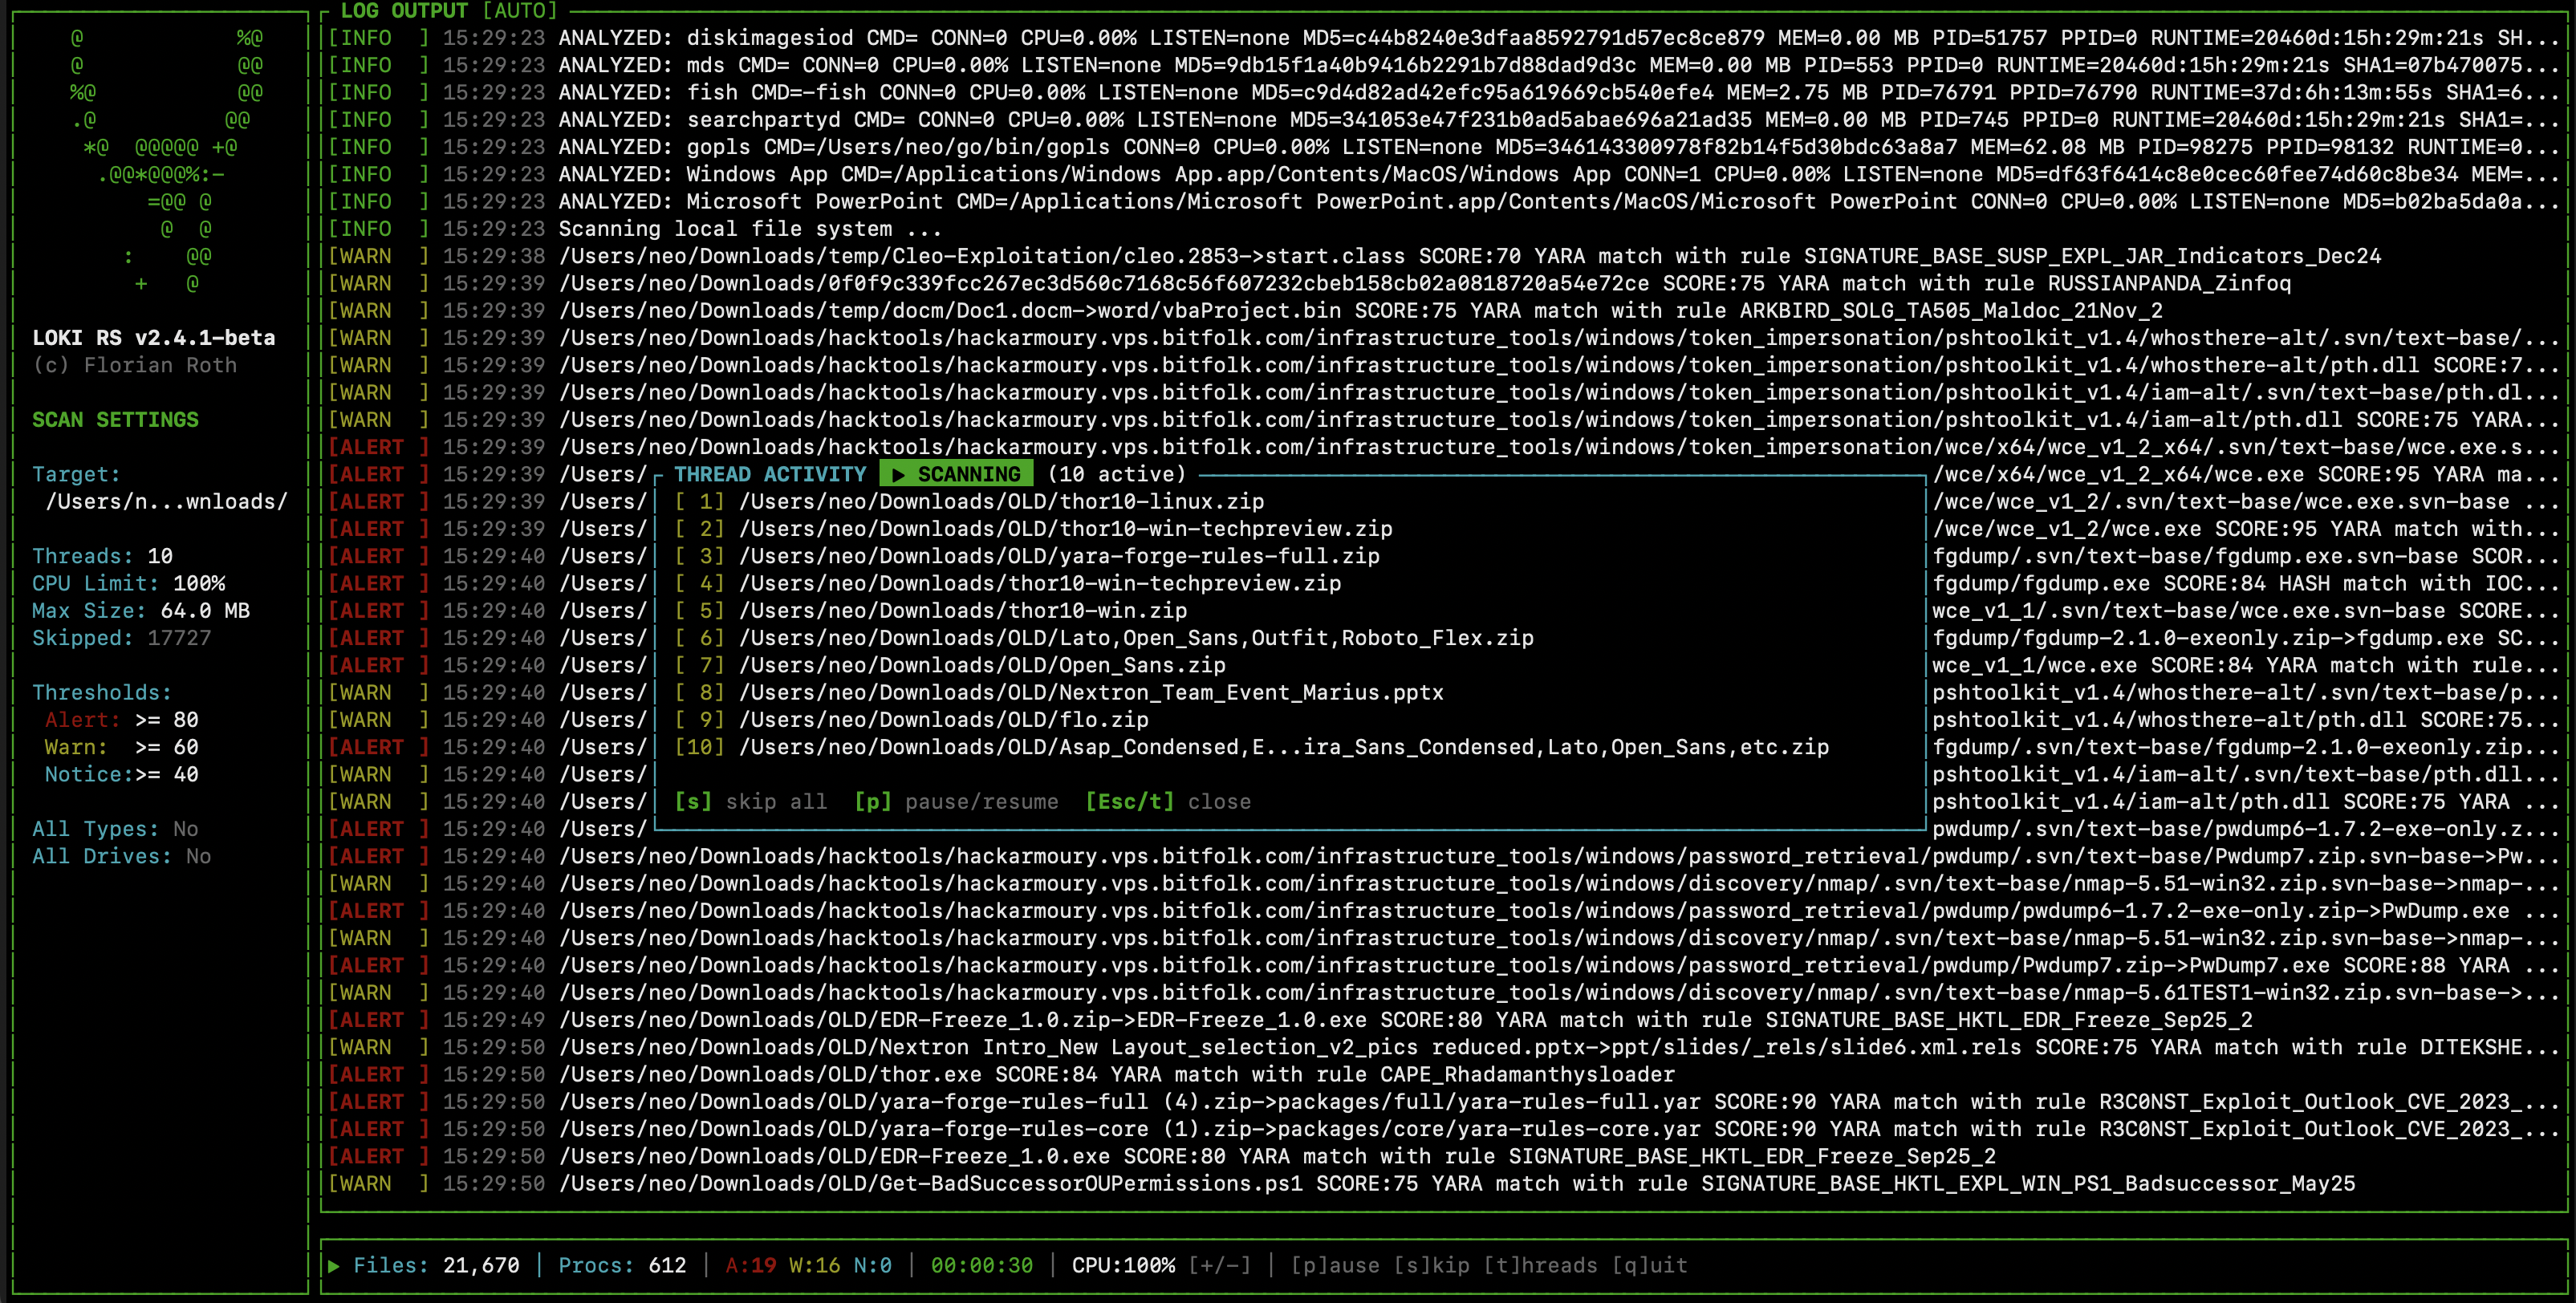 neo23x0/loki-rs
🐍 High-performance, multi-threaded YARA & IOC scanner
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
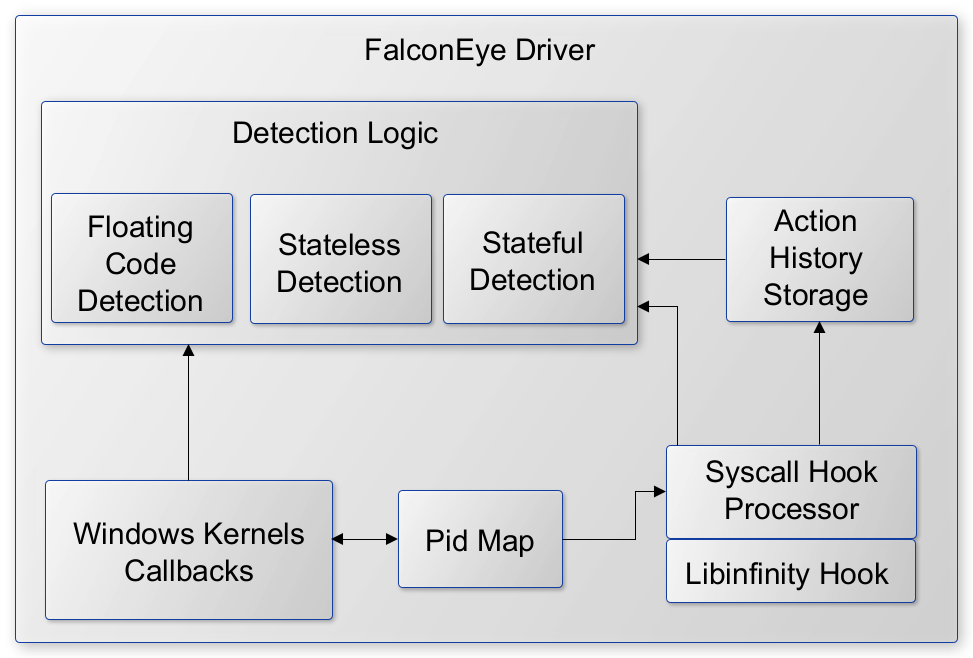 rajiv2790/falconeye
Kernel-mode Windows driver for real-time detection of process injection techniques, including shellcode, DLL, and reflective injection, with syscall…
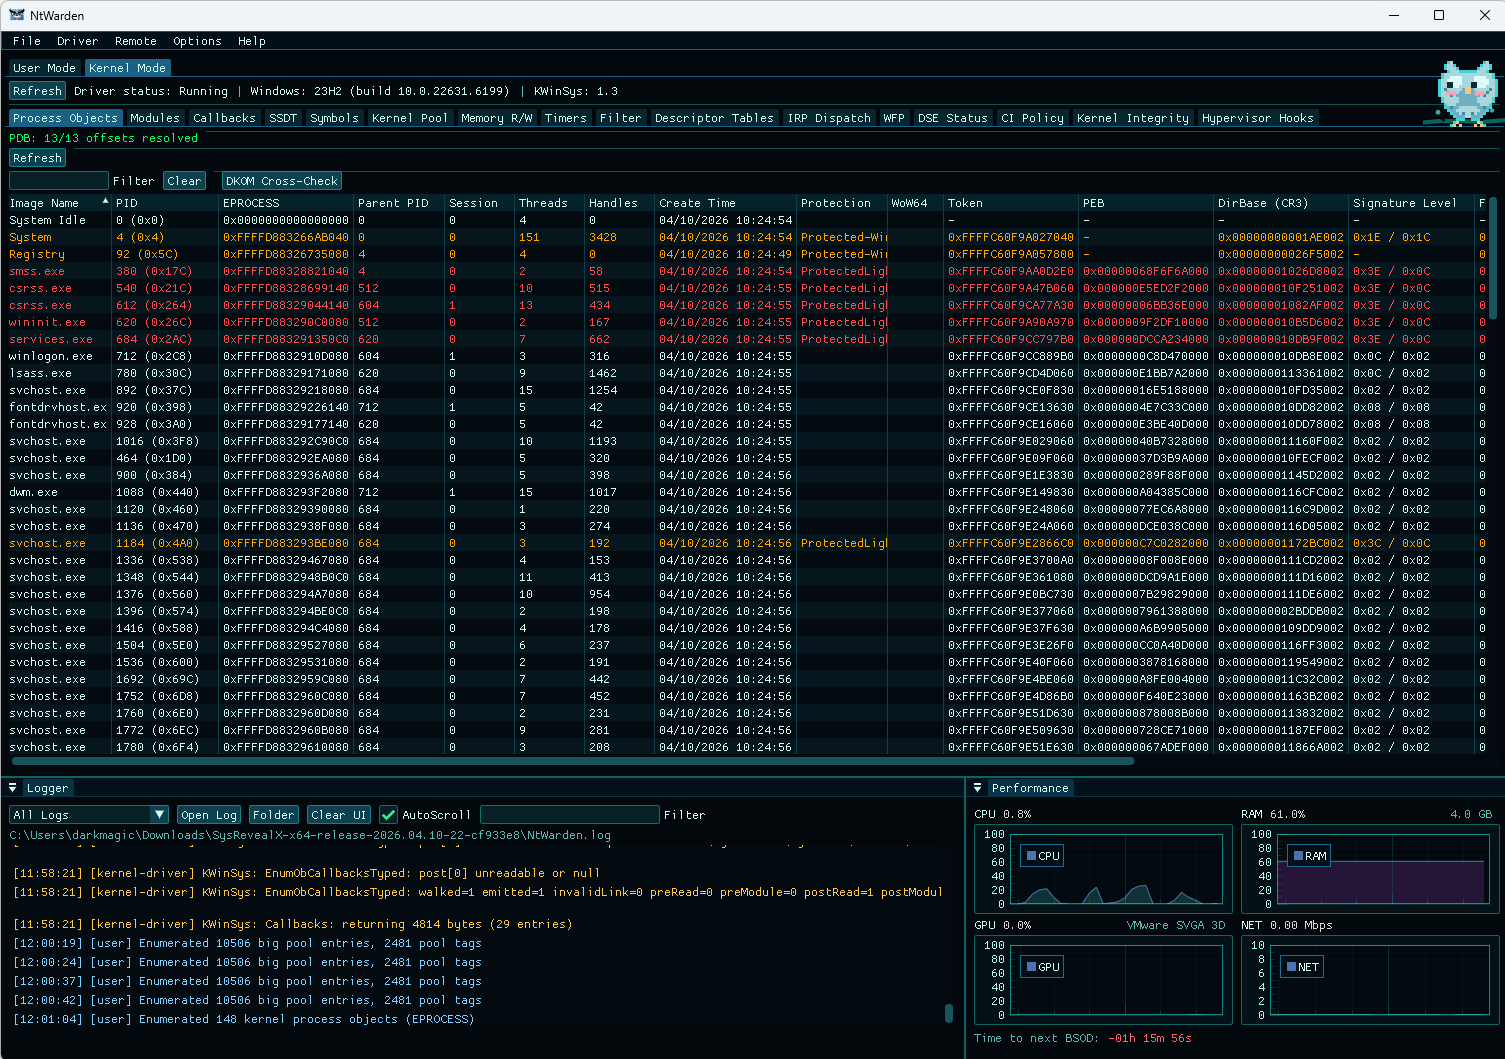 mrt4ntr4/ntwarden
Windows Analysis and Research Toolkit
 gui774ume/krie
Linux Kernel Runtime Integrity with eBPF
 0xkirisame/spica
eBPF-based Linux rootkit detector using multi-channel cross-view analysis (sched_switch, NMI, /proc) to detect DKOM, tracepoint tampering, and…

 corelight/zeek-elf
A Zeek ELF File Analyzer
 muhammednihalmp/google-chrome-zero-day
CVE-2025-6554
 h4ckm310n/cve-2022-0847-ebpf
An eBPF program to detect attacks on CVE-2022-0847
 corelight/zeek-xor-exe-plugin
Zeek plugin to detect and decrypt XOR-encrypted EXEs
 ares-sys/uefi_bootkit_softlanding
First public analysis of SoftLanding UEFI bootkit: Ring -2 implant, CVE-2025-7029, 240+ Gigabyte boards, GPU AI evasion, dual C2. YARA + Sigma +…
 hackspeak/cve-2026-23479
Redis UAF RCE PoC collection for CVE-2026-23479: safe version checker, exploit module, GDB-assisted PoC, and Sigma detection rules for authorized…
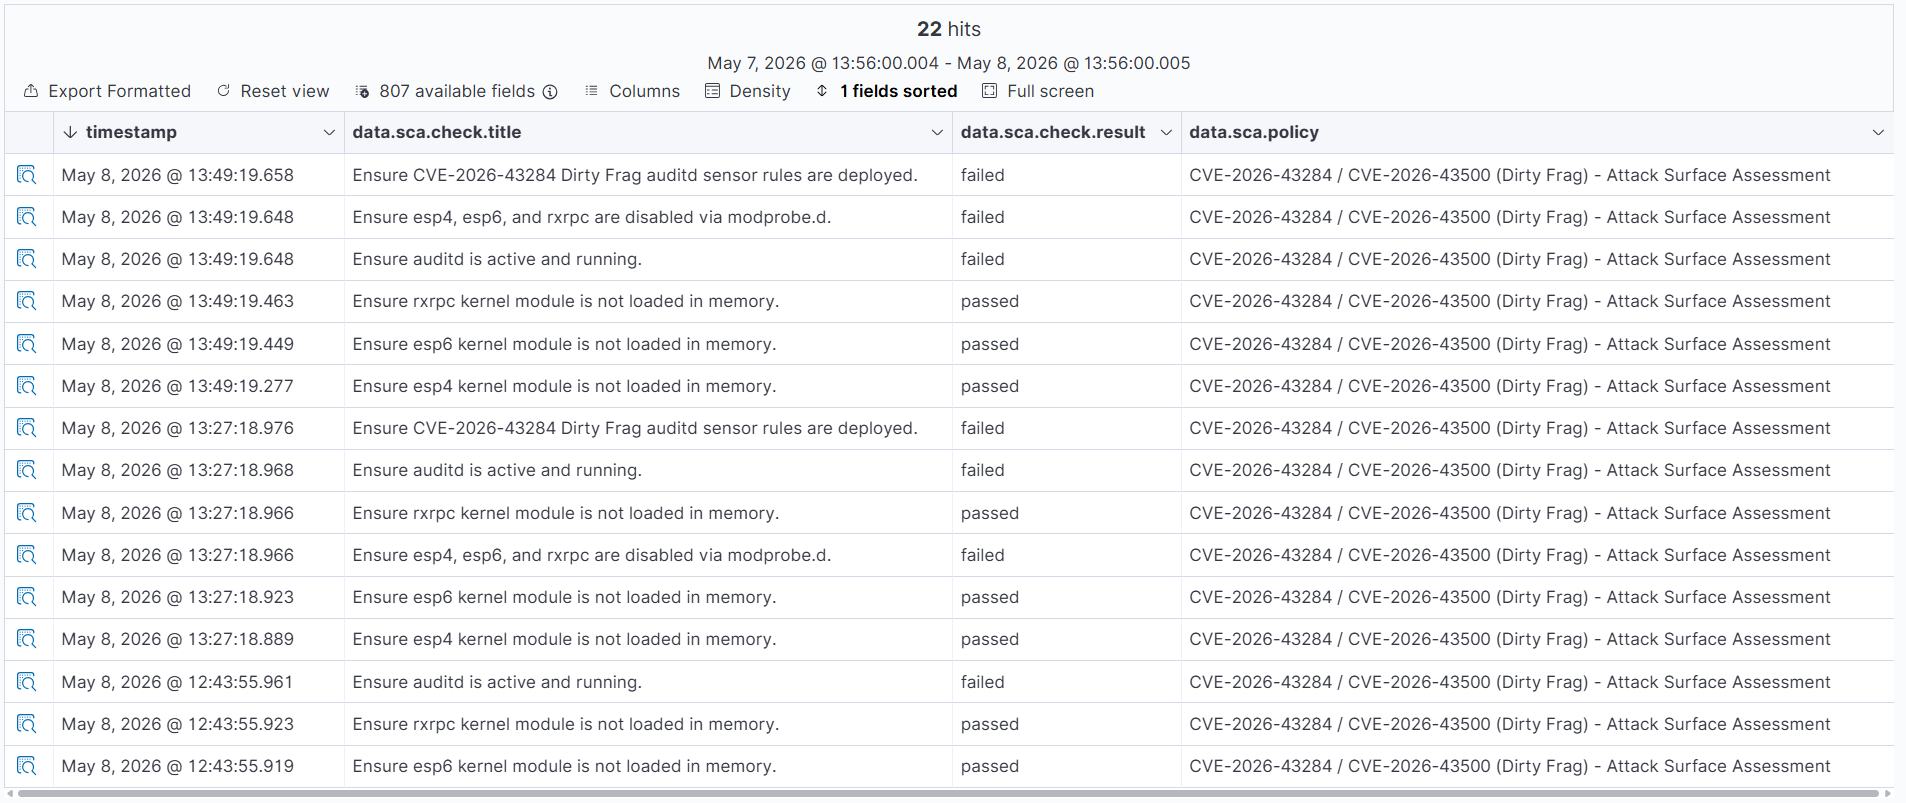 mym0us3r/dirty-frag-detection-with-wazuh-4.14.4
Wazuh 4.14.4 detection rules for CVE-2026-43284 / CVE-2026-43500 (Dirty Frag) - Linux Local Privilege Escalation via page cache write