

Elkeid
 bytedance/elkeid
Elkeid is an open source solution that can meet the security requirements of various workloads such as hosts, containers and K8s, and serverless. It…
cloud-securityconfiguration-auditingcontainer-security+6
2.7k
bytedance/elkeidElkeid is an open source solution that can meet the security requirements of various workloads such as hosts, containers and K8s, and serverless. It…
 bert-janp/open-source-threat-intel-feeds
This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…
 digitalruby/ipban
Automated IP ban service that detects failed login attempts from event logs and files, blocking attackers on Windows and Linux via firewall…
 cyb3rmik3/kql-threat-hunting-queries
A repository of KQL queries focused on threat hunting and threat detecting for Microsoft Sentinel & Microsoft XDR (Former Microsoft 365 Defender).
 perplexityai/numbat
Visibility into AI agent activity on endpoints, with on-device detection, optional pre-action blocking, and forensic reconstruction.
 gendigitalinc/ioc
Threat Intel IoCs + bits and pieces of dark matter. Published by Gen Threat Labs.
 aide/aide
File integrity monitoring tool that detects unauthorized changes to monitored files and directories using attribute checks, multiple hash algorithms,…
 rfxn/linux-malware-detect
Multi-engine Linux malware scanner with five detection stages (MD5, HEX pattern, YARA, ClamAV, statistical), real-time inotify monitoring,…
 certtools/intelmq
IntelMQ is a solution for IT security teams for collecting and processing security feeds using a message queuing protocol.
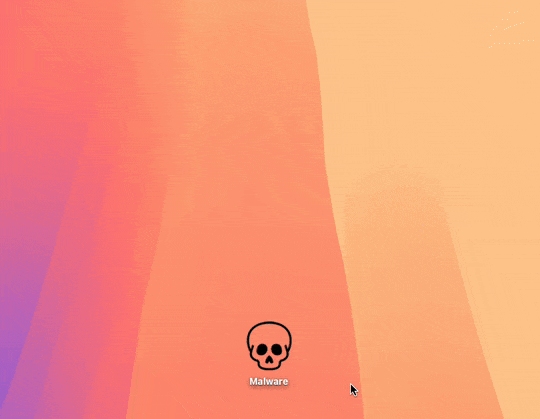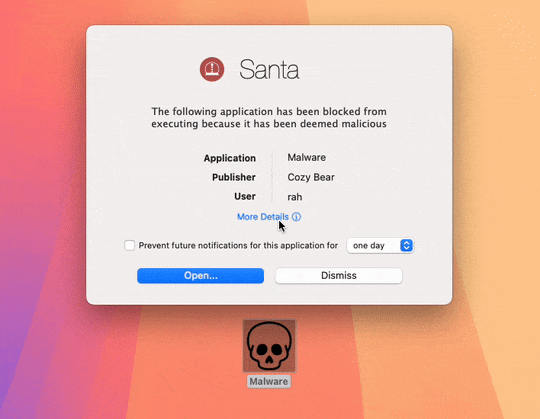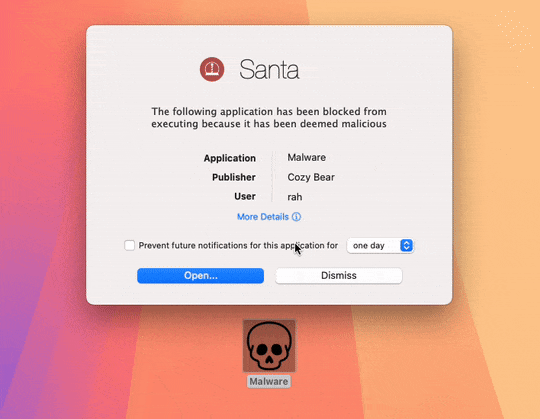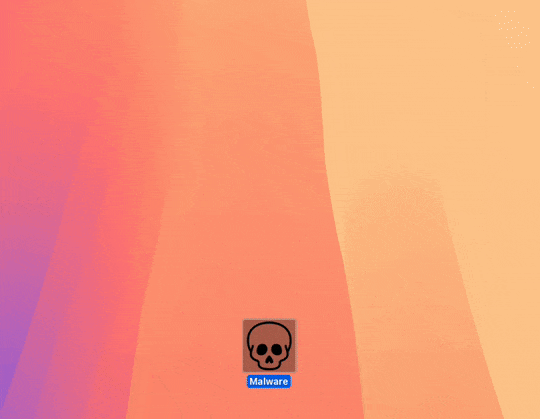 northpolesec/santa
A binary and file access authorization system for macOS.
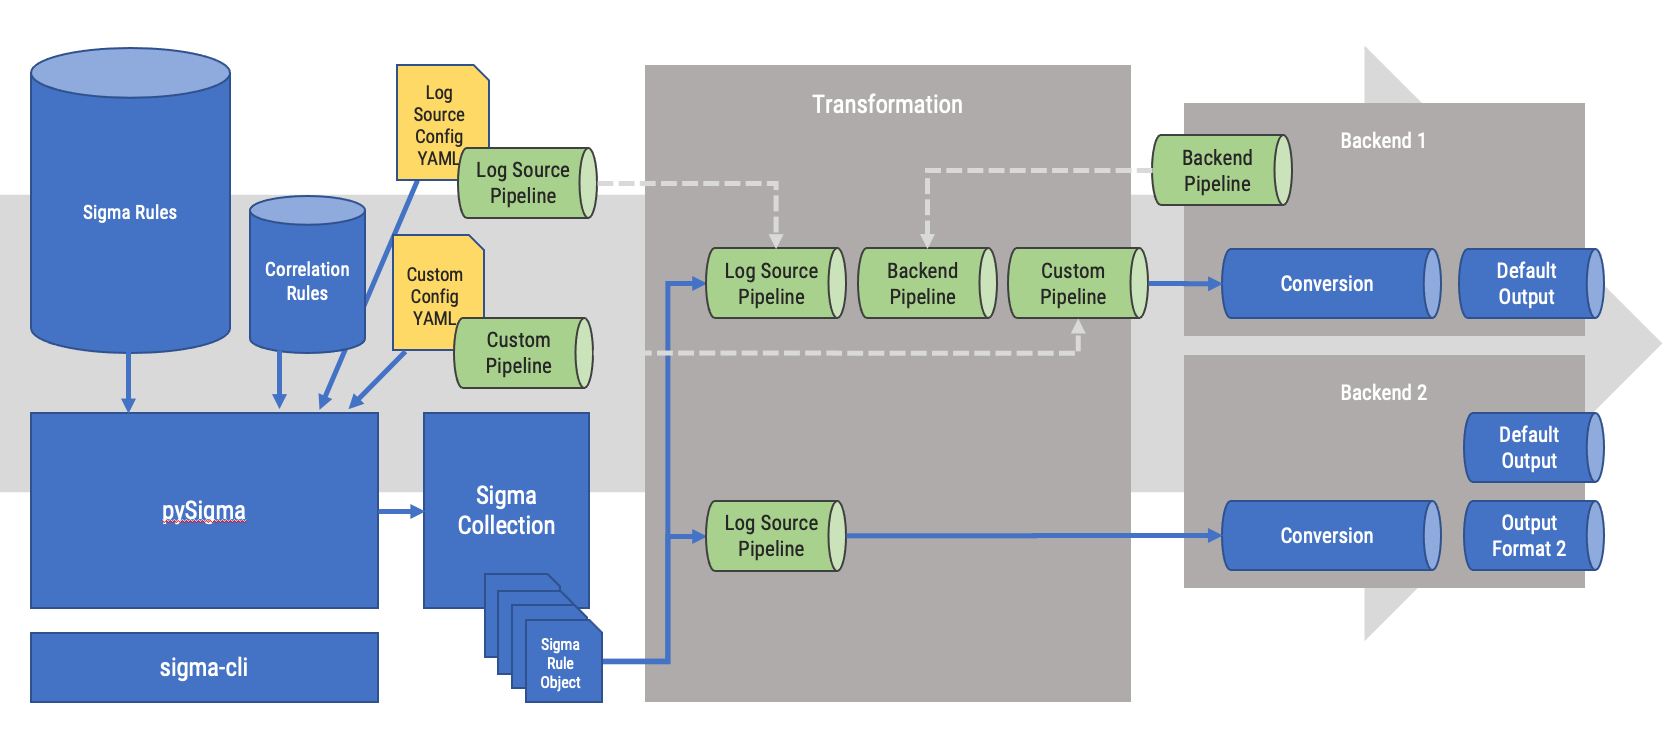 sigmahq/pysigma
Python library to parse and convert Sigma rules into queries (and whatever else you could imagine)
 ion-storm/sysmon-config
Advanced Sysmon ATT&CK configuration focusing on Detecting the Most Techniques per Data source in MITRE ATT&CK, Provide Visibility into Forensic…
 jaksi/sshesame
An easy to set up and use SSH honeypot, a fake SSH server that lets anyone in and logs their activity
 volexity/threat-intel
Signatures and IoCs from public Volexity blog posts.
 criticalpathsecurity/zeek-intelligence-feeds
Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…
 alphasoc/flightsim
A utility to safely generate malicious network traffic patterns and evaluate controls.
 idaholab/malcolm
Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
 dinotools/dionaea
Low-interaction honeypot that emulates vulnerable network services to capture malware, shellcode, and exploit attempts, with IPv6 and TLS support.