
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
583 results
snort3 preview

snort3

GitHubsnort3/snort3

Multi-threaded network intrusion detection and prevention system with rule-based detection, protocol-aware inspection, and pcap analysis for…
anti-botdefensive-toolsfuzzing+3
3.4k
5 months ago
packetfence preview

packetfence

GitHubinverse-inc/packetfence

PacketFence is a fully supported, trusted, Free and Open Source network access control (NAC) solution. Boasting an impressive feature set including a…
authentication-authorizationconfiguration-auditingdefensive-tools+6
1.7k2 days ago
DeepBlueCLI preview

DeepBlueCLI

GitHubsans-blue-team/deepbluecli

PowerShell-based threat hunting tool that analyzes Windows Event Logs to detect malicious activity including credential attacks, obfuscated commands,…

digital-forensicsincident-responseintrusion-detection+2
2.4k3 years ago
Loki preview

Loki

GitHubneo23x0/loki

IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
anomaly-detectiondigital-forensicsdisk-forensics+11
3.8k8 months ago
openrasp preview

openrasp

GitHubbaidu/openrasp

Runtime application self-protection engine that hooks into application servers to monitor and block malicious database queries, file operations, and…

anomaly-detectiondefensive-toolsdevsecops+2
3.0k11 months ago
Elkeid preview

Elkeid

GitHubbytedance/elkeid

Elkeid is an open source solution that can meet the security requirements of various workloads such as hosts, containers and K8s, and serverless. It…

cloud-securityconfiguration-auditingcontainer-security+6
2.7k4 months ago
nzyme preview

nzyme

GitHubnzymeorg/nzyme

WiFi, Bluetooth and Ethernet Threat Detection.
anomaly-detectionbluetooth-securitydefensive-tools+5
1.6k1 day ago
IPBan preview

IPBan

GitHubdigitalruby/ipban

Automated IP ban service that detects failed login attempts from event logs and files, blocking attackers on Windows and Linux via firewall…
defensive-toolsintrusion-detectionlog-analysis+1
2.2k2 months ago
stackrox preview

stackrox

GitHubstackrox/stackrox

The StackRox Kubernetes Security Platform performs a risk analysis of the container environment, delivers visibility and runtime alerts, and provides…
anomaly-detectioncloud-infrastructure-securitycloud-security+6
1.3k21h 44m ago
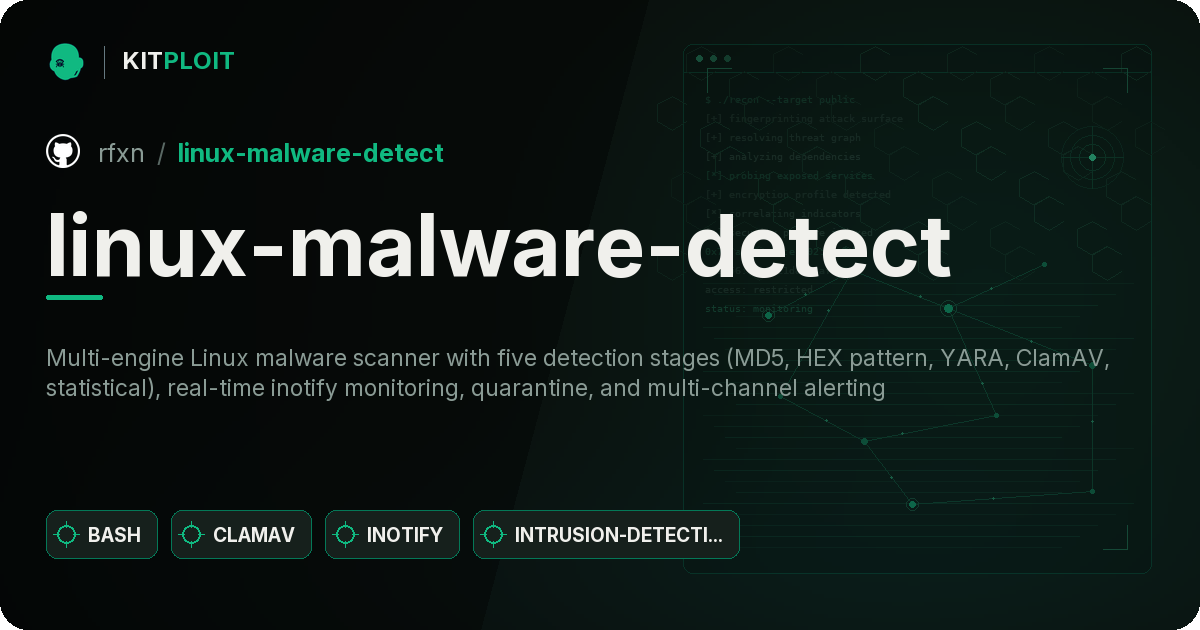
Open-Source-Threat-Intel-Feeds preview

Open-Source-Threat-Intel-Feeds

GitHubbert-janp/open-source-threat-intel-feeds

This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…
intrusion-detectionioc-managementnetwork-security+3
9468 days ago
linux-malware-detect preview

linux-malware-detect

GitHubrfxn/linux-malware-detect

Multi-engine Linux malware scanner with five detection stages (MD5, HEX pattern, YARA, ClamAV, statistical), real-time inotify monitoring,…
anomaly-detectiondefensive-toolsincident-response+3
1.5k3 months ago
intelmq preview

intelmq

GitHubcerttools/intelmq

IntelMQ is a solution for IT security teams for collecting and processing security feeds using a message queuing protocol.

incident-responseinformation-gatheringintrusion-detection+6
1.1k4 months ago
santa preview

santa

GitHubnorthpolesec/santa

A binary and file access authorization system for macOS.

authentication-authorizationbinary-analysisdefensive-tools+2
7922 days ago
pySigma preview

pySigma

GitHubsigmahq/pysigma

Python library to parse and convert Sigma rules into queries (and whatever else you could imagine)

defensive-toolsintrusion-detectionlog-analysis+2
59717h 27m ago
sysmon-config preview

sysmon-config

GitHubion-storm/sysmon-config

Advanced Sysmon ATT&CK configuration focusing on Detecting the Most Techniques per Data source in MITRE ATT&CK, Provide Visibility into Forensic…
anomaly-detectiondefensive-toolsdigital-forensics+5
8292 years ago
KQL-threat-hunting-queries preview

KQL-threat-hunting-queries

GitHubcyb3rmik3/kql-threat-hunting-queries

A repository of KQL queries focused on threat hunting and threat detecting for Microsoft Sentinel & Microsoft XDR (Former Microsoft 365 Defender).

ctfcurated-resourceseducation+4
7983 months ago
flightsim preview

flightsim

GitHubalphasoc/flightsim

A utility to safely generate malicious network traffic patterns and evaluate controls.

command-and-controldefensive-toolsdns-analysis+4
1.4k2 years ago
Zeek-Intelligence-Feeds preview

Zeek-Intelligence-Feeds

GitHubcriticalpathsecurity/zeek-intelligence-feeds

Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…

command-and-controlintrusion-detectionnetwork-security+3
40118h 42m ago
Previous1234…33Next