
 pedramamini/threatingestor
Automated threat intelligence aggregation tool that extracts and normalizes indicators from multiple sources (OSINT feeds, malware reports) into a…
 owasp/honeypot-project
Deploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…
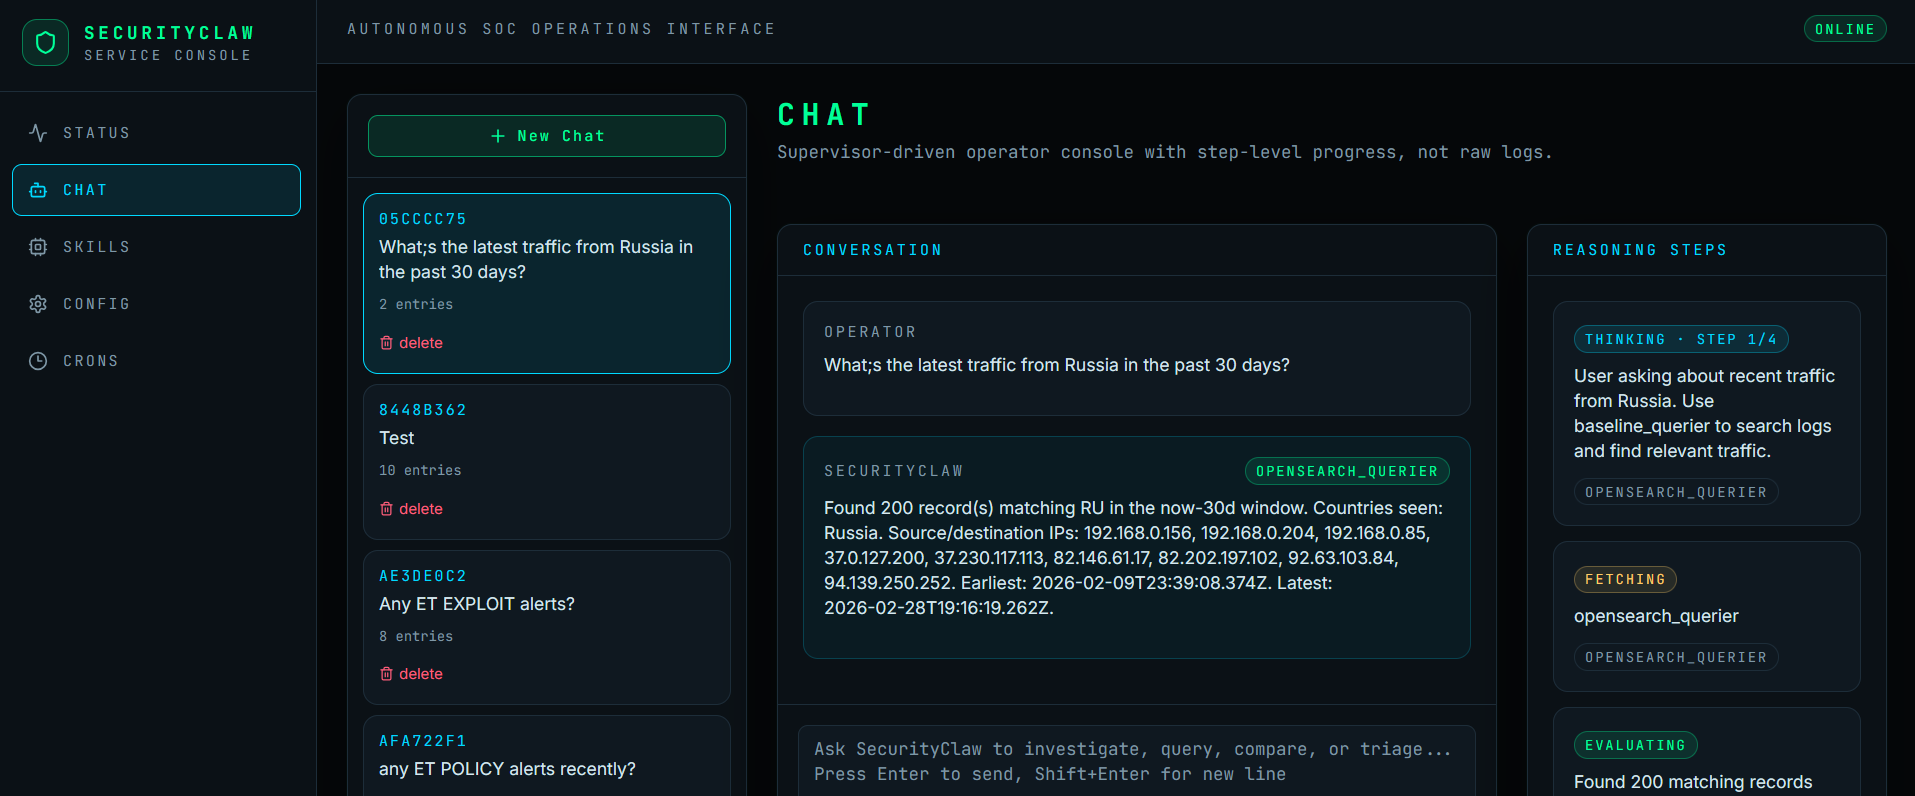 securityclaw/securityclaw
A modular, skill-based autonomous Security Operations Center (SOC) agent that monitors OpenSearch/Elasticsearch data, builds RAG-based behavioral…
 gbrindisi/wordpot
A Wordpress Honeypot
 gojue/ehids-agent
A Linux Host-based Intrusion Detection System based on eBPF.
 stamparm/tsusen
Network traffic sensor
 hpfeeds/hpfeeds
Honeynet Project generic authenticated datafeed protocol
 mushorg/buttinsky
Botnet monitoring is a crucial part in threat analysis and often neglected due to the lack of proper open source tools. Our tool will provide an open…
 cred-club/artif
An advanced real time threat intelligence framework to identify threats and malicious web traffic on the basis of IP reputation and historical data.
 a2awais/threat-hunting
Curated collection of threat hunting and detection queries for CrowdStrike Falcon (CQL) and Microsoft Defender XDR (KQL), mapped to MITRE ATT&CK…
 puniaze/portdog
Network anomaly detector that monitors raw packets to identify port scanning activity in real time, with flexible sniffing duration controls and live…
 randomuserid/tylium
Primary data pipelines for intrusion detection, security analytics and threat hunting
 kevin-robertson/conveigh
Conveigh is a Windows PowerShell LLMNR/NBNS spoofer detection tool
 malwaretech/log4jtools
Tools for investigating Log4j CVE-2021-44228
 nicholasadamou/minipwner
A script to configure a TP-Link MR3040 running OpenWRT into a simple, yet powerful penetration-testing "dropbox".
 thelightscope/thelightscope
TheLightScope
 rushyo/vindicatetool
LLMNR/NBNS/mDNS Spoofing Detection Toolkit