
go-zeek-broker-ws
 corelight/go-zeek-broker-ws
A Go library for using zeek broker's websocket API
authentication-authorizationintrusion-detectionnetwork-security+1
5
corelight/go-zeek-broker-wsA Go library for using zeek broker's websocket API
 corelight/icanntld
Zeek script using the official ICANN Top-Level Domain (TLD) list with the Input Framework to extract the relevant information from a DNS query and…
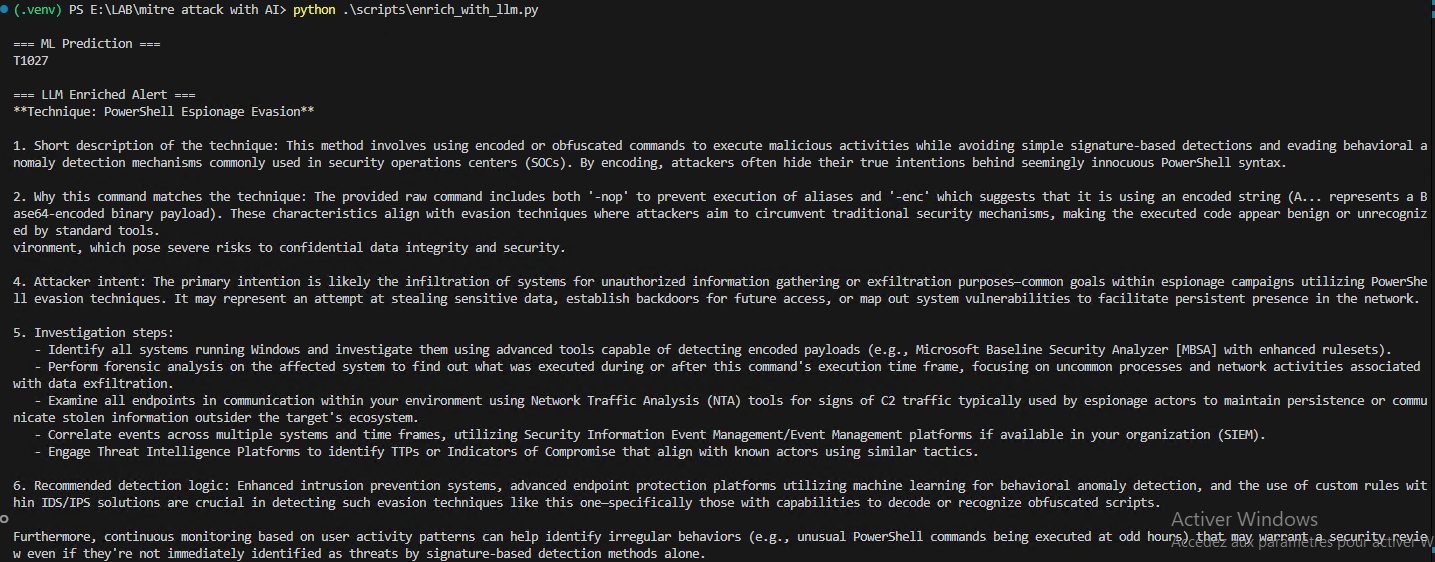 mouna23/ai-driven-mitre-attack
This repository demonstrates a machine learning pipeline for detecting MITRE ATT&CK techniques from logs and enriching the output using a local LLM.
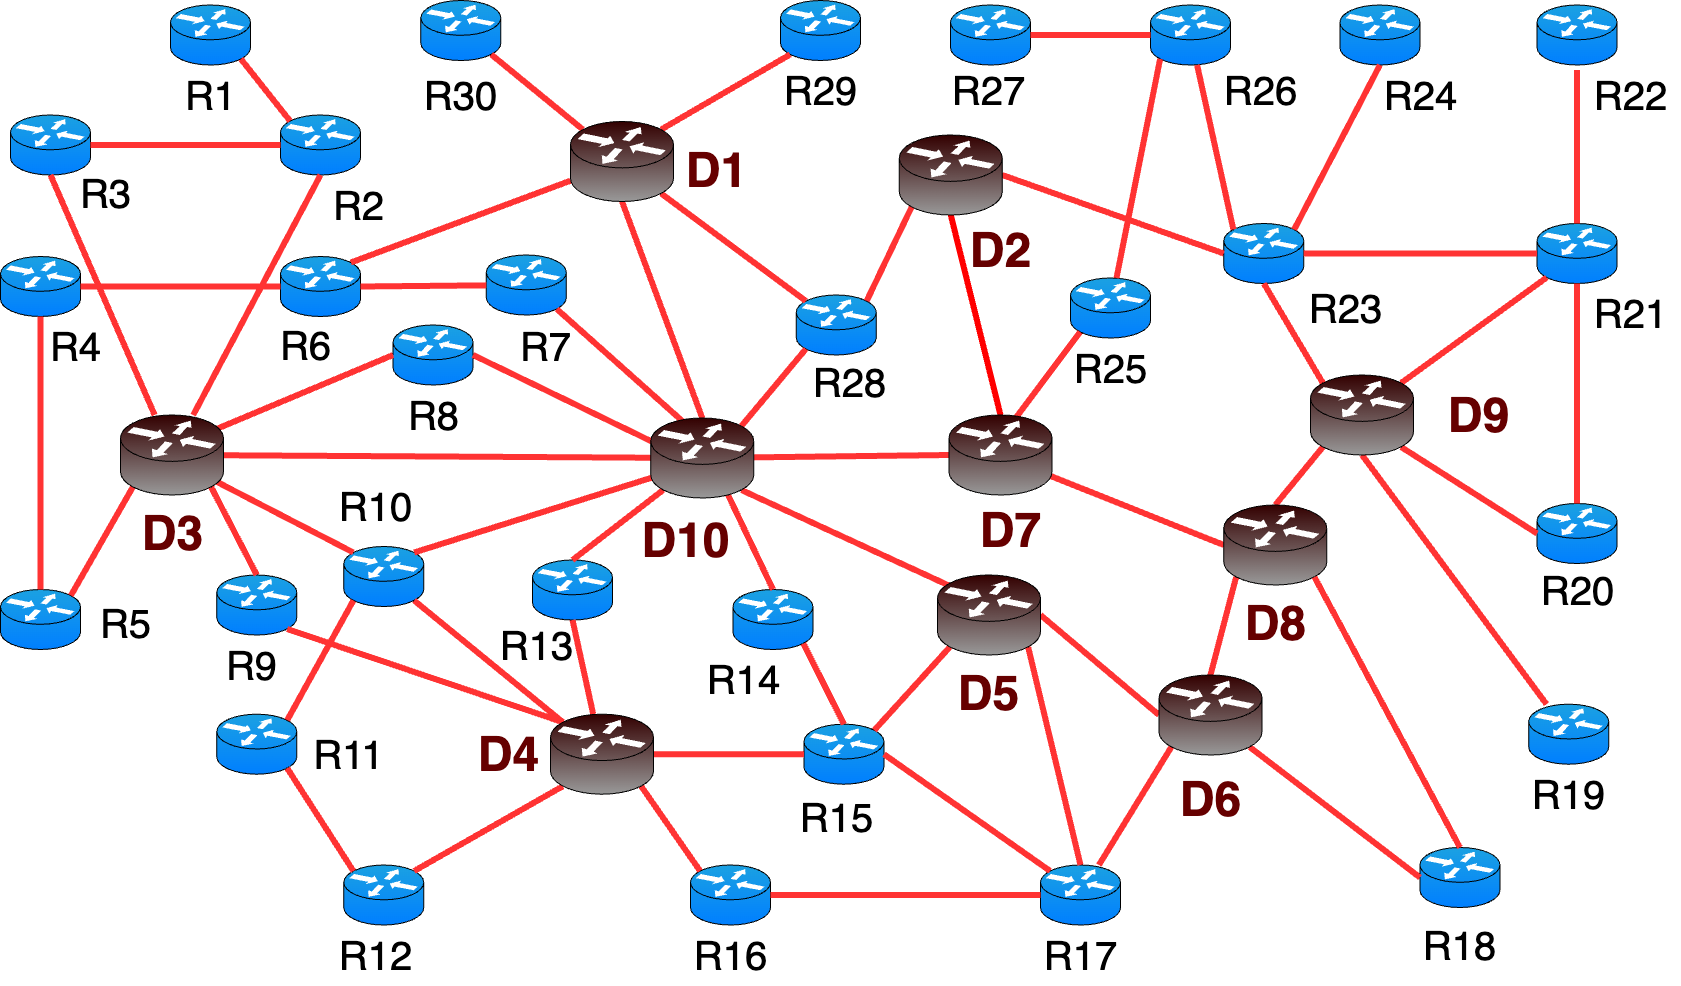 nsol-nmsu/fml-network
FLNET2023 is a dataset designed for intrusion detection in Federated Learning scenarios. It's built using the CORE emulator, simulating a realistic…
 devinblack001/ddos-reduction-system
Adaptive two-stage Layer 4 DDoS mitigation gateway using behavioral traffic analysis, Random Forest classification, and kernel-level ipset/iptables…
 nawaralseelawi/pvbrf-id
Simulation code and results for a private, verifiable, Byzantine-robust federated intrusion detection protocol using secret sharing, Merkle audits…
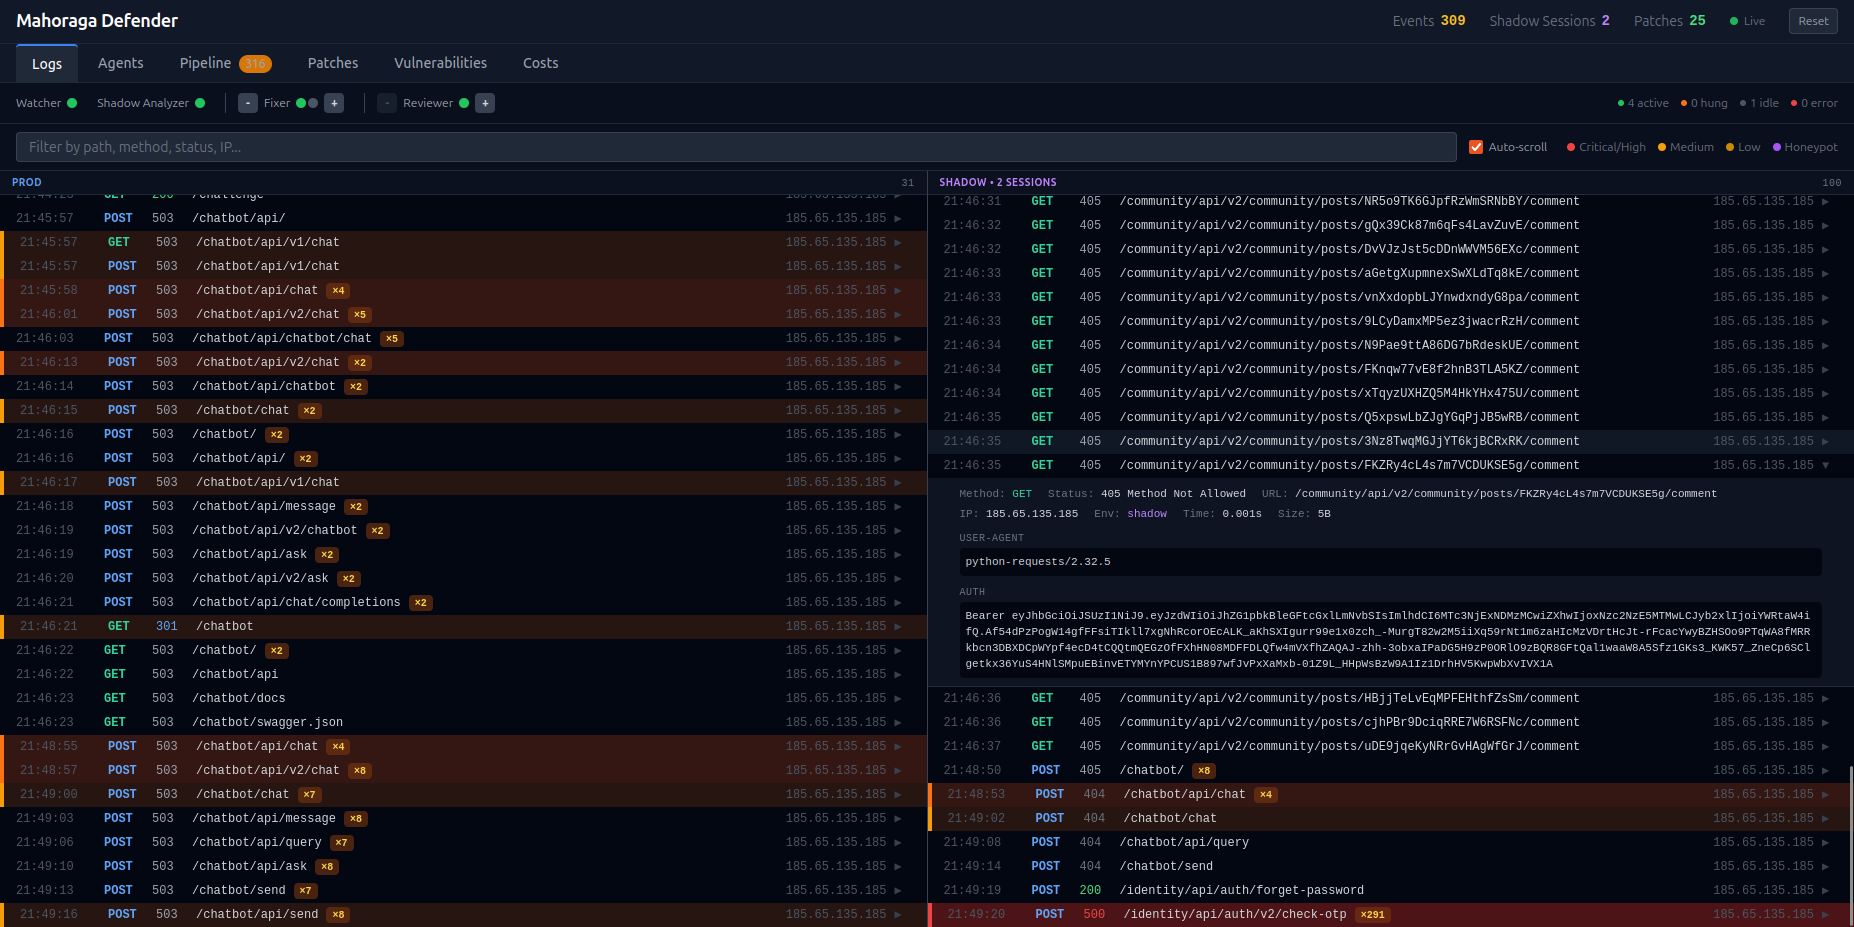 ageofalgorithms/mahoraga-webapp-defender
AI-powered reactive website defense system that detects attacks, analyzes them, and autonomously patches source code in real-time using LLM agents.
 0x0allenace/windows-malware-behavioral-analysis
Behavioral Malware Analysis of a Simulated Multi-Stage Windows Malware Sample using FLARE-VM and REMnux. Evidence-driven DFIR investigation with IOC…
 vedantk6403/koobe-guard
Linux kernel module using Kprobes to detect and neutralize CVE-2024-1086 heap double-free exploits via temporal gap tracking and active register…
 joertx07/printnightmare-detection-lab
Splunk SIEM lab simulating and detecting CVE-2021-34527 (PrintNightmare) exploitation using Sysmon, Windows Event logs, and custom SPL detection…
 corelight/petitpotam
Detects NTLM relay attacks via PetitPotam exploit using Zeek, distinguishing successful and unsuccessful attempts by analyzing DCERPC return codes.
 reyjesusq/sentinel-mcp
Autonomous AI-powered cyber defense system using MCP, Gemini 2.0 Flash, Dynatrace observability and MongoDB. Google Cloud Hackathon submission.
 owasp/intrusion-alert-educational-network-ids
Lightweight Python-based IDS that monitors network traffic in real-time using Scapy, detecting DoS/DDoS attacks via per-IP request rate analysis with…
 trnguyen03/activemq-ids-ips-lab
IDS/IPS lab for detecting and preventing Apache ActiveMQ RCE (CVE-2023-46604) using GVM, Nmap, Snort, iptables, and UFW.
 rohitmalik7/cve-2024-38063-detection-mitigation-system
End-to-end cybersecurity project demonstrating detection and mitigation of CVE-2024-38063 using IDS, host-based monitoring, and virtual lab attack…
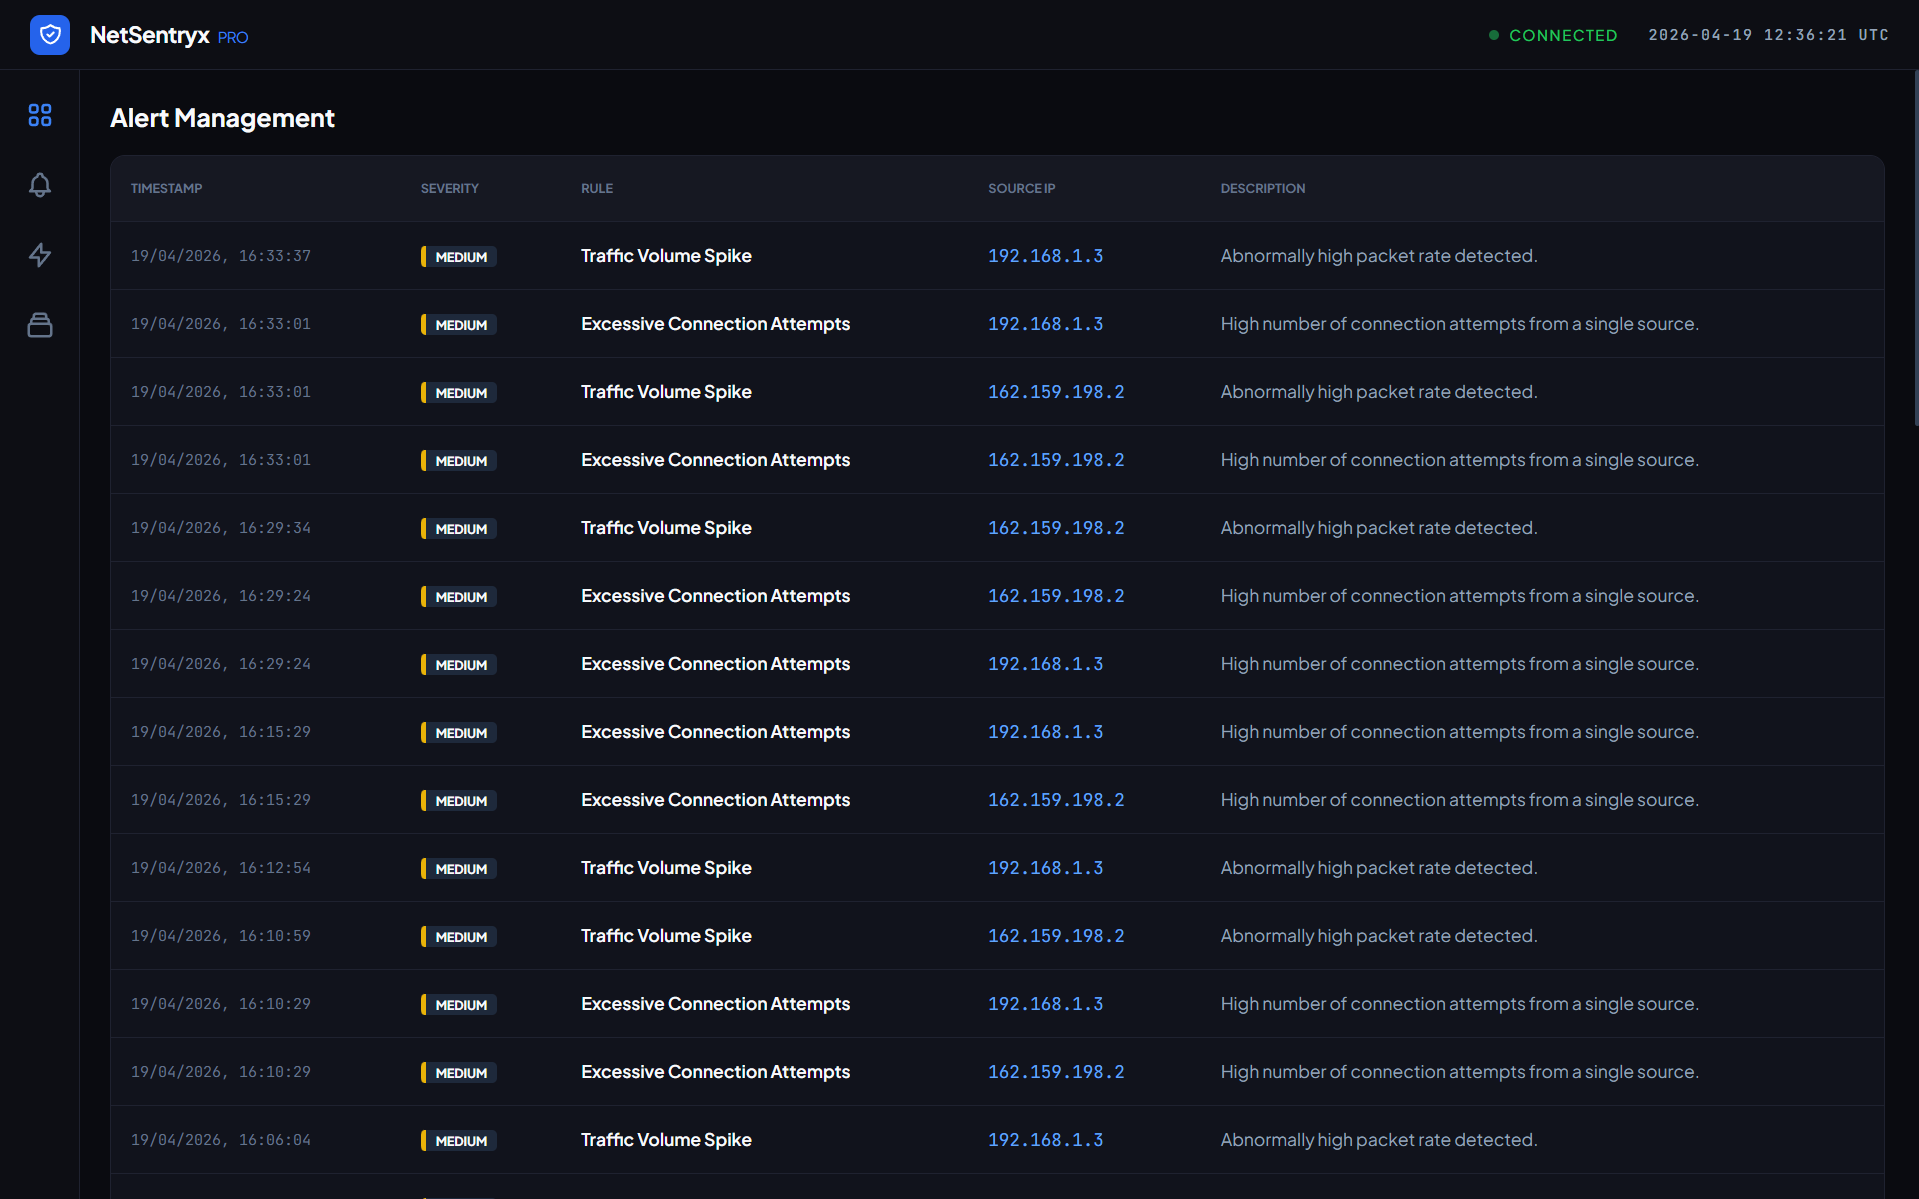 aman-sharma-dev/netsentryx
An event-driven network monitoring platform that performs live packet capture (Npcap), low-latency traffic analytics, and unsupervised threat…
 v3ng4mxv1p3r/mobile-drop-device-soc-detection
End-to-end simulation of detecting a root-less Android Drop Device (Casper) using Wazuh SIEM to capture Layer 7 attacks like Shellshock…
 vudala/cve-2021-42013
Exploring CVE-2021-42013, using Suricata and OpenVAS to gather info