
opensnitch
 evilsocket/opensnitch
Interactive GNU/Linux application firewall that filters outbound connections, blocks ads and malware domains, manages system firewall rules via GUI,…
defensive-toolsdns-analysisintrusion-detection+1
14.1k
evilsocket/opensnitchInteractive GNU/Linux application firewall that filters outbound connections, blocks ads and malware domains, manages system firewall rules via GUI,…
 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring
 zoneminder/zoneminder
ZoneMinder is a free, open source Closed-circuit television software application developed for Linux which supports IP, USB and Analog cameras.
 ossec/ossec-hids
OSSEC is an Open Source Host-based Intrusion Detection System that performs log analysis, file integrity checking, policy monitoring, rootkit…
 netalertx/netalertx
Centralized network visibility and continuous asset discovery. Monitor devices, detect change, and stay aware across distributed networks.
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
 cilium/tetragon
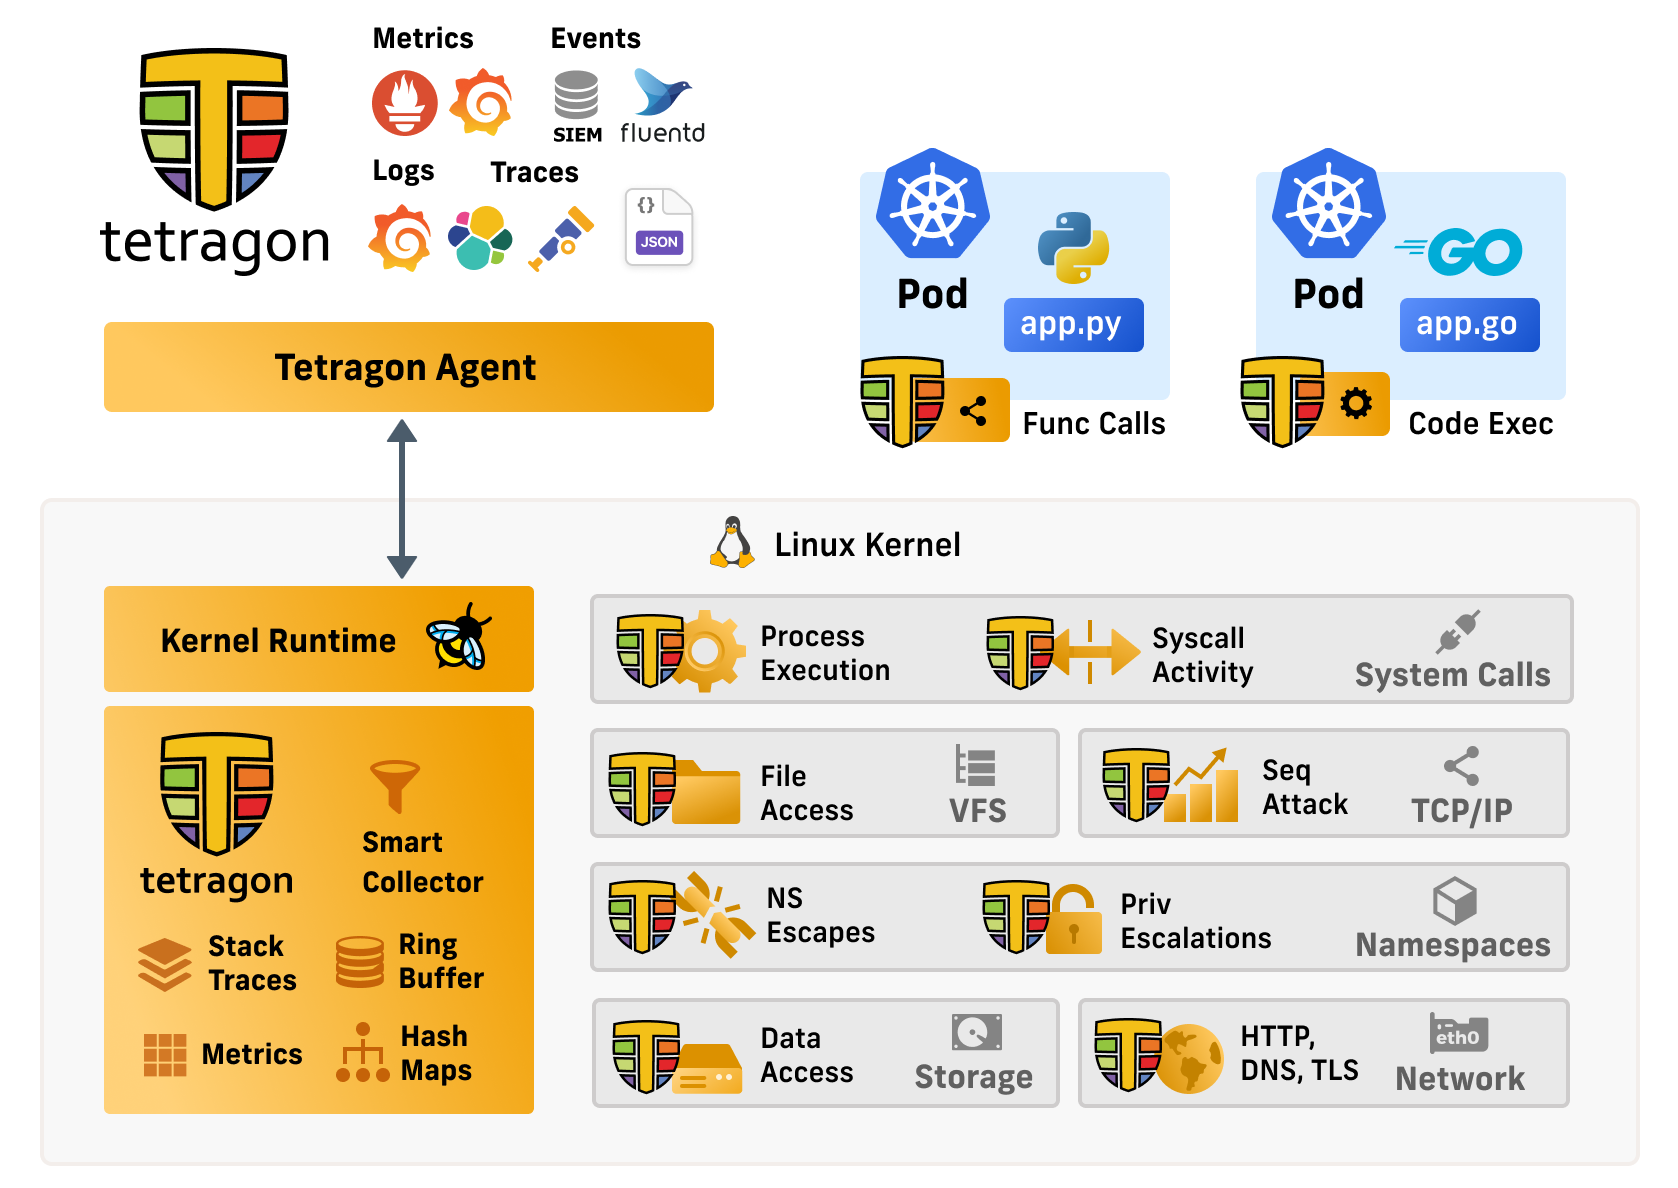
eBPF-based Security Observability and Runtime Enforcement
 clong/detectionlab
Automate the creation of a lab environment complete with security tooling and logging best practices
 0x4d31/awesome-threat-detection
Curated list of threat detection and hunting resources: detection rules, SIEM and log analysis tools, endpoint/network monitoring, datasets,…
 the-tcpdump-group/libpcap
System-independent library for user-level packet capture and filtering. Provides a portable framework for low-level network monitoring, security…
 hacklcx/hfish
Enterprise-grade honeypot system for detecting internal network breaches, external threats, and producing threat intelligence with 90+ service…
 thinkst/canarytokens
Canarytokens helps track activity and actions on your network
 neo23x0/signature-base
YARA signature and IOC database for my scanners and tools
 elastic/detection-rules
Develop, validate, and publish SIEM detection rules for Elastic Security, with Python CLI tooling, KQL parsing, Kibana integration, and packaged…
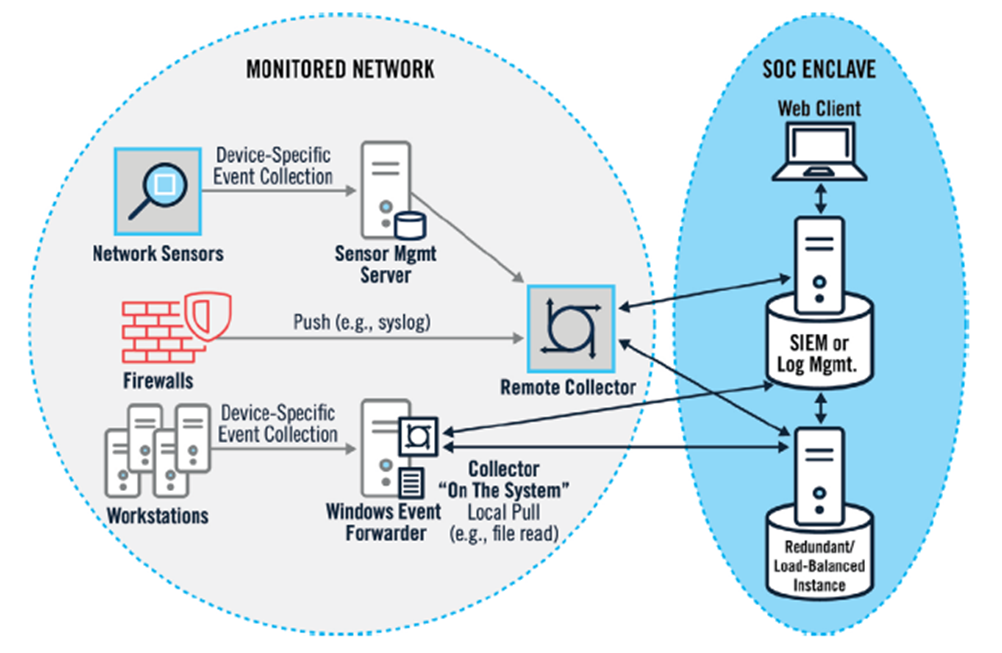 cyb3rxp/awesome-soc
A curated knowledge base to build, run and mature a SOC (including CSIRT).
 thinkst/opencanary
Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…
 cisagov/malcolm
Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…