
vulnerability-poc
 fankh/vulnerability-poc
CVE proof-of-concept labs, exploit scripts, and detection/prevention rules (Nginx, Apache, Snort, YARA) for high-severity CVEs. Authorized security…
ctfeducationexploitation+5
120
fankh/vulnerability-pocCVE proof-of-concept labs, exploit scripts, and detection/prevention rules (Nginx, Apache, Snort, YARA) for high-severity CVEs. Authorized security…
 arpsyndicate/vedas-signatures
VEDAS-Driven Autonomous Generation + Community Contributions of Suricata & Nuclei Rules for over 15k CVEs
 ahmed-tarek22752/security-vulnerability-in-microsoft-office.
Blue-team analysis of a malicious DOCX exploiting CVE-2017-0199, covering sandbox detonation, network forensics, IOC extraction, MITRE ATT&CK…
 ethan-andrews/exploitarium-detections
KQL detection rules for Microsoft Sentinel and Defender XDR covering the bikini/exploitarium anonymous disclosure — a personal research archive of…
 jhatchi/nexacorp-dfir-inc-2026-001
DFIR investigation + 7 Suricata rules on a simulated NexaCorp intrusion (vsftpd 2.3.4 CVE-2011-2523 + MITRE Caldera C2). 4-day solo engagement…
 techwithorgito/cve-2025-55182-researching-process
Defensive research repository for CVE-2025-55182 (Pre-Auth RCE in React Server Components/Next.js). Includes technical analysis, detection rules…
 vishvacyber/detection-tool-kit-for-cve-2026-31431
Layered detection toolkit for CVE-2026-31431 (Copy Fail) Linux kernel LPE. Provides eBPF, auditd, Sigma rules, page-cache diff, and IOC guides for…
 insomnisec/detections-cve-2026-23918
Detection rules for CVE-2026-23918 Apache http2 RCE - Credit: stringa.ai, isec.pl
 insomnisec/detections-cve-2026-31431
Detection rules, YARA signatures, auditd/Wazuh rules, and MISP event templates for CVE-2026-31431 Linux kernel LPE vulnerability (Copy Fail).…
 orgito1015/cve-2025-55182-researching-process
Defensive research repository for CVE-2025-55182 (Pre-Auth RCE in React Server Components/Next.js). Includes vulnerability analysis, detection rules…
 vasyapokemon/cve-2026-31431
Research and detection toolkit for Linux kernel LPE CVE-2026-31431, including exploit analysis, YARA rules, auditd/Falco detection, patching guide,…
 ashok523/cve-2026-31431
Defensive IR playbook and detection package for CVE-2026-31431 (Copy Fail) Linux kernel LPE, including Sigma, auditd, Falco, Wazuh, YARA, eBPF, and…
 cybersecurity-enthusiasts-ce/cve-2025-55182-researching-process
Defensive research repository for CVE-2025-55182 (Pre-Auth RCE in React Server Components/Next.js). Includes technical analysis, detection rules…
 garethmsheldon/cve-2025-60787-detection-motioneye-rce-via-config-injection
Detection rules and YARA/KQL signatures for CVE-2025-60787, an unauthenticated RCE in motionEye via config injection, with process execution and file…
 hullabrian/eventhorizon
Tool that gathers a customizable set of ETW telemetry and generates user-defined detections
 bartblaze/yara-rules
Collection of private Yara rules.
 malvuln/sigint-hombre
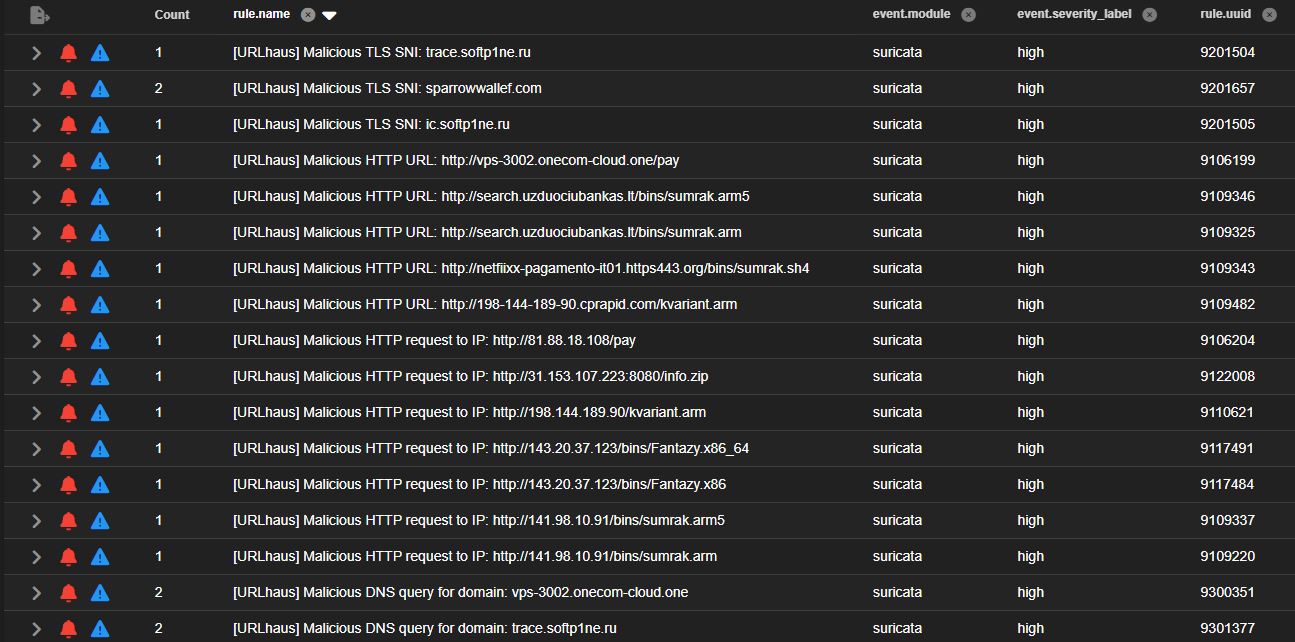
Dynamically generated Suricata rules from real-time threat feeds
 sumidcyber/zeroscout
🦅 ZeroScout: The Autonomous Local & Cloud Threat Hunter. Visualize attacks in a live War Room, identify APT groups via Genetic Analysis, and…